Fake GitHub Repositories Deliver Rapuncel Infostealer and EDR-Killing Driver
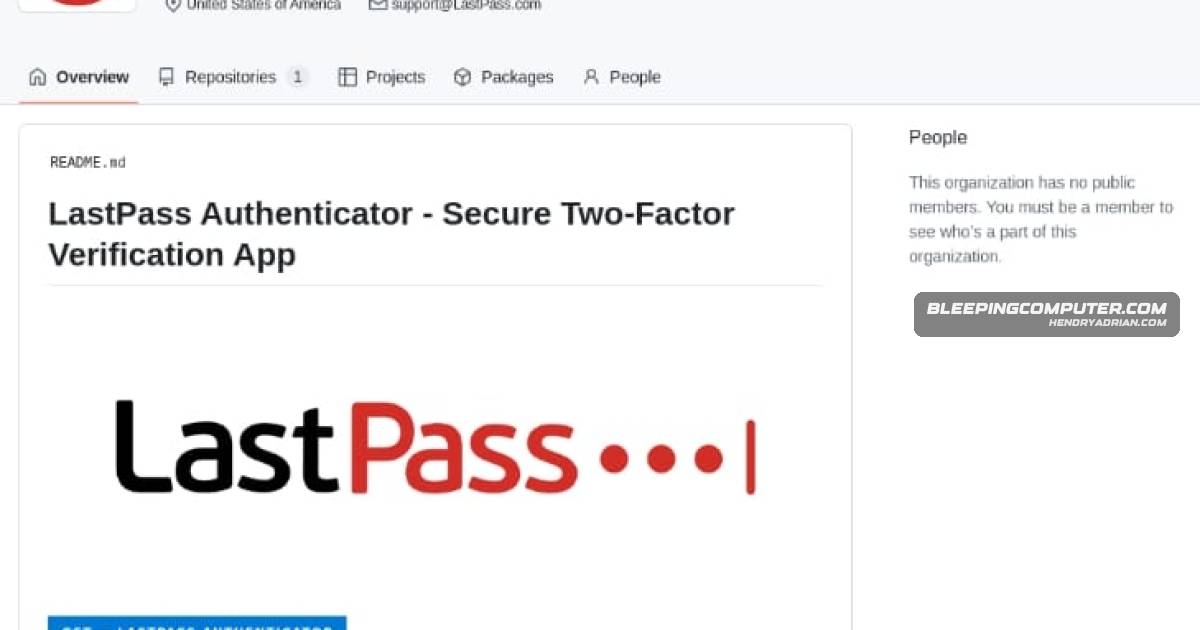
Summary
Researchers say SEO-optimized GitHub repos impersonate software brands to deliver Rapuncel, which steals credentials and other data. Its installer also deploys a Microsoft-signed driver reported to terminate 145 security products.
Key points
- LastPass and Delphos Labs reported that fake GitHub repositories impersonate LastPass and at least 39 other companies, luring users through search results and fake download pages.
- The downloaded archives contain a renamed Visual Studio CoreCLR Debugger configured to sideload a malicious DLL and install Rapuncel alongside the Alinubx.sys driver.
- The driver, disguised as an NVIDIA component and signed through Microsoft’s Windows Hardware Compatibility Publisher chain, targets 145 antivirus and EDR processes; researchers said it was not on Microsoft’s vulnerable-driver blocklist.
- Rapuncel steals browser credentials, cryptocurrency wallet data, session credentials, Windows Credential Manager contents, selected documents, screenshots, and system information.
- Researchers said Rapuncel bypasses browser app-bound encryption by injecting a helper DLL and invoking the browser’s Elevation Service. Stolen data is sent to 2.26.126[.]50 over raw TCP.
- The malware persists through a Windows service and reportedly terminates security tools again if they restart. Researchers assessed with moderate confidence that Rapuncel is a BoryptGrab variant.
- The researchers recommend downloading software only from official sites and avoiding suspicious GitHub repositories and promoted search results.
Article Details
- Attack Vectors
- SEO-optimized GitHub repositories impersonated LastPass and other software brands, directing searchers through fake download pages and redirections to payload-delivery servers.
- Inflated ZIP archives contained a renamed copy of vsdbg.exe, configured to sideload a malicious DLL and deploy Rapuncel and the Alinubx.sys driver.
- Rapuncel collected credentials and other data, then uploaded compressed information to 2.26.126[.]50 over raw TCP using an HTTP-formatted request.
- Defensive Notes
- Download software only from official websites; avoid dubious GitHub repositories and skip or block promoted Google Search results.
- The article reports that Alinubx.sys was not in Microsoft's vulnerable drivers blocklist at the time of reporting.
- The researchers said additional driver capabilities, including file and registry hiding, DLL injection, traffic manipulation, and port redirection, did not appear to be activated in this campaign.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 2[.]26[.]126[.]50 | External endpoint used by Rapuncel to upload stolen information. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelRapuncel uploads compressed stolen information to an external endpoint.T1055 · Process InjectionRapuncel injects a helper DLL into browser applications.T1082 · System Information DiscoveryRapuncel collects detailed system information.T1105 · Ingress Tool TransferThe fake download flow delivered ZIP archives containing the installer and payloads.T1204.002 · Malicious FileVictims clicked download buttons and ran the installer delivered in ZIP archives.T1543.003 · Windows ServiceRapuncel persists across reboots via a Windows service.T1555.003 · Credentials from Web BrowsersRapuncel steals credentials stored in web browsers.T1562.001 · Disable or Modify ToolsAlinubx.sys terminates antivirus and EDR processes to impair security defenses.T1574.002 · DLL Side-LoadingThe renamed vsdbg.exe installer was configured to sideload the malicious vsdbg.dll.T1608.006 · SEO PoisoningThe campaign used SEO-optimized GitHub repositories impersonating software brands to attract searchers to fake download pages.
People
Malware
Alinubx.sysThe chain also installs the Alinubx.sys kernel driver, which is signed through Microsoft and can terminate 145 antivirus and EDR products while stealing credentials, browser data, and wallet information.BoryptGrabLastPass and Delphos Labs assessed with moderate confidence that Rapuncel is a variant of BoryptGrab, while they also found that its loader was built with the Cruciferra PUROSANGUE crypter.RapuncelA malware campaign is using SEO-optimized GitHub repositories to impersonate LastPass and dozens of other software firms in order to distribute the newly observed Rapuncel information stealer.
Vendors
Delphos LabsLastPass and Delphos Labs uncovered the campaign, which they report impersonates the password manager brand and at least 39 other companies.LastPassA malware campaign is using SEO-optimized GitHub repositories to impersonate LastPass and dozens of other software firms in order to distribute the newly observed Rapuncel information stealer.MicrosoftThe chain also installs the Alinubx.sys kernel driver, which is signed through Microsoft and can terminate 145 antivirus and EDR products while stealing credentials, browser data, and wallet information.
Products
EdgeTo bypass Google’s app-bound encryption protection present on Chrome, Edge, and related browsers, Rapuncel injects a helper DLL into the app and invokes its own Elevation Service.Google ChromeTo bypass Google’s app-bound encryption protection present on Chrome, Edge, and related browsers, Rapuncel injects a helper DLL into the app and invokes its own Elevation Service.Google SearchUsers are recommended to only download software from official websites, avoid dubious GitHub repositories, and skip or block promoted results on Google Search.LastPass AuthenticatorThe attack chain begins when victims search for LastPass Authenticator or other popular software and follow links to fake GitHub repos.Microsoft Visual Studio CoreCLR DebuggerThe installer inside the archives is a copy of the legitimate Microsoft Visual Studio CoreCLR Debugger, ‘vsdbg.exe,’ renamed and configured to sideload a malicious DLL (vsdbg.dll).Microsoft WindowsCurrently, the driver is not in Microsoft’s vulnerable drivers blocklist, and the one used in the campaign is signed through Microsoft’s Windows Hardware Compatibility Publisher chain.