
DNS Analysis Expands IoCs Linked to Three Russian Threat Groups
Summary
An analysis of IoCs linked to three Russian threat groups found potentially victim-associated IP activity and additional domains and IPs, including some assessed as malicious. The findings are based on DNS, WHOIS, and threat-intelligence data.
Key points
- The analysis examined 33 network IoCs linked by Google Threat Intelligence Group to groups UNC6293, UNC7005, and UNC5976: two subdomains, 26 domains, and five IP addresses.
- One subdomain, drive.google.verify-drive.com, was assessed as high risk for impersonating Google Drive; mail.kiis.co.uk was rated moderately risky.
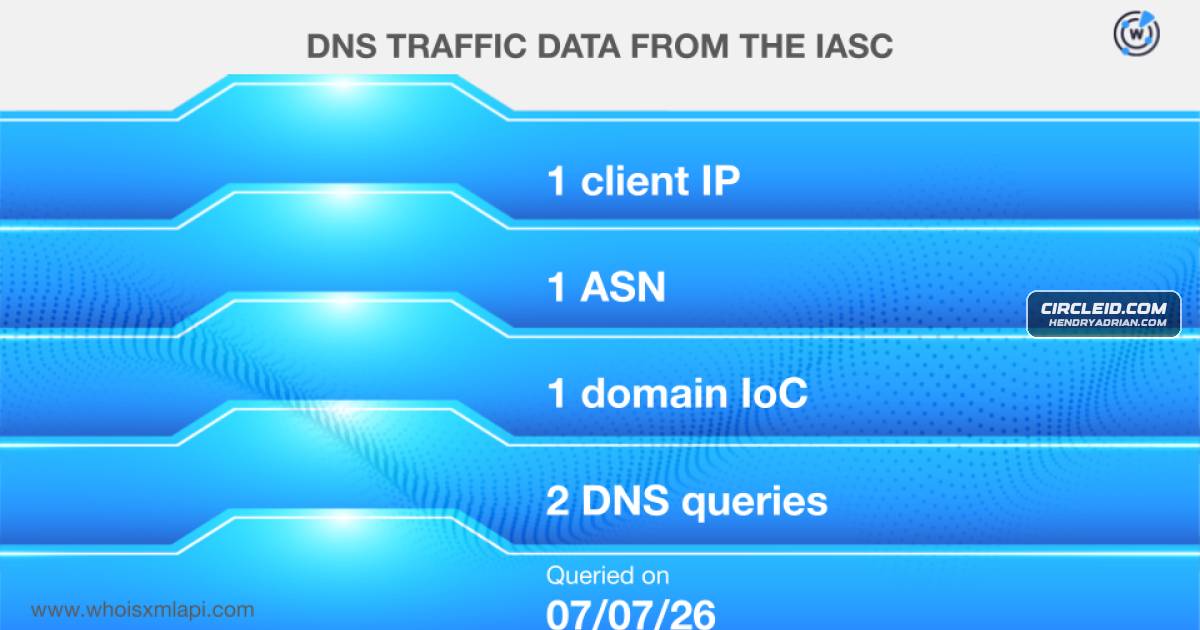
- Traffic data showed one client IP queried globsec.net, and 317 potentially victim-owned IP addresses communicated with five IP IoCs between 5 April and 23 August 2026.
- Researchers identified a 10-domain typosquatting group that included wa-connect.net and a domain reportedly listed as malicious on its registration date, 274 days before GTIG identified it as an IoC.
- WHOIS email analysis led to 2,494 associated domains; three were assessed as malicious, including one associated with malware distribution.
- Further analysis found 15 additional IP addresses, 14 assessed as malicious, and 29 IP-connected domains, 13 assessed as malicious.
- The article cautions that entities labeled malicious may require further investigation and recommends corroborating the findings.
Article Details
- Attack Vectors
- UNC6293, UNC7005, and UNC5976 targeted persons of interest, according to the article.
- drive[.]google[.]verify-drive[.]com was identified as a deceptive subdomain impersonating Google Drive.
- dsapdlqpwd[.]icu was associated with malware distribution between 26 April and 25 August 2026.
- Defensive Notes
- The article recommends avoiding both identified subdomain IoCs and advises supplementary investigation to corroborate entities labeled as threats.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | dosportal[.]app | Listed as a domain IoC in the article's DNS-history examples. |
| DOMAIN | dsapdlqpwd[.]icu | Associated with malware distribution between 26 April and 25 August 2026. |
| DOMAIN | fm-connect[.]site | Identified as a lookalike in the typosquatting group analyzed alongside domain IoCs. |
| DOMAIN | globsec[.]net | Domain IoC; sample traffic showed a client IP communicating with it. |
| DOMAIN | gmo-connect[.]cloud | Identified as a lookalike in the typosquatting group analyzed alongside domain IoCs. |
| DOMAIN | go-connect[.]live | Identified as a lookalike in the typosquatting group analyzed alongside domain IoCs. |
| DOMAIN | kiis[.]co[.]uk | Listed as a domain IoC in the article's DNS-history examples. |
| DOMAIN | kmconnect[.]nl | Identified as a lookalike in the typosquatting group analyzed alongside domain IoCs. |
| DOMAIN | kmconnect[.]online | Identified as a lookalike in the typosquatting group analyzed alongside domain IoCs. |
| DOMAIN | l-connect[.]io | Identified as a domain IoC in the article's typosquatting-group analysis. |
| DOMAIN | mioisiskwowiwjowuwjwolab[.]club | Listed as a domain IoC in the article's DNS-history examples. |
| DOMAIN | miov2iaiaoubqosiqoiajwowiwjso[.]online | Domain IoC reported on the First Watch Malicious Domains Data Feed when created. |
| DOMAIN | msmconnect[.]org | Identified as a lookalike in the typosquatting group analyzed alongside domain IoCs. |
| DOMAIN | pmo-connect[.]com | Identified as a lookalike in the typosquatting group analyzed alongside domain IoCs. |
| DOMAIN | ut-connect[.]net | Identified as a lookalike in the typosquatting group analyzed alongside domain IoCs. |
| DOMAIN | wa-connect[.]net | Domain IoC identified in a typosquatting group. |
| DOMAIN | wa-meeting[.]com | Listed as a domain IoC in the article's DNS-history examples. |
| HOSTNAME | drive[.]google[.]verify-drive[.]com | Deceptive subdomain identified as impersonating Google Drive. |
| HOSTNAME | mail[.]kiis[.]co[.]uk | Identified as a moderately risky subdomain IoC; the article notes prior reputation and registrar email forwarding. |
| IPV4 | 104[.]194[.]159[.]150 | IP IoC with reported historical IP-to-domain resolutions. |
Threat Actors
Products
Countries
NetherlandsThey were geolocated in three countries, two of which—the Netherlands and the U.S.— also appeared in the list of domain IoC registration countries.United StatesThey were geolocated in three countries, two of which—the Netherlands and the U.S.— also appeared in the list of domain IoC registration countries.