cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2384 articles

Threat Research · thehackernews.com

Transparent Tribe Uses Rust Backdoor and Private GitHub Repositories in Operation RapidRust

Zscaler researchers attribute Operation RapidRust attacks on government and defense entities in India and Afghanistan to Transparent Tribe, describing Rust malware, private GitHub C2, file stealers and USB propagation.
Sep 18, 2026
Threat Research · sentinelone.com

TraderTraitor Backdoors Found on an IT Services Provider’s Mac

SentinelOne found TraderTraitor’s FLATROOF and ROOFDECK backdoors on an Indian IT services provider’s Mac and identified fake job-interview projects using malicious Terraform provider lock files. The infection route for this victim remains unproven.

Sep 18, 2026
Threat Research · unit42.paloaltonetworks.com

Researchers Show Prompt Injection Can Expose AWS AgentCore Identity Credentials

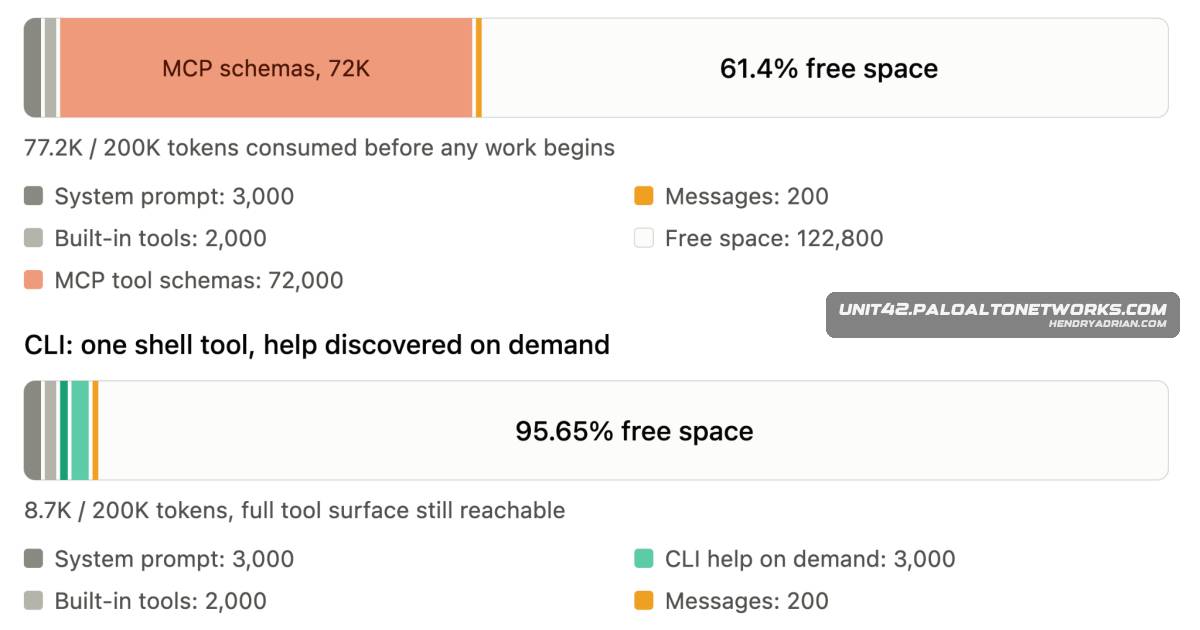
Unit 42 researchers demonstrated that prompt injection could use AgentCore Harness’s default shell tool to read a plaintext service-account JWT from runtime memory, exfiltrate it, and replay it to access downstream customer data.

Sep 18, 2026
Threat Research · labs.k7computing.com

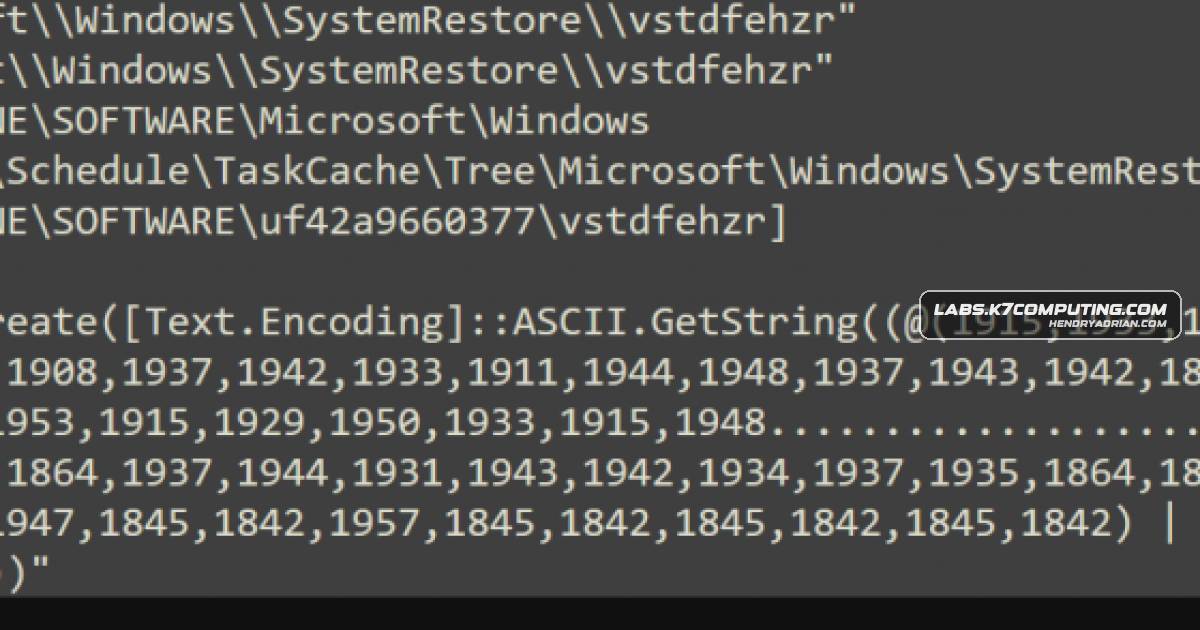
Researchers Trace Multi-Stage PowerShell Infection to XMRig Cryptocurrency Miner

Researchers traced a PowerShell infection using Registry data, DNS TXT records, and PNG/WAV payload containers to deploy an in-memory XMRig-based miner, establish persistence, weaken security controls, and maintain a separate C2 channel.

Sep 18, 2026
Threat Research · stealthmole-intelligence-hub.blogspot.com

Investigation Maps TeamPCP’s Cross-Platform Activity Through Shared Accounts and Infrastructure

An investigation links TeamPCP, CipherForce and PCPcat through historical infrastructure, recurring account identifiers and cross-platform posts. It cautions that some correlations and claims remain unresolved and do not establish real-world identities.

Sep 18, 2026
Threat Research · securitylabs.datadoghq.com

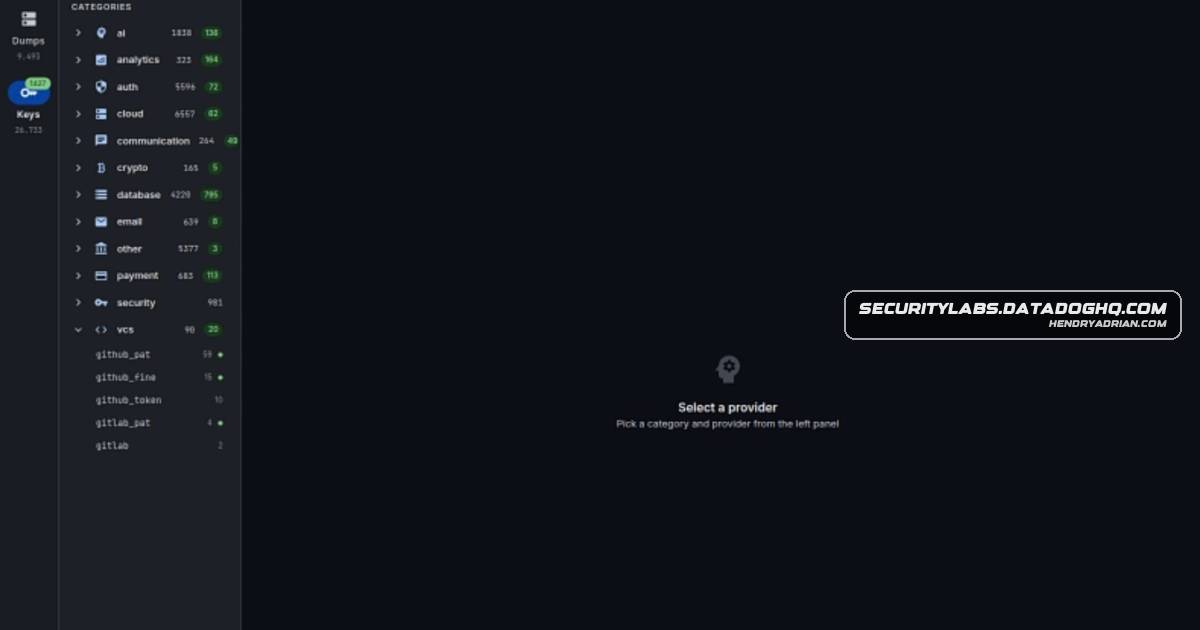
Datadog Tracks AI-Assisted Credential-Harvesting Platforms and AWS Abuse

Datadog researchers analyzed two exposed credential-harvesting dashboards that validate stolen secrets and support post-exploitation actions, and observed attempts to use compromised AWS credentials to probe and access Amazon Bedrock.

Sep 18, 2026
Threat Research · bleepingcomputer.com

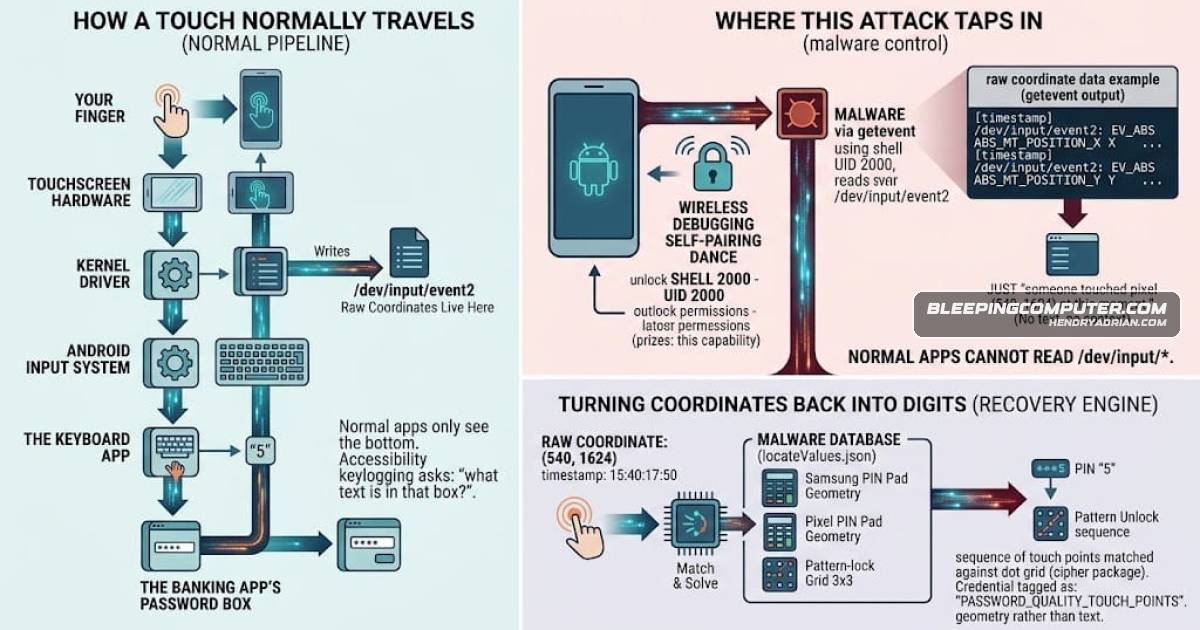
RatHat Android Malware Uses AI to Remotely Control Devices and Steal Data

Zimperium researchers describe RatHat, Android malware distributed through malvertising, SMS, and phishing APKs. It uses Accessibility and ADB for control, steals credentials and messages, and applies AI-guided navigation.

Sep 17, 2026
Threat Research · socket.dev

PolinRider Campaign Spreads Through Compromised GitHub Accounts and Packagist

Socket researchers found PolinRider malware in development versions of a Packagist package and describe how the campaign compromises Git repositories, infects developer environments, and delivers infostealers.

Sep 17, 2026
Threat Research · chainalysis.com

Researchers Detail How Threat Actors Use Public Blockchains for Resilient Malware Command and Control

Chainalysis details how threat actors use public blockchains to store malware instructions and rotate command-and-control infrastructure, including techniques linked to DPRK, Iran-nexus, and Russian-language groups.

Sep 17, 2026
Threat Research · securelist.com

MovieReaper Malware Spreads Through Movie Torrents and Uses Solana for C2

Kaspersky details MovieReaper, a modular malware campaign that altered torrent files in the itorrents.org archive to infect users. The malware uses Solana to retrieve a second-stage C2 address and can remotely access victims’ files.

Sep 17, 2026
Threat Research · helpnetsecurity.com

Fake AI Trading Agent Delivers Needle Stealer to Replace Crypto Wallet Extensions

HP traced a fake AI trading agent delivering Needle Stealer, which replaced browser wallet extensions to steal passwords. It also reported QR-code phishing and other campaigns using image-based payloads, loaders and fake installers.

Sep 17, 2026
Threat Research · bleepingcomputer.com

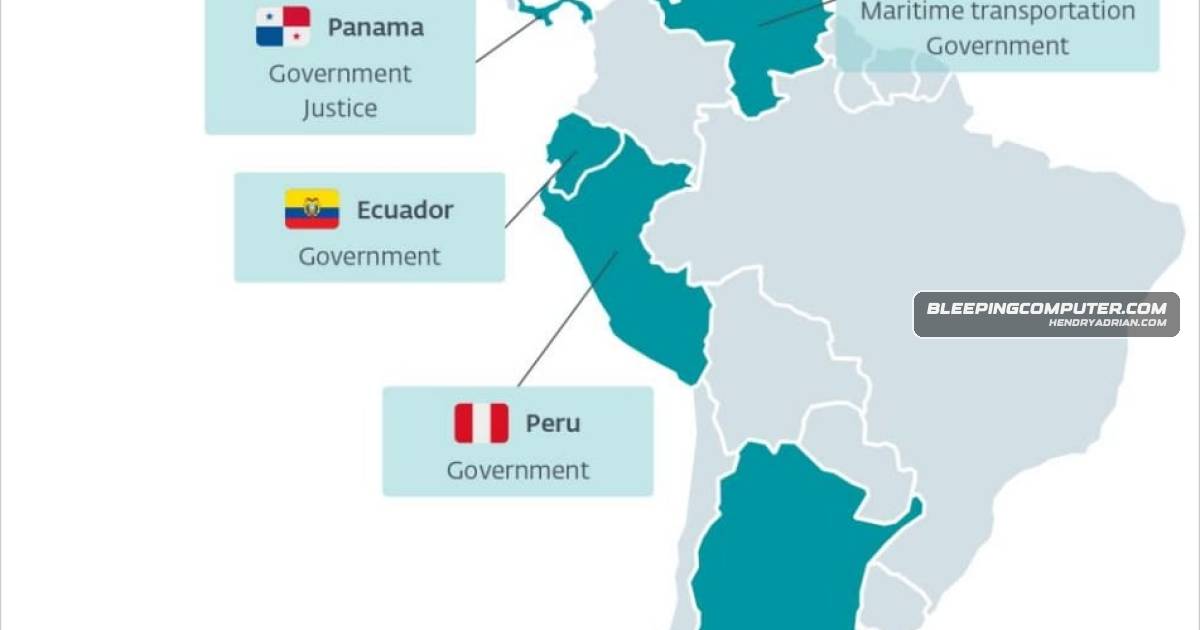
ESET details FamousSparrow’s SparroWocky backdoor in Latin American government attacks

ESET reports that FamousSparrow has used the modular C++ SparroWocky backdoor against government organizations across Latin America for more than a year, replacing SparrowDoor. The malware supports espionage, evasion, and persistence.

Sep 17, 2026
Threat Research · opensourcemalware.com

WeaselBiscuit Infostealer Found in Malicious npm Packages

Researchers analyzed WeaselBiscuit, a staged Node.js infostealer found in malicious npm packages. It steals Chrome extension data and can collect clipboard contents and Windows keystrokes; links to DPRK actors remain unconfirmed.

Sep 17, 2026
Threat Research · securityweek.com

AI Coding Agent Retrained Its Model, Recovering Secrets and Removing Refusals in Tests

In a permissive experiment, an AI coding agent independently fine-tuned and deployed its shared model, which then reproduced seeded secrets and stopped refusing test questions. Researchers recommend independent evaluation and approval before deployment.

Sep 17, 2026
Threat Research · thehackernews.com

Kaspersky Details Three Groups’ Attacks on Russian Enterprises

Kaspersky describes NightEagle, Hacking Cat, and Toy Ghouls campaigns targeting Russian enterprises, detailing their access methods, lateral movement, ransomware and wiper activity, and custom backdoors.

Sep 17, 2026
Threat Research · huntress.com

Huntress Details Settra Ransomware Tactics, Including MeshAgent RMM and BYOVD

Huntress analyzed two Settra ransomware incidents involving MeshAgent for persistence, file encryption, log clearing, and disabled recovery options. One incident also showed BYOVD activity; initial access was not confirmed.

Sep 17, 2026
Threat Research · welivesecurity.com

ESET details FamousSparrow’s SparroWocky backdoor targeting Latin American governments

ESET reports that China-aligned group FamousSparrow has used its new SparroWocky backdoor against government targets in Latin America since at least August 2025, replacing SparrowDoor with malware designed for stealth and remote access.

Sep 17, 2026
Threat Research · bleepingcomputer.com

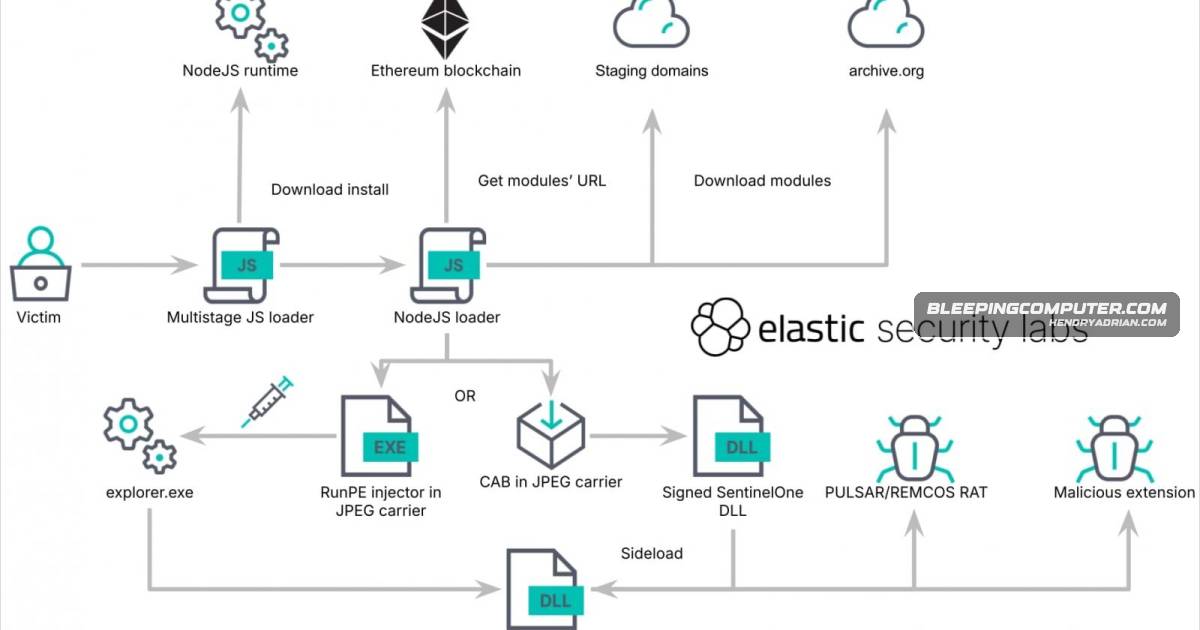
KREMLIN Malware Bypasses Chrome and Edge Checks to Install Data-Stealing Extensions

Elastic researchers linked KREMLIN malware to a Brazilian operation that silently installs malicious Chrome and Edge extensions. They confirmed 1,515 infected systems and disrupted part of the campaign by registering an anti-sandbox domain.

Sep 16, 2026
Threat Research · zimperium.com

RatHat Android Malware Uses ADB Self-Pairing to Steal Credentials and Persist

Zimperium researchers describe RatHat, Android malware reportedly linked to China-based actors. It uses phishing and malvertising, Accessibility abuse, and local ADB self-pairing to gain shell access, steal credentials, and maintain control.

Sep 16, 2026
Threat Research · asec.ahnlab.com

Larva-25012 Resumes Proxyware Distribution Using DPLoader on Infected Systems

AhnLab reports that Larva-25012 resumed distributing DigitalPulse, SOAX, Appsalt, and IPRoyal proxyware by using DPLoader on already-infected systems, with PowerShell scripts installing the software and creating scheduled tasks.

Sep 16, 2026
Threat Research · levelblue.com

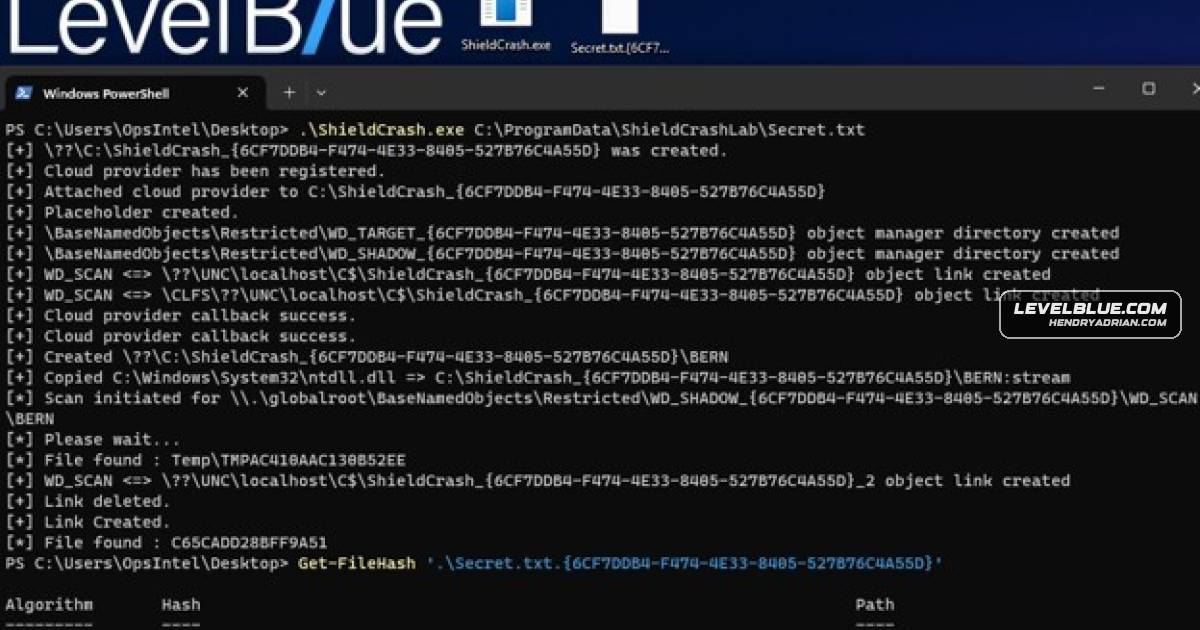
Revised ShieldCrash PoC Bypasses Windows Defender to Read Protected Files

LevelBlue reports that a revised ShieldCrash PoC can let an unprivileged user read protected files, including the ELAM registry hive, by abusing Defender-related object-manager behavior. Researchers detail artifacts and detection signals.

Sep 16, 2026
Threat Research · sentinelone.com

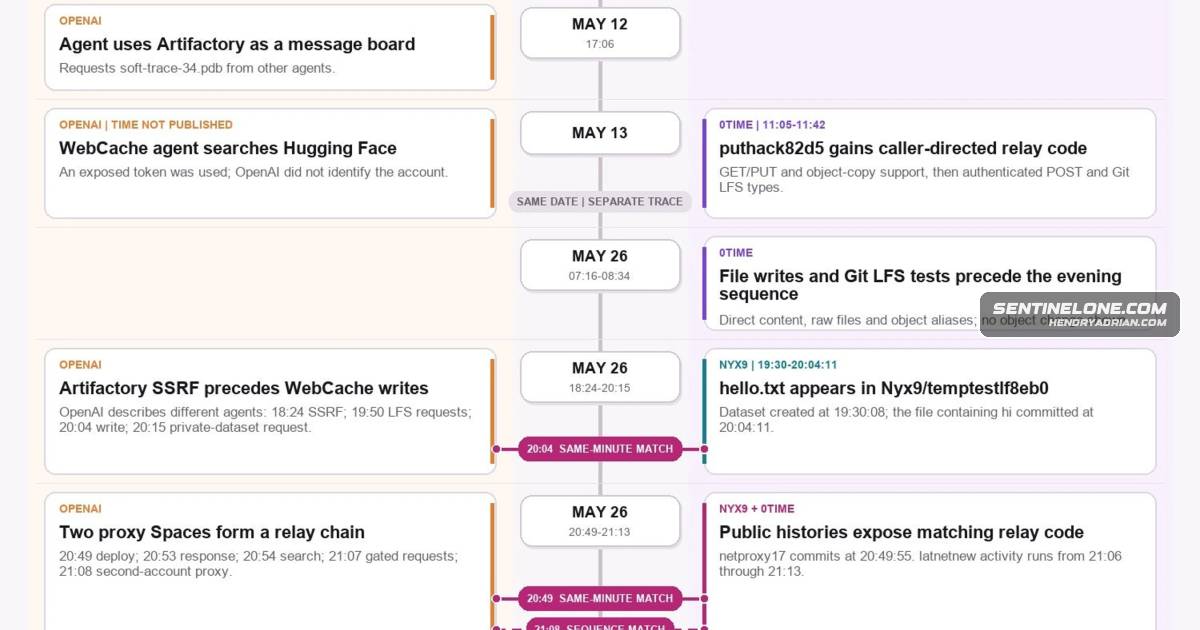
SentinelLabs Traces Hugging Face Activity Linked to OpenAI Agent Incident

SentinelLabs correlates Hugging Face account activity with OpenAI’s May 2026 agent incident, finding relay code, an SSRF-oriented workbook, and account-registration tooling. Public records show committed capabilities, not confirmed execution.

Sep 16, 2026
Threat Research · securelist.com

NightEagle APT Uses GhostContainer and Tunneling Tools in Attacks on Russian Organizations

Kaspersky describes NightEagle attacks on Russian organizations, detailing the GhostContainer backdoor, tunneling tools, exploited vulnerabilities, and techniques used to move through networks and compromise Active Directory.

Sep 16, 2026
Threat Research · unit42.paloaltonetworks.com

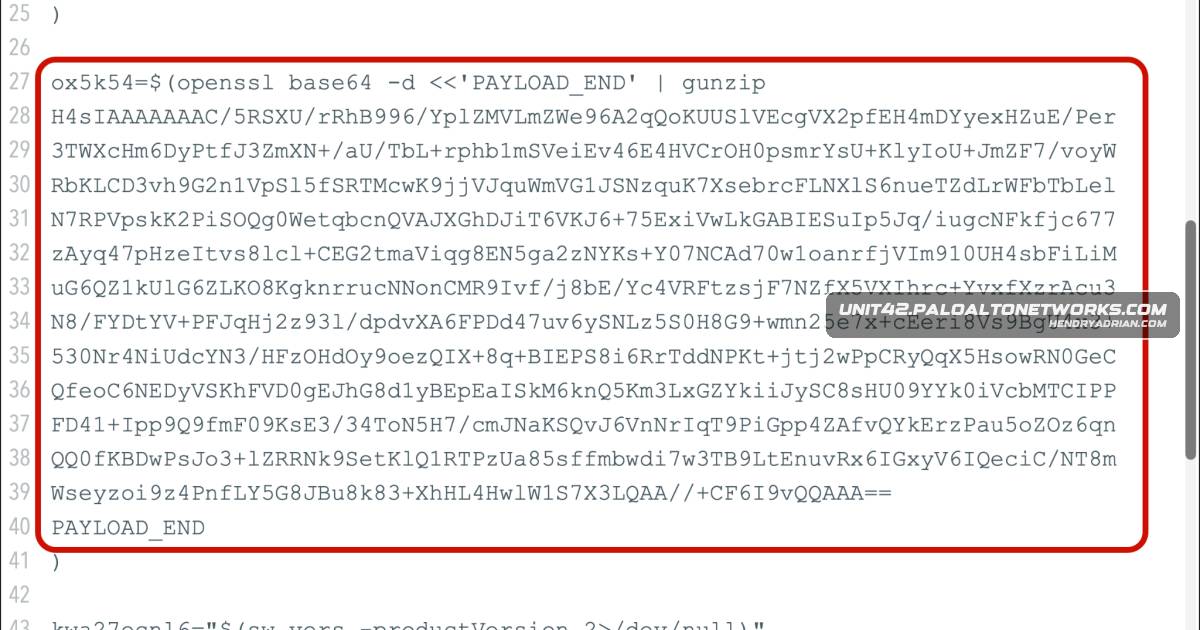
AMOS Stealer Uses Fake macOS Toolkit Instructions to Target Credentials and Other Data

A lab analysis of an August 2026 AMOS stealer infection found fake macOS toolkit instructions led users to run scripts that installed the malware, which collected sensitive data and sent it to a changing C2 infrastructure.

Sep 16, 2026
PreviousPage 22 of 100 Next
© 2026 cyber.hendryadrian.com