How AWS Quarantines Exposed IAM Credentials and How to Monitor the Response
Summary
Unit 42 examines how AWS’s quarantine policy limits exposed IAM credentials, documents a test in which it was attached within 10 seconds of a public GitHub exposure, and explains how teams can monitor AWS and GitHub logs for response events.
Key points
- AWS attaches the AWSCompromisedKeyQuarantine managed policy when it identifies exposed IAM credentials, denying selected actions to limit misuse while allowing other operations.
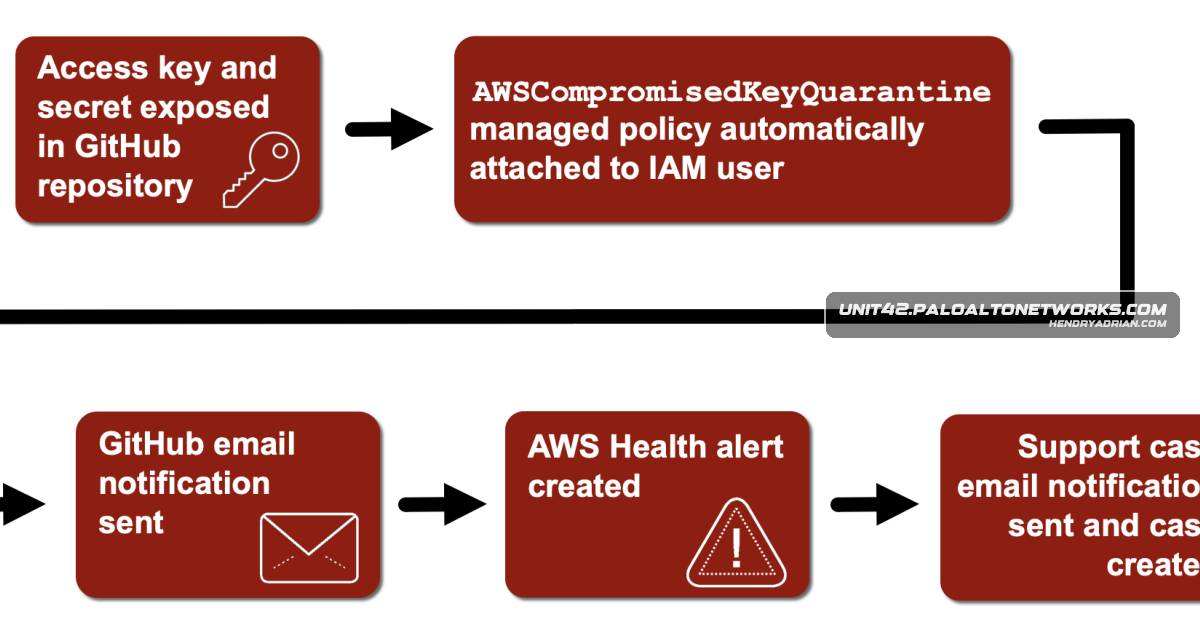
- In Unit 42’s test, AWS attached the V3 policy 10 seconds after credentials were pushed to a public GitHub repository; AWS and GitHub notifications and an AWS Support case followed.
- The policy has expanded over time to restrict actions across additional AWS services, reflecting changing attack methods, including cloud resource abuse and data deletion.
- The policy attachment appears in CloudTrail as an IAM AttachUserPolicy event; the policy ARN is in requestParameters.
- Security teams can monitor policy-attachment events and use AWS Systems Manager Explorer to aggregate AWS Support cases.
- GitHub’s AWS credential validity checks use STS GetCallerIdentity; teams can look for the associated GitHub IP ranges and user-agent strings in CloudTrail.
- GitHub push protection may miss secrets in very large pushes or alert on only five secrets in a single push, so organizations should account for possible scanning gaps.
Article Details
- Attack Vectors
- Long-term AWS IAM access keys and secrets exposed in public code repositories or publicly accessible environment-variable files can be misused by attackers.
- Exposed IAM credentials can enable unauthorized actions not explicitly denied by the AWSCompromisedKeyQuarantine policy.
- The article describes attacker activity that includes creating IAM roles and Lambda functions, deleting S3 data after exfiltration, and making unauthorized Amazon Bedrock API calls.
- Defensive Notes
- AWS automatically attaches an AWSCompromisedKeyQuarantine policy after detecting exposed credentials; the article advises not to remove it and to follow the AWS support-case instructions.
- Monitor CloudTrail for IAM AttachUserPolicy events and inspect the requestparameters PolicyArn value for AWSCompromisedKeyQuarantine policies.
- Use AWS Systems Manager Explorer to aggregate AWS Support cases and alert security teams to quarantine events.
- Monitor GitHub credential-validity checks appearing as GetCallerIdentity events, including the associated user agent and GitHub ASN IP addresses.
- Account for GitHub push-protection gaps: very large pushes may not be scanned, and only five exposed secrets in a single push may generate alerts.
- Apply least-privilege permissions and investigate exposed credentials promptly; quarantine policies deny selected actions but do not disable the credentials or deny every action.
MITRE ATT&CK
People
Vendors
Amazon Web ServicesThis article explores how AWS mitigates the security risks associated with publicly exposed Identity and Access Management (IAM) access keys through its AWSCompromisedKeyQuarantine managed policy.GitHubAdditionally, this article provides background to the partner integration between GitHub's secret scanning program and AWS.Palo Alto NetworksPalo Alto Networks customers are better protected from the threats discussed above through the following products and services:
Products
Amazon BedrockTo counter malicious activity targeting the Amazon Bedrock service, AWS expanded v5 of the AWSCompromisedKeyQuarantineV2 managed policy to restrict five Bedrock permissions.Amazon S3AWS CloudTrailThe timeline below details each step of the testing process with commentary about what actions appear in the default AWS CloudTrail logs.AWS IAMWhen organizations face attacks against their AWS environments, misuse of AWS IAM user access keys continue to account for a large majority of initial attack vectors.AWS Systems Manager Explorerof these emails. To prevent these communication gaps, security professionals can leverage AWS Systems Manager Explorer which helps aggregate AWS Support cases. The security team can also proactively enableAWSCompromisedKeyQuarantineThis article explores how AWS mitigates the security risks associated with publicly exposed Identity and Access Management (IAM) access keys through its AWSCompromisedKeyQuarantine managed policy.AWSCompromisedKeyQuarantineV2With AWSCompromisedKeyQuarantineV2, released on April 21, 2021, the permissions evolved to include the Amazon Simple Storage Service (S3) service with 11 permissions and 16 additional permissions to the original fiveAWSCompromisedKeyQuarantineV3During the test scenario, AWS attached the AWSCompromisedKeyQuarantineV3 managed policy within 10 seconds of the access key exposure.Cortex CloudCortex CloudGitHub Advanced SecurityGitHub has also created validity checks as part of its GitHub Secret Protection program (a subprogram of the GitHub Advanced Security program, or GHAS).GitHub Secret ProtectionGitHub has also created validity checks as part of its GitHub Secret Protection program (a subprogram of the GitHub Advanced Security program, or GHAS).