UNC7017 Used Brief AOMEI Update Tampering to Deliver CROSSROAD and SHINYROAD
Summary
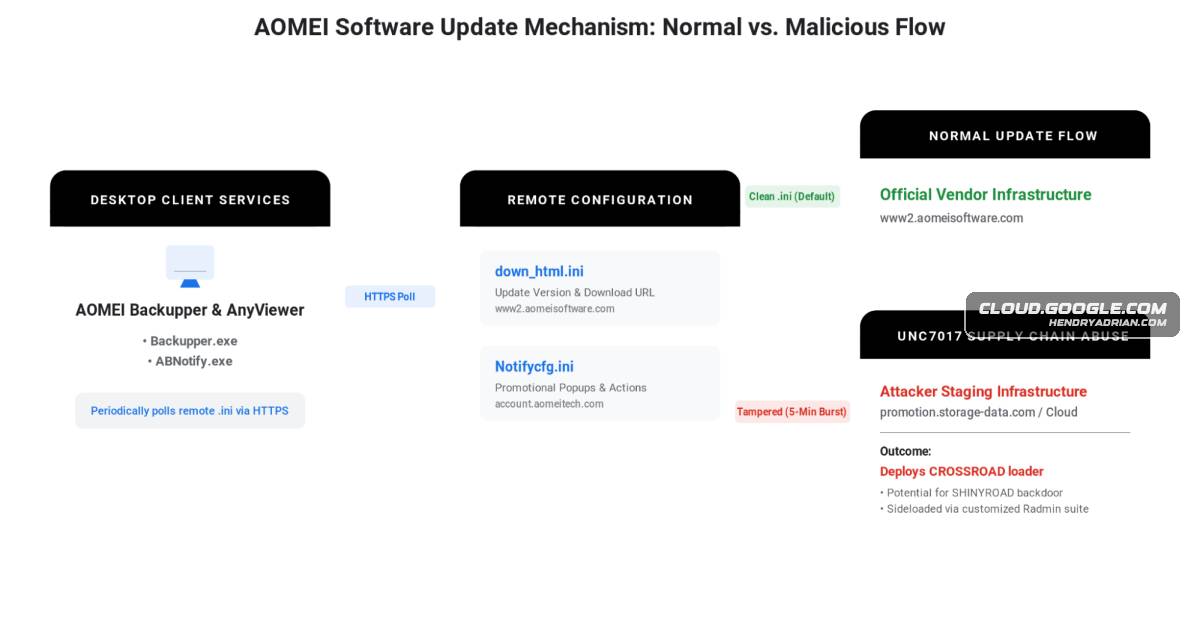
Google Threat Intelligence Group and Mandiant detail UNC7017’s brief tampering of AOMEI update configurations, which redirected some clients to malware and enabled WebDAV NTLM credential coercion. AOMEI says it took corrective action.
Key points
- Investigators observed AOMEI update-server configuration tampering in windows lasting five to ten minutes; affected clients polling during those periods could receive malicious instructions.
- The altered update flow delivered CROSSROAD, which staged SHINYROAD and established persistence through scheduled tasks; later activity included Adaptix C2 disguised as Nitro PDF tools.
- A July 20 notification-file modification used an invisible popup to coerce WebDAV/NTLM authentication to an actor-controlled IP, potentially exposing NetNTLMv2 hashes.
- UNC7017 shifted staging between Alibaba Cloud, actor-controlled domains including promotion[.]storage-data[.]com, and Google Cloud Storage.
- Mandiant says AOMEI reported taking corrective action, but server-side fixes do not remove payloads already installed on endpoints.
- The researchers recommend investigating endpoint artifacts and historical network telemetry, and advise vendors to cryptographically verify updates and configuration files.
Article Details
- Attack Vectors
- UNC7017 briefly tampered with AOMEI update and notification configuration files, redirecting clients that checked during the tampering windows to malicious payloads.
- AOMEI’s notification workflow was abused to execute the downloaded CROSSROAD dropper from the local application directory.
- An invisible popup caused clients to request a remote WebDAV resource, coercing NetNTLMv2 authentication to an attacker-controlled IP address.
- CROSSROAD downloaded the SHINYROAD payload bundle and established scheduled-task persistence; SHINYROAD used DLL search-order hijacking and COM staging.
- Later activity deployed ADAPTAGENT disguised as Nitro PDF software, with a scheduled task launching the payload and periodic C2 beaconing.
- Defensive Notes
- Hunt retrospectively across the April–July 2026 period; restoring vendor update servers does not remove payloads already staged on endpoints.
- Preserve and analyze cached AOMEI configuration files and correlate proxy and firewall telemetry with the precise time of suspicious updater activity rather than relying on live URL checks.
- Monitor updater processes for unsigned child processes, unauthorized network redirection, unsigned DLLs loaded by Radmin binaries, and executions using --runtimechk.
- Inspect for the named RadminComponentRuntime and NitroRuntime scheduled tasks, listed malicious artifacts, and the registry location identified in the article.
- Block the listed attacker infrastructure and restrict outbound SMB and WebDAV traffic to external IP addresses.
- For update systems, verify signatures on downloaded files and remote configuration, pin destinations to approved domains, and disallow file:// and UNC WebDAV schemes in embedded handlers.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | aomei[.]storage-data[.]com | Vendor-themed attacker-controlled domain identified as a SHINYROAD payload staging server. |
| DOMAIN | promotion[.]storage-data[.]com | Attacker-controlled staging domain used to deliver CROSSROAD and SHINYROAD payloads. |
| DOMAIN | serv[.]oss-cn-hongkong[.]aliyuncs[.]com | Alibaba Cloud OSS endpoint used for early CROSSROAD staging, according to the article. |
| DOMAIN | storage-data[.]com | Threat-actor domain used for payload staging and C2-related activity. |
| IPV4 | 47[.]239[.]60[.]117 | Listed as secondary campaign infrastructure and included in the article's outbound-blocking guidance. |
| IPV4 | 8[.]210[.]84[.]56 | Attacker-controlled WebDAV NTLM coercion server and ADAPTAGENT C2 address. |
| IPV4 | 8[.]218[.]65[.]184 | Historical SHINYROAD C2 server, observed on ports 41397 and 443. |
| SHA256 | 11e576df44e9c9eef72b9f5b699291bcdb200a19130778ec231e5b0987b913ad | SHA-256 of the May 20 CROSSROAD upgrade-now.exe loader. |
| SHA256 | 14b31918075e6130b9123158743db0a81e2d7bfcf6d39731ee7d9200a98cd591 | SHA-256 of NitroPromotion.exe, identified as a launcher for ADAPTAGENT masquerading as a Nitro executable. |
| SHA256 | 286e0d8c7bdfaa7c251a3e8f0f2fefbe25c67586c0149d39b1095c89dc6023c8 | SHA-256 of the July 20 tampered Notifycfg.ini used for WebDAV coercion. |
| SHA256 | 4b4d25b3501519476f9a62a88a781e4f446f669280eb5e98c6b96eb6d3743431 | SHA-256 of metadata.dat, the encrypted SHINYROAD payload. |
| SHA256 | 4c0a75e0f62ddc0bb350c224fe996f3b2ab08dcb0d288231c61ffe9406c7045b | SHA-256 of the config.zip Python bytecode archive associated with SHINYROAD. |
| SHA256 | 5837bc26a73cfb46ffd466cf889f03ce2f6a48f1f3fd42ec8be22189d51cab1e | SHA-256 of the malicious BlkScrDl.dll used for SHINYROAD staging. |
| SHA256 | 6670ab3f0434a42f33416f8354150b1701e7615f3cfa2f1635e54f8df0f6eec7 | SHA-256 of the May 20 CROSSROAD upgrade-now.zip archive. |
| SHA256 | 7b252be444dee2fb2a57043a823dc5b5e1fae970aea91ee2c8339aa70329969d | SHA-256 of the identified secondary payload abe.exe. |
| SHA256 | 8c8090aca8ddb1cf968d2b810457e0cfce97c03cd721f70d2eca7f37f2681fc4 | SHA-256 of Eztwain4.dll, identified as the ADAPTAGENT helper DLL. |
| SHA256 | 8fbaa74b27dc1e89abfc694e834378746f0ad37a688098c5f8f511410157c8b8 | SHA-256 of the custom RuntimeComponent.dll PocketPy engine associated with SHINYROAD. |
| SHA256 | 924ad92d89dde577d5858b2ebc5703a485467842d78e98b75019b2e2e0ac3fe6 | SHA-256 of down_html.ini during the July 16 tampering window. |
| SHA256 | 9a58e8f49edf5644e5728f74cf36f560d3d486fa51db4db69d927963c7aca450 | SHA-256 of a July 16 CROSSROAD loader. |
| SHA256 | 9ed503c6a9a3a493fb859401e9ed469eed77ab9927341964d6dbfbfa6255aeba | SHA-256 of the July 20 CROSSROAD upgrade-now.zip archive. |
| SHA256 | b360b6db0c2b668317edc1504a7c39ef047f0d925c8f113b521f6724c157ae21 | SHA-256 of the July 20 CROSSROAD loader. |
| SHA256 | d167bc898e856da8a4003cb4dfc7de55fea109eee3cd64fc8999710314109464 | SHA-256 of the component.zip / en.zip SHINYROAD package. |
| SHA256 | d2f9ef2429312667f0512504b6a19ba4a9cc5514f1b2933923dd42f75a1c5934 | SHA-256 of Notifycfg.ini during the July 16 tampering window. |
| SHA256 | f2a7d0a4c8613a9cdd31ede6131b27040c0571ca97970b245a710191806d7ac4 | SHA-256 of down_html.ini during the July 20 tampering window. |
| URL | hxxps[:]//promotion[.]storage-data[.]com/config/component.zip | Attacker-controlled URL identified as a SHINYROAD payload source. |
| URL | hxxps[:]//promotion[.]storage-data[.]com/config/en.zip | Attacker-controlled URL identified as a Stage-3 SHINYROAD payload source. |
| URL | hxxps[:]//promotion[.]storage-data[.]com/config/whitelist.ini | Attacker-controlled endpoint used to provide the target IP allowlist. |
| URL | hxxps[:]//promotion[.]storage-data[.]com/download/abpopup/upgrade-now.zip | Attacker-controlled URL used to deliver the CROSSROAD archive. |
| URL | hxxps[:]//storage[.]googleapis[.]com/aomeiupdate/component.zip | Specific Google Cloud Storage URL identified as a July 20 component staging resource. |
| URL | hxxps[:]//storage[.]googleapis[.]com/aomeiupdate/upgrade-now.zip | Specific Google Cloud Storage URL identified as the July 20 CROSSROAD staging resource. |
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryCROSSROAD queried external DNS and HTTP reflection services to determine the host's external IP address.T1036.005 · Match Legitimate Resource Name or LocationBlkScrDl.dll imitated a Radmin driver library, while ADAPTAGENT payloads used Nitro PDF-themed filenames and DLL names.T1053.005 · Scheduled TaskCROSSROAD created the RadminComponentRuntime scheduled task; later activity also used the NitroRuntime task.T1059.001 · PowerShellThe NitroRuntime task ran a hidden PowerShell command to start NitroPromotion.exe.T1059.006 · PythonRuntimeComponent.dll executed compiled Python bytecode using an embedded PocketPy interpreter.T1070.004 · File DeletionCROSSROAD used a child process with the --nitrod parameter to remove its original executable.T1105 · Ingress Tool TransferCROSSROAD downloaded component.zip or en.zip and unpacked the payload bundle into the user's local application data directory.T1187 · Forced AuthenticationAn invisible popup rendered a UNC WebDAV resource, coercing clients to send NetNTLMv2 authentication hashes to 8.210.84.56.T1195.002 · Compromise Software Supply ChainUNC7017 briefly altered AOMEI remote update and notification configuration files to redirect clients to malicious payloads.T1559.001 · Component Object ModelBlkScrDl.dll registered RuntimeComponent.dll as an in-process COM server, which was loaded when Radmin instantiated the registered CLSID.T1564.004 · NTFS File AttributesBefore deletion, CROSSROAD renamed the executable's primary data stream to the alternate data stream :wtfbbq.T1571 · Non-Standard PortSHINYROAD used raw TCP C2 on port 41397, and ADAPTAGENT beaconed to port 6800.T1573.001 · Symmetric CryptographySHINYROAD encrypted its custom C2 traffic using a hard-coded handshake key and then a symmetric key derived from the agent ID.T1574.001 · DLLThe signed Radmin executable loaded the unsigned BlkScrDl.dll through search-order hijacking; Nitro-themed executables also sideloaded Eztwain4.dll.T1614 · System Location DiscoveryCROSSROAD used the IP-derived country code and aborted its primary payload path when the code was CN.
Threat Actors
Malware
ADAPTAGENTIn mid-July 2026, following the successful deployment of SHINYROAD, telemetry identified later-stage activity where UNC7017 pushed down ADAPTAGENT, the client portion of the Adaptix C2 post-exploitation framework.CROSSROADThe campaign delivered a multi-stage payload chain involving the newly tracked CROSSROAD downloader and SHINYROAD backdoor.SHINYROADThe campaign delivered a multi-stage payload chain involving the newly tracked CROSSROAD downloader and SHINYROAD backdoor.
Vendors
Alibaba CloudEarly Cloud Staging (April–May 2026): Early CROSSROAD payloads (upgrade-now.exe observed May 20) relied on Alibaba Cloud Object Storage (serv.oss-cn-hongkong.aliyuncs.com).AOMEI TechnologyGoogle Threat Intelligence Group (GTIG) and Mandiant investigated a software supply chain compromise campaign targeting the update infrastructure belonging to AOMEI Technology between April 2026 and July 2026.FamatechThe payload archive unpacked into %LOCALAPPDATA%\Radmin\ by CROSSROAD contains a Famatech Radmin 3.x administration bundle used to deliver the SHINYROAD modular backdoor framework.Google Cloudon July 20, the threat actor modified down_html.ini to direct initial client downloads to a public Google Cloud Storage bucket (storage.googleapis.com/aomeiupdate/upgrade-now.zip) rather than storage-data.com.Nitro Software$camo_copy = "Nitro Software, Inc." ascii wide
Products
ABMarketUsers of these products rely on the ABMarket update flow and its associated background services (Backupper.exe and ABNotify.exe) that periodically poll remote endpoints over HTTPS for update notifications andAnyViewerAOMEI Backupper provides data backup, disk cloning, and disaster recovery, while AnyViewer facilitates remote desktop access and support.AOMEI BackupperAOMEI Backupper provides data backup, disk cloning, and disaster recovery, while AnyViewer facilitates remote desktop access and support.Nitro PDFPost-Exploitation: Nitro PDF Theme & Adaptix C2Radmin ServerModified Radmin Server Backdoor: During the May 28 wave, the unsigned loader dropped into the html/ directory executed rsetup64.exe /intsetup, silently installing a modified version of the commercial remote
Tools
Countries
Australiadiverse sectors, including IT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and theBrazilsectors, including IT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.Indiaincluding IT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.PakistanIT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.Portugaltelecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.Singaporehigher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.South Africahigher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.Spaineducation and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.Switzerlandand related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.United StatesBrazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States.
Industries
Higher Educationimpacted organizations spanned diverse sectors, including IT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa,IT servicesBased on available telemetry, impacted organizations spanned diverse sectors, including IT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore,TelecommunicationsBased on available telemetry, impacted organizations spanned diverse sectors, including IT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore,