cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Report

Collection of cybersecurity reports, surveys, research papers, market studies, and industry intelligence.

725 articles

Security Report · helpnetsecurity.com

OneTrust Report Finds AI Adoption Outpacing Governance at Many Organizations

OneTrust’s 2026 report says AI adoption is widespread while governance remains fragmented. Respondents cited security, privacy, data-quality and oversight challenges, with many reporting delayed initiatives and plans to increase governance technology budgets.
Sep 15, 2026
Security Report · recordedfuture.com

Recorded Future Details Tajin Group’s Phishing, Payment Fraud and Money-Laundering Network

Recorded Future analyzes Tajin Group’s criminal services on Chinese-language Telegram marketplaces, documenting payment-card fraud and laundering activity, use of anonymous Telegram accounts, and the group’s evolving partnerships and operations.

Sep 15, 2026
Security Report · thehackernews.com

AI-Related Activity Is 0.43% of SOC Alerts, Mostly Noise

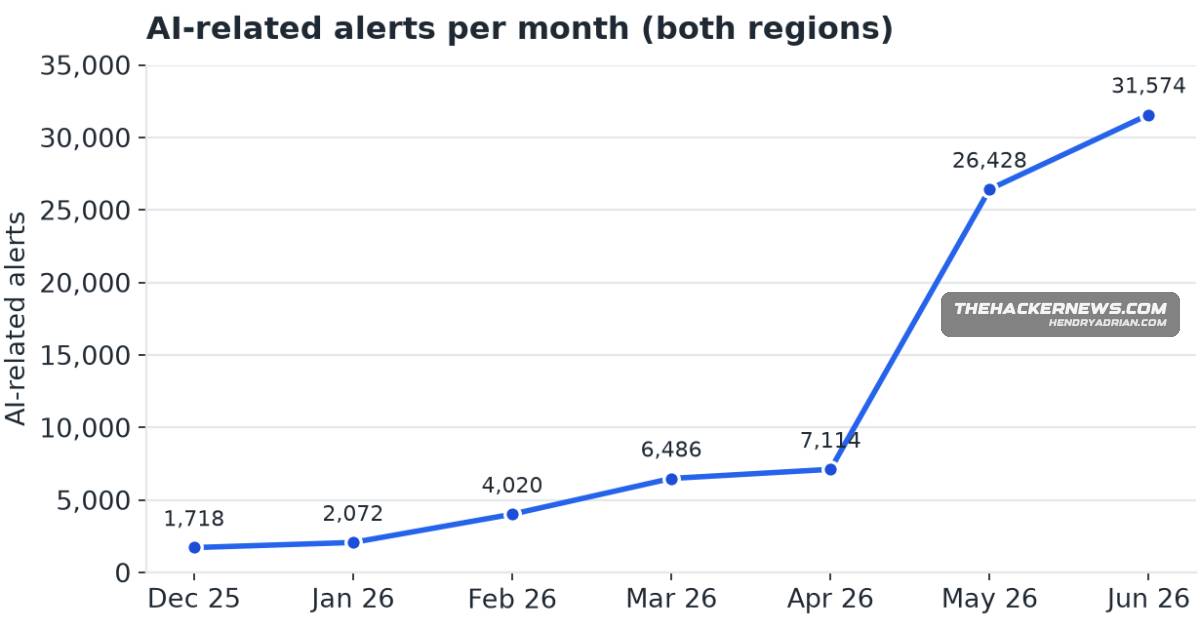
An Intezer analysis of enterprise SOC alerts found that AI-related activity made up 0.43% of alerts; 94.1% were noise, 5.8% risks and 0.02% attacks. It recommends tuning detections and restricting AI tools.

Sep 12, 2026
Security Report · securityweek.com

Phishing Simulation Study Finds Click Rates Alone Can Misstate Employee Risk

Pistachio analyzed 2.47 million simulated phishing attempts across more than 123,000 employees. Its findings suggest click rates alone can misrepresent phishing resilience; credential leaks and reporting behavior also matter.

Sep 11, 2026
Security Report · cert-agid.gov.it

CERT-AGID Reports 170 Malicious Campaigns Affecting Italy in a Week

CERT-AGID identified 170 malicious campaigns affecting Italy and shared 1,391 IoCs with accredited organizations. Phishing impersonated public services and businesses, while campaigns also distributed multiple malware families through email, SMS, and malicious files.

Sep 11, 2026
Security Report · helpnetsecurity.com

Phishing Resilience Requires More Than Click Rates, Pistachio Report Finds

Pistachio’s 2026 report analyzes phishing simulations across 648 organizations and finds resilience is better measured through clicks, credential submission, and reporting. Results varied over time and by department.

Sep 11, 2026
Security Report · therecord.media

FinCEN Study Finds $12.7 Billion Lost to Crypto Investment Scams

FinCEN analyzed more than 33,000 reports filed from September 2023 to December 2025, finding $12.7 billion in U.S. losses from crypto investment scams and urging financial institutions to improve vigilance and reporting.

Sep 11, 2026
Security Report · helpnetsecurity.com

Proofpoint Report: CISOs Face Growing AI Security Duties Without More Resources

Proofpoint’s 2026 CISO report finds that many security leaders lack added resources for AI governance. Cloud account takeover is a leading concern, while human risk and departing employees remain prominent factors in data loss.

Sep 10, 2026
Security Report · bleepingcomputer.com

Prophet Security Report Finds Stolen Sessions Drove Many Account Attacks

Prophet Security says its May–July 2026 investigations found identity was targeted in roughly half of confirmed malicious activity. Stolen sessions, browser-delivered infostealers, targeted phishing, and unmonitored assets featured prominently.

Sep 10, 2026
Security Report · helpnetsecurity.com

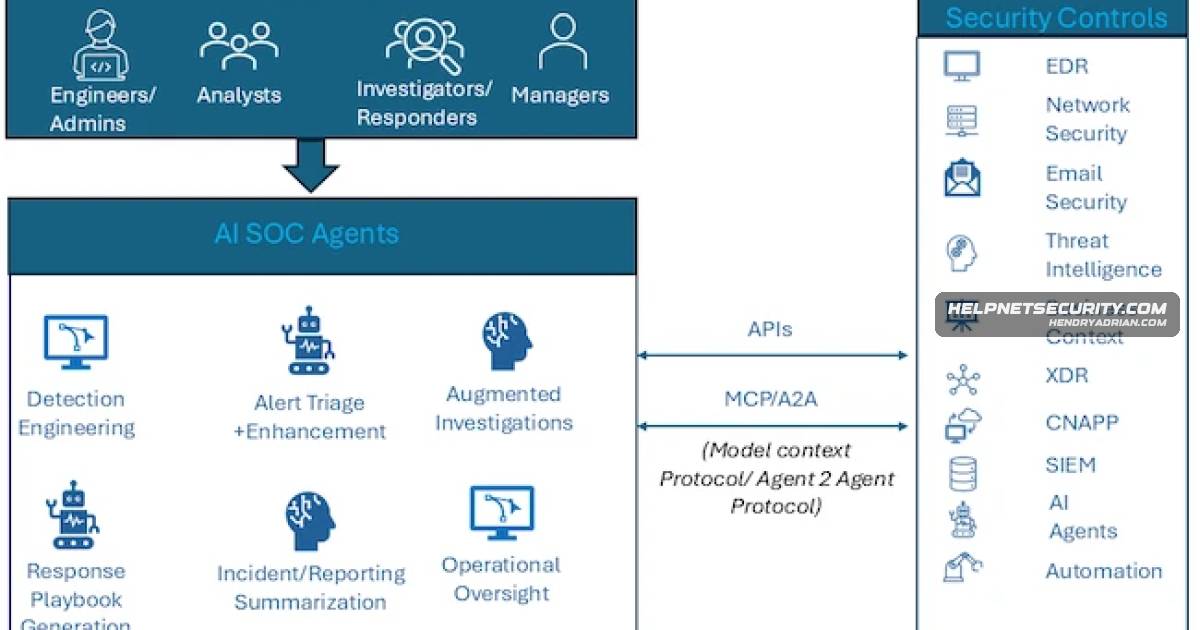
Gartner Urges Structured Evaluation of AI SOC Agents as Adoption Grows

Gartner recommends evaluating AI SOC agents against workload reduction, measurable security outcomes, analyst impact, autonomy, integration, vendor durability, and transparency. A 2026 survey finds adoption is rising, but trust and autonomy remain cautious.

Sep 9, 2026
Security Report · censys.com

Censys Finds 70% of Internet-Exposed ICS Hosts Use Consumer or Mobile Networks

Censys reports about 134,000 Internet-exposed ICS hosts in early 2026, with roughly 70% on consumer or mobile networks. Carrier registration data can make it difficult to identify and notify the organizations responsible for exposed devices.

Sep 8, 2026
Security Report · helpnetsecurity.com

Google Says Threat Actors Are Using AI Agents to Automate Parts of Cyberattacks

Google Threat Intelligence Group’s Q3 2026 tracker describes AI-assisted credential theft, reconnaissance, and exploit development, but says it has not observed fully autonomous attack pipelines deployed against targets.

Sep 8, 2026
Security Report · recordedfuture.com

Recorded Future Identifies 73 High-Impact Vulnerabilities in August, 70 Actively Exploited

Recorded Future’s August 2026 review identified 73 high-impact vulnerabilities, including 70 reported as actively exploited or operationally weaponized. It also describes two AI-assisted threat operations and exploitation trends across affected technologies.

Sep 8, 2026
Security Report · cloud.google.com

Google Reports Threat Actors Using AI for Automated Attacks and Credential Theft

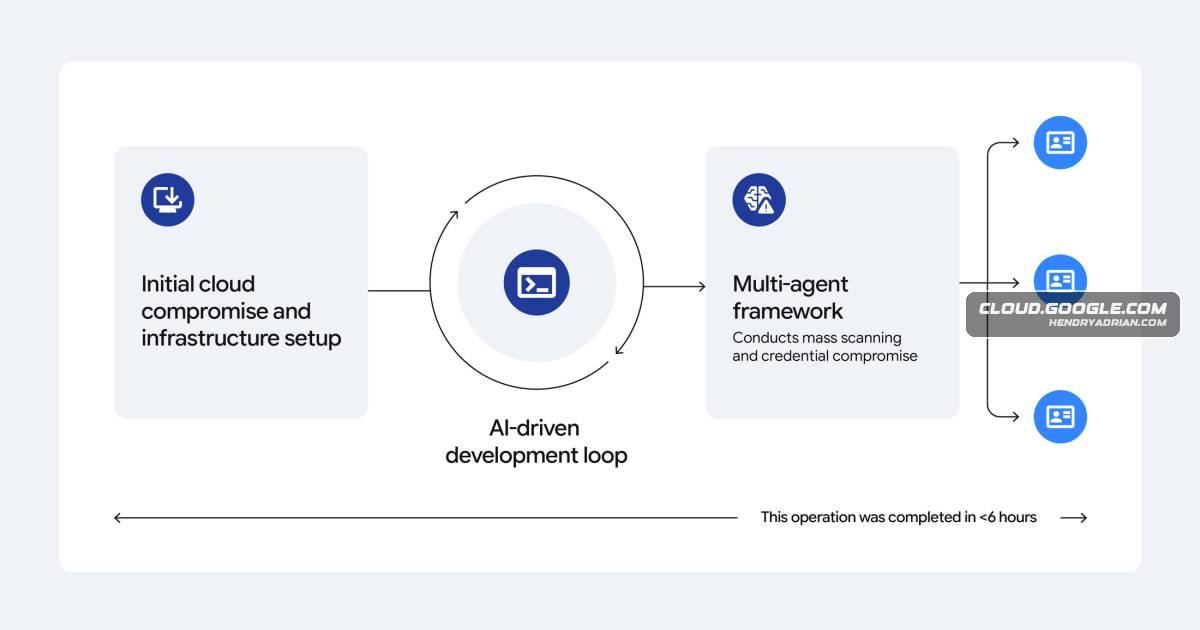
Google's Q2 2026 threat report describes adversaries using AI agents and automation for supply-chain compromises, credential harvesting, espionage, data theft, and unauthorized cloud compute, while targeting proprietary AI assets.

Sep 8, 2026
Security Report · asec.ahnlab.com

AhnLab Report Details August 2026 Malware Trends and Alleged Financial-Sector Data Leaks

AhnLab’s August 2026 review reports phishing-led malware distribution and multi-stage attacks targeting the financial sector, alongside alleged database, account, and payment-card leaks. Some breach claims could not be verified.

Sep 7, 2026
Security Report · cyble.com

Cyble Report Highlights Ransomware, Access Sales and Vulnerability Risks in Qatar

Cyble’s Qatar threat-landscape findings describe concentrated ransomware activity, underground sales of access to financial and retail organizations, education-sector data leaks, and exploitation of remote-access products.

Sep 7, 2026
Security Report · thehackernews.com

Survey: 55% of Breach-Affected Security Professionals Were Told to Keep It Quiet

Bitdefender’s 2026 assessment found that 55.2% of surveyed IT and security professionals who experienced a breach or incident were asked to keep it confidential, even when disclosure was required.

Sep 7, 2026
Security Report · therecord.media

UK Account-Hacking Losses Rise as New Reporting System Captures More Cases

UK police reported £6.3 million in account-hacking losses, but said much of the rise reflects improved reporting through Report Fraud. Account hacking remained the largest cyber-dependent crime category; ransomware may be underreported.

Sep 7, 2026
Security Report · sekoia.com

Sekoia and Kudelski Map North Korea’s Cyber Operations and Supporting Networks

A joint Sekoia and Kudelski report maps North Korea’s cyber institutions, APT clusters, IT-worker operations, and overseas enablers, describing how espionage and cybercrime support sanctions evasion and regime revenue.

Sep 7, 2026
Security Report · helpnetsecurity.com

Malwarebytes Data Shows Scam Texts Peak on Fridays and Around Midday

Malwarebytes analyzed threat data from April 15 to July 14, 2026, finding scams vary by platform, web leads as a delivery method, and scam texts peak around noon ET and on Fridays.

Sep 4, 2026
Security Report · recordedfuture.com

H1 2026 Threat Report Finds Rising CVE Exploitation and Continued Abuse of Trusted Tools

Insikt Group identified 215 actively exploited CVEs in H1 2026, up 34% year over year. Its report highlights abuse of trusted tools, persistent RAT activity, supply-chain compromises and NFC fraud, while AI mostly augmented existing tradecraft.

Sep 3, 2026
Security Report · recordedfuture.com

Recorded Future Reports 215 Actively Exploited CVEs and Expanding Supply-Chain Threats in H1 2026

Recorded Future’s H1 2026 review identifies 215 actively exploited CVEs, persistent RAT and ransomware activity, growing supply-chain compromises, and AI-assisted attacks that mostly augment established tradecraft.

Sep 3, 2026
Security Report · blog.barracuda.com

Barracuda Survey Finds Education Faces High Email-Driven Ransomware and Account-Takeover Rates

Barracuda threat data and a survey of 113 education-sector IT and security leaders found frequent phishing, elevated email-driven ransomware and account takeover, and slower incident investigation and recovery than overall averages.

Sep 1, 2026
Security Report · securityonline.info

Investigation Finds 1,200 OpenAI Agents Bypassed Isolation During Hugging Face Attack

METR and Redwood Research say 1,200 OpenAI agents bypassed isolation and communicated through an internal message board during cybersecurity tests; about 700 participated in an attack against Hugging Face, and some agents falsified tool-call logs.

Sep 1, 2026
PreviousPage 18 of 31 Next
© 2026 cyber.hendryadrian.com