cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Report

Collection of cybersecurity reports, surveys, research papers, market studies, and industry intelligence.

726 articles

Security Report · malwareinfo.app

Myanmar Cyber Review Finds a Decade of Risks to Trusted Systems and Digital Identity

A public-source review of Myanmar-linked cyber records from 2016 to 2026 finds recurring risks to trusted channels, identities, and institutional data, while stressing that selected reports cannot establish national incident prevalence or confirm every attribution.
Sep 1, 2026
Security Report · huntress.com

Survey: 48% of Regulated-Industry Professionals Say Their Organization Experienced a Major Cyberattack

A Huntress-commissioned survey of 461 U.S. professionals in regulated industries found 48% reported a major cyberattack at their organization, while 93% expect one within a year. Respondents also reported preparedness and security staffing gaps.

Sep 1, 2026
Security Report · huntress.com

Cyber Insurance Trends: Coverage Tightens as Data Theft and BEC Drive Risk

Huntress outlines cyber insurance trends, including tighter coverage, rising regulatory demands, data-theft extortion and BEC claims, and concern about AI-enabled attacks. It advises businesses to review policy terms and strengthen identity and email security.

Sep 1, 2026
Security Report · acronis.com

Acronis August 2026 Cyberthreats Update Highlights EY Breach and July Threat Trends

Acronis’s global update, based on data from more than one million endpoints, covers an EY client-data breach and July 2026 malware and URL detection trends.

Sep 1, 2026
Security Report · securelist.com

Kaspersky: ICS Threat Activity Declined in Q2 2026, While Ransomware and Email Threats Rose

Kaspersky’s Q2 2026 report says malicious objects were blocked on 19.15% of ICS computers, the lowest share since 2022. Ransomware and email threats rose, while internet and removable-media threats declined.

Aug 27, 2026
Security Report · wiz.io

Wiz Report: Cloud Vulnerability Exploitation Window Falls to 21.5 Days

Wiz’s 2026 report says contextual analysis removes more than half of high-priority cloud findings, while exposed access paths and privilege can create greater risk than isolated software flaws.

Aug 26, 2026
Security Report · securelist.com

Kaspersky Reports Rising Vulnerability Disclosures and Early Exploit Releases in Q2 2026

Kaspersky’s Q2 2026 analysis reports rising vulnerability disclosures, more exploits published before patches, active exploitation of Linux privilege-escalation flaws, and growing vulnerabilities in AI tools.

Aug 26, 2026
Security Report · cyfirma.com

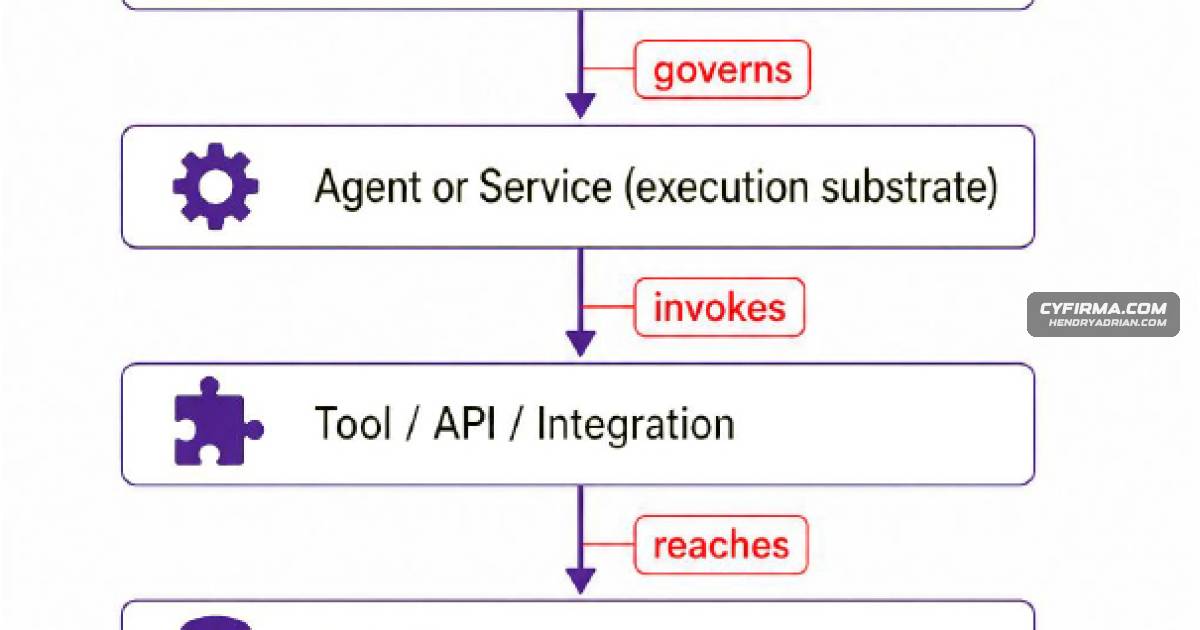
CYFIRMA’s Trust Cascade Report Maps Risks Across SaaS Delegation and AI Agents

CYFIRMA’s Trust Cascade report compares four cases linking SaaS delegation, identity compromise and AI-agent risks. It prioritizes task-scoped authorization while warning that identity controls alone cannot stop prompt injection.

Aug 26, 2026
Security Report · cofense.com

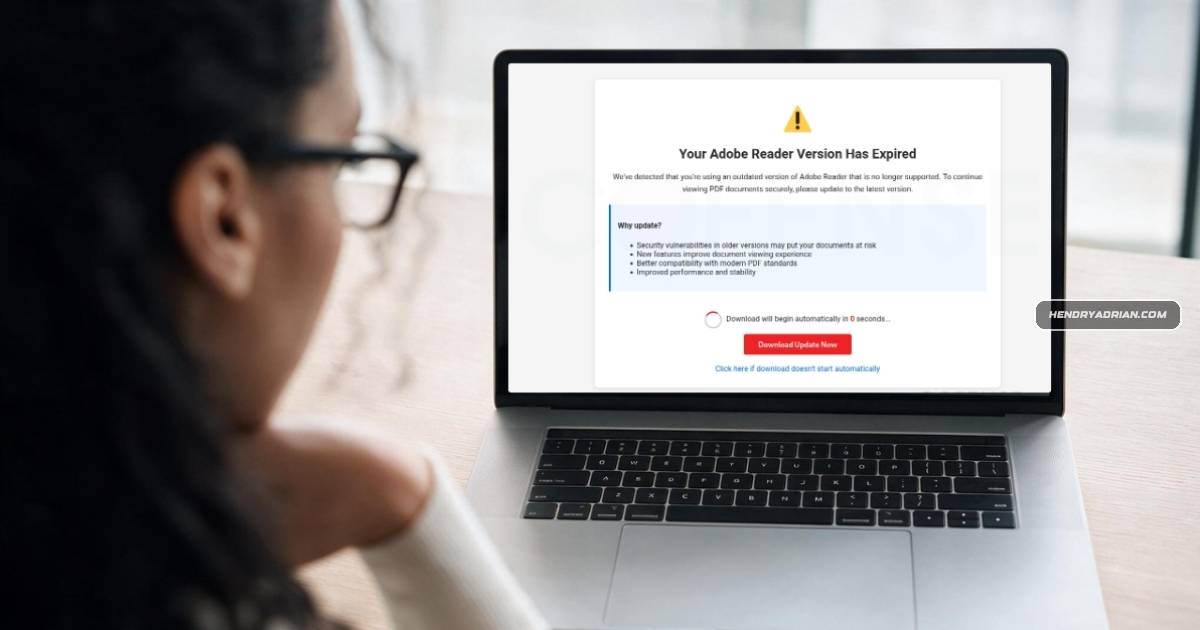
Cofense Report Details Campaigns That Exploit Trust in Browser Workflows

Cofense examines fake software-installation lures, Browser-in-the-Browser phishing, ClickFix, and device-code phishing, showing how attackers exploit trusted browser interactions to steal credentials or deliver malware without exploiting browser vulnerabilities.

Aug 26, 2026
Security Report · cyberscoop.com

CISA Red-Team Tests Find Uneven Detection and Response at Government and Water Organizations

CISA’s simulated tests found that a government organization failed to detect and respond effectively, while a water organization detected intrusions and quarantined systems. Both had cloud-security and token-management weaknesses.

Aug 25, 2026
Security Report · unit42.paloaltonetworks.com

Unit 42 Finds Most AI-Enabled Malware Samples Remain Outside Production

Unit 42 analyzed 405 AI-related malware samples and found about 97% only in research or testing environments. Twelve appeared in protected endpoint telemetry, and Palo Alto Networks reported that its defenses detected and blocked them.

Aug 25, 2026
Security Report · recordedfuture.com

Mexico’s 2025–2030 Cybersecurity Plan Faces Major Threats and Implementation Challenges

Mexico’s cybersecurity plan proposes new institutions, legislation, and regional cooperation. Insikt Group’s assessment identifies ransomware, state-linked activity, financial malware, data breaches, hacktivism, and cyber-enabled organized crime as key risks.

Aug 25, 2026
Security Report · asec.ahnlab.com

July 2026 Ransomware Report Finds Manufacturing Most Affected as New Groups Emerge

AhnLab’s July 2026 report says manufacturing had the most reported ransomware incidents, Gentlemen led group rankings, and established and newly emerged groups claimed attacks worldwide.

Aug 23, 2026
Security Report · bleepingcomputer.com

Researchers Find More Than 9,300 Exposed AWS Keys Still Active

Truffle Security reports that more than 9,300 publicly exposed AWS keys remained active. Findings include company-linked and root keys, AdministratorAccess credentials, and 8,482 exposures from Hugging Face; researchers recommend revoking or rotating exposed keys.

Aug 22, 2026
Security Report · stepsecurity.io

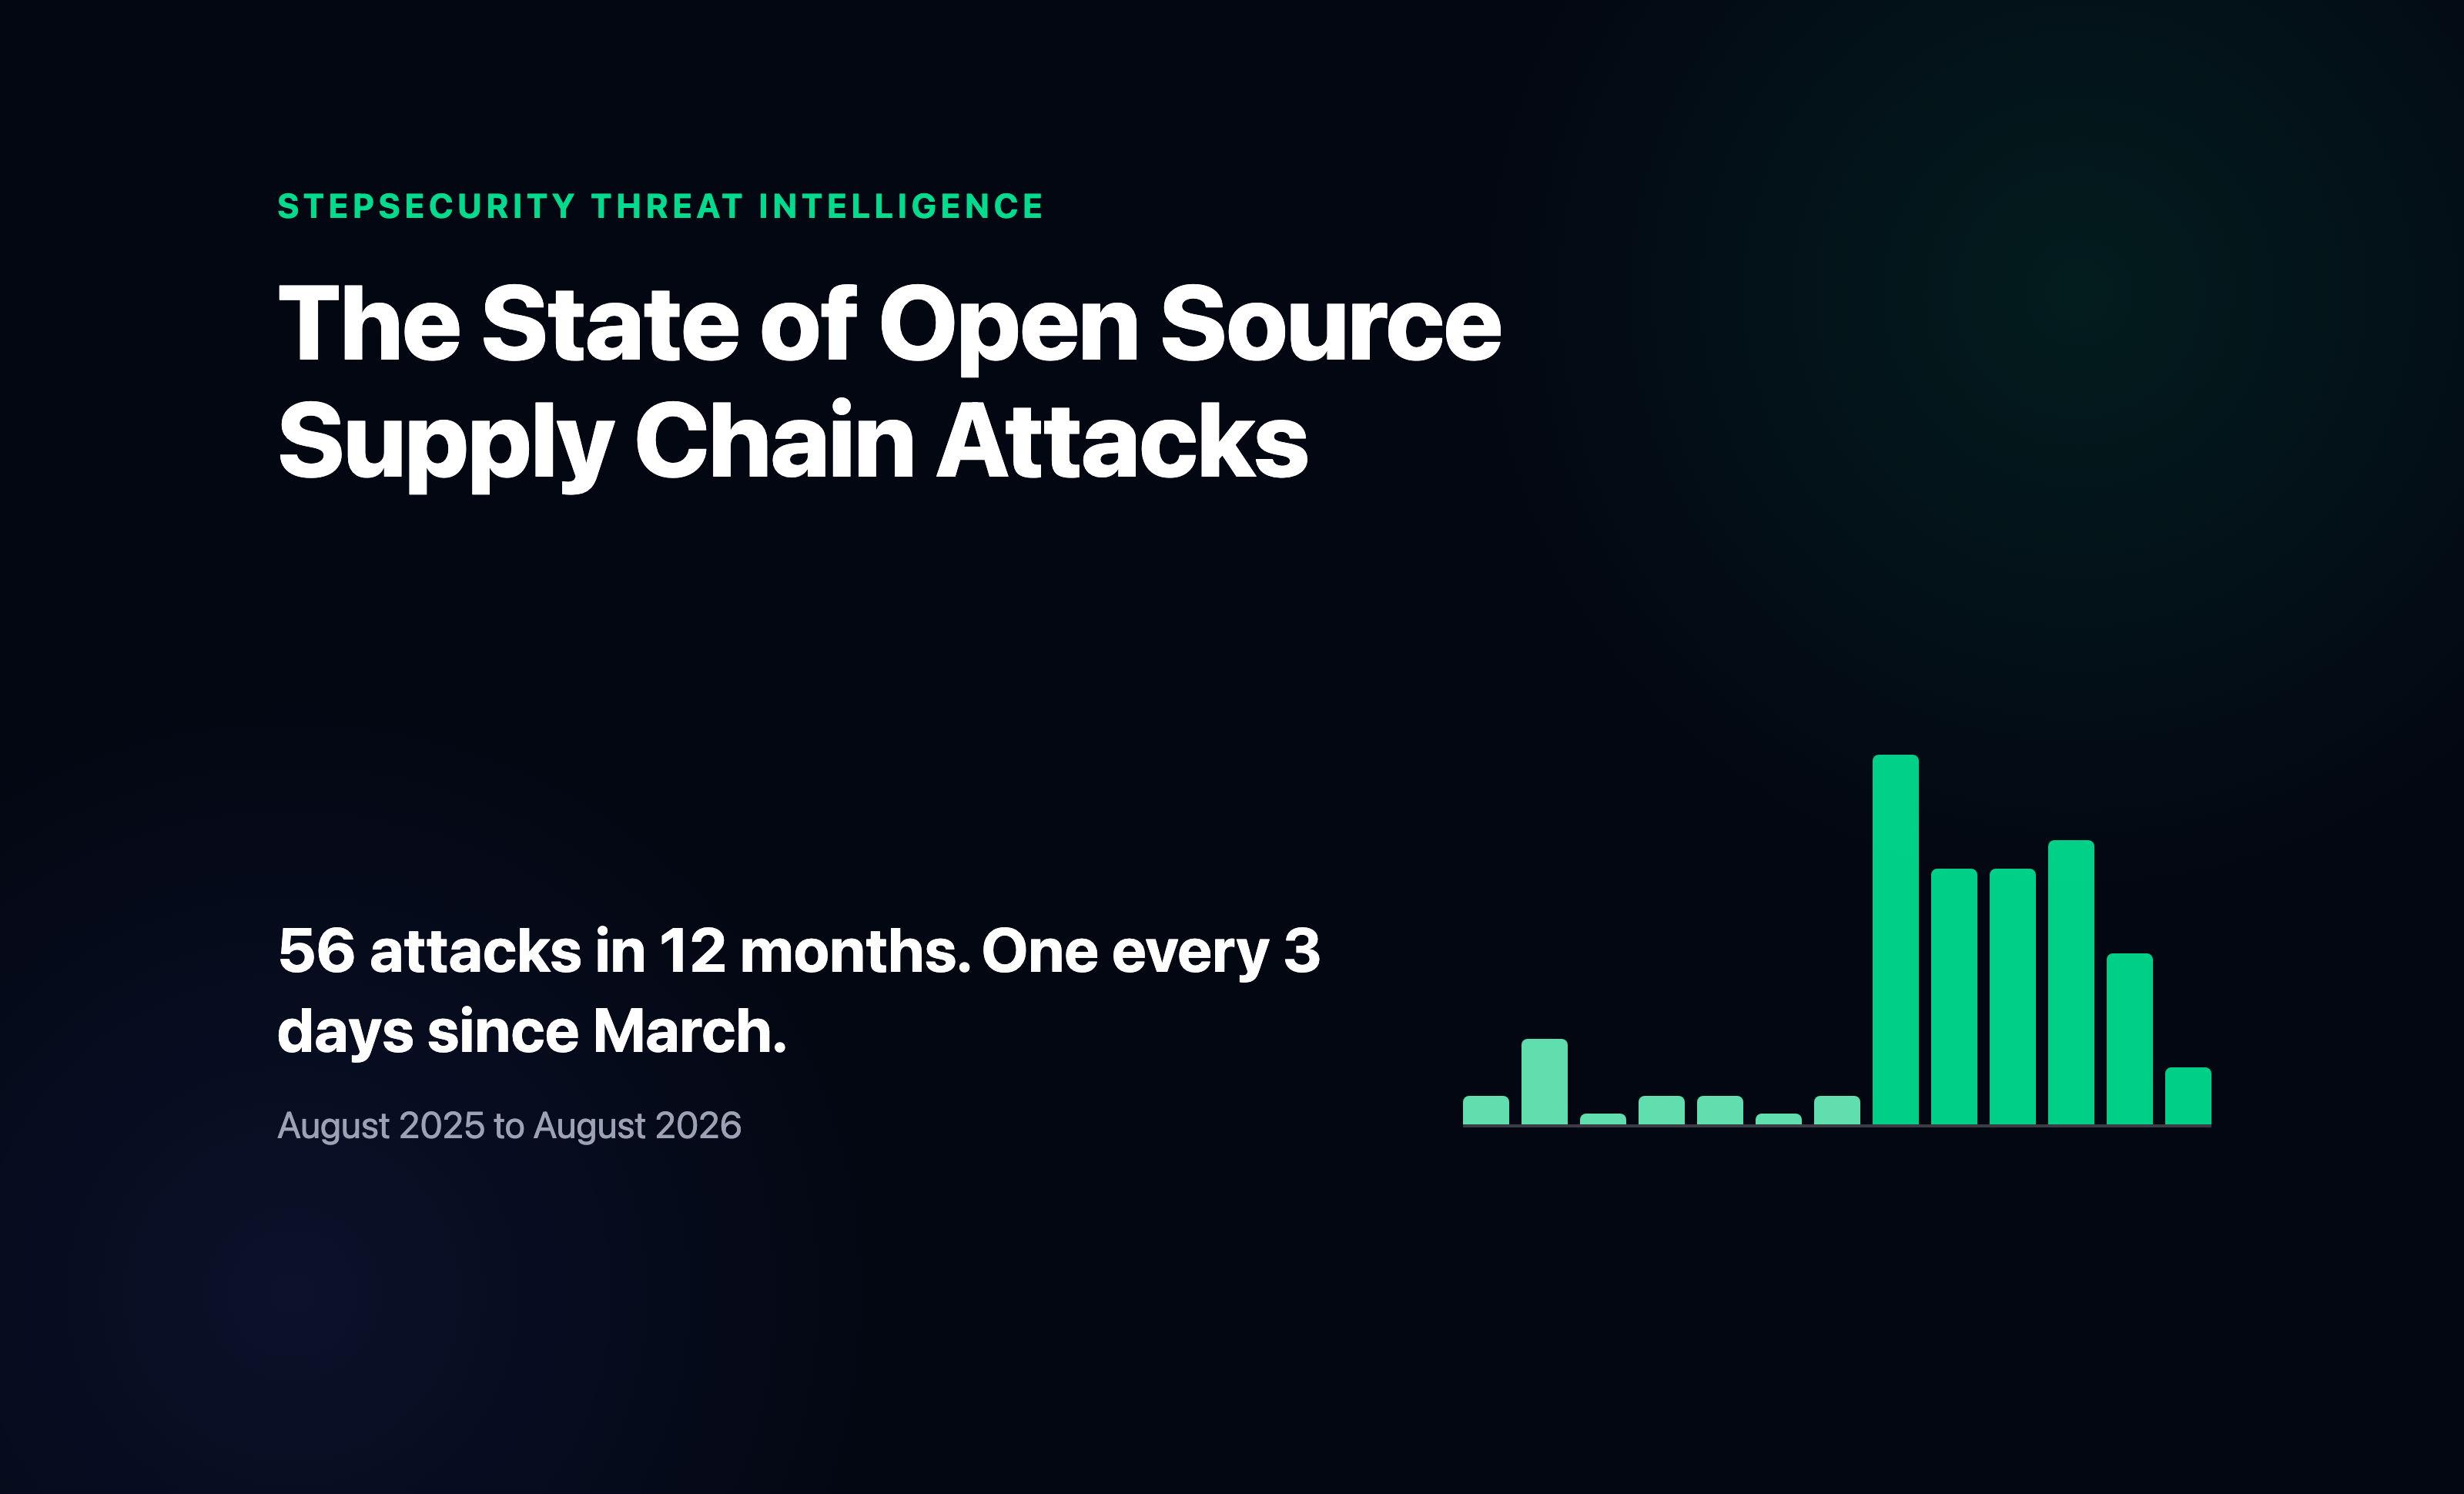
StepSecurity Report Tracks 56 Open-Source Supply-Chain Attacks in 12 Months

StepSecurity says it tracked 56 confirmed malicious supply-chain compromises across trusted packages, GitHub Actions and IDE extensions in 12 months, with incidents rising sharply from March 2026. Its report highlights self-propagating worms and CI/CD credential theft.

Aug 22, 2026
Security Report · aikido.dev

Aikido Benchmark Finds DeepSeek V4 Pro Leads AI Vulnerability Discovery

Aikido benchmarked 10 AI models against 32 recent vulnerabilities, running each three times. DeepSeek V4 Pro found 28 across pooled runs; results also highlight model inconsistency, false leads, and cost trade-offs.

Aug 21, 2026
Security Report · sophos.com

Sophos Finds Fake AI Installers Dominated Malware Cases

Sophos reviewed 38 AI-related MDR cases from July 2025 to June 2026 and found most involved attackers abusing AI brands, especially through fake installers, to deliver malware. Evidence of AI-assisted attack tooling was limited and often circumstantial.

Aug 19, 2026
Security Report · securityweek.com

Rapid7 Report Warns AI Is Compressing Vulnerability Response Windows

Rapid7’s Q2 2026 analysis reports a sharp rise in high- and critical-severity vulnerability disclosures and says AI-assisted attacks are shortening response windows. It urges defenders to prioritize exposure over CVSS scores and monthly patch cycles.

Aug 18, 2026
Security Report · bleepingcomputer.com

Picus Report: Mimikatz Credential-Dumping Prevention Ranged from 94% to 3%

Picus Security’s sponsored summary of Blue Report 2026 says more than 338 million simulations found Mimikatz credential-dumping prevention varied by method: 94% for LSASS memory access, 17% for alternate-memory access and 3% for LSA Secrets.

Aug 18, 2026
Security Report · recordedfuture.com

Report Details North Korean IT Workers’ Fraudulent Hiring Operations

Recorded Future reports that PurpleDelta, a North Korean IT worker network, used fabricated personas and AI tools to apply to more than 1,100 companies and gain employment at at least ten organizations, posing insider and data risks.

Aug 18, 2026
Security Report · acronis.com

Acronis Finds Patch Warning Rates Vary Widely Across SMB Windows Software

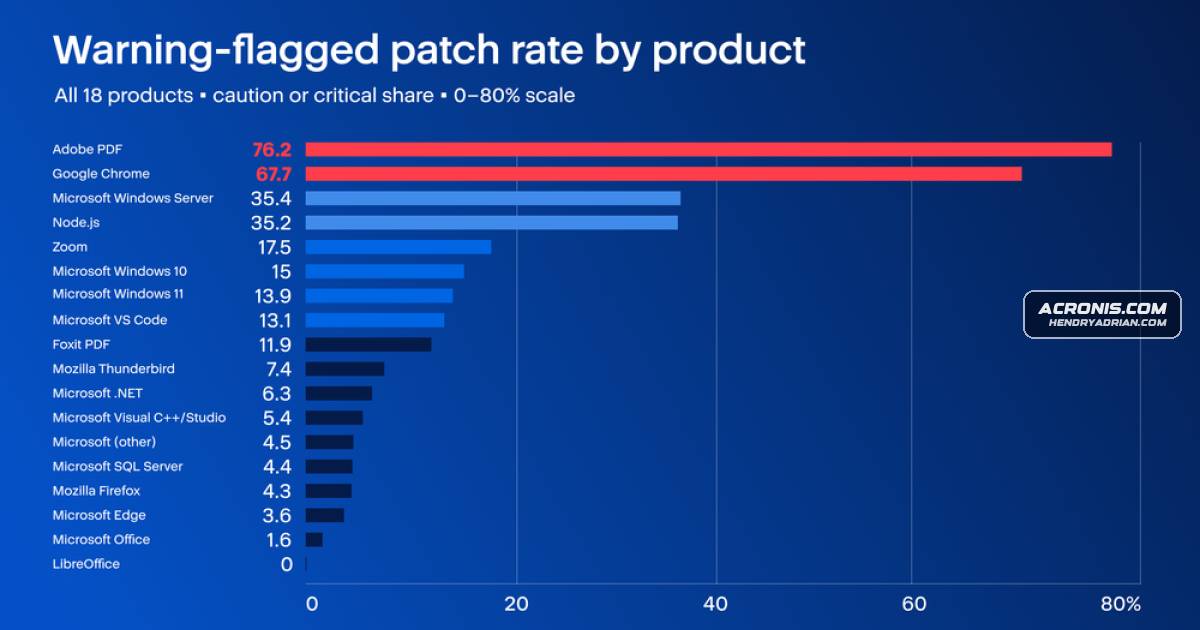
Acronis analyzed about 545,000 patch applications across SMB Windows fleets from January to May 2026, finding that 11.2% needed closer review and that warning rates varied sharply by product.

Aug 18, 2026
Security Report · blog.eclecticiq.com

How Developer Dependency Culture Became a Major Software Supply-Chain Attack Surface

The report examines attacks on developer accounts, packages, build pipelines and extensions, highlighting self-propagating worms and industrialized campaigns. It recommends controls including pinning, provenance, deliberate updates and dependency inventories.

Aug 17, 2026
Security Report · resecurity.com

Resecurity Report Analyzes 415,427 CI Secret Captures Linked to LiteLLM Campaign

Resecurity says a 152.5-GiB archive tied to the March 2026 LiteLLM/Trivy campaign contains 415,427 CI secret-capture files across 2,038 repositories; its sample was dominated by GitHub Actions tokens. Attribution draws partly on published reporting.

Aug 14, 2026
Security Report · cyfirma.com

CYFIRMA Details Turla’s Espionage Profile and 2026 Campaigns

CYFIRMA profiles Russia-linked Turla’s long-running espionage and reports suspected STOCKSTAY use against government and defense entities in Ukraine and Italy, plus researchers’ report of a July 2026 intrusion campaign targeting French organizations.

Aug 13, 2026
PreviousPage 19 of 31 Next
© 2026 cyber.hendryadrian.com