cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3800 articles

Security News · thehackernews.com

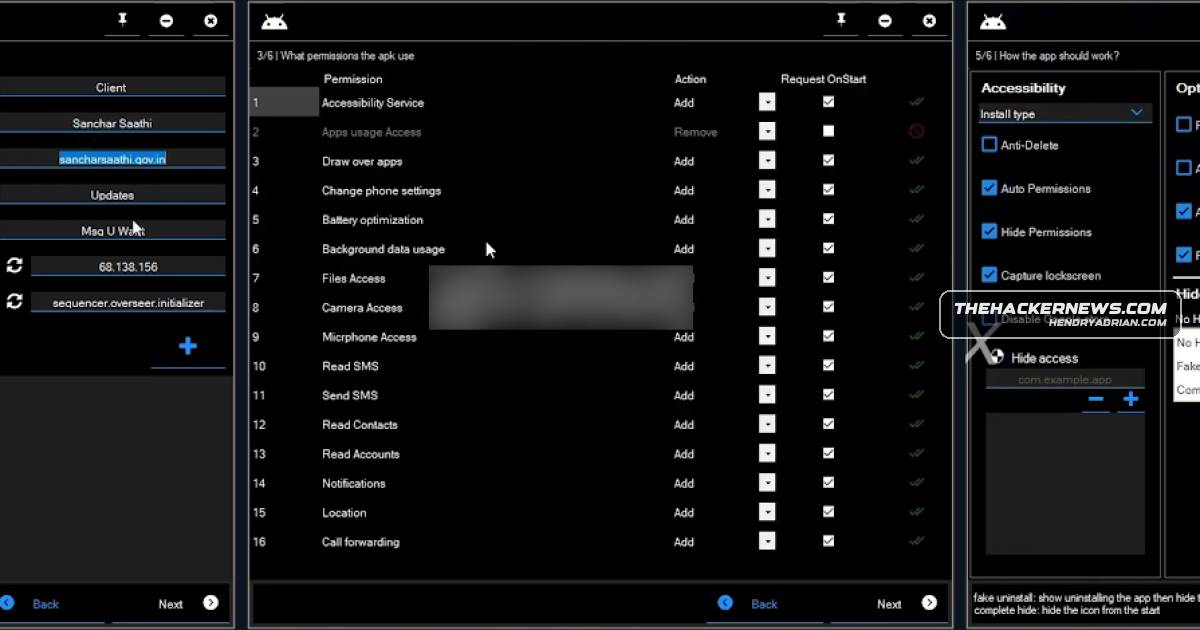
Grandoreiro and BTMOB Campaigns Target Windows and Android Users

WatchGuard and ESET report active Grandoreiro and BTMOB campaigns targeting organizations and users in Europe and Latin America, using phishing, DLL side-loading, WebRTC-related communications and Android accessibility services to steal financial data and enable remote.
May 28, 2026
Security News · esentire.com

OMB Memo M-26-14 Replaces Federal Logging Mandate With Risk-Based Approach

OMB’s M-26-14 replaces the prior federal logging mandate with separate priorities for real-time monitoring and deeper forensic retention. CISA is directed to issue a Logging Reference Architecture within 90 days; eSentire also promotes its logging services.

May 28, 2026
Security News · cert-agid.gov.it

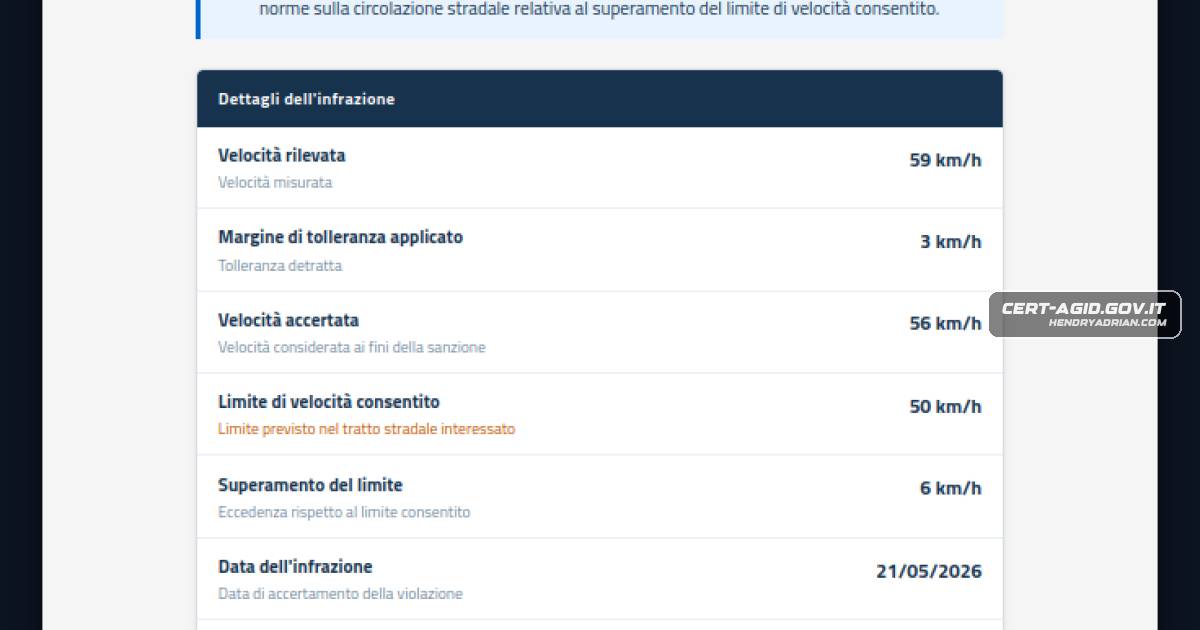
CERT-AGID Warns of SEND-Themed Phishing Targeting PagoPA Users

CERT-AGID reports email and SMS phishing impersonating SEND and PagoPA, directing users to fake traffic-fine payment pages to steal credit card details. It is coordinating takedowns and sharing related indicators.

May 27, 2026
Security News · cyberscoop.com

GCHQ Chief Warns AI Is Reshaping Cyber Offense and Defense

GCHQ chief Anne Keast-Butler warned that AI is changing cyber offense and defense, describing GCHQ’s development of defensive capabilities integrated with agentic AI and citing growing AI-enabled risks from China and Russia.

May 27, 2026
Security News · cyberscoop.com

FBI Warns U.S. Law Firms About Silent Ransom Group’s In-Person Data Theft

The FBI warned that Silent Ransom Group targets U.S. law firms with fake IT support calls and phishing, and may send an associate to attach a storage device when remote access fails. The group reportedly steals data without encrypting systems.

May 27, 2026
Security News · cyberscoop.com

OpenAI outlines cybersecurity and information safeguards for 2026 midterms

OpenAI outlined a five-part plan for the 2026 midterms, including cybersecurity support for election officials, reliable voting information, deepfake watermarking, limits on election interference, and an Associated Press data-sharing partnership.

May 27, 2026
Security News · securityweek.com

GCHQ Chief Warns of AI Weaponization and Rising Russian Hybrid Activity

GCHQ Director Anne Keast-Butler warned that AI is being weaponized and Russia is escalating hybrid activity. She said GCHQ plans to integrate agentic AI into cyber defense and urged greater cybersecurity urgency.

May 27, 2026
Security News · wiz.io

Wiz Launches Automated Forensics for Runtime Sensor Customers

Wiz Forensics is generally available to Runtime Sensor customers, automatically collecting threat-scoped artifacts when detections fire and using AI to analyze evidence for investigation verdicts.

May 27, 2026
Security News · bleepingcomputer.com

FBI Warns Silent Ransom Group Is Using In-Person Data Theft Against Law Firms

The FBI warns that Silent Ransom Group actors are targeting U.S. law firms by impersonating IT support, seeking remote access, or visiting in person to connect storage devices and steal data for extortion.

May 27, 2026
Security News · bleepingcomputer.com

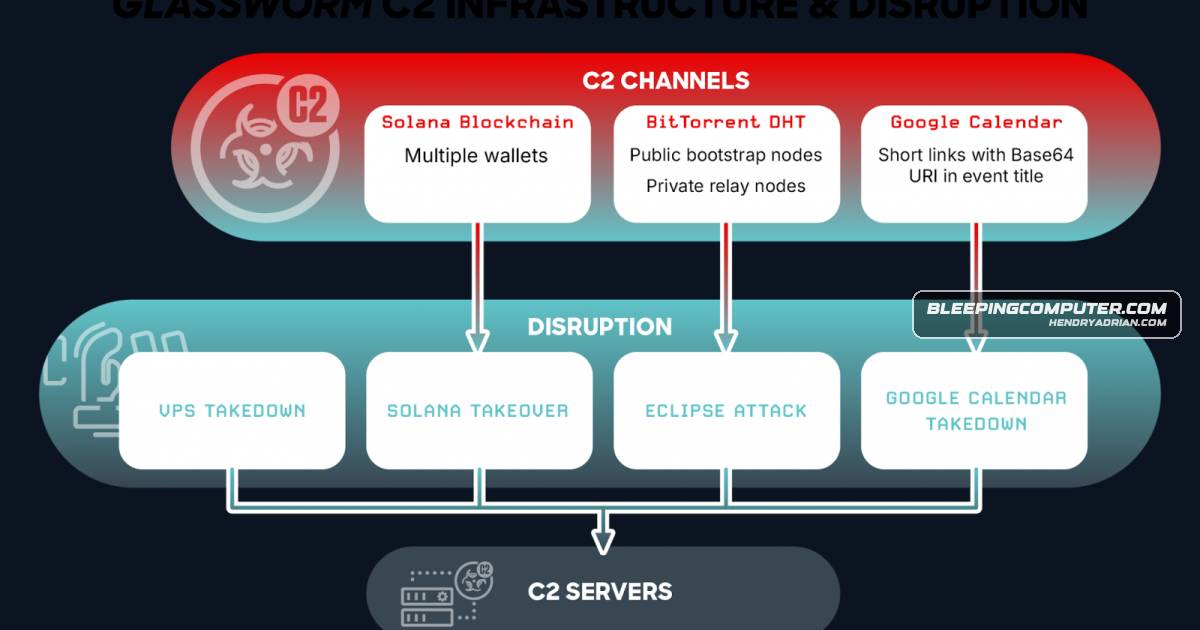
CrowdStrike, Google and Shadowserver Disrupt Glassworm Botnet

CrowdStrike, Google and The Shadowserver Foundation disrupted Glassworm by cutting off four C2 channels. The botnet targeted developers through malicious extensions and packages; infected hosts now beacon to 164.92.88[.]210.

May 27, 2026
Security News · cybersecuritypulse.net

Megalodon Supply-Chain Campaign Infects 5,500+ GitHub Repositories

The newsletter covers Megalodon’s reported compromise of more than 5,500 GitHub repositories to steal CI secrets and credentials, alongside supply-chain security findings and other security industry developments.

May 27, 2026
Security News · securityweek.com

RevEng.AI Raises $15 Million to Analyze Software Binaries for Security Flaws

RevEng.AI raised $15 million in Series A funding and says its BinNet AI platform analyzes compiled software without source code to identify vulnerabilities, backdoors, and other security issues.

May 27, 2026
Security News · securityweek.com

Romanian Hacker Sentenced to 56 Months for Selling Access to Oregon State Network

Catalin Dragomir was sentenced to 56 months in U.S. prison after pleading guilty to obtaining information from a protected computer and aggravated identity theft. Prosecutors said he hacked an Oregon state network and sold access to it and other networks.

May 27, 2026
Security News · bleepingcomputer.com

Windows 11 KB5089573 Preview Adds Performance Improvements and Secure Boot Certificate Rollout

Microsoft’s optional KB5089573 preview for Windows 11 25H2 and 24H2 includes performance and reliability changes, Windows Hello refinements, and expanded phased delivery of replacement Secure Boot certificates; it contains no security updates.

May 27, 2026
Security News · bleepingcomputer.com

Dutch Police Arrest Suspect in Ajax Systems Hack

Dutch police arrested a 35-year-old man suspected of repeatedly hacking AFC Ajax. Ajax said flaws exposed data on hundreds and enabled ticket transfers and stadium-ban changes; RTL reported API access to over 300,000 accounts. Ajax patched the flaws.

May 27, 2026
Security News · securityweek.com

FBI Warns Silent Ransom Group Uses In-Person USB Intrusions

The FBI says Silent Ransom Group is posing as IT support to target law firms, using remote access or in-person USB drives to steal data and extort victims without deploying file-encrypting ransomware.

May 27, 2026
Security News · therecord.media

Putin Names Former Rostec Cyber Executive to Security Council Role Amid Reported GRU Link

Putin appointed former Rostec cybersecurity executive Andrei Kozlov as aide to Security Council Secretary Sergei Shoigu. The Insider reported leaked data linking Kozlov’s clearance to GRU unit 26165, associated with APT28; the connection remains alleged.

May 26, 2026
Security News · therecord.media

Dutch Authorities Arrest Two IT Entrepreneurs in Investigation of Infrastructure for Russian Cyber Operations

Dutch authorities arrested two IT entrepreneurs over alleged EU sanctions violations, searching business sites and data centers and seizing more than 800 servers. Investigators allege the infrastructure supported Russian-linked cyberattacks and disinformation; MIRhos

May 26, 2026
Security News · inews.setn.com

EVERY8D Investigates Service Disruptions and Dark-Web Data Claims

EVERY8D says service disruptions followed server-disk data corruption and system anomalies. Trend Micro is conducting forensics; initial findings show no concrete evidence of mass customer-data leakage, while the cause and impact remain under investigation.

May 26, 2026
Security News · cyberscoop.com

White House Replaces Federal Cybersecurity Logging Guidance With Risk-Based Rules

OMB memo M-26-14 replaces federal logging guidance from 2021 with a risk-based approach. CISA has 90 days to develop a logging architecture; experts warn rescinding the old guidance first could delay agency prioritization.

May 26, 2026
Security News · cyberscoop.com

Apple Releases Quantum-Resistant Cryptography Code and Verification Tools

Apple released ML-KEM and ML-DSA implementations in corecrypto, plus formal verification tools and documentation. Apple says verification uncovered a missing ML-DSA step that could have silently broken digital signatures if it had reached production.

May 26, 2026
Security News · any.run

ANY.RUN Details Six Business-Themed Phishing and Malware Campaigns From May 2026

ANY.RUN’s May 2026 roundup describes six campaign patterns, including fake invitations, Agent Tesla document lures, OTP phishing, fileless delivery from compromised B2B sites, ScreenConnect remote-access chains and BlobPhish browser-based credential theft.

May 26, 2026
Security News · cyberscoop.com

Anthropic says Mythos found over 10,000 high- or critical-severity flaws in Project Glasswing’s first month

Anthropic says Project Glasswing identified over 10,000 high- or critical-severity vulnerabilities. Partner and evaluation results include Cloudflare and Mozilla findings, while Anthropic cites human triage and patching capacity as the main bottleneck.

May 26, 2026
Security News · bleepingcomputer.com

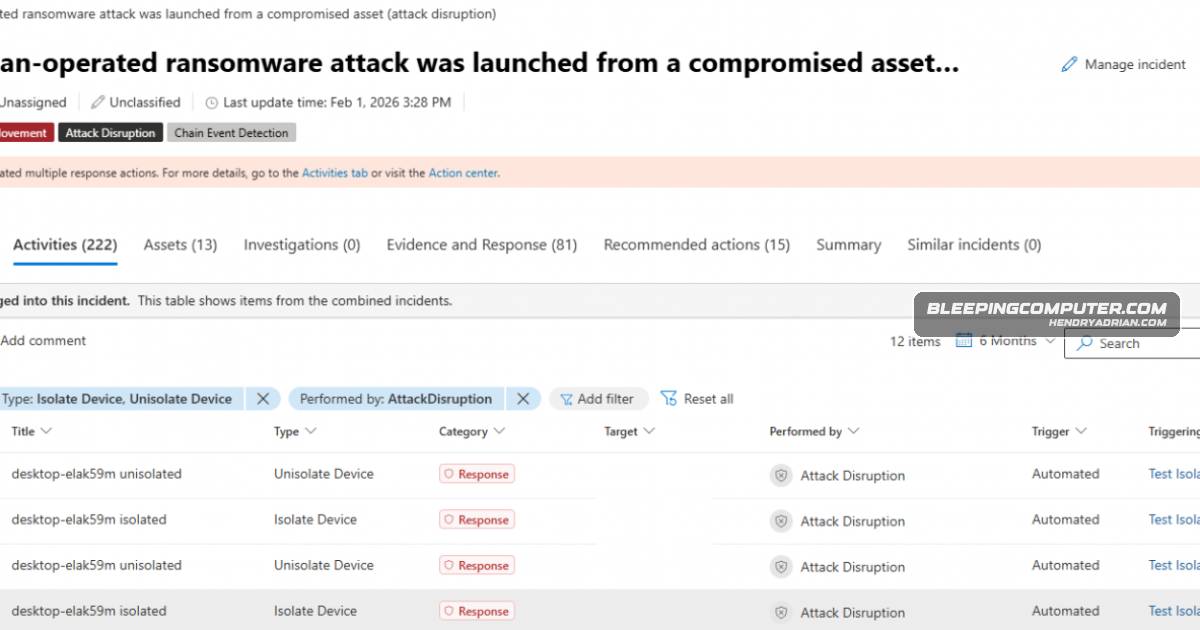
Microsoft Defender previews automatic isolation for compromised endpoints

Microsoft is previewing automatic isolation in Defender for Endpoint to limit lateral movement and contain attacks. Isolated devices lose network access but remain connected to the service for monitoring.

May 26, 2026
PreviousPage 98 of 159 Next
© 2026 cyber.hendryadrian.com