
Laravel Lang Packages Hijacked to Deliver Credential-Stealing Malware
Summary
Attackers rewrote GitHub tags for Laravel Lang packages to distribute a Composer dropper and the DebugElevator credential stealer. Packagist removed malicious versions; developers were urged to review installations and rotate exposed credentials.
Key points
- Attackers rewrote GitHub tags across Laravel Lang repositories, making malicious commits appear to be legitimate releases.
- Affected packages included laravel-lang/lang, http-statuses, attributes, and possibly actions; researchers reported differing estimates of the number of impacted versions.
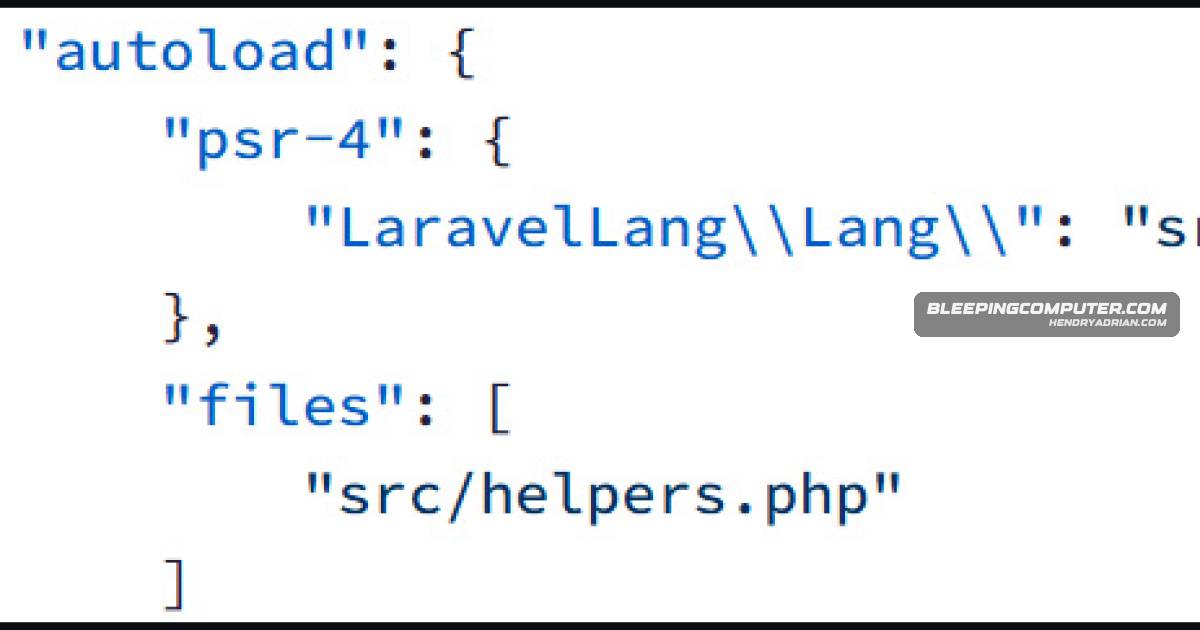
- Composer automatically loaded a malicious src/helpers.php dropper, which downloaded a second-stage payload from flipboxstudio[.]info.
- The credential stealer targeted cloud and Kubernetes secrets, Git credentials, SSH keys, browser data, and other sensitive information.
- BleepingComputer identified the Windows executable as DebugElevator, which targets Chrome, Brave, and Edge credentials.
- Packagist removed malicious versions and temporarily unlisted affected packages; developers were advised to review installations, rotate exposed credentials, and inspect systems.
Article Details
- Event Type
- Supply-chain compromise distributing credential-stealing malware through Laravel Lang packages.
- Impact
- Attackers rewrote GitHub tags so Composer installations of affected package versions could load a dropper and credential-stealing payload. The malware targeted cloud credentials, Kubernetes secrets, Git credentials, SSH keys, browser data, and other sensitive information, then encrypted and sent collected data to its C2 server. Aikido reported that Packagist removed the malicious versions and temporarily unlisted affected packages. Aikido said 233 versions across three repositories were compromised; Socket estimated roughly 700 historical versions may have been affected.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | flipboxstudio[.]info | Attacker-controlled C2 domain used to deliver the second-stage credential-stealing payload and receive stolen data. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe malware encrypted extracted data and sent it to the C2 server.T1105 · Ingress Tool TransferThe dropper downloaded a second-stage PHP payload from the attacker’s C2 server.T1552.001 · Credentials In FilesThe malware searched files and environment variables for credentials, including secrets in local .env files.T1552.004 · Private KeysThe malware targeted SSH private keys.T1555.003 · Credentials from Web BrowsersThe Windows malware targeted stored credentials in Chrome, Brave, and Edge.
Malware
Products
ComposerA supply chain attack against Laravel Lang localization packages abused GitHub tags and Composer distribution to deliver malicious releases that installed a credential-stealing payload.GitHubA supply chain attack against Laravel Lang localization packages abused GitHub tags and Composer distribution to deliver malicious releases that installed a credential-stealing payload.Laravel LangA supply chain attack against Laravel Lang localization packages abused GitHub tags and Composer distribution to deliver malicious releases that installed a credential-stealing payload.PackagistPackagist removed the malicious versions and developers were urged to rotate exposed credentials.