
Megalodon Campaign Injected Malicious Workflows Into 5,561 GitHub Repositories
Summary
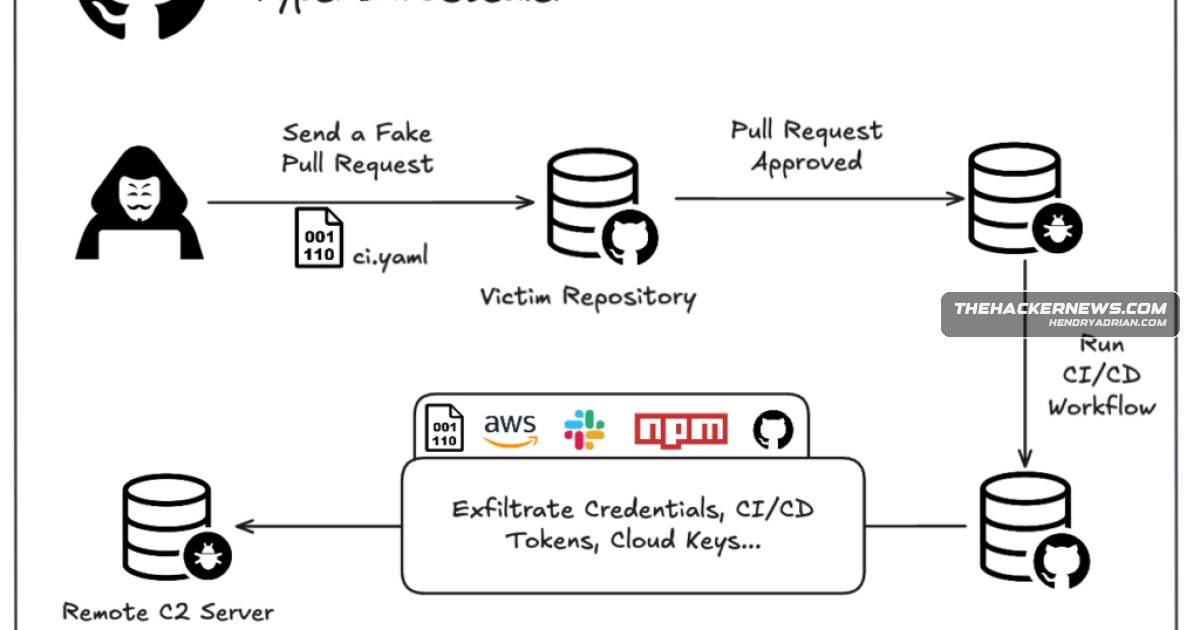
SafeDep reported that Megalodon pushed 5,718 malicious commits to 5,561 GitHub repositories in six hours, adding workflows designed to steal CI/CD secrets. The article also describes related TeamPCP activity and fake Polymarket npm packages targeting wallet keys.
Key points
- SafeDep reported 5,718 malicious commits across 5,561 repositories on May 18, 2026, within a six-hour period.
- The workflows used forged author identities and base64-encoded bash payloads to collect CI secrets, cloud credentials, SSH keys, tokens, and configuration data.
- Two variants were reported: SysDiag, triggered on pushes and pull requests, and Optimize-Build, triggered manually through workflow_dispatch.
- The article describes broader TeamPCP supply-chain activity and says npm invalidated certain write tokens that bypassed two-factor authentication while urging maintainers to use Trusted Publishing.
- Nine fake Polymarket npm packages reportedly used a postinstall prompt to trick users into entering Ethereum or Polygon private keys, which were sent to an attacker-controlled endpoint.
Article Details
- Event Type
- Automated software supply-chain campaign targeting GitHub repositories, alongside a separate campaign using fake Polymarket npm packages to steal private keys.
- Impact
- Megalodon reportedly pushed 5,718 malicious commits to 5,561 repositories in six hours. Its workflows were designed to steal CI secrets, cloud credentials, SSH keys, tokens, and source-code secrets. Separately, nine fake npm packages prompted users to enter Ethereum or Polygon private keys and sent them to an attacker-controlled endpoint.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 216[.]126[.]225[.]129 | C2 server identified by SafeDep as the destination for secrets exfiltrated by the malicious GitHub Actions workflows. |
| URL | hxxps[:]//polymarketbot[.]polymarketdev[.]workers[.]dev/v1/wallets/keys | Attacker-controlled endpoint used by the fake npm packages to POST users’ Ethereum or Polygon private keys in plaintext. |
MITRE ATT&CK
T1059.004 · Unix ShellThe GitHub Actions payloads included base64-encoded bash.T1078 · Valid AccountsSafeDep reported that the attacker pushed commits using compromised personal access tokens or deploy keys.T1195.002 · Compromise Software Supply ChainMalicious GitHub Actions workflows were injected into repositories, and fake npm packages were published to distribute credential-stealing code.T1567 · Exfiltration Over Web ServiceThe malicious workflows exfiltrated secrets to a C2 server, and the fake npm packages POSTed private keys to an attacker-controlled web endpoint.
People
Threat Actors
LAPSUS$The article says TeamPCP has established partnerships with extortion crews including LAPSUS$.TeamPCPThe article reports that TeamPCP has compromised GitHub and abused software supply chains across multiple ecosystems. It links related ecosystem abuse to the group but does not specifically attribute the Megalodon campaign to it.VectThe article says TeamPCP has established partnerships with extortion crews including VECT.
Malware
ChainDropThe fallout from TeamPCP’s attack spree and the Mini Shai-Hulud worm has prompted npm to invalidate granular access tokens with write access that bypasses two-factor authentication (2FA).Optimize-BuildTwo variants were seen: SysDiag for broad execution and Optimize-Build for targeted activation.SysDiagTwo variants were seen: SysDiag for broad execution and Optimize-Build for targeted activation.
Vendors
Products
GitHub ActionsResearchers uncovered Megalodon, an automated supply-chain campaign that injected malicious GitHub Actions workflows into thousands of repositories to steal CI secrets, cloud credentials, SSH keys, and other sensitivenpmThe report also links related ecosystem abuse to TeamPCP and a set of fake Polymarket npm packages used to steal Ethereum/Polygon private keys.
Countries
IranWhat’s more, the group seems to be geopolitically motivated as well, as evidenced by the deployment of wiper malware upon detecting machines located in Iran and Israel.IsraelWhat’s more, the group seems to be geopolitically motivated as well, as evidenced by the deployment of wiper malware upon detecting machines located in Iran and Israel.