
Ghost CMS Flaw Exploited in ClickFix Campaign Affecting 700+ Sites
Summary
XLab reports that attackers exploited Ghost CMS CVE-2026-26980 to steal admin API keys and inject ClickFix scripts on more than 700 sites. Ghost fixed the flaw in version 6.19.1; administrators should upgrade and rotate keys.
Key points
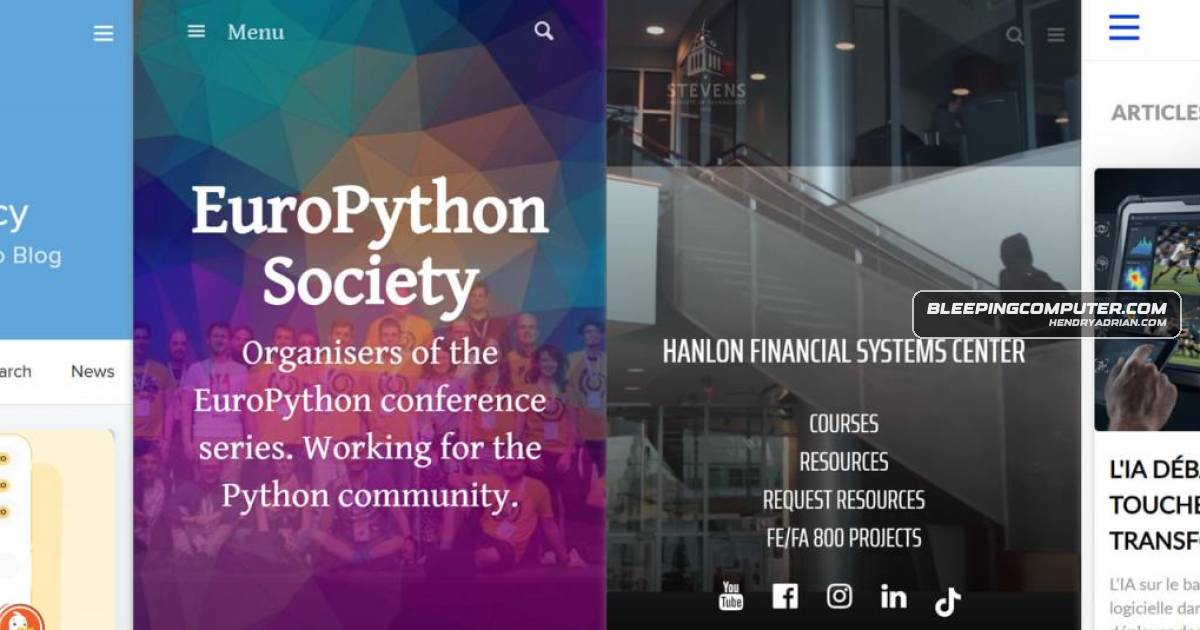
- XLab reported that the campaign affected more than 700 domains, including sites linked to Harvard University, Oxford University, Auburn University, and DuckDuckGo.
- CVE-2026-26980 affects Ghost 3.24.0 through 6.19.0 and allows unauthenticated attackers to read database data, including admin API keys.
- Attackers used stolen keys to inject JavaScript into articles; the scripts fetched cloaking code that selected visitors for a fake Cloudflare ClickFix prompt.
- The prompt instructed victims to paste a command into Windows Command Prompt, leading to payloads including DLL loaders, JavaScript droppers, and UtilifySetup.exe.
- Researchers observed two activity clusters, including cases where attackers re-infected sites or replaced another cluster’s scripts.
- Ghost released a fix in version 6.19.1 on February 19. Administrators are advised to upgrade, rotate previously used keys, inspect and remove injected scripts, and retain 30 days of admin API logs.
Article Details
- Event Type
- Large-scale exploitation campaign targeting Ghost CMS through CVE-2026-26980
- Impact
- XLab reported that more than 700 domains were affected. Attackers used the flaw to read database data, including admin API keys, and inject JavaScript that served ClickFix lures and payloads, including the Electron-based malware sample UtilifySetup.exe. Ghost released a fix in version 6.19.1 on February 19; the article reports that many sites had not installed the update.
MITRE ATT&CK
T1059.007 · JavaScriptInjected JavaScript loaded second-stage cloaking code from attacker infrastructure.T1190 · Exploit Public-Facing ApplicationAttackers exploited CVE-2026-26980, a SQL injection flaw in Ghost CMS, to compromise vulnerable websites.T1204.004 · Malicious Copy and PasteThe ClickFix lure instructed victims to paste a supplied command into Windows Command Prompt.
CVE
Malware
Products
Industries
AI/SaaScompany Qianxin, who confirmed impact on more than 700 domains, including university portals, AI/SaaS companies, media outlets, fintech firms, security sites, and personal blogs.CybersecurityThe campaign was discovered by XLab threat intelligence researchers at Chinese cybersecurity company Qianxin, who confirmed impact on more than 700 domains, including university portals, AI/SaaS companies, mediafintechimpact on more than 700 domains, including university portals, AI/SaaS companies, media outlets, fintech firms, security sites, and personal blogs.MediaQianxin, who confirmed impact on more than 700 domains, including university portals, AI/SaaS companies, media outlets, fintech firms, security sites, and personal blogs.