
FBI Warns Kali365 Phishing Service Targets Microsoft 365 Accounts
Summary
The FBI warns that Kali365 uses OAuth device-code phishing and session-token capture to target Microsoft 365 and Entra accounts. It recommends restricting device-code authentication and auditing its use.
Key points
- Kali365 emerged in April 2026 and is reportedly distributed through Telegram channels.
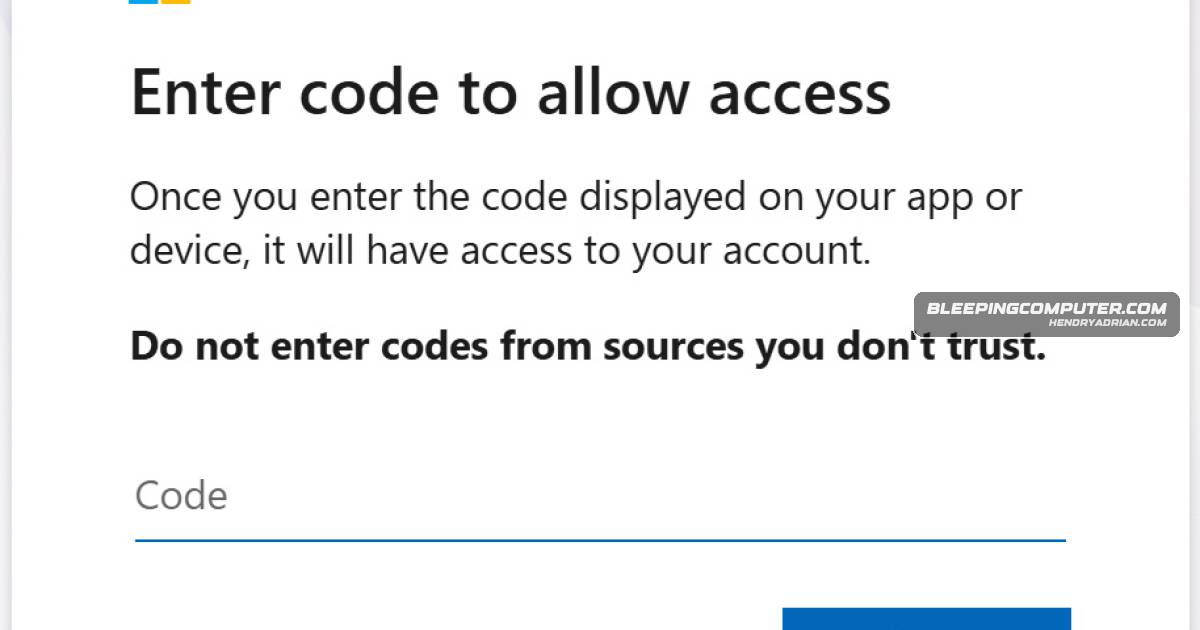
- The service tricks victims into entering attacker-generated codes on Microsoft’s device login page, allowing attackers to obtain OAuth tokens after victims complete MFA.
- Its “Cookie Link” mode proxies victims through attacker-controlled infrastructure to capture authenticated browser sessions, cookies, and tokens.
- Arctic Wolf reported campaigns targeting organizations worldwide; reported activity included malicious mailbox rules and unauthorized device registrations.
- The FBI recommends restricting device-code authentication with Conditional Access policies, auditing its use, and blocking authentication-transfer policies where possible.
- The FBI advises affected organizations to report incidents and preserve phishing emails, suspicious login information, and unauthorized device registrations.
Article Details
- Event Type
- FBI warning about Kali365, a phishing-as-a-service platform used to hijack Microsoft 365 and Entra accounts through OAuth device code phishing and session-token theft.
- Impact
- According to the FBI and Arctic Wolf researchers, attackers can obtain access to victims’ accounts without stealing passwords or intercepting MFA codes, then access mailboxes and other applications available through single sign-on. Researchers reported malicious inbox rules and unauthorized device registrations in some attacks.
MITRE ATT&CK
T1098.005 · Device RegistrationResearchers reported that attackers registered new devices in some victims’ Microsoft environments.T1528 · Steal Application Access TokenKali365 is reported to capture OAuth access tokens and authenticated session tokens to gain access to victims’ accounts.T1566.002 · Spearphishing LinkArctic Wolf researchers reported phishing emails directing victims to Microsoft’s device code login portal.
Threat Actors
Vendors
Arctic WolfSecurity researchers at Arctic Wolf reported on Kali365 activity in April after observing a widespread campaign targeting organizations worldwide.MicrosoftThe FBI is warning that the Kali365 phishing-as-a-service platform is helping attackers hijack Microsoft 365 and Entra accounts by abusing OAuth device code authentication to steal session tokens and bypass MFA.
Products
Microsoft 365 Apps for EnterpriseThe FBI is warning that the Kali365 phishing-as-a-service platform is helping attackers hijack Microsoft 365 and Entra accounts by abusing OAuth device code authentication to steal session tokens and bypass MFA.Microsoft EntraThe platform uses device code phishing, an increasingly popular method that abuses Microsoft’s legitimate OAuth 2.0 Device Authorization grant flow to gain access to Microsoft Entra and Microsoft 365 accounts.
Tools
EvilTokensThis adoption includes the EvilTokens PhaaS and Tycoon2FA, which are also using it to compromise Microsoft 365 and Entra accounts.Kali365The FBI is warning that the Kali365 phishing-as-a-service platform is helping attackers hijack Microsoft 365 and Entra accounts by abusing OAuth device code authentication to steal session tokens and bypass MFA.Tycoon2FAThis adoption includes the EvilTokens PhaaS and Tycoon2FA, which are also using it to compromise Microsoft 365 and Entra accounts.