
Researchers Report Megalodon Attack on 5,000+ GitHub Repositories
Summary
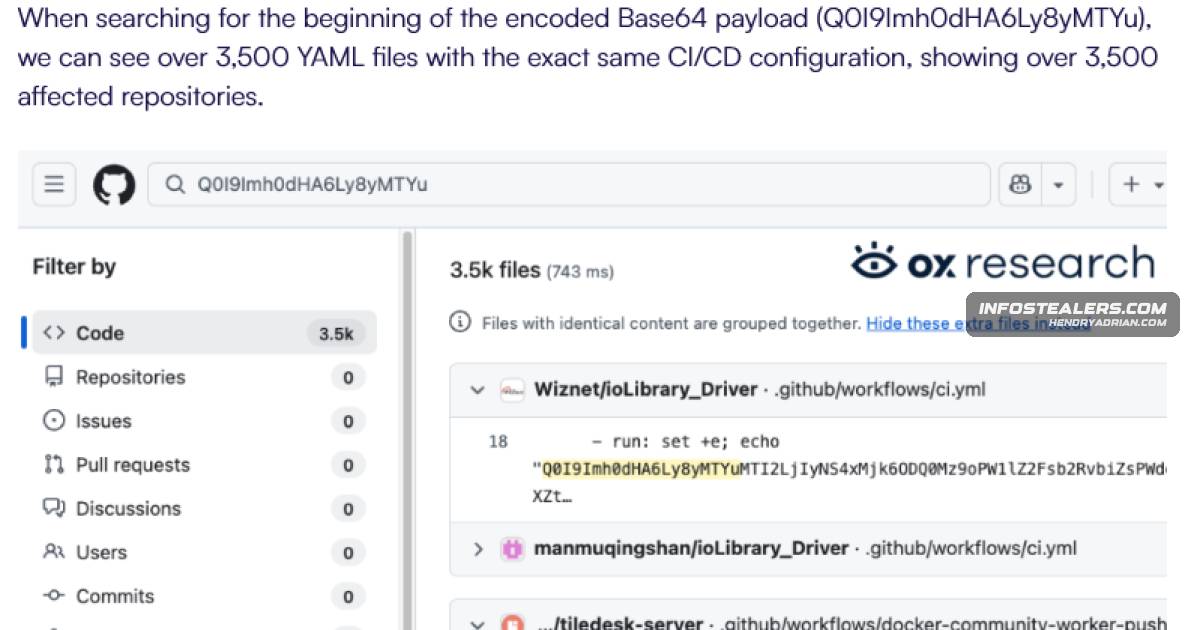
Researchers say the Megalodon campaign injected malicious GitHub Actions workflows into 5,000+ repositories in six hours to steal accessible secrets. Hudson Rock says 331 of 978 associated usernames matched computers infected by infostealers.
Key points
- The article reports that attackers pushed thousands of malicious commits to more than 5,000 public GitHub repositories in about six hours.
- OX Security and SafeDep described malicious GitHub Actions workflows, with weak branch protections and throwaway or compromised accounts cited as enabling factors.
- The workflows were designed to steal accessible AWS keys, GCP OAuth tokens, SSH private keys and GitHub OIDC tokens, and to deploy additional infostealers.
- Hudson Rock says 331 of 978 unique usernames associated with affected repositories matched computers in its infostealer database; it also describes a manual email-based match for one account.
- The article links the campaign’s spread to TeamPCP’s open-source release of the Shai Hulud framework, citing Datadog Security Labs’ analysis.
- Hudson Rock says its new monitoring feature found compromised GitHub credentials associated with employees at more than 24,000 companies; this is a vendor-reported finding.
Article Details
- Event Type
- Automated GitHub supply-chain attack involving malicious GitHub Actions workflows pushed through compromised or throwaway accounts.
- Impact
- The article reports that Megalodon affected more than 5,000 public repositories and pushed thousands of malicious commits within six hours. The workflows were designed to steal accessible secrets, including AWS keys, GCP tokens, SSH private keys, and GitHub OIDC tokens, and to deploy additional infostealers. Hudson Rock reported matching 331 of 978 affected usernames to infostealer-infected computers and said a further investigation linked an initially unmatched account to an infection; its conclusion that the affected accounts were exclusively sourced from infostealer data is the company's claim.
Threat Actors
Malware
Products
GitHubMegalodon is a large automated supply chain attack that infected over 5,000 GitHub repositories by abusing GitHub Actions workflows to steal secrets such as AWS keys, GCP tokens, SSH private keys, and GitHub OIDC tokens.GitHub ActionsMegalodon is a large automated supply chain attack that infected over 5,000 GitHub repositories by abusing GitHub Actions workflows to steal secrets such as AWS keys, GCP tokens, SSH private keys, and GitHub OIDC tokens.