cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3802 articles

Security News · securityweek.com

Cylake Launches With $45 Million to Build On-Premises Security Platform

Cybersecurity startup Cylake announced its launch and $45 million in seed funding for a platform aimed at regulated organizations unable to use public cloud services. General availability is expected in early 2027.

Mar 10, 2026
Security News · therecord.media

White House Order Targets Scam Centers, Calls for Victim Restoration Program

A U.S. executive order directs agencies to develop a 120-day plan against transnational criminal organizations and calls for a 90-day program to return seized funds to victims of cyber-enabled fraud.

Mar 10, 2026
Security News · therecord.media

White House Cyber Strategy Calls for Offensive Operations and Lighter Regulation

The White House’s four-page cyber strategy calls for more offensive operations, lighter regulation, stronger federal and critical-infrastructure defenses, and secure AI. Critics say it lacks implementation details; planned measures include pilot programs and incentives.

Mar 10, 2026
Security News · therecord.media

Senate Clears Procedural Hurdle for Joshua Rudd to Lead Cyber Command and NSA

The Senate voted 68-28 to limit debate on Joshua Rudd’s nomination to lead Cyber Command and the NSA, setting up a final vote. Sen. Ron Wyden opposes the nomination, citing Rudd’s lack of signals-intelligence experience.

Mar 10, 2026
Security News · securityonline.info

Zscaler Links Dust Specter Campaign to Hijacked Iraqi Government Site

Zscaler ThreatLabz attributes an espionage campaign targeting Iraqi officials, with medium-to-high confidence, to Dust Specter. The group allegedly used hijacked Iraqi infrastructure, tailored lures, custom .NET malware, and protected C2 paths.

Mar 10, 2026
Security News · securityonline.info

Threat Hunter Team Reports Seedworm Campaign and New Dindoor Backdoor

The Threat Hunter Team reports increased Seedworm activity since early February 2026 against U.S. and Canadian organizations, including entities tied to Israel, and says researchers found the previously undocumented Dindoor backdoor on several networks.

Mar 10, 2026
Security News · darkowl.com

Hacktivists and Extremist Groups React to Iran–Israel Conflict with Cyberattack Claims and Propaganda

DarkOwl reports increased hacktivist activity and cyberattack claims after U.S. and Israeli strikes on Iran, alongside Telegram-based propaganda and reactions from jihadist and Iranian-aligned groups.

Mar 9, 2026
Security News · bleepingcomputer.com

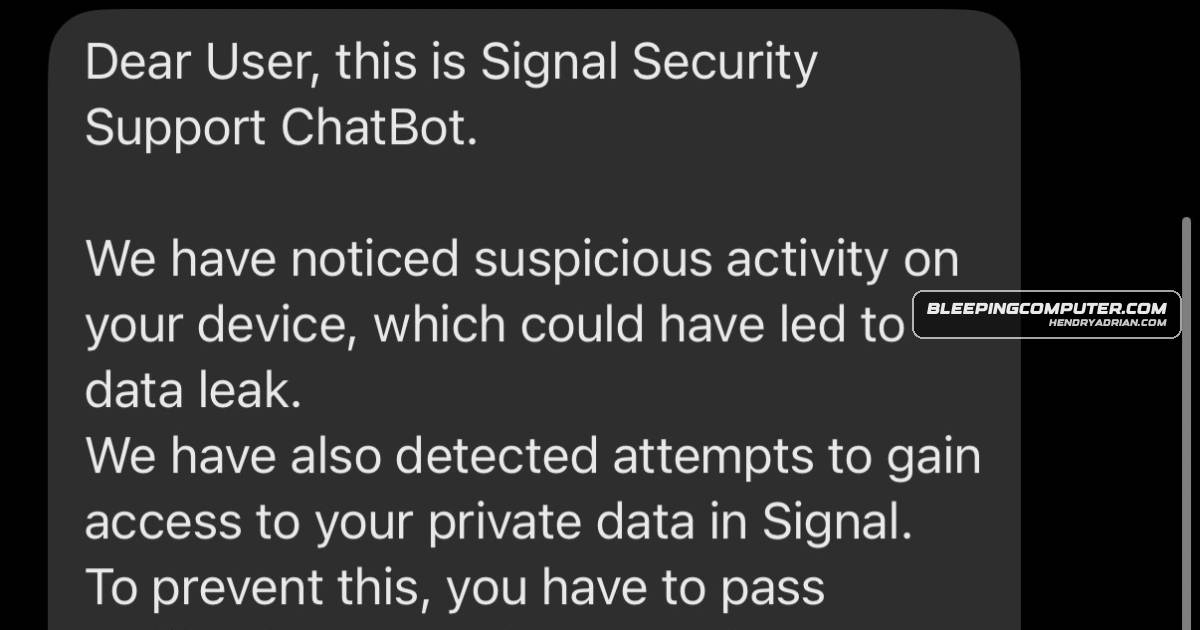
Dutch Agencies Warn of Signal and WhatsApp Account-Hijacking Campaign

Dutch intelligence agencies say Russian state-sponsored actors are targeting officials, military personnel and journalists with Signal and WhatsApp phishing, using stolen verification codes or malicious device-linking QR codes to access messages.

Mar 9, 2026
Security News · hackread.com

Social Security Scam Emails Use Fake Tax Documents to Install RATs via Datto RMM

LifeLock reported emails impersonating the Social Security Administration that use fake document links or attachments and Datto RMM to install a RAT. The article says the malware can enable device control and data theft.

Mar 9, 2026
Security News · sysdig.com

Sysdig Details Malware Detection and Blocking for Cloud Workloads

Sysdig says its cloud detection and response uses file-write and execution monitoring, YARA rules, signatures and intelligence feeds to detect and block malware across cloud, hybrid and on-prem workloads.

Mar 9, 2026
Security News · bleepingcomputer.com

FBI Warns of Phishing Impersonating City and County Officials

The FBI warns that criminals are using public permit details to impersonate local planning and zoning officials and solicit fraudulent fees by wire transfer, peer-to-peer payment, or cryptocurrency. It advises verifying requests with local government offices.

Mar 9, 2026
Security News · bleepingcomputer.com

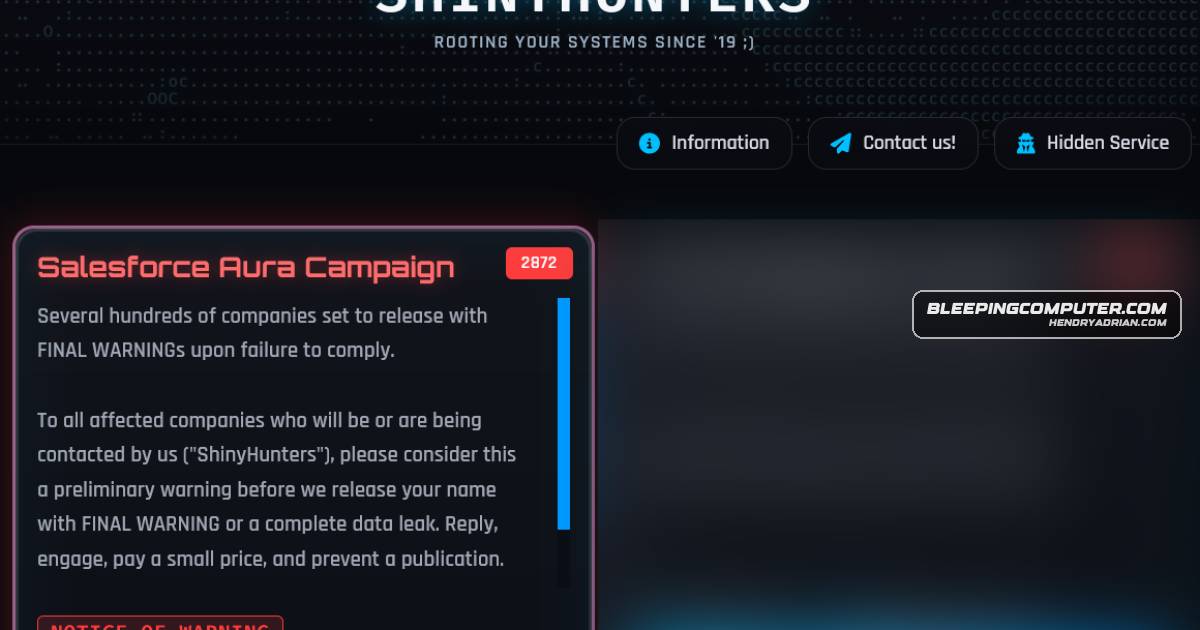
ShinyHunters Claims Ongoing Salesforce Aura Data-Theft Campaign

Salesforce says attackers are abusing misconfigured Experience Cloud guest permissions via the Aura API, not a platform flaw. ShinyHunters claims hundreds of victims, but the claims are unverified. Salesforce recommends restricting guest access and monitoring Aura logs.

Mar 9, 2026
Security News · bleepingcomputer.com

Microsoft Teams to Label Third-Party Bots in Meeting Lobbies

Microsoft says Teams will label external third-party bots waiting in meeting lobbies, requiring organizers to admit them separately. The feature is scheduled for May 2026 across major platforms and standard multi-tenant and GCC clouds.

Mar 9, 2026
Security News · securityweek.com

42 Cybersecurity M&A Deals Announced in February 2026

SecurityWeek reported 42 cybersecurity-related M&A deals announced in February 2026, spanning areas including attack surface management, AI security, endpoint protection, identity fraud detection, and post-quantum cryptography.

Mar 9, 2026
Security News · securityweek.com

ClickFix Variant Uses Windows Terminal to Evade Detection

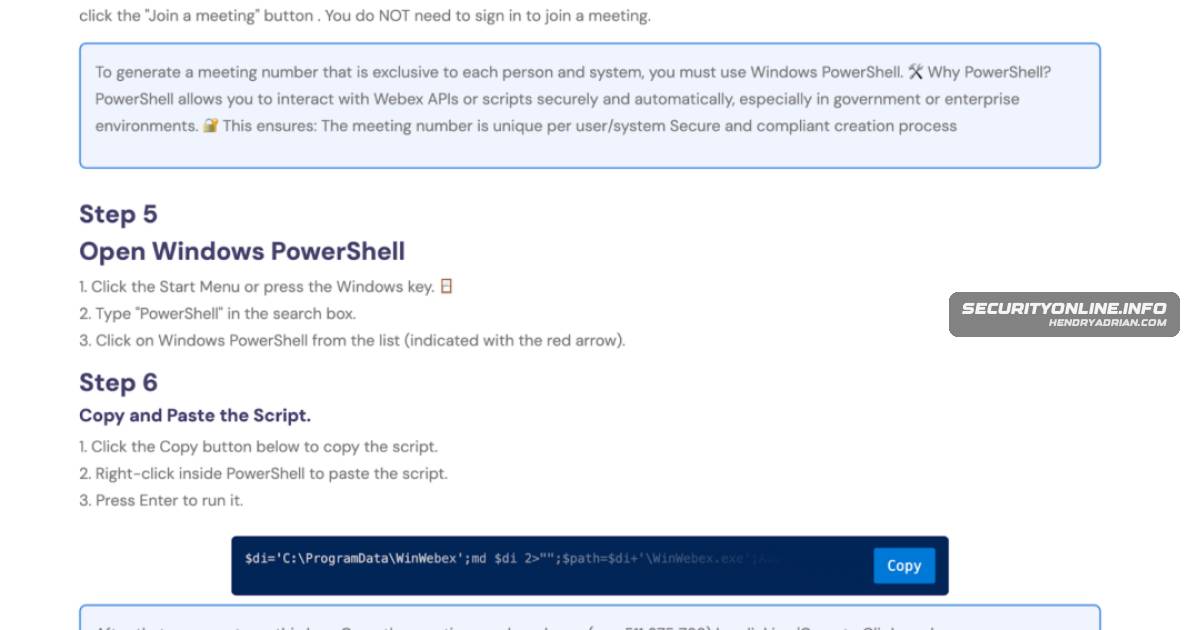
Microsoft says a ClickFix variant observed in February directs victims to run malicious PowerShell commands in Windows Terminal, leading to Lumma Stealer. Other variants use batch scripts, browser-process injection, or cloned AI tool sites.

Mar 9, 2026
Security News · securityweek.com

Infoblox Reports Phishing Campaign Abusing .arpa Reverse-DNS Records

Infoblox reports a phishing campaign abusing arpa reverse-DNS records and hijacked CNAMEs. Attackers use misleading redirects and randomized subdomains; the toolkit has reportedly been used by multiple actors since 2017.

Mar 9, 2026
Security News · bleepingcomputer.com

Phishing Campaign Abuses IPv6 Reverse DNS to Evade Defenses

Infoblox reports phishing campaigns abusing ip6[.]arpa reverse-DNS records, trusted DNS providers and short-lived TDS redirects to evade domain-reputation checks; it also observed more than 100 hijacked CNAMEs.

Mar 8, 2026
Security News · bleepingcomputer.com

EU Advocate General Says Banks Must Promptly Refund Phishing Victims Under PSD2

An EU Advocate General advised that banks should promptly refund unauthorized PSD2 transactions unless they have written grounds to suspect customer fraud. The opinion is advisory; the CJEU’s eventual ruling will be binding.

Mar 8, 2026
Security News · bleepingcomputer.com

Microsoft Reports Threat Actors Using AI Across the Cyberattack Lifecycle

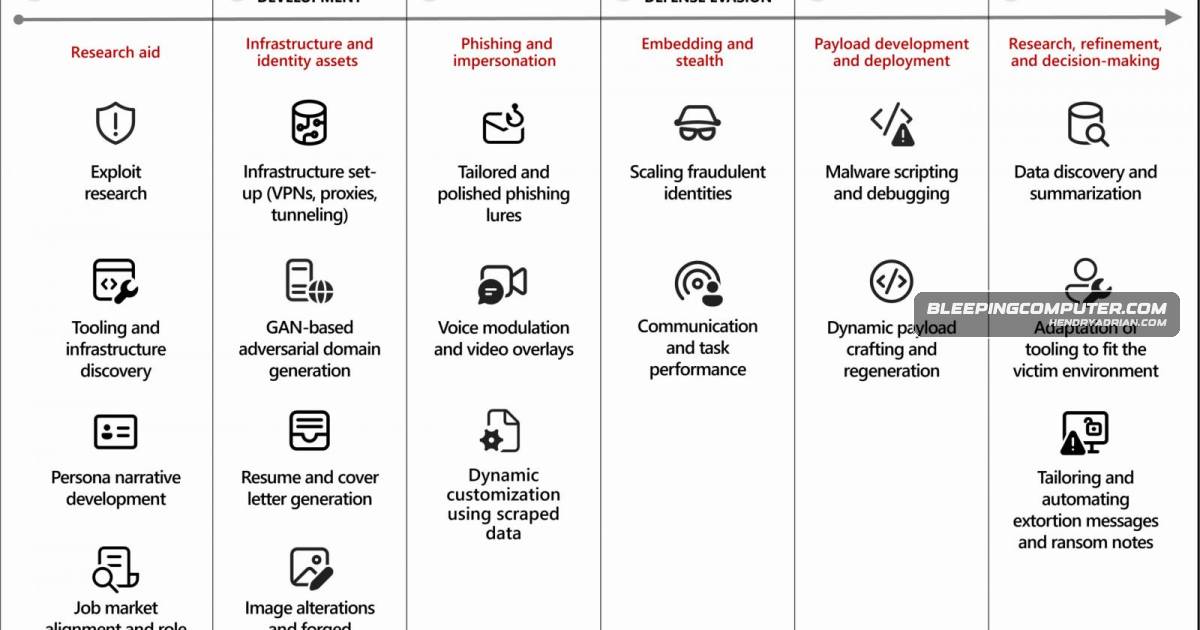
Microsoft says threat actors use generative AI for reconnaissance, phishing, identity fraud, malware development and post-compromise tasks. It recommends stronger identity defenses and monitoring for abnormal credential use.

Mar 7, 2026
Security News · bleepingcomputer.com

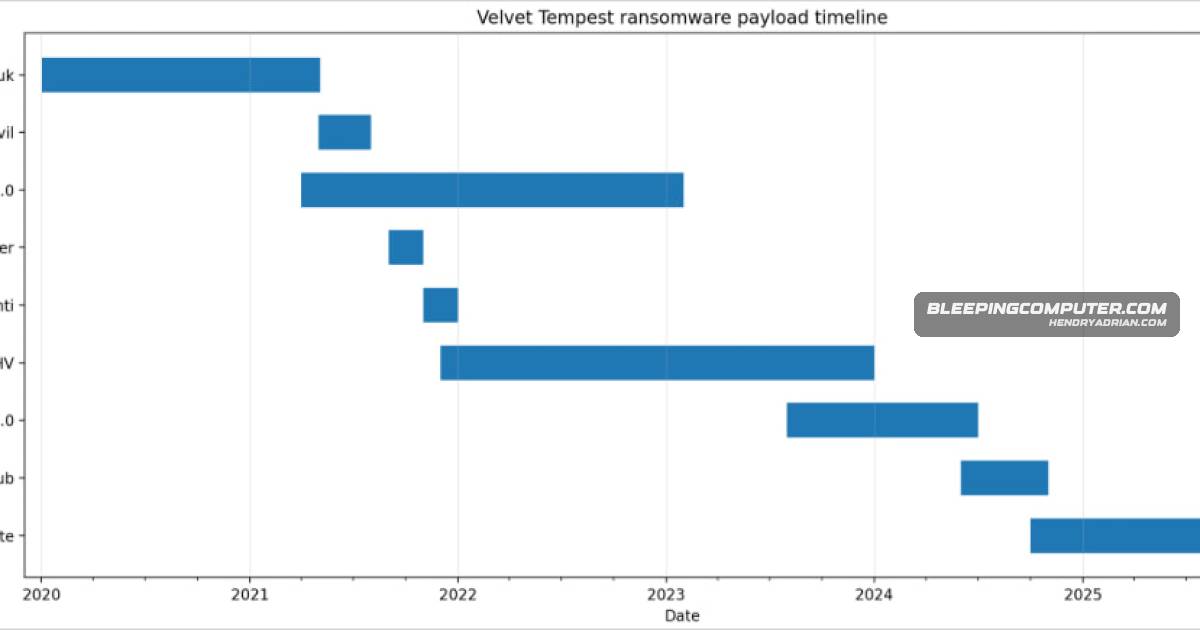
Velvet Tempest Used ClickFix to Deploy CastleRAT in Emulated Intrusion

MalBeacon observed Velvet Tempest use a ClickFix lure to stage DonutLoader and retrieve CastleRAT in a 12-day emulated intrusion. The researchers said Termite ransomware was not deployed.

Mar 7, 2026
Security News · bleepingcomputer.com

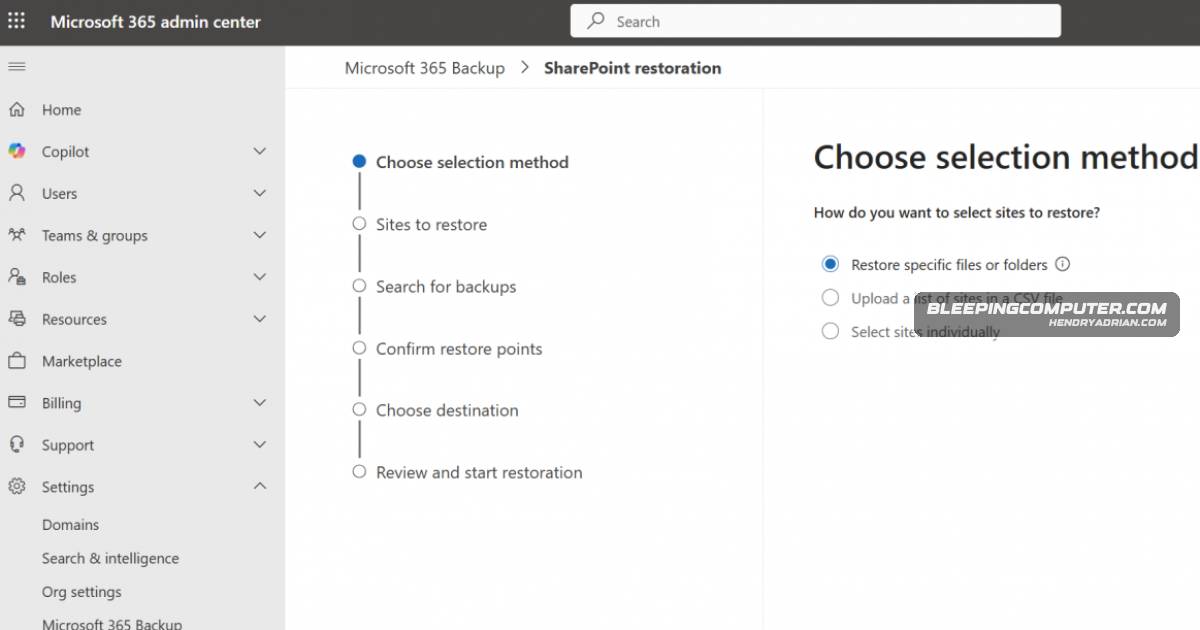
Microsoft 365 Backup to Add File- and Folder-Level Restore

Microsoft 365 Backup is adding admin-only file- and folder-level restores for SharePoint and OneDrive. The feature entered public preview in March 2026, with general availability expected in late April to early May.

Mar 7, 2026
Security News · bleepingcomputer.com

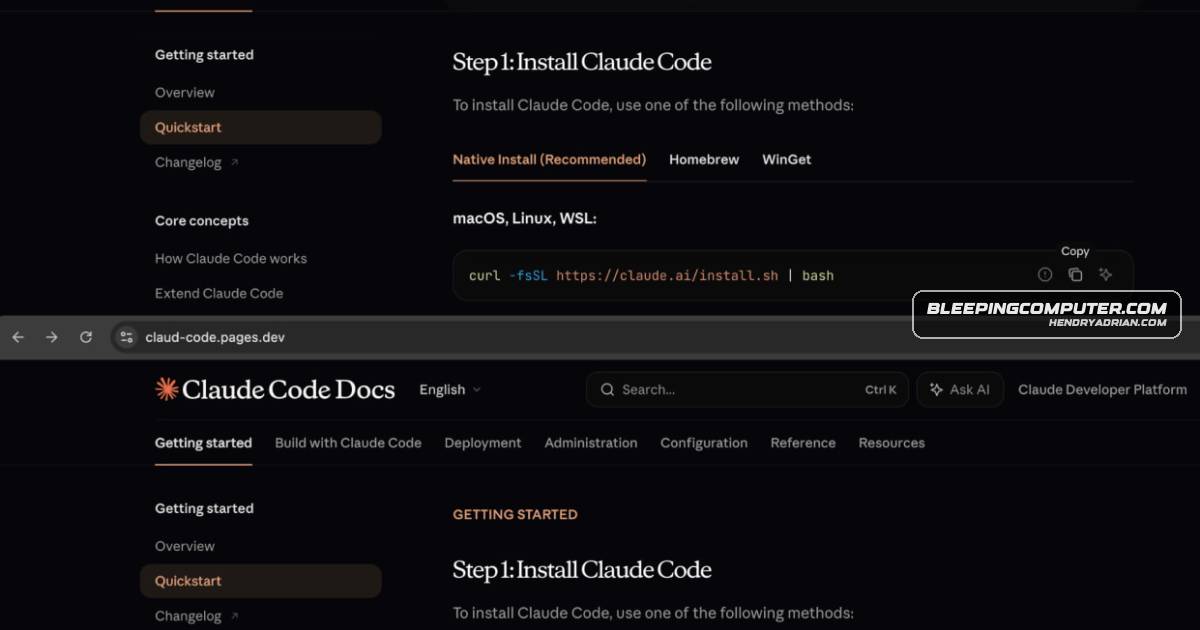
Fake Claude Code Install Guides Deliver Amatera Stealer via InstallFix Attacks

Attackers use cloned CLI installation pages and sponsored search results to trick users into running commands that deliver Amatera Stealer. The commands use different execution methods on macOS and Windows.

Mar 7, 2026
Security News · bleepingcomputer.com

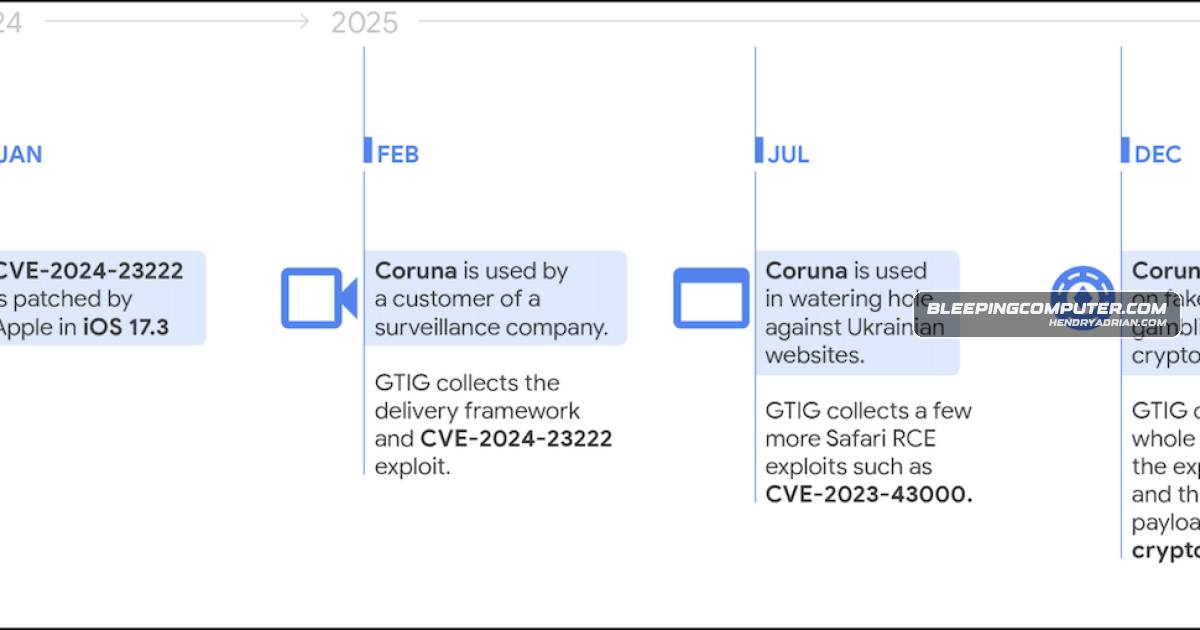
CISA Orders Federal Agencies to Patch iOS Flaws Used by Coruna

CISA added three iOS flaws exploited by Coruna to its KEV catalog and ordered federal agencies to mitigate them by March 26. GTIG reported the kit’s use in espionage and cryptocurrency theft, and said newer iOS versions block its exploits.

Mar 7, 2026
Security News · hackread.com

Bitdefender Reports APT36 Using AI-Generated ‘Vibeware’ Against Indian Government Targets

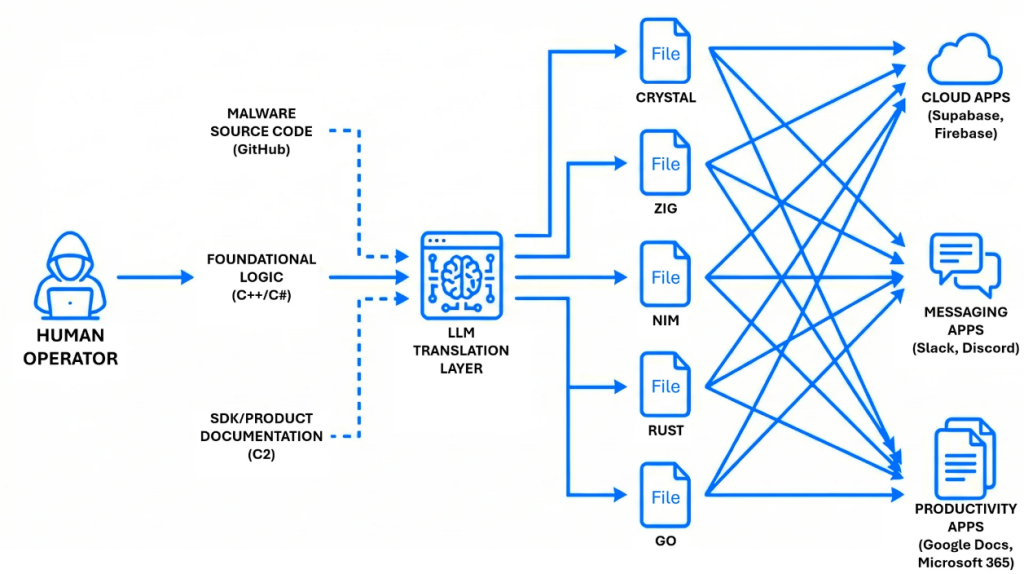
Bitdefender reports that APT36 is using high volumes of low-quality, AI-assisted malware against Indian government and diplomatic targets, including browser-data theft, modified shortcut lures, and cloud services for instructions and exfiltration.

Mar 7, 2026
PreviousPage 135 of 159 Next
© 2026 cyber.hendryadrian.com