
Fake Claude Code Install Guides Deliver Amatera Stealer via InstallFix Attacks
Summary
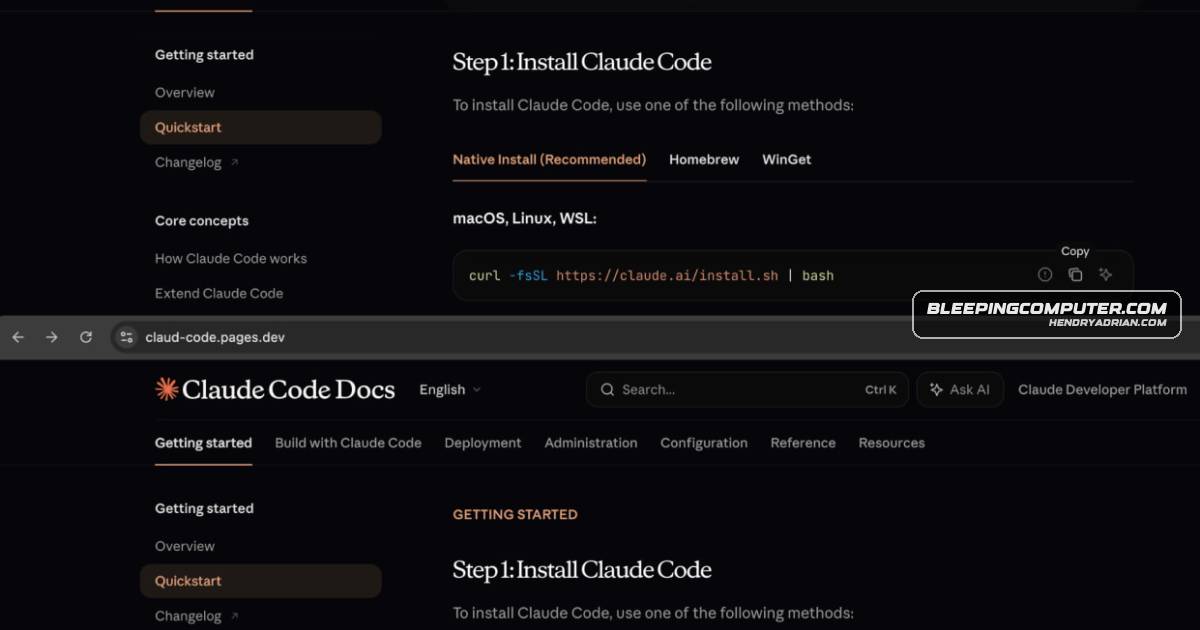
Attackers use cloned CLI installation pages and sponsored search results to trick users into running commands that deliver Amatera Stealer. The commands use different execution methods on macOS and Windows.
Key points
- Push Security reports that InstallFix, a ClickFix variant, uses cloned CLI installation pages with malicious commands.
- Attackers promote fake pages through sponsored search results, including ads for Claude Code installation queries.
- The macOS commands use base64-encoded instructions to download and run a binary; Windows commands use mshta.exe and conhost.exe.
- The delivered Amatera Stealer can steal credentials, browser cookies, session tokens, cryptocurrency wallets, and system information.
- The cloned pages are hosted on legitimate platforms, complicating efforts to identify them by hosting provider alone.
- Users should get installation instructions from official sites and avoid promoted search results.
Article Details
- Event Type
- InstallFix social-engineering attacks distributing Amatera Stealer through cloned CLI installation pages and promoted search results.
- Impact
- The commands can install Amatera Stealer on macOS and Windows systems. The malware can steal credentials, browser cookies, session tokens, cryptocurrency wallets, and system information.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | wriconsult[.]com | Attacker-controlled domain used to deliver a malware binary in an InstallFix attack; the article reports that it is currently down. |
| HOSTNAME | claude-code-cmd[.]squarespace[.]com | Specific Squarespace-hosted hostname serving a cloned Claude Code installation page with malicious commands, promoted in Google search results. |
MITRE ATT&CK
T1105 · Ingress Tool TransferThe macOS commands download a binary from an attacker-controlled domain.T1204.004 · Malicious Copy and PasteVictims are tricked into copying and running malicious installation commands presented on cloned CLI pages.T1218.005 · MshtaThe Windows command uses mshta.exe to retrieve malware.
Malware
ACR (AcridRain) StealerAmatera is a fairly new malware family, believed to be based on the ACR Stealer, sold as a subscription service (MaaS) to cybercriminals.Amatera StealerThe payload, Amatera stealer, exfiltrates credentials, cookies, session tokens, cryptocurrency wallets, and system information.
Vendors
Products
Claude CodeInstallFix clones legitimate CLI installation pages (e.g., Claude Code) to present malicious install commands.OpenClawIn a campaign last week, threat actors used the InstallFix technique with fake OpenClaw installers hosted in GitHub repositories that were promoted by Bing’s AI-enhanced search results.