cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3802 articles

Security News · cisecurity.org

CIS Updates Security Benchmarks for Windows, Cloud, Cassandra and More

CIS announced updates and new releases for benchmarks covering Windows, Oracle Cloud, Apache Cassandra, GitHub, Microsoft Defender, Intune for Edge, Apple platforms, and Debian Linux.

Mar 6, 2026
Security News · security.com

Seedworm Activity Found Across U.S. and Canadian Organizations as New Backdoors Emerge

A report links activity since February 2026 at U.S. and Canadian organizations to Seedworm, citing Dindoor and Fakeset backdoors and an attempted Rclone transfer to Wasabi whose success is unknown. It recommends stronger credential and exfiltration monitoring.

Mar 6, 2026
Security News · wiz.io

Wiz Introduces Tenant Manager for Centralized Multi-Tenant Cloud Security

Wiz Tenant Manager lets organizations aggregate security posture across cloud tenants, enforce shared policies, manage licenses, and access member environments through explicitly authorized, audited connections.

Mar 6, 2026
Security News · therecord.media

Phobos Ransomware Developer Pleads Guilty, Faces Up to 20 Years

Evgenii Ptitsyn pleaded guilty to wire fraud over his alleged role as a key Phobos ransomware developer and operator. He faces up to 20 years; prosecutors link Phobos and 8Base to attacks on more than 1,000 organizations.

Mar 6, 2026
Security News · therecord.media

Spanish Police Arrest 12 in Alleged $5.5 Million Gambling Fraud Scheme

Spanish police arrested 12 suspects after a two-year probe into a scheme that allegedly hijacked accounts opened by 55 displaced Ukrainian women, using stolen identities, compromised cards and betting bots to launder about $5.5 million.

Mar 6, 2026
Security News · securityonline.info

Report: Iranian-Nexus Actors Target Middle East IP Cameras for Reconnaissance

Check Point Research reports Iranian-nexus actors are exploiting known Hikvision and Dahua flaws to target Middle East IP cameras for reconnaissance and battle damage assessment, potentially supporting missile operations.

Mar 6, 2026
Security News · zscaler.com

ThreatLabz Finds Conflict-Themed Scams and Malware Campaigns Amid Middle East Tensions

ThreatLabz identified more than 8,000 conflict-themed domains and campaigns using lures, phishing sites, scams, and redirects to deliver StealC and the LOTUSLITE backdoor.

Mar 6, 2026
Security News · proofpoint.com

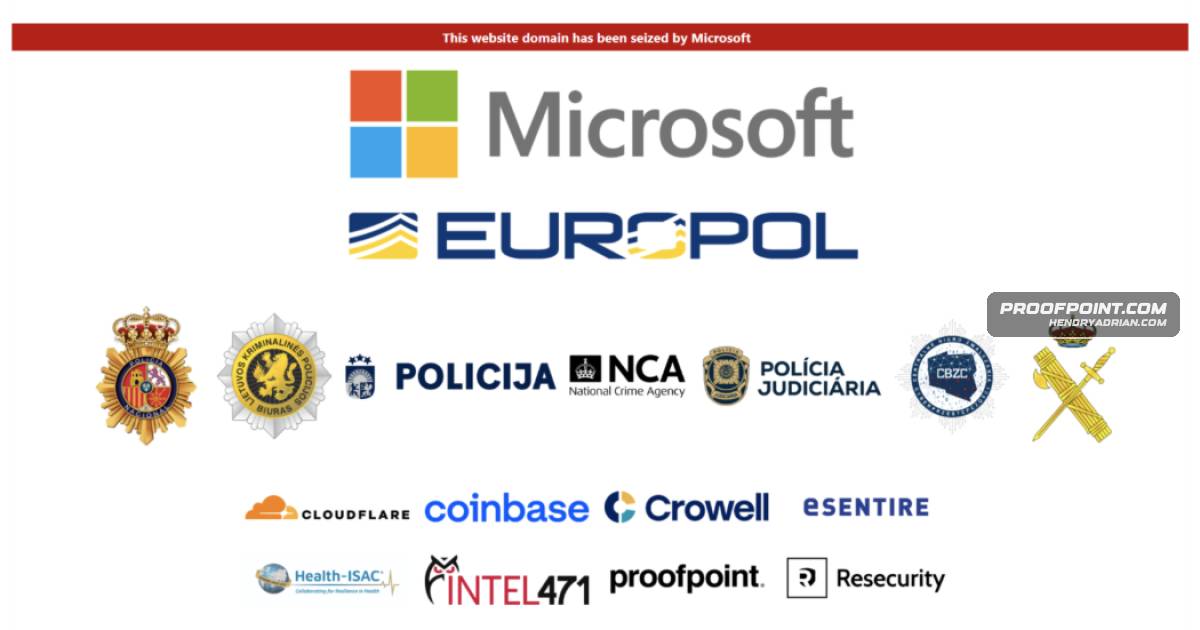
Microsoft Disrupts Tycoon 2FA, Seizing 330 Control Panel Domains

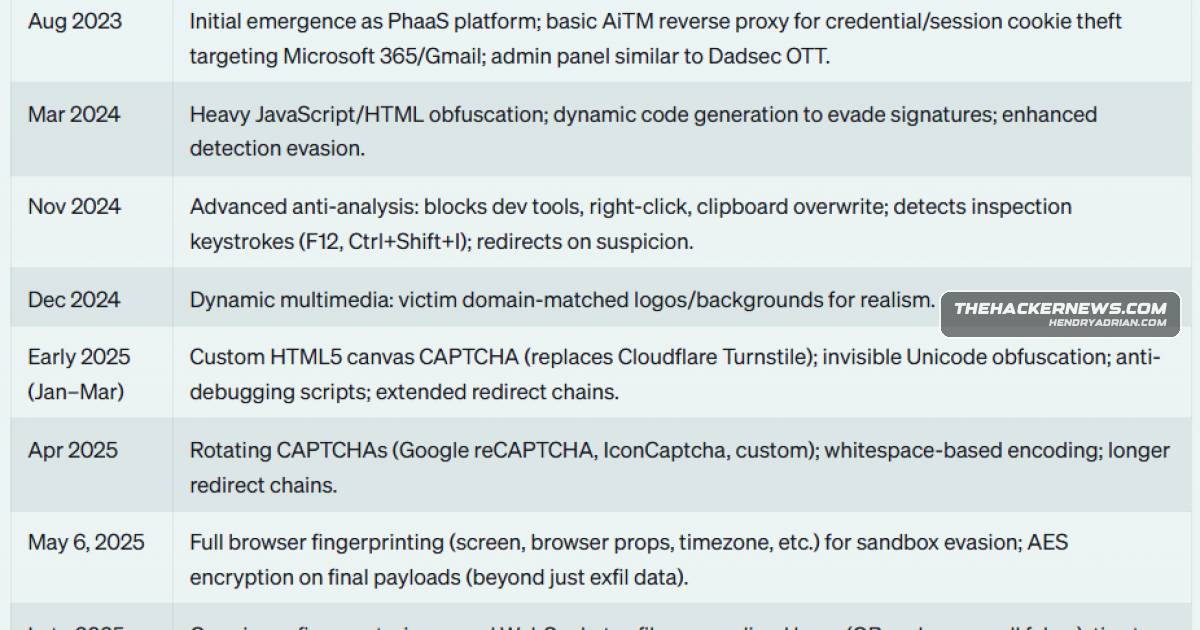
Microsoft and partners disrupted Tycoon 2FA on March 4, 2026, seizing 330 control-panel domains; Microsoft and Health-ISAC also sued its alleged creator. Proofpoint says the AiTM service stole credentials and session cookies to bypass MFA.

Mar 5, 2026
Security News · blogs.jpcert.or.jp

JSAC2026 Sessions Cover Malware Analysis, Phishing Threats and Security Operations

JPCERT/CC recaps JSAC2026 sessions on malware reverse engineering, phishing campaigns, spoofing risks in shared hosting, phishing-site investigations, and fraud prevention, alongside a discussion of 2025 security incidents.

Mar 5, 2026
Security News · bleepingcomputer.com

Spanish Police Dismantle Gambling Fraud Ring Exploiting Ukrainian Women

Spanish and Ukrainian authorities dismantled a gambling fraud operation that allegedly used stolen identities and accounts opened by exploited Ukrainian women to launder an estimated €4.75 million. Spanish police arrested 12 suspects.

Mar 5, 2026
Security News · therecord.media

Authorities Dismantle Tycoon 2FA Phishing Service, Seizing 330 Domains

Authorities dismantled Tycoon 2FA and seized 330 domains. The service intercepted login sessions and one-time codes to bypass MFA; Microsoft reported widespread targeting and operational disruptions at affected organizations.

Mar 5, 2026
Security News · thecyberexpress.com

Israel Says It Struck Iran’s Cyber Warfare Headquarters, Impact Unclear

Israel says it struck a Tehran compound housing Iran’s cyber warfare headquarters, but the impact is unclear. Researchers report that pre-positioned threats, an Android phishing campaign and hacktivist activity persist.

Mar 5, 2026
Security News · securityweek.com

Phobos Ransomware Operator Evgenii Ptitsyn Pleads Guilty in US

Evgenii Ptitsyn pleaded guilty to wire fraud conspiracy over his alleged role in the Phobos ransomware operation. Arrested in South Korea in 2024 and extradited to the US, he faces up to 20 years in prison.

Mar 5, 2026
Security News · theregister.com

Fake OpenClaw Installers Promoted by Bing AI Deliver Vidar and GhostSocks

Huntress researchers linked fake OpenClaw installers promoted through Bing AI search suggestions to Vidar and GhostSocks payloads. The malicious GitHub repositories and accounts were reported and removed.

Mar 5, 2026
Security News · securityaffairs.com

LastPass Warns of Phishing Emails Targeting Master Passwords

LastPass says an active phishing campaign, underway since about March 1, 2026, uses spoofed display names and fake security alerts to send users to a fraudulent SSO page that steals master passwords. The company is pursuing takedowns and urges caution.

Mar 5, 2026
Security News · securityweek.com

Reclaim Security Raises $20 Million in Series A Funding

Reclaim Security raised $20 million in a Series A round to expand engineering, integrations and sales. The startup says its AI-driven platform identifies exposures and helps organizations deploy remediations safely.

Mar 5, 2026
Security News · bleepingcomputer.com

Phobos Ransomware Administrator Pleads Guilty to Wire Fraud Conspiracy

Evgenii Ptitsyn pleaded guilty to wire fraud conspiracy for administering Phobos ransomware. Authorities say the operation collected over $39 million from more than 1,000 organizations; coordinated enforcement actions seized servers and led to arrests.

Mar 5, 2026
Security News · thehackernews.com

Europol-Led Operation Disrupts Tycoon 2FA Phishing Service, Taking Down 330 Domains

A coordinated law enforcement and industry operation dismantled Tycoon 2FA, a subscription AiTM phishing service, taking down 330 domains. Researchers and vendors linked it to tens of millions of phishing emails and large-scale account takeover attempts.

Mar 5, 2026
Security News · thecyberexpress.com

Florida Distributor Sentenced for Trafficking Microsoft COA Labels

Heidi Richards received a 22-month federal sentence and $50,000 fine after a jury convicted her of conspiring to traffic genuine Microsoft COA labels, whose product keys were allegedly extracted and sold in bulk.

Mar 5, 2026
Security News · securityweek.com

LeakBase Cybercrime Forum Shut Down in International Operation; Suspects Arrested

An international law-enforcement operation shut down LeakBase, seized its database and identified multiple users. Authorities arrested suspects and took unspecified measures against 37 of the forum’s most active users.

Mar 5, 2026
Security News · securityweek.com

Cisco Fixes 50 Vulnerabilities Across Enterprise Networking Products

Cisco released 25 advisories addressing 50 vulnerabilities, including two critical flaws in Secure FMC that could enable root access. Cisco says it is unaware of in-the-wild exploitation and advises users to update.

Mar 5, 2026
Security News · securityonline.info

CYFIRMA Reports Transparent Tribe Campaign Targeting Indian Government and Defense Organizations

CYFIRMA reports that Transparent Tribe (APT36) is targeting Indian government and defense organizations with social-engineered ZIPs, LNK and PPAM-based execution, and a RAT for covert monitoring and data exfiltration.

Mar 5, 2026
Security News · thecyberexpress.com

Europol-Led Operation Dismantles LeakBase Forum, Targets 37 Users

An international operation coordinated by Europol seized LeakBase, a stolen-data forum with more than 142,000 registered users. Authorities conducted about 100 enforcement actions and targeted 37 active users.

Mar 5, 2026
Security News · sysdig.com

February 2026 Security Briefing Highlights AI-Enabled Attacks and Supply-Chain Risks

Sysdig’s February 2026 briefing covers rapidly exploited vulnerabilities, a compromised Cline CLI update, AI-enabled attacks, and reported data exposures. It recommends stronger identity controls, token rotation, AI inventory, patching, and active detection.

Mar 5, 2026
PreviousPage 136 of 159 Next
© 2026 cyber.hendryadrian.com