
ShinyHunters Claims Ongoing Salesforce Aura Data-Theft Campaign
Summary
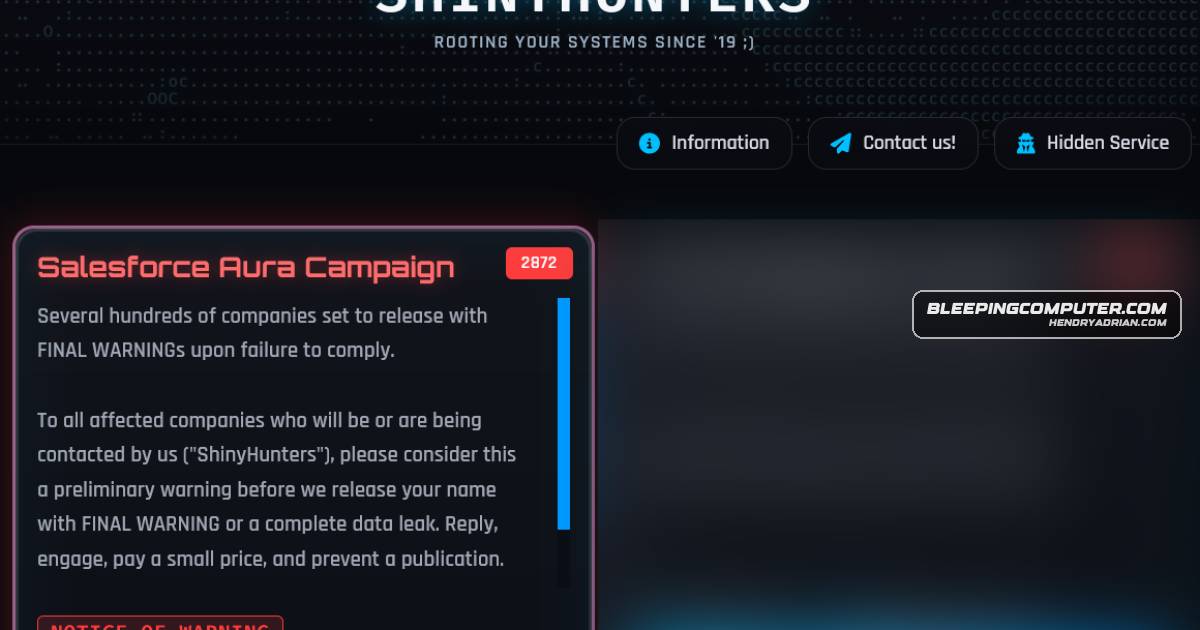
Salesforce says attackers are abusing misconfigured Experience Cloud guest permissions via the Aura API, not a platform flaw. ShinyHunters claims hundreds of victims, but the claims are unverified. Salesforce recommends restricting guest access and monitoring Aura logs.
Key points
- Salesforce says attackers can use the /s/sfsites/aura API to query CRM objects without authentication when Experience Cloud guest profiles have excessive permissions; it says this is not a platform vulnerability.
- ShinyHunters claims around 100 high-profile companies and 300–400 organizations were compromised; the claims have not been independently confirmed.
- Salesforce says a modified AuraInspector tool was used to mass-scan public-facing Experience Cloud sites. Mandiant cautions that scan activity in an organization’s logs does not by itself indicate compromise.
- ShinyHunters says it modified AuraInspector for reconnaissance and built custom data-theft tooling. Its claims about bypassing Salesforce’s 2,000-record query limit and finding a further data-theft method remain unverified.
- Salesforce recommends reducing guest permissions, disabling guest access to public APIs and the API Enabled setting, setting external org-wide defaults to Private, and disabling unnecessary visibility and self-registration settings.
- Administrators are advised to review Aura Event Monitoring logs for unusual access and queries, and to designate a Security Contact.
Article Details
- Event Type
- Reported data-theft campaign targeting misconfigured Salesforce Experience Cloud guest-user access. ShinyHunters claims responsibility and alleges a newer vulnerability is being exploited, but that claim has not been independently confirmed; Salesforce says the activity stems from customer-configured settings, not a platform vulnerability.
- Impact
- Misconfigured guest permissions can allow unauthenticated visitors to query Salesforce CRM data. ShinyHunters claims it compromised around 100 high-profile companies and told BleepingComputer that the total number of breached organizations is between 300 and 400; these figures are unverified.
MITRE ATT&CK
People
Threat Actors
Vendors
MandiantMandiant and Salesforce are sharing detection guidance; orgs should monitor Aura Event Monitoring logs and designate a security contact.SalesforceSalesforce warns that attackers are scanning misconfigured Experience Cloud sites and abusing the /s/sfsites/aura API endpoint to let guest users query CRM data without authentication.