
CISA Orders Federal Agencies to Patch iOS Flaws Used by Coruna
Summary
CISA added three iOS flaws exploited by Coruna to its KEV catalog and ordered federal agencies to mitigate them by March 26. GTIG reported the kit’s use in espionage and cryptocurrency theft, and said newer iOS versions block its exploits.
Key points
- CISA added three of the 23 iOS vulnerabilities targeted by Coruna to its Known Exploited Vulnerabilities catalog; FCEB agencies must secure devices by March 26 under BOD 22-01.
- GTIG reported that Coruna uses multiple exploit chains against 23 iOS vulnerabilities, many deployed as zero-days.
- On vulnerable devices, Coruna can enable WebKit remote code execution, PAC, sandbox and PPL bypasses, and kernel privilege escalation.
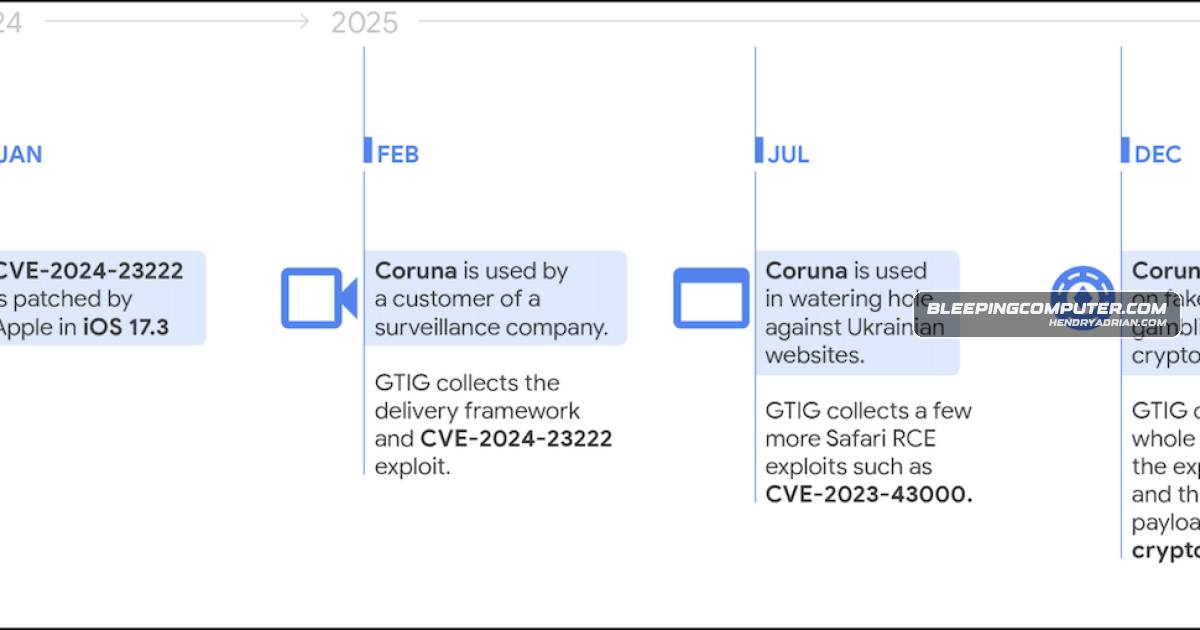
- GTIG observed Coruna use by a surveillance-vendor customer, suspected Russian state-backed group UNC6353, and financially motivated actor UNC6691.
- GTIG reported that UNC6691 used fake gambling and cryptocurrency websites to deliver malware designed to steal cryptocurrency wallets.
- The article says the exploits do not work on recent iOS versions and can be blocked by private browsing or Apple Lockdown Mode; CISA urged all organizations to prioritize patching.
Article Details
- Event Type
- CISA directive to patch iOS vulnerabilities exploited by the Coruna exploit kit
- Impact
- Coruna exploit chains can achieve WebKit remote code execution and kernel privilege escalation, enabling surveillance and cryptocurrency theft. The exploits do not work on recent iOS versions and can be blocked by private browsing or Apple’s Lockdown Mode.