
Velvet Tempest Used ClickFix to Deploy CastleRAT in Emulated Intrusion
Summary
MalBeacon observed Velvet Tempest use a ClickFix lure to stage DonutLoader and retrieve CastleRAT in a 12-day emulated intrusion. The researchers said Termite ransomware was not deployed.
Key points
- MalBeacon observed the activity from February 3 to 16 in an emulated U.S. nonprofit environment with more than 3,000 endpoints and 2,500 users.
- A malvertising ClickFix/CAPTCHA lure prompted victims to paste an obfuscated command into the Windows Run dialog.
- The operators used nested cmd.exe chains, finger.exe, PowerShell, and csc.exe to fetch, compile, and execute payloads.
- The intrusion staged DonutLoader and retrieved the CastleRAT backdoor; Python-based components were used for persistence.
- Researchers said a PowerShell script harvested credentials stored in Chrome. Its hosting IP was linked to tool staging for Termite ransomware intrusions.
- Velvet Tempest, also tracked as DEV-0504, did not deploy Termite ransomware during this observed emulated intrusion.
Article Details
- Event Type
- Emulated intrusion involving a ClickFix malvertising lure and deployment of DonutLoader and CastleRAT, attributed by MalBeacon to Velvet Tempest.
- Impact
- In the 12-day emulated intrusion, operators reportedly harvested credentials stored in Chrome and staged DonutLoader and CastleRAT. MalBeacon reported that Termite ransomware was not deployed in this intrusion; the article does not report impact to a real victim organization.
MITRE ATT&CK
T1059.001 · PowerShellOperators used PowerShell to download and execute commands and additional payloads.T1059.003 · Windows Command ShellThe pasted command triggered nested cmd.exe chains.T1105 · Ingress Tool TransferThe operators used finger.exe and PowerShell to retrieve malware loaders and additional payloads.T1204.004 · Malicious Copy and PasteVictims were instructed to paste an obfuscated command into the Windows Run dialog as part of the ClickFix/CAPTCHA lure.T1555.003 · Credentials from Web BrowsersA PowerShell script was used to harvest credentials stored in Chrome.
Threat Actors
DEV-0504The article identifies DEV-0504 as another tracking name for Velvet Tempest, which MalBeacon attributed with the observed ClickFix intrusion.Velvet TempestMalBeacon attributed the ClickFix intrusion and deployment of DonutLoader and CastleRAT in its emulated environment to Velvet Tempest. The article also describes the group as a ransomware affiliate.
Malware
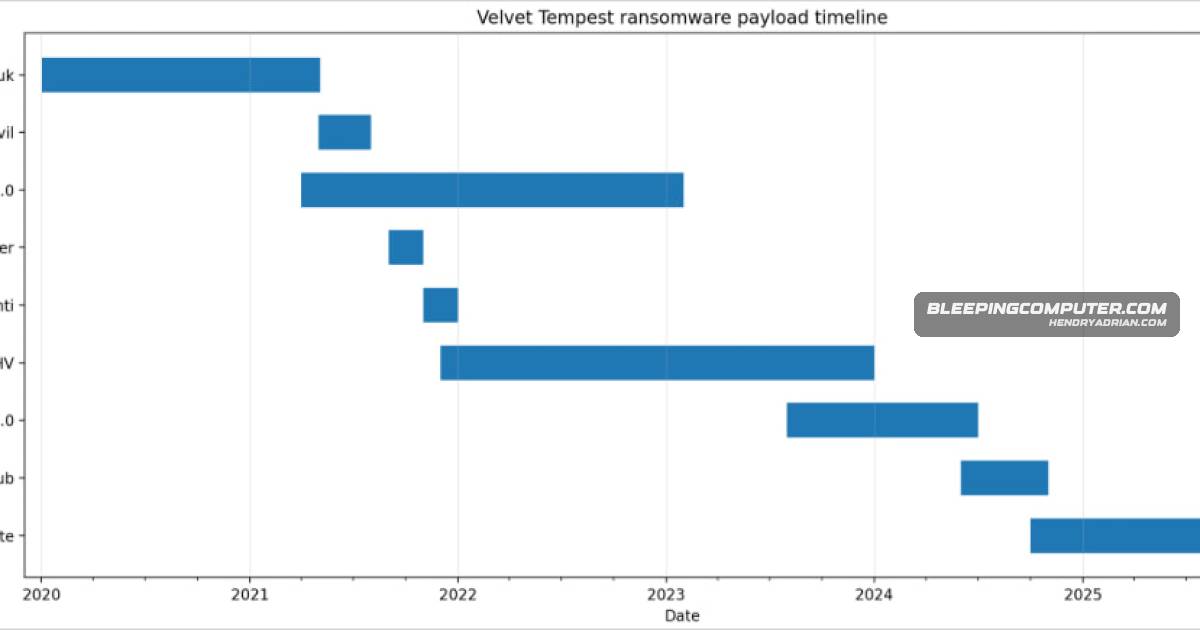
BlackCat/ALPHVThe actor has been associated with deploying some of the most devastating ransomware strains: Ryuk (2018 – 2020), REvil (2019-2022), Conti (2019-2022), BlackMatter, BlackCat/ALPHV (2021-2024), LockBit, and RansomHub.BlackMatterThe actor has been associated with deploying some of the most devastating ransomware strains: Ryuk (2018 – 2020), REvil (2019-2022), Conti (2019-2022), BlackMatter, BlackCat/ALPHV (2021-2024), LockBit, and RansomHub.CastleLoaderThe campaign staged DonutLoader and retrieved the CastleRAT backdoor, a RAT linked to CastleLoader and information stealers like LummaStealer.CastleRATResearchers at MalBeacon observed Velvet Tempest use a ClickFix malvertising lure and legitimate Windows utilities to stage DonutLoader and retrieve the CastleRAT backdoor during a 12âday emulated intrusion.ContiThe actor has been associated with deploying some of the most devastating ransomware strains: Ryuk (2018 – 2020), REvil (2019-2022), Conti (2019-2022), BlackMatter, BlackCat/ALPHV (2021-2024), LockBit, and RansomHub.DonutLoaderResearchers at MalBeacon observed Velvet Tempest use a ClickFix malvertising lure and legitimate Windows utilities to stage DonutLoader and retrieve the CastleRAT backdoor during a 12âday emulated intrusion.LockBitThe actor has been associated with deploying some of the most devastating ransomware strains: Ryuk (2018 – 2020), REvil (2019-2022), Conti (2019-2022), BlackMatter, BlackCat/ALPHV (2021-2024), LockBit, and RansomHub.LummaStealerThe campaign staged DonutLoader and retrieved the CastleRAT backdoor, a RAT linked to CastleLoader and information stealers like LummaStealer.RansomHubThe actor has been associated with deploying some of the most devastating ransomware strains: Ryuk (2018 – 2020), REvil (2019-2022), Conti (2019-2022), BlackMatter, BlackCat/ALPHV (2021-2024), LockBit, and RansomHub.REvilThe actor has been associated with deploying some of the most devastating ransomware strains: Ryuk (2018 – 2020), REvil (2019-2022), Conti (2019-2022), BlackMatter, BlackCat/ALPHV (2021-2024), LockBit, and RansomHub.RyukThe actor has been associated with deploying some of the most devastating ransomware strains: Ryuk (2018 – 2020), REvil (2019-2022), Conti (2019-2022), BlackMatter, BlackCat/ALPHV (2021-2024), LockBit, and RansomHub.TermiteVelvet Tempest (DEVâ0504) is a longârunning ransomware affiliate tied to multiple strains, though Termite ransomware was not deployed in this observed intrusion.
Products
Google Chromeand environment profiling, as well as using a PowerShell script to harvest credentials stored in Chrome.Microsoft WindowsResearchers at MalBeacon observed Velvet Tempest use a ClickFix malvertising lure and legitimate Windows utilities to stage DonutLoader and retrieve the CastleRAT backdoor during a 12âday emulated intrusion.