cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · cyberbuilders.substack.com

Mythos Marks an Acceleration in AI-Driven Vulnerability Discovery, Not a Beginning

The author argues that Mythos accelerates an existing trend in AI-assisted vulnerability discovery, citing vendor and open-source examples, while warning that organizations may struggle to triage and remediate the growing volume of findings.
Apr 23, 2026
Security Insights · darkowl.com

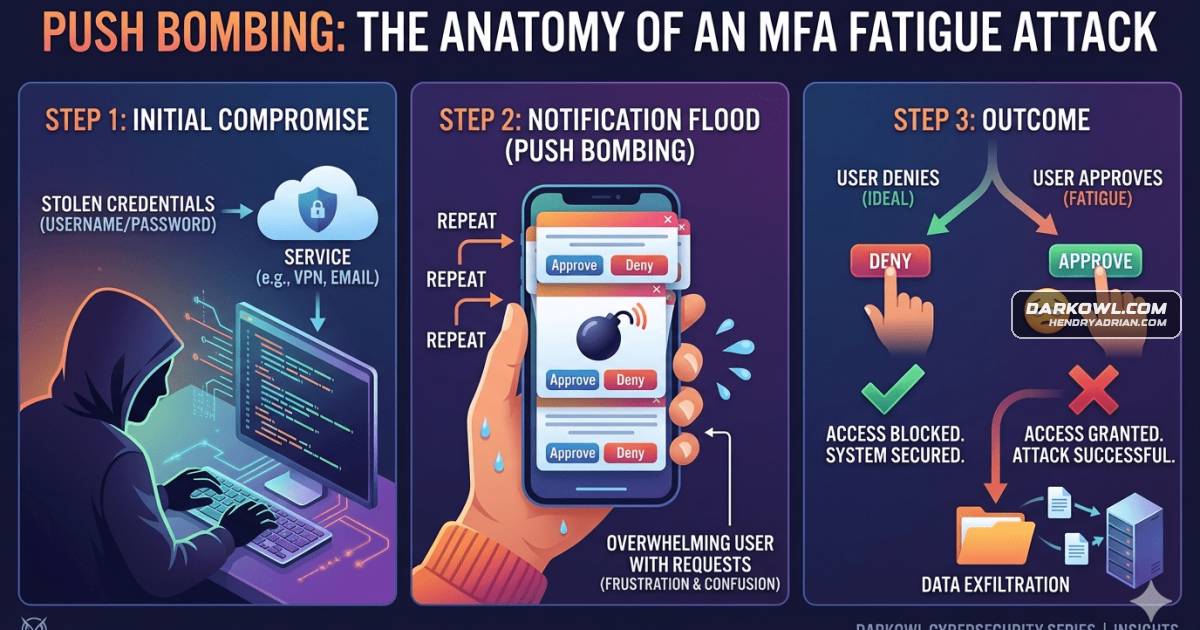
What Is MFA Push Bombing? How Attackers Exploit Repeated Prompts

Push bombing, or MFA fatigue, overwhelms users with repeated login prompts after credentials are stolen, hoping they approve one. The article describes Uber and Cisco incidents and recommends phishing-resistant MFA and reporting unexpected prompts.

Apr 23, 2026
Security Insights · helpnetsecurity.com

Zoom CISO Sandra McLeod on Security Strategy and Leadership

After a year as Zoom’s CISO, Sandra McLeod reflects on shifting from reactive incident response to strategic security leadership, balancing risk reduction with business goals, and taking responsibility for incident escalation and prevention.

Apr 23, 2026
Security Insights · huntress.com

Huntress Shares Practical Cyber Hygiene Tips for Organizations

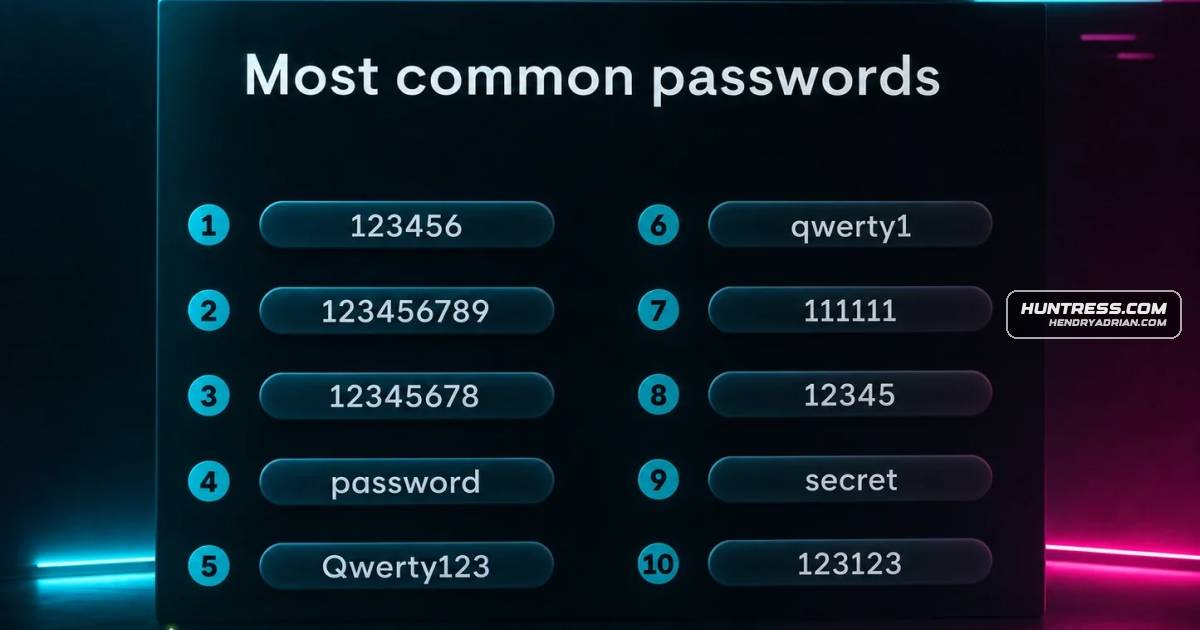
Huntress outlines ongoing security practices for organizations, including MFA, phishing awareness, patching, strong passwords, limiting exposed RDP, monitoring, access controls, logging, backups, and least privilege.

Apr 23, 2026
Security Insights · huntress.com

MFA Guide Explains Authentication Methods, Bypass Risks and Safer Rollout

A practical MFA guide explains authentication factors, phishing and bypass risks, and organizational rollout. It recommends prioritizing privileged accounts and favoring authenticator apps or phishing-resistant keys over SMS.

Apr 23, 2026
Security Insights · hackingarticles.in

CloudGoat Lab Demonstrates AWS Credential Theft Through EC2 SSRF

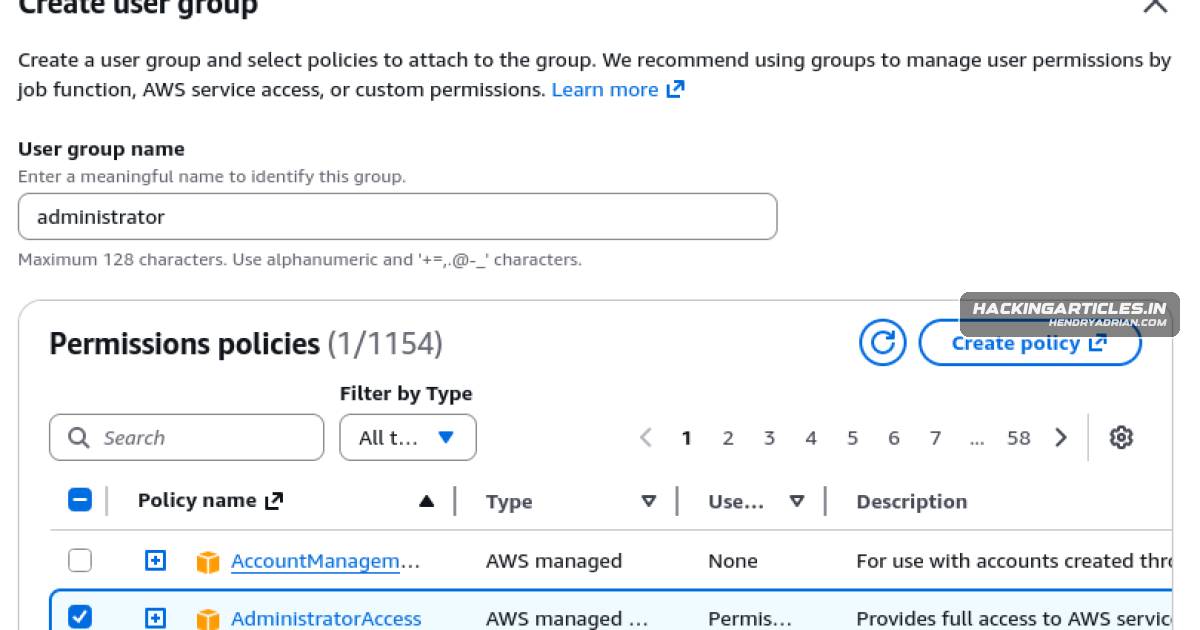
A CloudGoat walkthrough shows how SSRF in an EC2-hosted application can expose IMDS credentials and enable privilege escalation through Lambda, EC2 and S3. It recommends enforcing IMDSv2, restricting requests and using least-privilege IAM.

Apr 22, 2026
Security Insights · cyberscoop.com

AI-Era Threats Require CISOs to Move Beyond Static Risk Measures

An op-ed argues that AI-driven threat acceleration makes static audits and posture snapshots insufficient, urging CISOs to prioritize runtime visibility, identity inventory, least privilege, contextual alert triage, and realistic incident rehearsals.

Apr 22, 2026
Security Insights · cyfirma.com

Profile: Red Menshen Uses BPFDoor for Stealthy Telecom Espionage

The profile describes China-linked Red Menshen’s alleged use of BPFDoor, a packet-triggered Linux backdoor, to maintain stealthy access. It highlights telecom and network-edge targeting, exploitation for initial access, and multi-stage post-compromise tools.

Apr 22, 2026
Security Insights · sysdig.com

Sysdig Urges Defenders to Prepare for AI-Accelerated Vulnerability Discovery

Sysdig argues that Claude Mythos’s reported vulnerability discoveries signal faster AI-enabled offense and urges security teams to expand AI-assisted code review, continuous patching, automated response, governance and agent measurement.

Apr 22, 2026
Security Insights · bleepingcomputer.com

Flare Analysis Details the Organized Hiring Model Behind Scam-Call Operations

Flare’s sponsored analysis describes scam-call operations using specialized roles, underground recruitment, real-time supervision and performance-based pay, and recommends stronger identity checks, anomaly detection and awareness of social-engineering calls.

Apr 22, 2026
Security Insights · huntress.com

Attackers Are Building Workflows Around AI, Not Just Using AI Tools

Huntress describes attacks using malicious search results, fake AI-style instructions and AI-assisted phishing infrastructure to blend into trusted workflows and scale credential theft and identity attacks.

Apr 22, 2026
Security Insights · bleepingcomputer.com

Using Risk Signals to Detect Fraud Across Signup, Login and Checkout

An IPQS-sponsored article outlines using email, phone, device, location, session, identity and payment signals at signup, login and checkout, with risk-based verification to detect fraud while limiting friction for legitimate users.

Apr 21, 2026
Security Insights · cyberscoop.com

Mythos Advances Vulnerability Discovery, but Enterprise Response Still Needs Human Oversight

The article says Mythos advances AI vulnerability discovery but does not make enterprise exploitation automatic. It urges defenders to use auditable, context-aware AI to improve prioritization and remediation while keeping humans involved.

Apr 21, 2026
Security Insights · toxsec.com

Guide Details Five Jailbreak Families for Testing Claude Opus 4.7’s Cyber Safeguards

The guide describes five prompt-jailbreak families for probing Claude Opus 4.7’s cyber safeguards, outlines use of PyRIT, Garak and Promptfoo, and discusses multi-turn testing and Anthropic’s bug-bounty program.

Apr 20, 2026
Security Insights · thehackernews.com

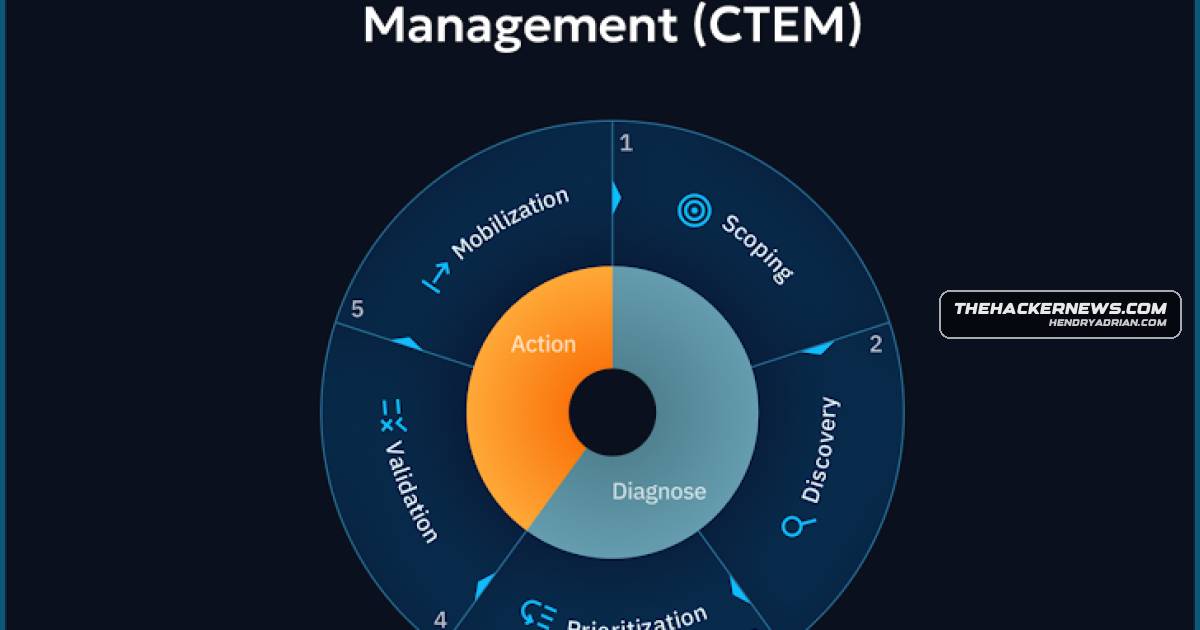
How Threat Intelligence Can Improve CTEM Prioritization and Validation

The article explains how structured threat intelligence can help organizations prioritize CTEM exposures by asset criticality, exploitability, and adversary relevance, then validate controls with threat-aligned simulations.

Apr 20, 2026
Security Insights · darkreading.com

Excel XSS Could Let Copilot Agent Exfiltrate Spreadsheet Data, Opinion Warns

The article says Microsoft patched an Excel XSS flaw that could let a malicious file hijack Copilot Agent to exfiltrate spreadsheet data. It argues AI agents amplify traditional vulnerabilities and recommends egress controls, monitoring, permission reviews, and reprior.

Apr 19, 2026
Security Insights · netspi.com

ForceHound Maps Salesforce Permissions in BloodHound CE for Security Audits

ForceHound builds BloodHound CE graphs of Salesforce identities and permissions. The article explains API and Aura collection, empirical CRUD testing, graph integration, audit logging, and scope controls for security assessments.

Apr 18, 2026
Security Insights · hackingarticles.in

How to Build an Active Directory Penetration-Testing Lab with PowerShell

Walkthrough builds an isolated two-VM Active Directory lab on Windows Server 2019 and Windows 10, configures AD DS and AD CS, creates deliberately overprivileged accounts, and disables Defender and the firewall for testing, with a warning not to use those settings in or

Apr 18, 2026
Security Insights · netspi.com

Using ForceHound to Map Salesforce Privilege-Escalation Paths

A walkthrough shows how ForceHound loads Salesforce identity and entitlement data into BloodHound to map privilege-escalation paths, Connected App access, and object permissions, including legacy authorizations not addressed by Salesforce’s 2025 restrictions.

Apr 18, 2026
Security Insights · bleepingcomputer.com

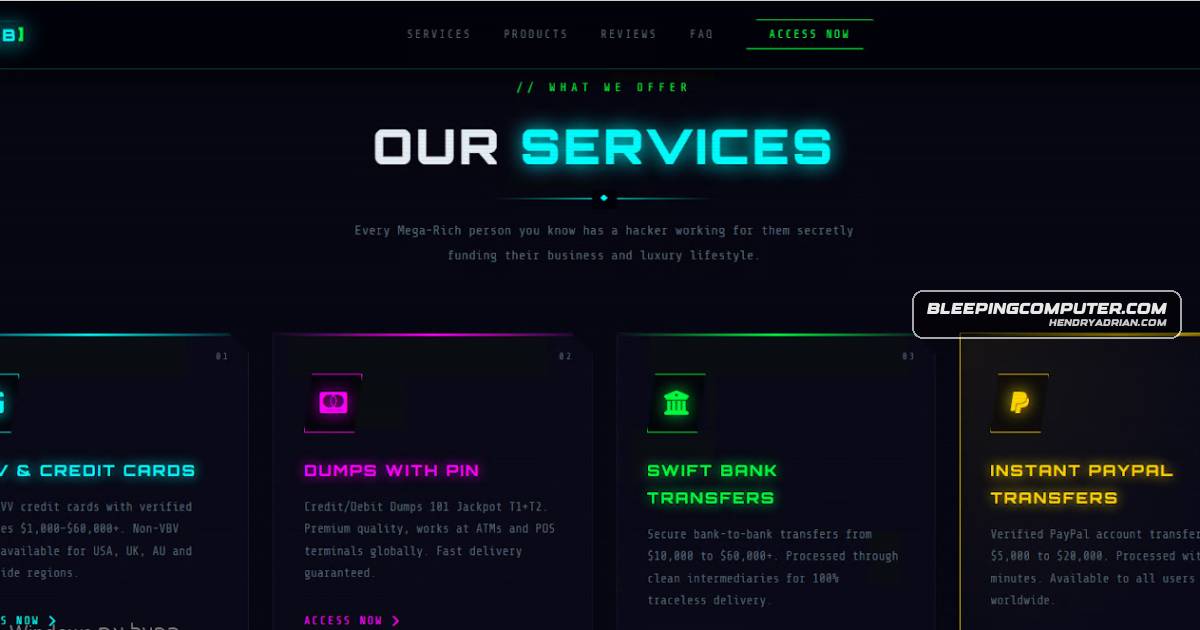
Underground Guide Details How Carding Actors Vet Stolen Credit Card Shops

A Flare-analyzed underground forum guide describes how carding actors vet stolen-card shops, assess supplier reliability, and use layered operational security. The article notes the guide may promote specific services.

Apr 17, 2026
Security Insights · forcepoint.com

Simulated AI Attack Chain Shows Path from Prompt Injection to CI/CD Code Execution

A local Python and Flask simulation demonstrates how prompt injection could expose an admin token, enable MCP server and model compromise, and lead to code execution through an unsafe CI/CD deploy endpoint.

Apr 17, 2026
Security Insights · hackingarticles.in

Walkthrough Demonstrates Seven Ways to Enable RDP Remotely on a Windows Domain Controller

A hands-on walkthrough demonstrates seven ways to enable RDP on a Windows Server 2019 domain controller using credentials or hashes over SMB, WMI, WinRM, and RPC, then connect from Kali; it also outlines hardening and detection measures.

Apr 17, 2026
Security Insights · cisecurity.org

CIS’s Tony Sager Reflects on AI Governance and Cybersecurity Priorities at RSAC 2026

Tony Sager’s RSAC 2026 reflections emphasize separating AI governance from AI-assisted GRC, grounding trust in established security practices, and sustaining cybersecurity work through practical outcomes, outreach, visibility, and partnerships.

Apr 16, 2026
Security Insights · bleepingcomputer.com

Why AI SOCs Need End-to-End Workflows, Not Just Faster Triage

This sponsored article argues that AI SOC tools often stop at triage. Scaling their value requires integrated, auditable workflows combining AI agents, deterministic automation, and human oversight, plus testing execution in the buyer’s own environment.

Apr 16, 2026
PreviousPage 33 of 54 Next
© 2026 cyber.hendryadrian.com