Attackers Are Building Workflows Around AI, Not Just Using AI Tools
Summary
Huntress describes attacks using malicious search results, fake AI-style instructions and AI-assisted phishing infrastructure to blend into trusted workflows and scale credential theft and identity attacks.
Key points
- A Huntress engineer clicked a sponsored search result for Claude Code that delivered credential-stealing malware; a fast SOC response prevented a full incident.
- An AMOS stealer campaign used pages imitating AI conversations to persuade macOS users to run Terminal commands that exposed credentials, compromised systems and installed persistent malware.
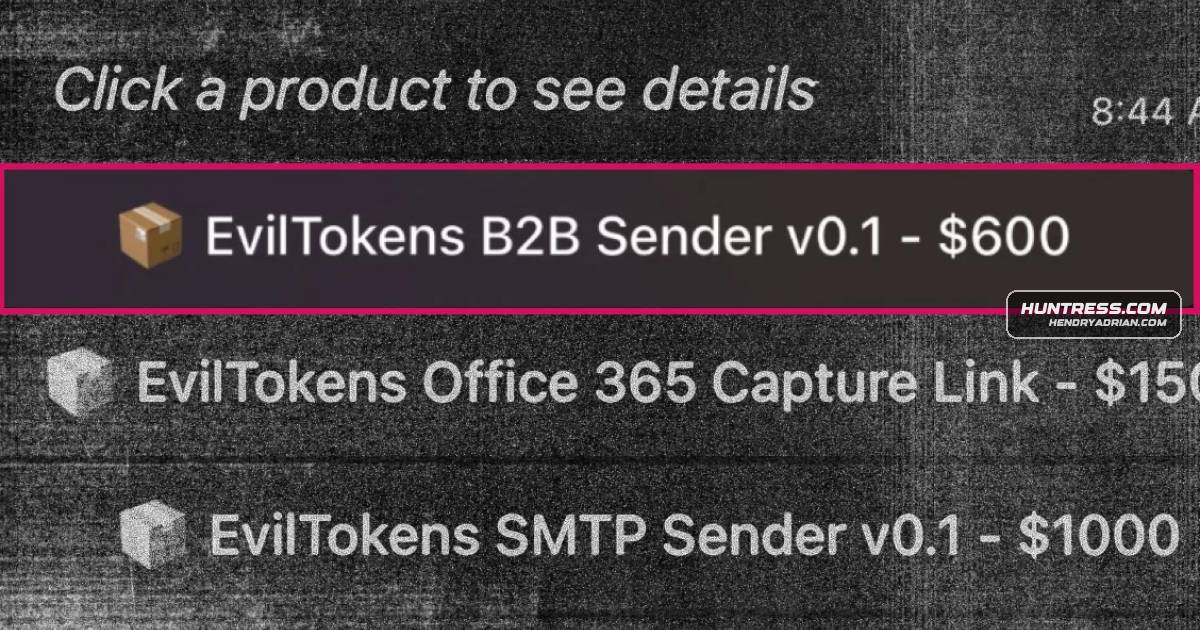
- Huntress says EvilTokens products use AI workflows to tailor phishing lures, evade email filtering and identify sensitive conversations for fraud or data theft.
- The article reports that attackers used Railway to deploy session-token theft infrastructure on demand, affecting hundreds of organizations globally in a matter of weeks.
- Huntress’s central argument is that attackers exploit trusted search, AI-style answers and identity workflows, making malicious activity resemble normal user behavior.
Article Details
- Topic
- AI-enabled cybercrime workflows, including malicious search results, AI-styled malware delivery instructions, and scalable phishing infrastructure.
People
Casey SmithHuntress Principal Researcher, Identity Threats; listed as a speaker for the EvilTokens session.Chris HendersonHuntress CISO quoted about incidents blending in with normal activity.Eric StrideHuntress Chief Security Officer quoted about malicious sponsored search results.John HammondHuntress Senior Principal Security Researcher quoted discussing threat actors’ adoption of AI.Sherrod DeGrippoMicrosoft Partner GM of Global Threat Intelligence; listed as a speaker for the EvilTokens session.
Malware
Products
ChatGPTRight now, users are searching for and downloading AI tools, like Claude Code, ChatGPT integrations, and developer assistants, often multiple times a day.Claude CodeRight now, users are searching for and downloading AI tools, like Claude Code, ChatGPT integrations, and developer assistants, often multiple times a day.EvilTokensOperations like EvilTokens highlight that shift.GrokIn a recent AMOS stealer campaign, users searching for something as routine as “clear disk space on macOS” were served results that looked like ChatGPT or Grok conversations.RailwayBy early 2026, attackers were already using platforms like Railway to spin up session token theft infrastructure on demand, impacting hundreds of organizations globally in a matter of weeks.