
CloudGoat Lab Demonstrates AWS Credential Theft Through EC2 SSRF
Summary
A CloudGoat walkthrough shows how SSRF in an EC2-hosted application can expose IMDS credentials and enable privilege escalation through Lambda, EC2 and S3. It recommends enforcing IMDSv2, restricting requests and using least-privilege IAM.
Key points
- The intentionally vulnerable CloudGoat ec2_ssrf scenario models an EC2-hosted application that can be abused to access the Instance Metadata Service.
- The walkthrough demonstrates retrieving IAM role credentials through SSRF and using them to enumerate AWS resources.
- Credentials discovered in Lambda environment variables and S3 are used in the lab to pivot identities and escalate privileges.
- The article recommends requiring IMDSv2, restricting metadata access and outbound requests, and applying least-privilege IAM roles.
- The author advises destroying the lab environment after testing to avoid ongoing AWS charges.
Article Details
- Topic
- CloudGoat ec2_ssrf lab demonstrating SSRF-based access to EC2 instance metadata, IAM credential exposure, credential pivoting, and privilege escalation in AWS.
MITRE ATT&CK
T1078.004 · Cloud AccountsThe demonstrated attack uses discovered AWS credentials to authenticate as cloud identities and access additional resources.T1190 · Exploit Public-Facing ApplicationThe lab demonstrates exploiting an SSRF vulnerability in an EC2-hosted web application.T1526 · Cloud Service DiscoveryThe walkthrough uses obtained AWS credentials to enumerate Lambda functions, EC2 instances, and S3.T1530 · Data from Cloud StorageThe lab downloads a credentials object from an S3 bucket.T1552.005 · Cloud Instance Metadata APIThe SSRF is used to query the EC2 Instance Metadata Service and retrieve IAM role credentials.T1619 · Cloud Storage Object DiscoveryThe walkthrough lists an S3 bucket and enumerates its contents.
Vendors
Products
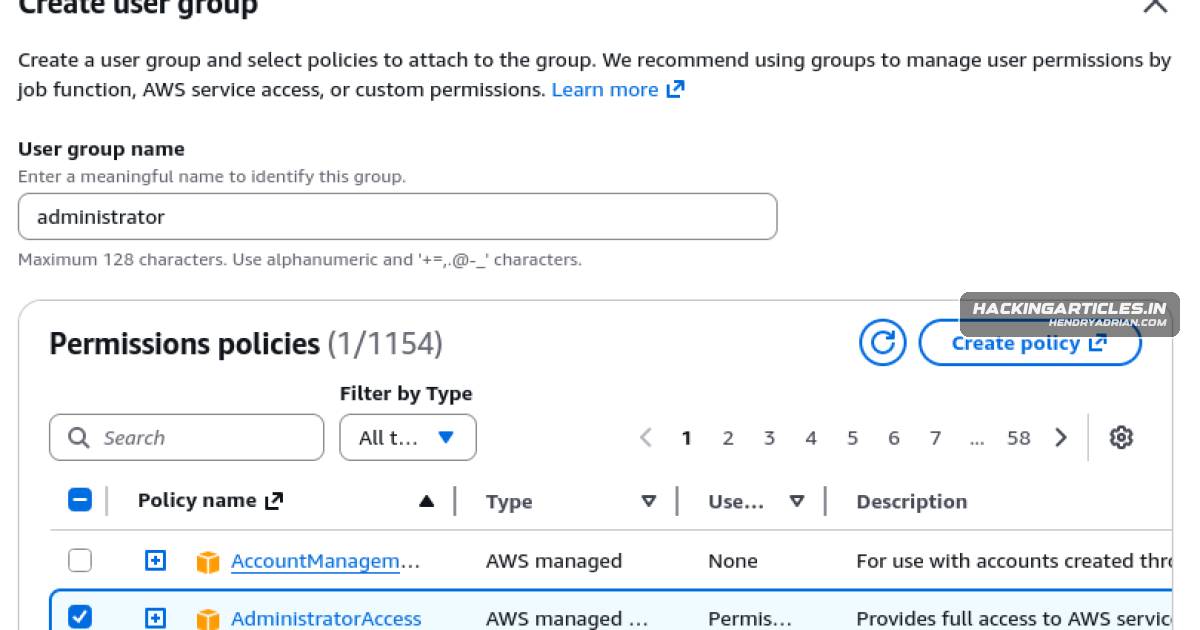
AWS Instance Metadata Serviceexploit a Server-Side Request Forgery (SSRF) in an EC2-hosted web application to access the AWS Instance Metadata Service and steal IAM credentials.AWS LambdaThe step-by-step walkthrough covers lab setup, enumeration of Lambda, EC2, and S3, credential pivoting to escalate privileges, and recommendations such as enforcing IMDSv2 and least-privilege IAM to mitigate the risk.EC2ec2_ssrf lab that demonstrates how an attacker can exploit a Server-Side Request Forgery (SSRF) in an EC2-hosted web application to access the AWS Instance Metadata Service and steal IAM credentials.IAMForgery (SSRF) in an EC2-hosted web application to access the AWS Instance Metadata Service and steal IAM credentials.S3The step-by-step walkthrough covers lab setup, enumeration of Lambda, EC2, and S3, credential pivoting to escalate privileges, and recommendations such as enforcing IMDSv2 and least-privilege IAM to mitigate the risk.
Tools
AWS CLIThe walkthrough details setup steps including IAM configuration, Terraform, AWS CLI, and launching the ec2_ssrf scenario.CloudGoatThis article walks through a CloudGoat ec2_ssrf lab that demonstrates how an attacker can exploit a Server-Side Request Forgery (SSRF) in an EC2-hosted web application to access the AWS Instance Metadata Service andTerraformThe walkthrough details setup steps including IAM configuration, Terraform, AWS CLI, and launching the ec2_ssrf scenario.