What Is MFA Push Bombing? How Attackers Exploit Repeated Prompts
Summary
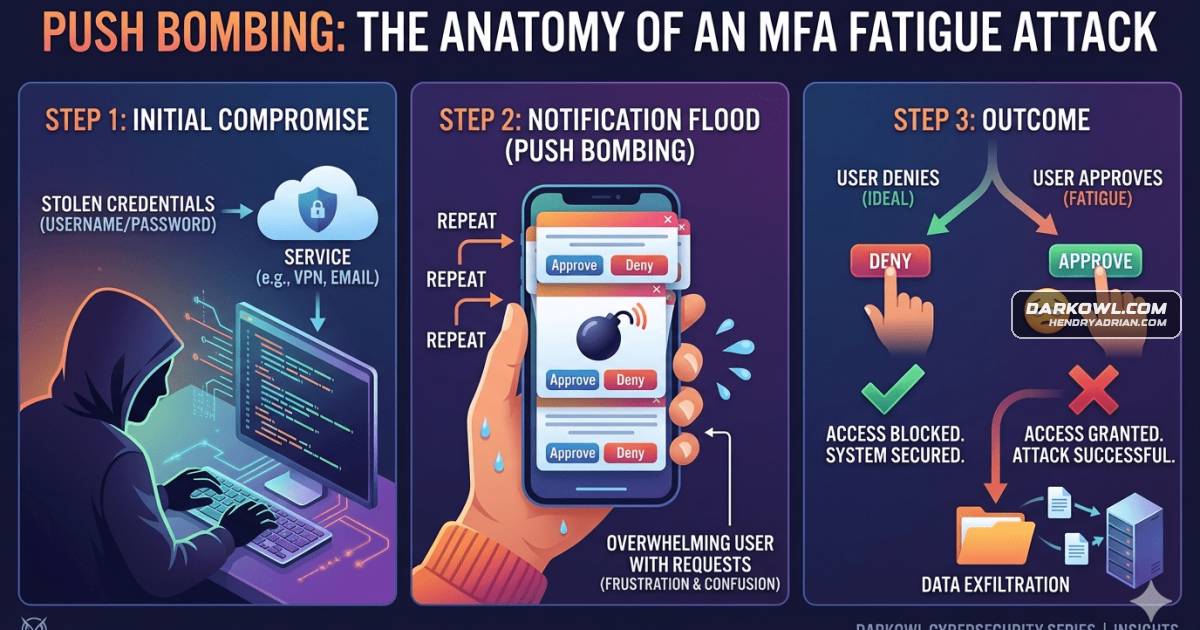
Push bombing, or MFA fatigue, overwhelms users with repeated login prompts after credentials are stolen, hoping they approve one. The article describes Uber and Cisco incidents and recommends phishing-resistant MFA and reporting unexpected prompts.
Key points
- Attackers use valid credentials to trigger repeated MFA push notifications, hoping a target eventually approves a login.
- The prompts may be combined with impersonation through chat, phone calls, or SMS to pressure the target.
- Repeated unexpected prompts, especially outside normal hours, can indicate an attempted account takeover.
- The article describes the 2022 Uber incident, in which a contractor approved a prompt after an attacker impersonated IT.
- It also describes a 2022 Cisco attack involving vishing and MFA fatigue, followed by lateral movement.
- Recommended protections include phishing-resistant MFA such as FIDO2 keys, WebAuthn, and passkeys, and reporting prompts the user did not initiate.
Article Details
- Topic
- Push bombing (MFA fatigue): how attackers abuse repeated MFA push notifications and measures to prevent account compromise.