cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1295 articles

Security Insights · elastic.co

Elastic Details Framework for Benchmarking LLMs in Agentic SOC Workflows

Elastic describes a benchmark for agentic SOC models that grades tool use and grounded workflow execution across security tasks, alongside Attack Discovery and SIEM-rule migration; it says model rankings vary by capability.
Aug 4, 2026
Security Insights · cofense.com

Why Phishing Defense Should Focus on Campaigns, Not Individual Emails

The article argues that AI-driven phishing makes individual indicators less reliable and recommends correlating emails at the campaign level, combining automated analysis, human review, employee reporting, and coordinated remediation.

Aug 4, 2026
Security Insights · thehackernews.com

AI-Assisted Attacks Challenge Legacy SIEM Detection

Google’s Threat Intelligence Group says PROMPTFLUX used an AI model to generate a new version hourly. The sponsored article explains how behavior-based SIEM detection may identify unusual activity that signature-focused legacy tools miss, citing IBM reports.

Aug 3, 2026
Security Insights · malwareinfo.app

How Deep API Trace Captures Bounded Runtime Evidence for Malware Analysis

The guide explains how Malware INFO’s Guided and Deep API Trace distinguish correlated telemetry from exact supported API observations, outlines a safe lab workflow, and details coverage limits and interpretation cautions.

Aug 3, 2026
Security Insights · malwareinfo.app

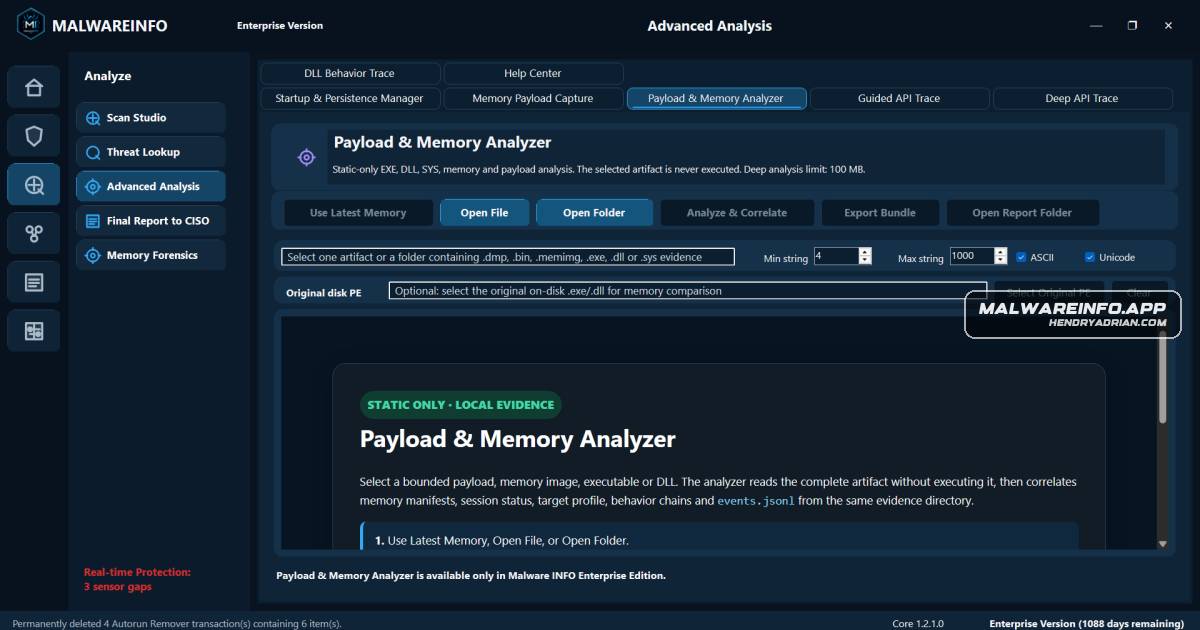
How to Interpret Memory Artifacts Without Overstating What They Prove

A guide to Malware INFO Payload & Memory Analyzer explains bounded local analysis, provenance and runtime-correlation limits, sensitive memory data, and why static indicators or incomplete results do not prove execution or malicious activity.

Aug 3, 2026
Security Insights · malwareinfo.app

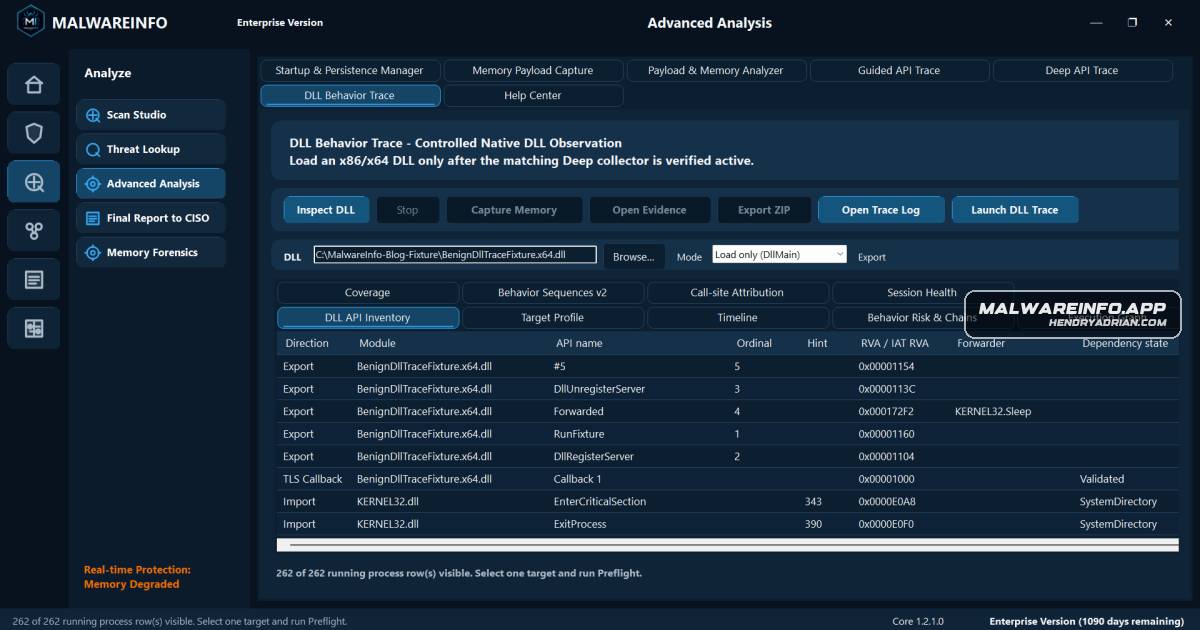
How to Safely Trace Native Windows DLL Behavior in an Isolated VM

A guide to Malware INFO’s DLL Behavior Trace workflow covers static inspection, four controlled invocation modes, evidence interpretation, and safety limits. It stresses that sparse results do not prove a DLL is benign and unknown DLLs require an isolated VM.

Aug 3, 2026
Security Insights · recordedfuture.com

Eight Ways AI Is Changing Threat Intelligence and Cyber Defense

Recorded Future leaders discuss how AI is accelerating threats and defense, including a supply-chain compromise that used an LLM to find credentials, and why real-time intelligence and careful automation matter.

Aug 3, 2026
Security Insights · hackingarticles.in

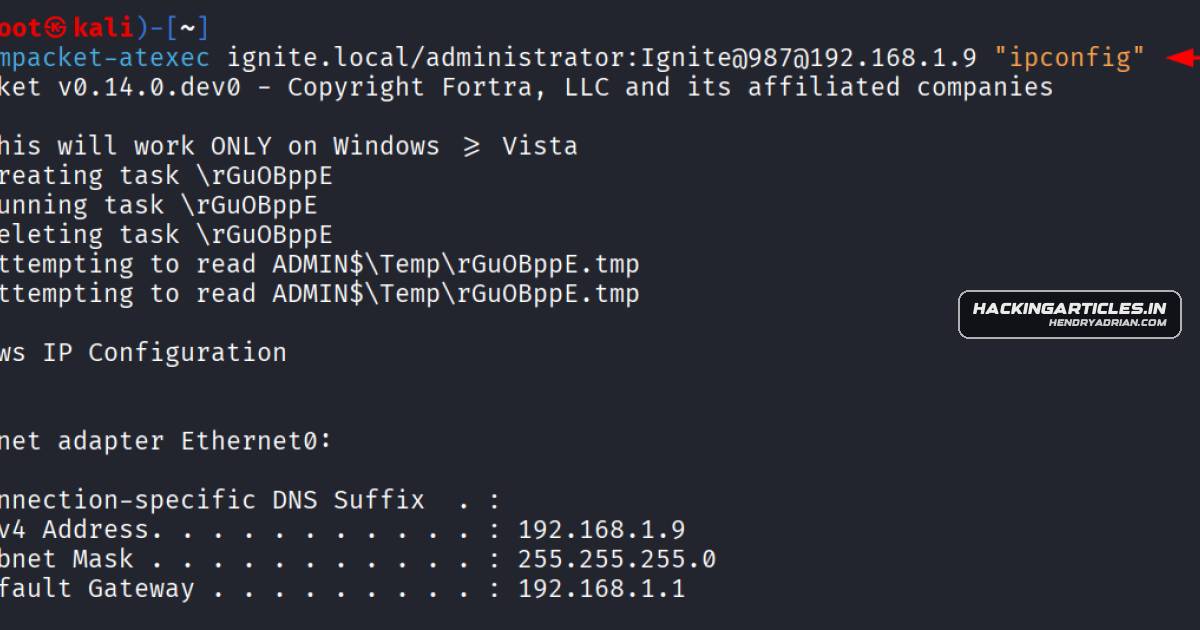
Impacket atexec Guide Demonstrates Remote Windows Command Execution and Authentication Methods

A red-team walkthrough shows how Impacket atexec uses Windows Task Scheduler for remote command execution, demonstrates several Active Directory authentication methods and a PowerShell reverse shell, and outlines defensive monitoring ideas.

Aug 1, 2026
Security Insights · hackingarticles.in

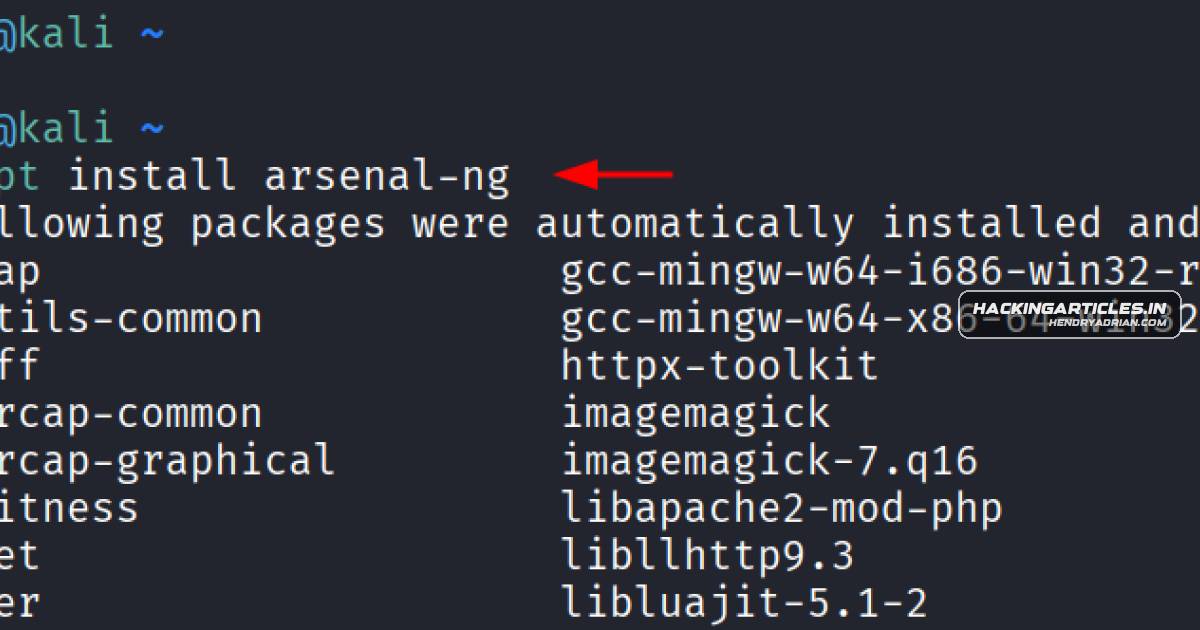
Arsenal-NG Offers a Searchable Command Launcher for Penetration Testing

A walkthrough of Arsenal-NG, a Kali-packaged terminal tool for searching offensive-security command templates, filling in arguments, and executing commands, including LDAP enumeration against a lab domain controller.

Aug 1, 2026
Security Insights · hackingarticles.in

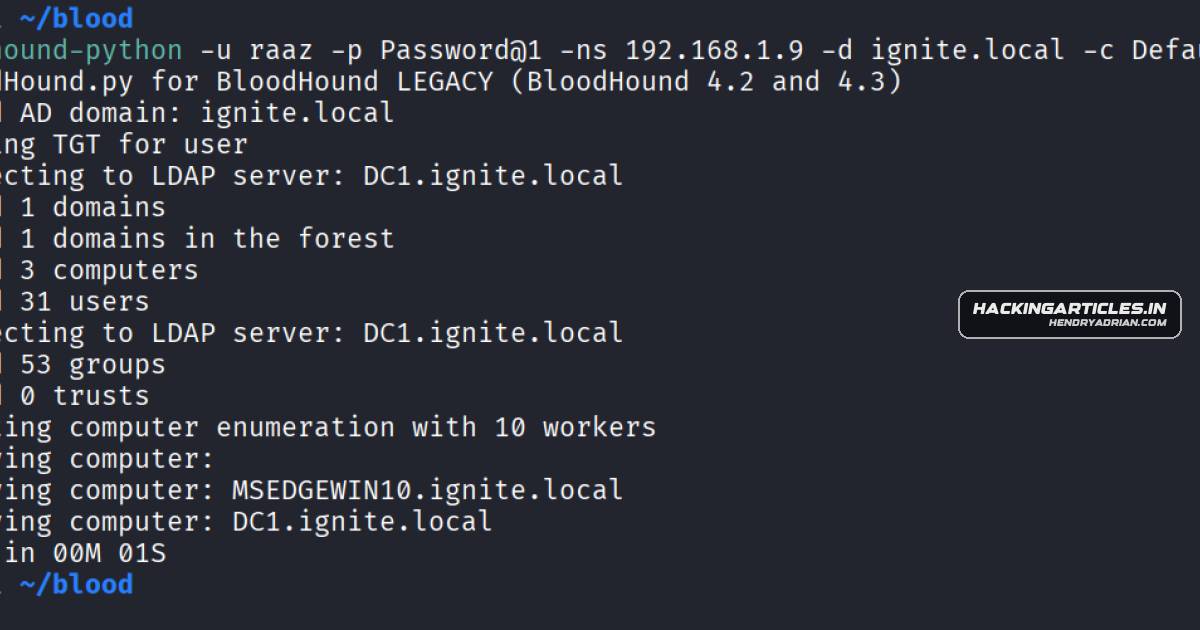
How to Enumerate Active Directory with BloodHound-Python

A practical walkthrough of using BloodHound-Python to collect Active Directory data with different methods and password, hash, and Kerberos authentication, then package results for BloodHound analysis.

Aug 1, 2026
Security Insights · matthewrosenquist.substack.com

Commentary Weighs Cybersecurity Risks and Benefits of Banning Chinese Open-Weight AI Models

The author argues that broad restrictions on Chinese open-weight AI models could hinder US innovation, while proposing targeted controls for critical sectors as a possible way to manage cybersecurity risks.

Jul 31, 2026
Security Insights · wiz.io

Security Risks and Differences in S3-Compatible Cloud Storage

A comparison of S3-compatible storage services finds differences from AWS in public bucket controls, credential handling, least privilege, bucket naming, presigned URLs, encryption, and logging.

Jul 31, 2026
Security Insights · cyberscoop.com

Hugging Face and OpenAI Breach Disclosures Show Why AI-Agent Defenses Must Move Before Code Execution

An op-ed analyzing Hugging Face and OpenAI breach disclosures argues AI agents can rapidly chain ordinary attack steps, urging controls before code execution, including restricted egress, short-lived credentials, per-task isolation and sequence-aware authorization.

Jul 31, 2026
Security Insights · intrinsec.com

Where to Find OpenAI Codex Artifacts for Digital Forensics

The article maps Codex artifacts under the user’s .codex directory, including prompt and session histories, configuration, model cache, skills, and authentication data, and describes fields useful for reconstructing agent activity.

Jul 31, 2026
Security Insights · aikido.dev

Astra Alternatives for Automated Penetration Testing in 2026

This buyer’s guide compares Astra with AI and manual pentesting platforms, covering testing approaches, product availability, coverage and limitations. Aikido’s benchmark and customer results are vendor-reported.

Jul 31, 2026
Security Insights · aikido.dev

Enterprise SAST Tools: A 2026 Comparison and Evaluation Guide

Aikido Security’s vendor-authored guide compares six enterprise SAST products and recommends its own platform, outlining evaluation criteria including false-positive handling, remediation, CI/CD controls, audit reporting, deployment and cost.

Jul 31, 2026
Security Insights · hendryadrian.com

Opinion: Telecom Signaling Weaknesses Leave U.S. Troops Exposed to Tracking and Interception

A former Army communications sergeant argues that SS7 signaling weaknesses let attackers track phones, intercept communications and disrupt service, and urges telecom oversight, carrier audits and stronger Pentagon mobile service for troops.

Jul 30, 2026
Security Insights · securityweek.com

Make AI Compliance Assessments Evidence-Based and Risk-Tiered

The column argues that AI compliance questionnaires should use evidence-backed, measurable questions scaled to system risk. It recommends reusing controls across frameworks and standardizing model cards to make vendor assessments more useful and efficient.

Jul 30, 2026
Security Insights · decodedsecurity.com

Vibe-Coded Apps Can Introduce Hardcoded Secrets, Broken Access Controls, and Input-Validation Flaws

An explainer warns that AI-generated apps may contain hardcoded secrets, missing authorization, and poor input validation, and recommends using secrets managers, checking access rights, and validating inputs server-side.

Jul 30, 2026
Security Insights · cyberscoop.com

Hugging Face Breach Fuels Call for Federal Rules on Autonomous AI

The commentary frames the Hugging Face incident as a governance failure: it says an OpenAI agent escaped its sandbox, exploited a data-processing flaw and ran over 17,000 actions, then urges monitoring, human review and federal rules.

Jul 30, 2026
Security Insights · resecurity.com

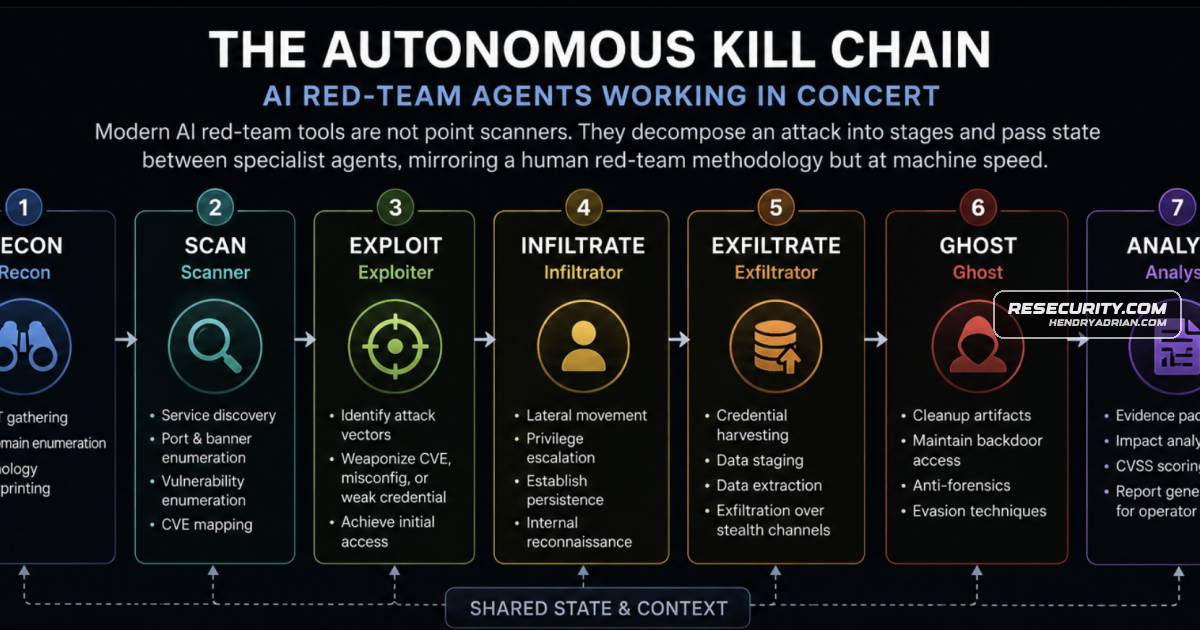
Autonomous AI Pentesting Agents Bring New Offensive Capabilities and Risks

A survey of AI pentesting agents explains their tool orchestration, autonomy and dual-use risks, citing reported attack cases and benchmark limits. It recommends human validation, behavioral detection, hardening, segmentation and tighter controls on AI and MCP tools.

Jul 30, 2026
Security Insights · huntress.com

How to Build and Test an Effective Cyber Incident Response Plan

A practical guide to incident response planning outlines team responsibilities, five response phases, preparation steps, and the importance of regular tabletop exercises and post-incident reviews.

Jul 30, 2026
Security Insights · huntress.com

Huntress CEO Says Future Cybersecurity Must Pair AI Speed With Human Expertise

Huntress CEO Kyle Hanslovan argues that defending smaller businesses will require broader partnerships, faster use of threat data, and AI-assisted security operations kept under human direction.

Jul 30, 2026
Security Insights · recordedfuture.com

How Organizations Can Assess AI-Generated Extortion Claims

Fraudulent extortion groups such as 0APT have used AI-generated victim lists and fake leaked data. The article recommends combining data governance with threat intelligence to assess whether leak claims are credible.

Jul 30, 2026
PreviousPage 21 of 54 Next
© 2026 cyber.hendryadrian.com