Impacket atexec Guide Demonstrates Remote Windows Command Execution and Authentication Methods
Summary
A red-team walkthrough shows how Impacket atexec uses Windows Task Scheduler for remote command execution, demonstrates several Active Directory authentication methods and a PowerShell reverse shell, and outlines defensive monitoring ideas.
Key points
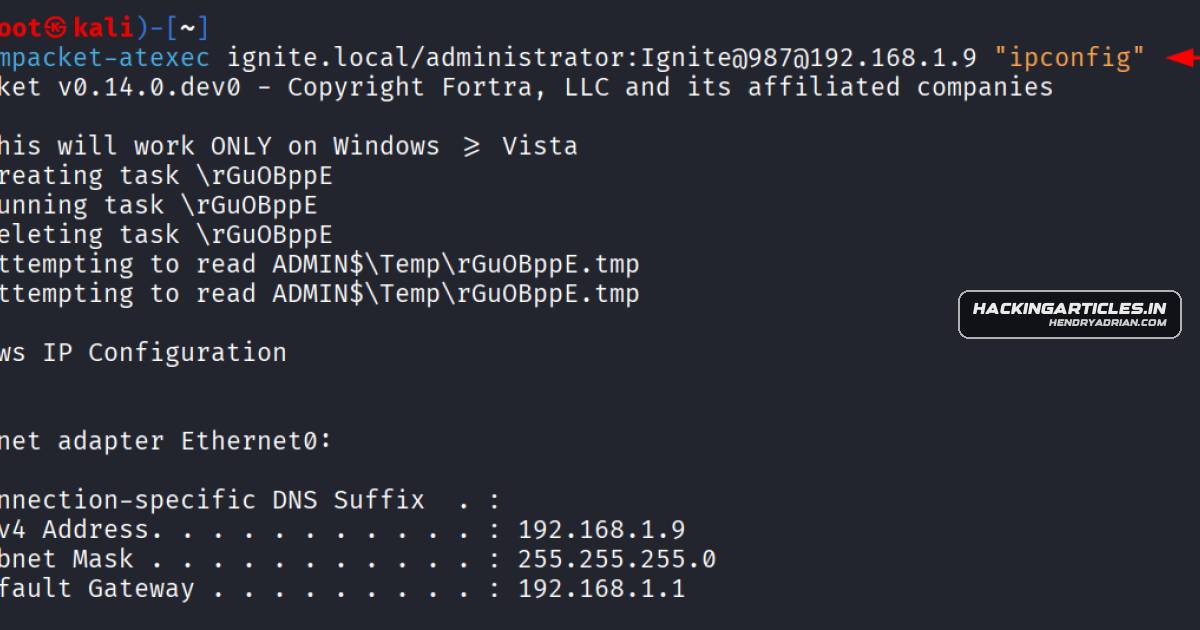
- Impacket atexec uses the Windows Task Scheduler service over MSRPC to run commands remotely, retrieving output through ADMIN$\Temp and deleting the temporary task afterward.
- The guide demonstrates authentication with plaintext credentials, NTLM Pass-the-Hash, Kerberos Pass-the-Ticket, and an AES key.
- It shows using atexec with a Base64-encoded PowerShell payload to establish an interactive reverse shell.
- Options covered include -silentcommand, timestamped and debug output, specifying a domain controller IP, and selecting an output encoding.
- The article recommends monitoring scheduled-task events 4698, 4700, 4701, and 4702, watching for unusual writes to ADMIN$\Temp, limiting administrative-share access, and protecting credential material.
Article Details
- Topic
- A practical guide to using Impacket-atexec for remote command execution, Active Directory authentication methods, and reverse-shell delivery.
MITRE ATT&CK
T1053.005 · Scheduled TaskUses Windows Task Scheduler to create and run a temporary scheduled task for remote command execution.T1059.001 · PowerShellExecutes a PowerShell reverse-shell payload on the target.T1550.002 · Pass the HashDemonstrates Pass-the-Hash authentication using an NTLM hash.T1550.003 · Pass the TicketDemonstrates Pass-the-Ticket authentication using a Kerberos ticket.
Vendors
Products
Tools
atexecImpacket for Pentester: atexecDcomExecIt sits alongside its siblings — psexec, smbexec, wmiexec, and dcomexec — as a semi-interactive command executor, but it stands apart by using the Task Scheduler rather than services or WMI, which makes it a valuablenetcat Before launching the payload, we started a Netcat listener on port 443, wrapped in rlwrap to give us a more comfortable, history-enabled shell experience.PsExecIt sits alongside its siblings — psexec, smbexec, wmiexec, and dcomexec — as a semi-interactive command executor, but it stands apart by using the Task Scheduler rather than services or WMI, which makes it a valuablerlwrap Before launching the payload, we started a Netcat listener on port 443, wrapped in rlwrap to give us a more comfortable, history-enabled shell experience.smbexecIt sits alongside its siblings — psexec, smbexec, wmiexec, and dcomexec — as a semi-interactive command executor, but it stands apart by using the Task Scheduler rather than services or WMI, which makes it a valuablewmiexecIt sits alongside its siblings — psexec, smbexec, wmiexec, and dcomexec — as a semi-interactive command executor, but it stands apart by using the Task Scheduler rather than services or WMI, which makes it a valuable