cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · wiz.io

Wiz Shares VCS Logging and Threat-Hunting Guidance for GitHub, GitLab, Bitbucket, and Azure DevOps

Wiz CIRT's VCS DFIR guide maps log sources, readiness settings, and audit events across four platforms to help security teams improve visibility, investigate incidents, and hunt for attacker activity.
Aug 27, 2026
Detection & Defense · ncsc.gov.uk

NCSC Urges Organisations to Secure Internet-Exposed OT and Edge Devices

The NCSC reports increased targeting of internet-exposed operational technology across sectors, with limited real-world disruption, and urges organisations to inventory exposed assets, harden access, monitor networks and prepare for recovery.

Aug 27, 2026
Detection & Defense · huntress.com

Five Cybersecurity Decisions to Help ANZ Retailers Keep Trading

Huntress outlines five security priorities for Australian and New Zealand retailers, from mapping critical systems and securing identities to rehearsing incident response. Its partner telemetry highlights compromised Microsoft 365 accounts and endpoint footholds as key,

Aug 27, 2026
Detection & Defense · bleepingcomputer.com

Snowflake’s Phase 3 Password Migration Puts Service-Account Governance in Focus

Snowflake’s Phase 3 rollout migrates legacy service users to passwordless SERVICE accounts by account-specific deadlines. The article advises inventorying dependencies and owners, choosing authentication per workload, and revoking exposed credentials.

Aug 26, 2026
Detection & Defense · abstract.security

How to Detect Threat Actors’ Abuse of Remote Management Tools

The article explains how defenders can use the LOLRMM catalog to inventory and detect remote management tool activity, then correlate first-seen tools with phishing and other suspicious behavior.

Aug 26, 2026
Detection & Defense · huntress.com

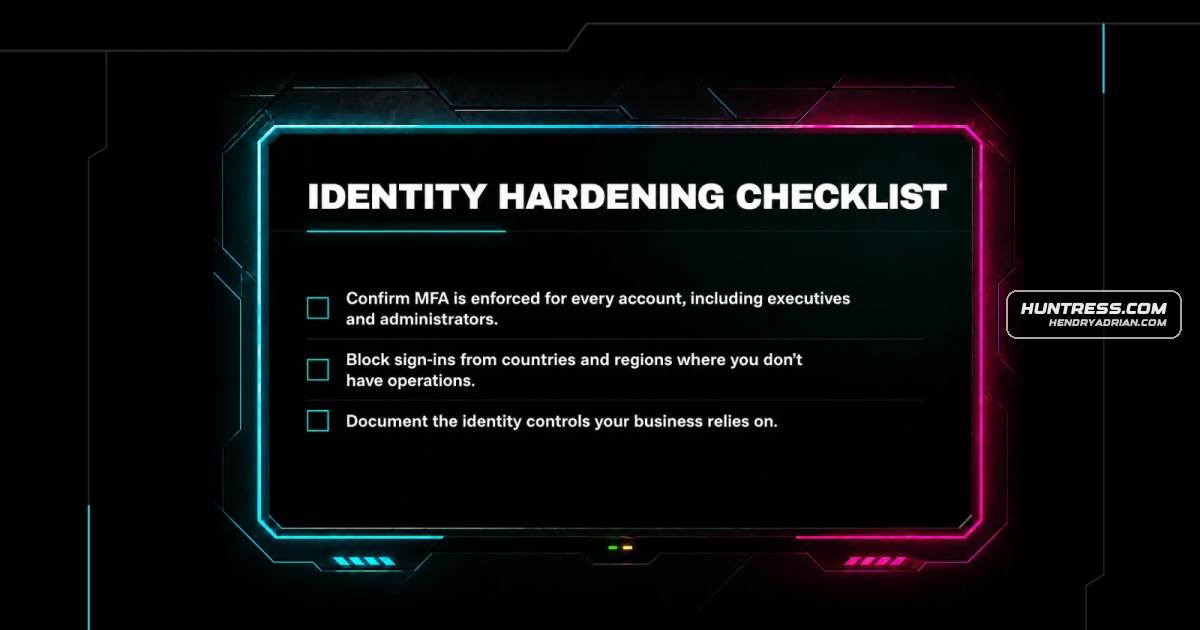
Huntress outlines identity-hardening steps that go beyond MFA

Huntress recommends layered identity defenses beyond MFA, including device and location controls, least privilege, removing stale accounts, blocking legacy authentication, monitoring unusual sign-ins, and regularly reviewing exceptions and configuration drift.

Aug 25, 2026
Detection & Defense · securonix.com

Why Effective Detection Engineering Requires Environment-Specific Tuning

Detection rules work best when teams tune them to local systems and workflows. The article recommends documenting exceptions, measuring detection quality, and managing rule changes with testing and version control.

Aug 24, 2026
Detection & Defense · bleepingcomputer.com

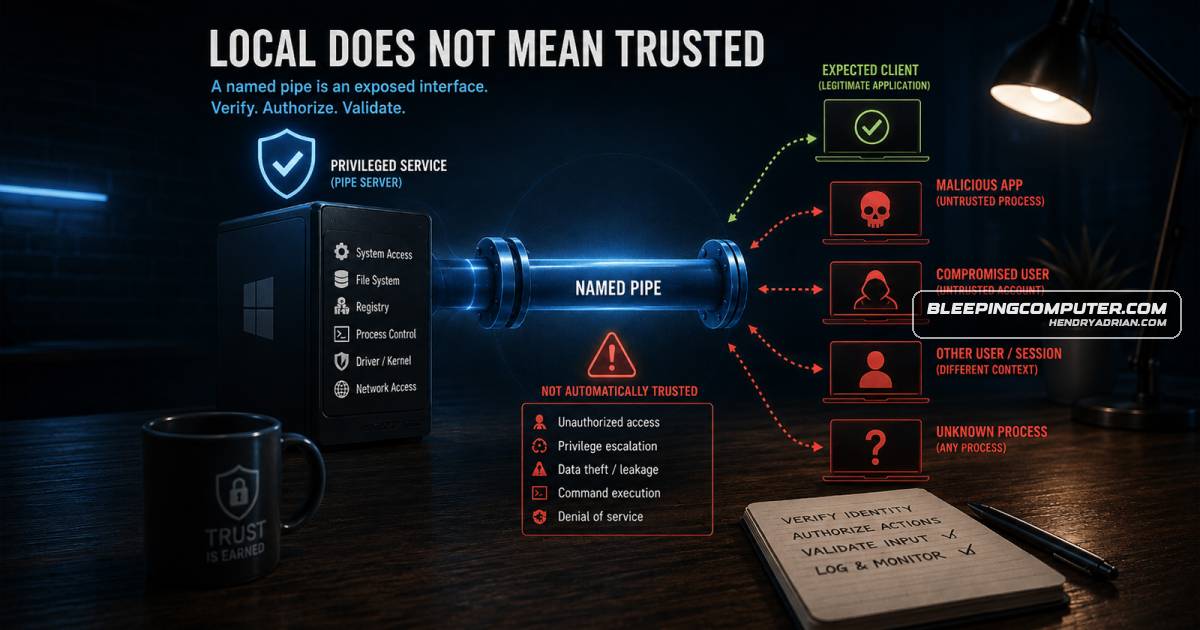
Securing Windows Named Pipes Against Privilege Abuse and Remote Access

A ThreatLocker-sponsored guide explains how to harden Windows named pipes through restrictive permissions, endpoint verification, per-command authorization, bounded messages, safe impersonation, and explicit remote-access restrictions.

Aug 22, 2026
Detection & Defense · jamf.com

Back-to-School Device Security Checklist for School IT Admins

A back-to-school security checklist for school IT admins recommends auditing device enrollment, OS versions and check-ins, updating security baselines, reviewing filters and shadow IT, and preparing incident-response steps.

Aug 21, 2026
Detection & Defense · huntress.com

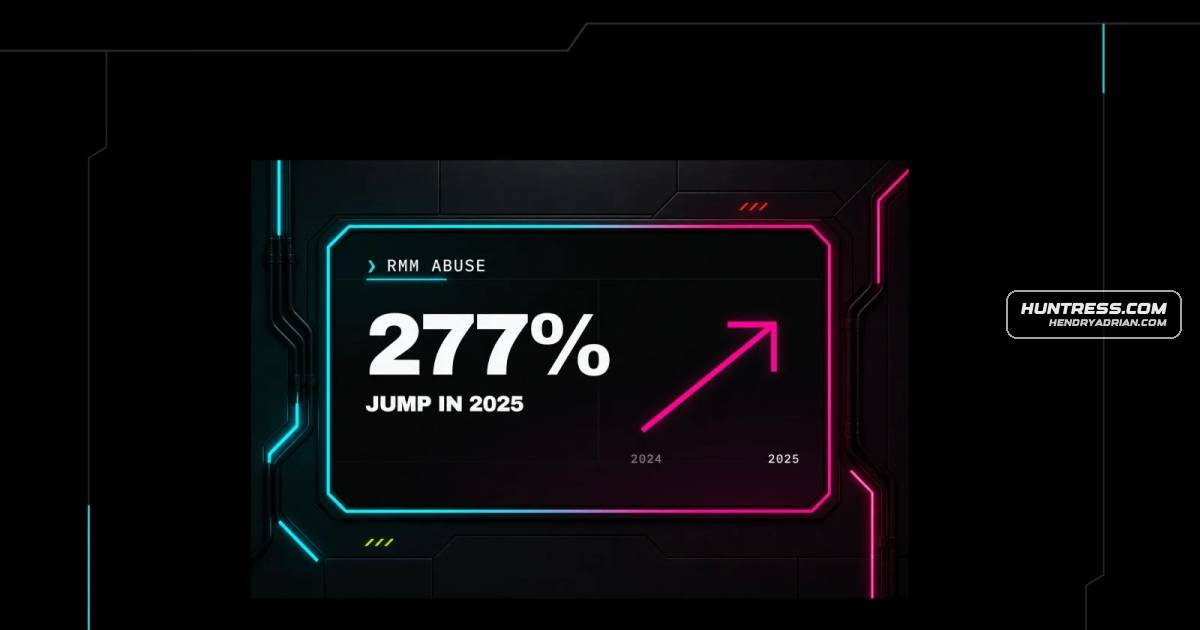
RMM Abuse Surged 277% as Attackers Exploit Trusted Remote Access Tools

Huntress reports a 277% rise in RMM abuse, with attackers using legitimate remote access tools for stealthy access. It recommends tracking authorized tools, enabling MFA, and strengthening user awareness and endpoint defenses.

Aug 21, 2026
Detection & Defense · wazuh.com

Wazuh Shows How to Detect Exploitation of Langflow CVE-2026-33017

A Wazuh walkthrough uses nginx access logs, auditd, and custom detection rules to identify attempts to exploit Langflow’s unauthenticated code-injection flaw, CVE-2026-33017, and resulting host activity.

Aug 20, 2026
Detection & Defense · bleepingcomputer.com

How MSPs Can Detect Phishing Attacks That Email Filters Miss

A sponsored Kaseya article advises MSPs to look beyond email filters by monitoring account behavior, correlating identity, email and endpoint signals, and quickly containing suspected compromises.

Aug 20, 2026
Detection & Defense · jamf.com

How to Respond to an Apple Mercenary Spyware Threat Notification

Apple says its alerts identify people specifically targeted by mercenary spyware, not confirmed compromises. The article advises verifying alerts independently, preserving device evidence, seeking expert forensics, enabling Lockdown Mode, updating iOS and securing Apple

Aug 20, 2026
Detection & Defense · cisa.gov

U.S. Agencies Warn of AI-Assisted Threat Targeting Siemens S7 PLCs

U.S. agencies warn that AI-assisted scripts and Snap7-based tools are being used against exposed Siemens S7 PLCs. They assess the activity as reconnaissance and capability development, and recommend patching, isolation, stronger access controls and monitoring.

Aug 19, 2026
Detection & Defense · malwarebytes.com

Fake Crypto AML Checkers Trick Users Into Approving Malicious Wallet Transactions

Fake AML-checking sites impersonate services such as AMLBot, prompting users to connect wallets and approve attacker-generated transactions. The article explains the scam and advises disconnecting sites, revoking token permissions, and moving exposed funds.

Aug 19, 2026
Detection & Defense · wiz.io

How to Detect and Prevent Rogue Device Registrations in Microsoft Entra ID

Attackers use phishing to register rogue Entra ID devices and bypass Conditional Access. The article recommends detecting anomalous naming and correlating device-code sign-ins with registrations, and suggests policy controls to limit abuse.

Aug 18, 2026
Detection & Defense · threatlabs.netskope.com

How Malware Uses Blockchain Dead Drops to Rotate C2 Infrastructure

A practitioner guide explains how eight malware families across EVM, Solana, and TON use blockchain dead drops to retrieve C2 pointers, and how defenders can investigate RPC calls and identify suspicious process activity.

Aug 18, 2026
Detection & Defense · opensourcemalware.com

Developer Guide Explains How to Contain and Remove the PolinRider Malware

A field-tested guide explains how PolinRider infects and re-infects developers, spreads through repositories and packages, steals credentials, and how to contain it, clean affected systems and repositories, and rotate exposed credentials.

Aug 13, 2026
Detection & Defense · bleepingcomputer.com

AI-Suggested Dependencies Create Supply-Chain Risks Before Builds

The sponsored article warns that hallucinated or unvetted AI-suggested packages can enable supply-chain attacks. It describes a reported react-codeshift spread across repositories and recommends controlling dependency intake before builds.

Aug 13, 2026
Detection & Defense · wiz.io

Wiz Details Investigation Playbook for GitHub PAT Theft and Repository Exfiltration

Wiz describes a multi-organization campaign using stolen GitHub PATs for repository reconnaissance and mass cloning, and outlines how responders can contain tokens, trace activity, assess exposed secrets and data, rotate credentials, and hunt for follow-on misuse.

Aug 13, 2026
Detection & Defense · wazuh.com

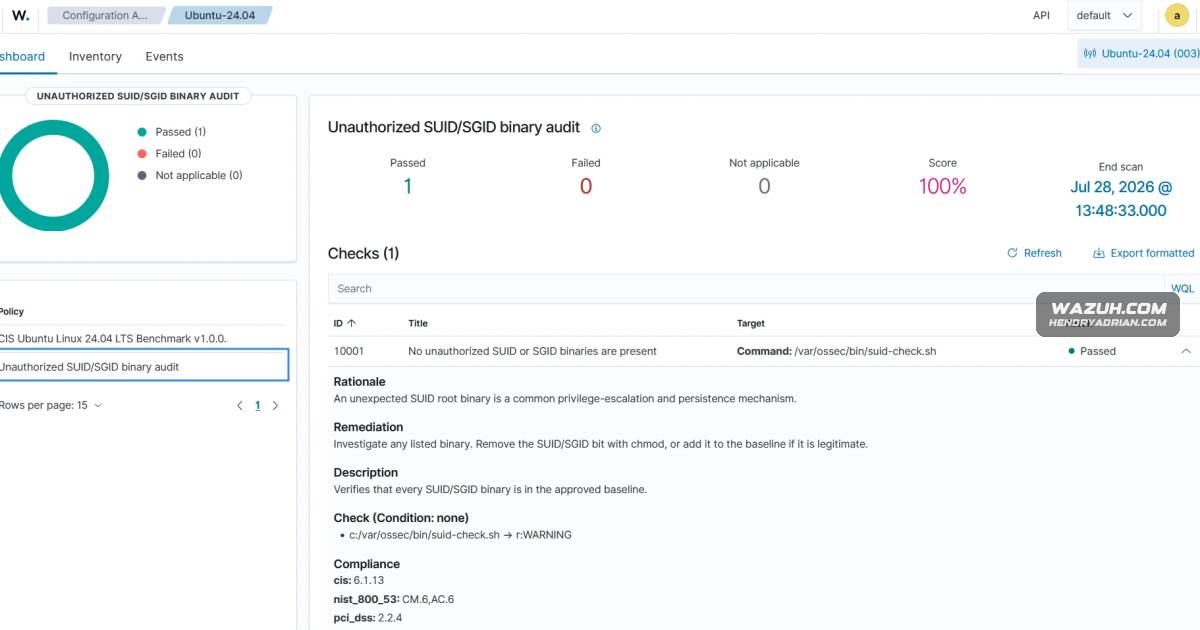
How to Detect Unauthorized Linux SUID and SGID Binaries with Wazuh

A Wazuh tutorial shows how to baseline Linux SUID/SGID binaries and use command monitoring and Security Configuration Assessment to alert on unauthorized additions.

Aug 13, 2026
Detection & Defense · reliaquest.com

Five Steps to Defend Against AI-Driven Attacks and Secure Enterprise AI Use

ReliaQuest outlines five ways to address AI-related security risks, including automating response, governing enterprise AI use, limiting agent permissions, continuously testing defenses, and keeping governance aligned with adoption.

Aug 13, 2026
Detection & Defense · bleepingcomputer.com

How Fake Remote Workers Exploit Hiring and Onboarding Gaps

The sponsored article describes tactics used by fake remote workers, including North Korean IT workers, and lists warning signs and identity-proofing measures organizations can use during onboarding and later access changes.

Aug 12, 2026
Detection & Defense · cyberscoop.com

Water Utilities Urged to Secure Internet-Exposed PLCs After Multi-State Attacks

The FBI and EPA warned of attacks on internet-facing PLCs at water and wastewater utilities in at least seven states. Some utilities reported operational problems; the article urges access controls, asset inventories and continuous OT monitoring.

Aug 10, 2026
PreviousPage 12 of 26 Next
© 2026 cyber.hendryadrian.com