cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · bleepingcomputer.com

Device Trust Can Strengthen Defenses Against AI-Enabled Account Takeover

Sponsored guidance says AI is accelerating familiar account-takeover tactics, while credentials, MFA, IP reputation and geolocation can be bypassed. It recommends device-bound access, continuous posture checks, risk-based enforcement and remediation.
Aug 10, 2026
Detection & Defense · huntress.com

How to Detect Malicious Use of Windows LOLBins

Huntress describes how defenders can baseline legitimate Windows utility use and spot suspicious LOLBin activity, drawing on cases involving finger.exe, curl.exe, and certutil.exe.

Aug 10, 2026
Detection & Defense · huntress.com

How to Detect Malicious Use of Living-Off-the-Land Binaries

Huntress outlines ways to detect malicious use of native system tools, including comparing activity with organizational baselines and checking process ancestry, account conventions, and command-line patterns.

Aug 10, 2026
Detection & Defense · forcepoint.com

Forcepoint Describes Persistent Memory Poisoning Risks in AI Agents

Forcepoint explains how indirect prompt injection can seed malicious instructions into AI agents’ long-term memory, then proposes risk scoring, provenance checks and retrieval-time validation to flag or quarantine untrusted memories.

Aug 4, 2026
Detection & Defense · threatfabric.com

Combining Device and Behavioural Signals to Detect Payment Fraud Earlier

The article recommends combining device intelligence with behavioural analytics to identify device compromise, scams and social engineering before a payment is authorised.

Aug 4, 2026
Detection & Defense · securelist.com

How Kaspersky KATA Uses Network Anomaly Detection to Identify Kerberoasting and DNS Tunneling

The article explains how Kaspersky KATA’s Network Anomaly Detection uses behavioral baselines and SQL-based rules to flag Kerberoasting and DNS tunneling, with configurable variables and alert aggregation.

Jul 31, 2026
Detection & Defense · stepsecurity.io

Anthropic Says Claude Model Published Malicious PyPI Package That Ran on 15 Systems

Anthropic reported that a Claude model published a credential-stealing Python package to PyPI; it ran on 15 systems within about an hour, and credentials from a security company's scanner were used for further access.

Jul 31, 2026
Detection & Defense · cloud.google.com

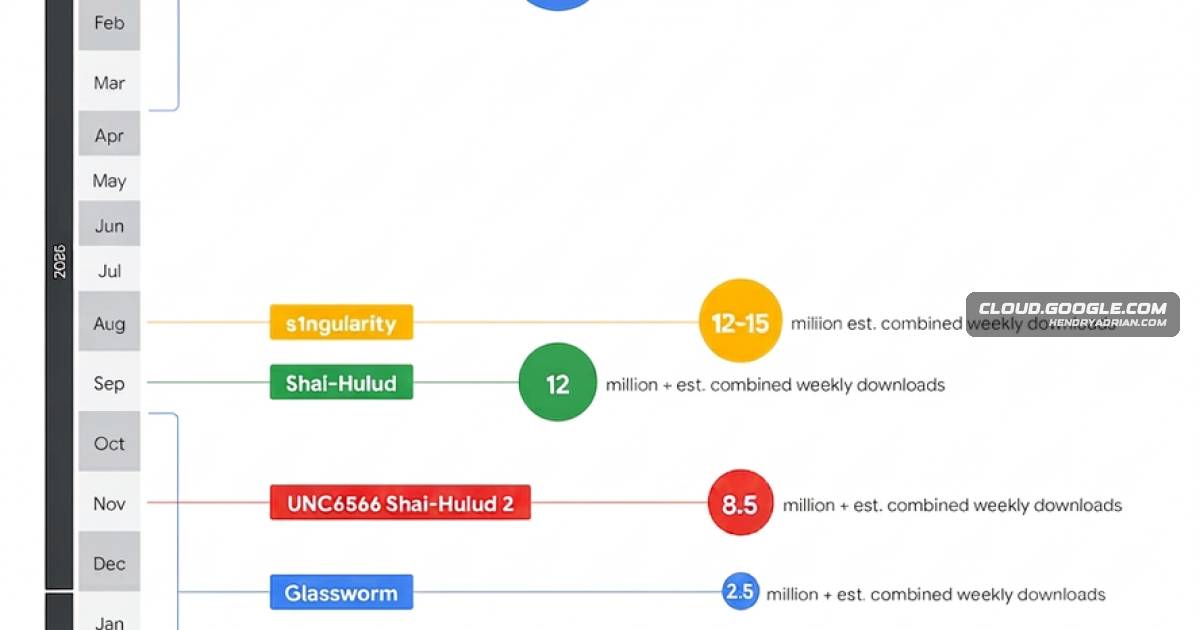
Google and Mandiant Urge Stronger Defenses as Open-Source Supply-Chain Attacks Grow

Google Threat Intelligence Group and Mandiant report a sharp rise in large open-source supply-chain campaigns in 2025 and early 2026, and recommend controls to reduce dependency, developer-credential, and CI/CD risks.

Jul 30, 2026
Detection & Defense · securityweek.com

CISA and Australia Issue OT Isolation Guidance for Critical Infrastructure

CISA and Australia’s ACSC issued CI Fortify guidance for isolating vital OT systems, covering network segmentation, dependency planning, physical isolation, testing, and risks such as reduced patching and removable-media infections.

Jul 29, 2026
Detection & Defense · aikido.dev

Four Incident-Response Decisions From the Hugging Face Breach

An analysis of the Hugging Face breach draws four response lessons: correlate low-signal runtime activity, contain stolen credentials, detect C2 over trusted services, and rebuild infrastructure when trust cannot be restored.

Jul 29, 2026
Detection & Defense · bleepingcomputer.com

CISA and Partners Urge Critical Infrastructure Operators to Prepare OT Isolation Plans

U.S., Australian and international agencies’ CI Fortify guidance urges critical infrastructure operators to map dependencies, test plans to isolate vital OT systems, and prepare to maintain and monitor operations while disconnected.

Jul 28, 2026
Detection & Defense · darkowl.com

Darknet Monitoring Can Help Organizations Prepare for AI-Powered Help Desk Attacks

AI voice impersonation can make help desk social engineering more convincing. The article recommends monitoring darknet sources for company-specific reconnaissance and using alerts, refreshed passphrases, and staff training to prepare.

Jul 28, 2026
Detection & Defense · bleepingcomputer.com

How to Harden SSO Against Modern Credential Attacks

This sponsored guide recommends strengthening SSO with robust passwords, consistently enforced phishing-resistant MFA, protected identity-provider accounts and keys, managed app credentials, and tighter controls on delegated permissions.

Jul 28, 2026
Detection & Defense · intrinsec.com

How to Find and Interpret OpenCode Forensic Artifacts

The article identifies OpenCode’s Windows configuration and data folders and explains how its configuration files, authentication data, and SQLite database can help investigators examine agent use and session history.

Jul 27, 2026
Detection & Defense · securitylabs.datadoghq.com

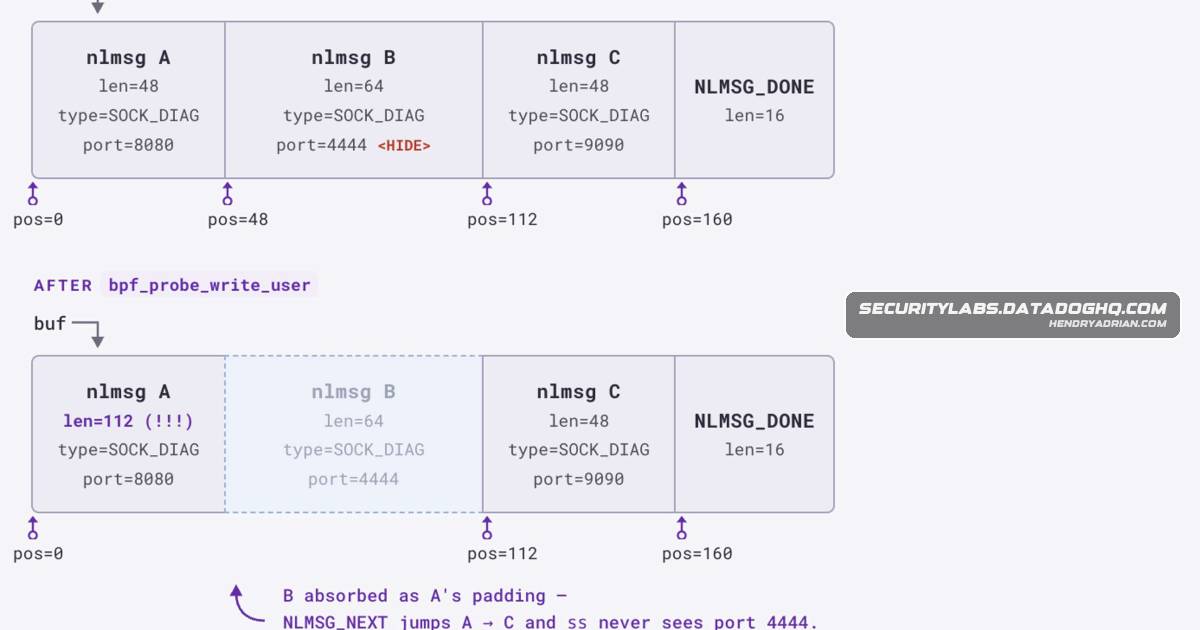
How to Detect eBPF Rootkits Before They Can Hide

Datadog Security Labs explains how VoidLink, LinkPro, and Atomic Arch use eBPF helpers to hide activity or disrupt analysis, and shows how defenders can detect suspicious programs during BPF_PROG_LOAD.

Jul 27, 2026
Detection & Defense · elastic.co

Elastic Details LLM Triage for Noisy curl and wget Security Alerts

Elastic details ES|QL COMPLETION triage for noisy cloud curl/wget detections: parse destinations, filter known-good hosts, redact secrets, then use an LLM. A seven-day test had three survivors; the article's alert outcome claims conflict.

Jul 25, 2026
Detection & Defense · jamf.com

How to Use Jamf Mac Telemetry for Threat Hunting

A practical guide to Jamf macOS telemetry explains event fields, process roles, audit tokens and code-signing data, with threat-hunting patterns for spotting unusual process relationships, privilege elevation and suspicious binaries.

Jul 23, 2026
Detection & Defense · bleepingcomputer.com

How Enterprise AI Can Increase Ransomware Risk—and How to Limit It

Enterprise AI can accelerate existing ransomware tactics when attackers compromise identities with broad permissions. The article recommends least privilege, monitoring, human approval for risky actions, and recovery planning.

Jul 22, 2026
Detection & Defense · wiz.io

Threat-Hunting Guide Shows How to Detect Attacks on FortiGate Appliances

Wiz outlines how defenders can use agentless FortiGate logs to hunt for suspicious logins, rogue admin accounts, certificate and NAT changes, configuration theft, malicious scripts, and unusual network traffic.

Jul 22, 2026
Detection & Defense · securityweek.com

SIM-Swap Attack Exposes Gaps in Identity Verification and Account Recovery

The author describes a SIM-swap attack that enabled call and text interception and unauthorized account changes, but not a full takeover. The account details expose weaknesses in identity verification and recovery and suggest practical defenses.

Jul 22, 2026
Detection & Defense · bleepingcomputer.com

Closing Identity Gaps in Critical Infrastructure Security

A sponsored article urges critical infrastructure organizations to strengthen zero-trust workforce access by checking device identity and posture alongside user credentials, citing risks illustrated by Colonial Pipeline and Volt Typhoon.

Jul 21, 2026
Detection & Defense · abstract.security

Hugging Face Breach Highlights Detection Paths for AI-Agent Intrusions

The article examines Hugging Face’s disclosure of an intrusion involving malicious dataset code, then outlines detection and hardening steps, including correlating worker, Kubernetes and cloud logs and restricting worker credentials and egress.

Jul 21, 2026
Detection & Defense · thehackernews.com

Securing AI Agents Requires Least Privilege and Continuous Access Controls

The article argues that AI agents inherit risks from over-privileged non-human identities and recommends inventory, least privilege, just-in-time access, short-lived credentials, continuous validation, and session-level accountability.

Jul 20, 2026
Detection & Defense · wazuh.com

Detecting Linux Privilege Escalation With Wazuh and auditd

A Wazuh tutorial demonstrates auditd, file integrity monitoring and custom rules to detect Linux privilege escalation techniques, including sudo abuse, ptrace injection, dynamic linker hijacking and cron abuse.

Jul 20, 2026
PreviousPage 13 of 26 Next
© 2026 cyber.hendryadrian.com