
Securing Windows Named Pipes Against Privilege Abuse and Remote Access
Summary
A ThreatLocker-sponsored guide explains how to harden Windows named pipes through restrictive permissions, endpoint verification, per-command authorization, bounded messages, safe impersonation, and explicit remote-access restrictions.
Key points
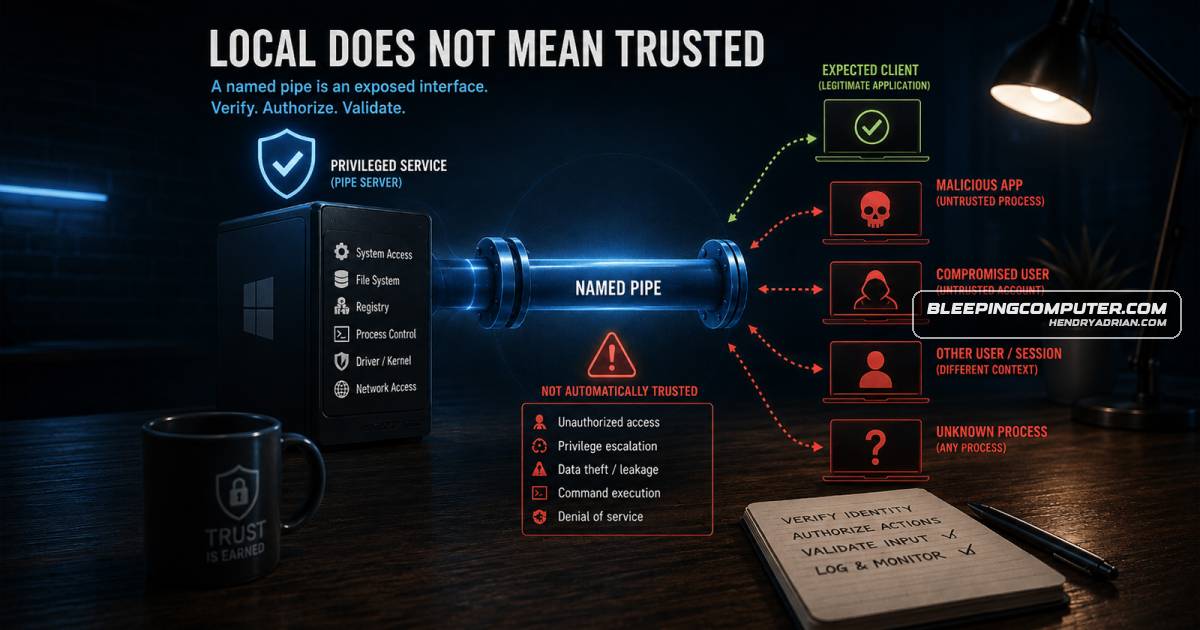
- Treat named pipes as exposed trust boundaries, particularly when standard-user applications communicate with LocalSystem services.
- Use explicit, restrictive pipe DACLs and verify Windows identities; authorize sensitive commands individually rather than treating connection permission as blanket access.
- Verify both endpoints, but treat PID, executable-path, signature, and hash checks as secondary controls because pipe handles can be transferred and reported client PIDs can be spoofed.
- Expose narrowly defined application operations instead of arbitrary file, registry, process, or command execution; validate framing, payload sizes, paths, and field values.
- Keep impersonation scopes short, reject requests if impersonation fails, restore the original identity reliably, and revalidate data crossing into privileged execution.
- Use PIPE_REJECT_REMOTE_CLIENTS where supported and deny network identities when communication must remain local.
- Limit connections, queues, message sizes, concurrency, and request duration; isolate privileged execution and log security-relevant failures without sensitive payloads.
Article Details
- Defense Focus
- Secure privileged Windows named-pipe communication against unauthorized operations, endpoint impersonation, untrusted input, resource exhaustion, and unintended remote access.
- Detection Methods
- Audit rejected connections, failed identity checks, unauthorized commands, malformed or oversized messages, repeated timeouts, and privileged-operation results.
- Investigate abnormal connection and request rates using user identity, session, peer PID, command type, and result; repeated failures may also indicate defective clients or deployment issues.
- After connection, inspect peer PIDs with GetNamedPipeClientProcessId or GetNamedPipeServerProcessId and optionally verify executable paths, signatures, or approved hashes. Treat these as secondary controls because PIDs can be spoofed and connected handles transferred.
- Use the first-pipe-instance option to help detect an already claimed pipe name, without treating it as a substitute for server identity verification.
- Data Sources
- Protected service audit and diagnostic logs
- Connected clients' Windows identities, SIDs, access tokens, and logon sessions
- Peer process IDs, executable paths, Authenticode signatures, and approved executable hashes
- Pipe connection counts, request rates, timeouts, message sizes, queue depth, and operation results
- Defensive Actions
- Define explicit restrictive pipe DACLs granting access only to required identities or logon sessions; authorize each sensitive command separately.
- For local-only communication, specify PIPE_REJECT_REMOTE_CLIENTS where supported and deny NT AUTHORITY\NETWORK in the pipe security descriptor.
- Verify both endpoints and reject connections when identity checks cannot be completed; do not trust a predictable pipe name.
- Expose narrowly defined application operations rather than arbitrary file access, registry modification, process creation, or command execution.
- Enforce protocol versions, explicit message framing, bounded payload and field sizes, command allowlists, schema validation, and operation-specific value validation.
- Normalize paths and restrict them to approved resources, accounting for symbolic links, junctions, reparse points, and time-of-check/time-of-use races.
- Keep impersonation scopes short, verify impersonation succeeds, reliably restore the original identity, and revalidate data crossing into privileged execution.
- Separate parsing and validation from a small privileged execution layer; consider separate processes and restricted channels for sensitive applications.
- Bound connections, pipe instances, queues, concurrency, request frequency, and execution time; support cancellation and promptly release resources from clients exceeding limits.
- Reject invalid sizes before allocation or expensive processing, return controlled error codes, and keep detailed diagnostics in protected logs without secrets or sensitive payloads.
- Use separate endpoints only for materially different trust boundaries, protecting each endpoint independently.
- Independently verify client claims and keep security-sensitive choices, such as approved update locations, signatures, and installation parameters, under server control.