cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · huntress.com

Correlating VSS Activity Helps Detect Ransomware and Credential Theft

Attackers can delete shadow copies to hinder recovery or create them to extract credentials. Because legitimate tools also use VSS, detections should correlate its activity with process behavior, lateral movement, and credential-harvesting signals.
Sep 14, 2026
Detection & Defense · elastic.co

How to Correlate Kubernetes Audit Logs with Container Runtime Data

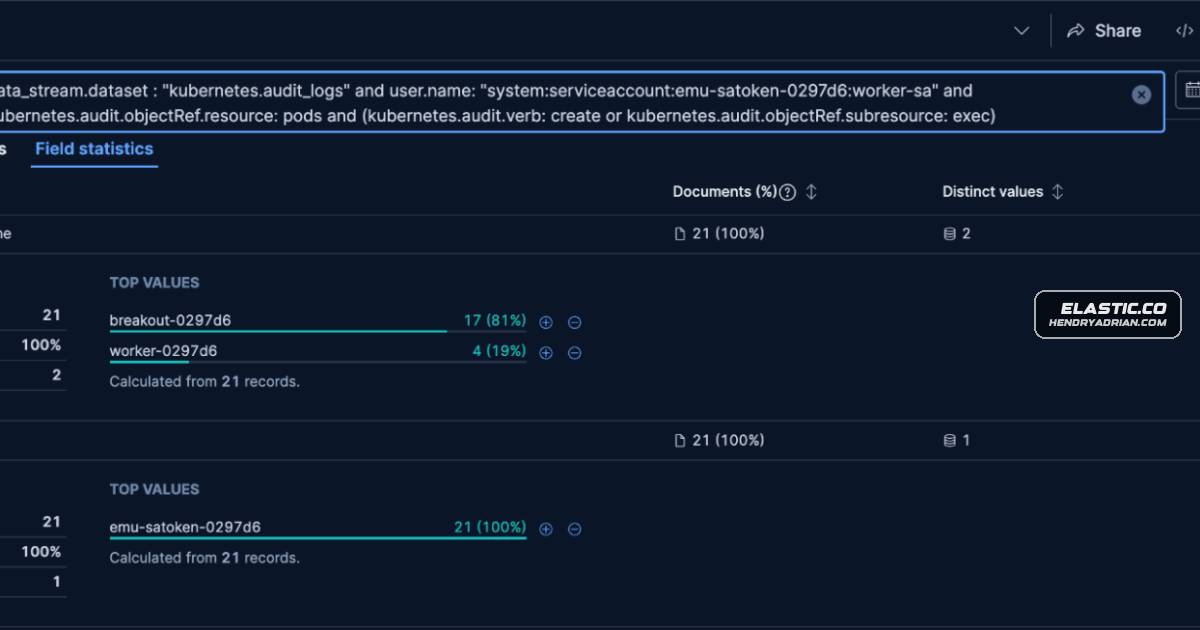
The tutorial shows how to correlate Kubernetes audit logs with Elastic Defend for Containers telemetry to investigate suspicious service-account activity. In an EKS lab, decoded audit exec URIs exposed nsenter and chroot wrappers missing from runtime events.

Sep 13, 2026
Detection & Defense · elastic.co

Layered Linux Detection Framework Targets Privilege Escalation Across Exploit Families

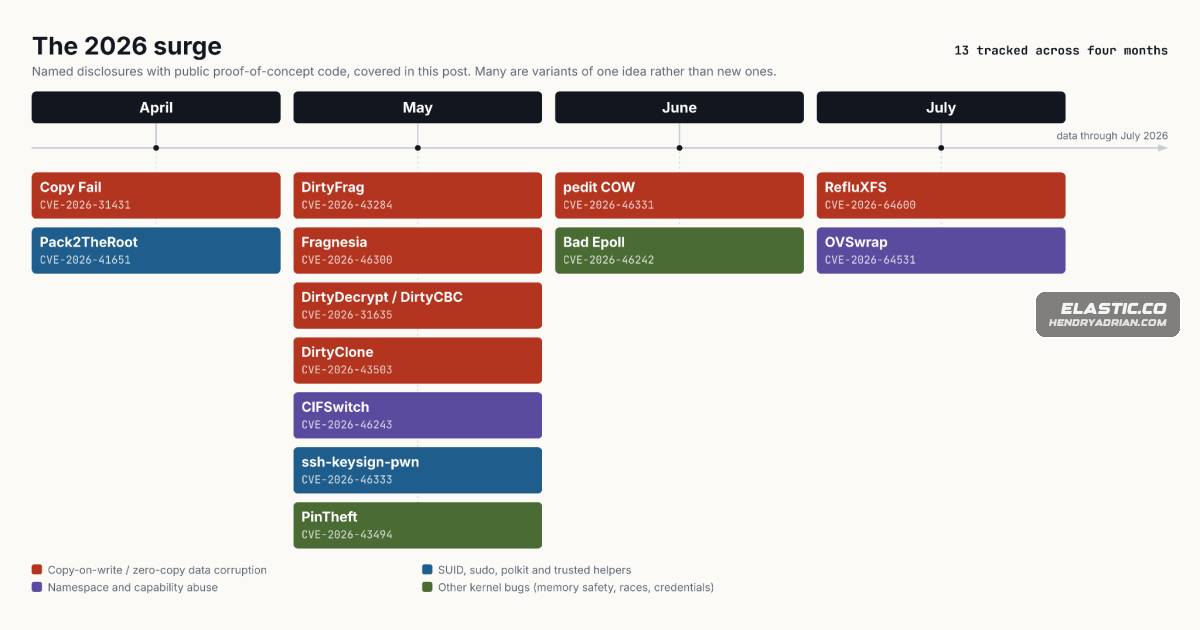
Elastic outlines layered Linux privilege-escalation detection using root-transition correlations and technique-specific rules. Tests cover 11 public exploit PoCs and two SUID misconfigurations, with coverage limitations acknowledged.

Sep 13, 2026
Detection & Defense · helpnetsecurity.com

Arctic Wolf Video Urges Organizations to Plan Ransomware Decisions in Advance

Arctic Wolf’s Kerri Shafer-Page outlines decisions to prepare for ransomware incidents, including containment, negotiation authority and limits, payment tradeoffs, law-enforcement involvement, legal advice, and communications.

Sep 11, 2026
Detection & Defense · cyber.gov.au

Guidance Details Security Controls for Agentic AI Harnesses

The guidance explains how agentic AI harnesses connect LLMs to organizational data and tools, creating security and operational risks. It recommends least privilege, human approval, monitoring, logging and phased deployment to manage those risks.

Sep 11, 2026
Detection & Defense · wazuh.com

How to Detect Windows Attacks with Microsoft Defender ASR and Wazuh

A step-by-step guide to enabling Microsoft Defender ASR rules on Windows, forwarding Defender events to Wazuh, and creating alerts for blocked attack techniques and ASR configuration changes.

Sep 10, 2026
Detection & Defense · decodedsecurity.com

How to Run AI Coding Agents More Safely in YOLO Mode

The article explains the risks of letting AI coding agents run commands without approval and recommends using disposable containers or VMs, scoped credentials, restricted networking, non-root access, and limited project files.

Sep 10, 2026
Detection & Defense · huntress.com

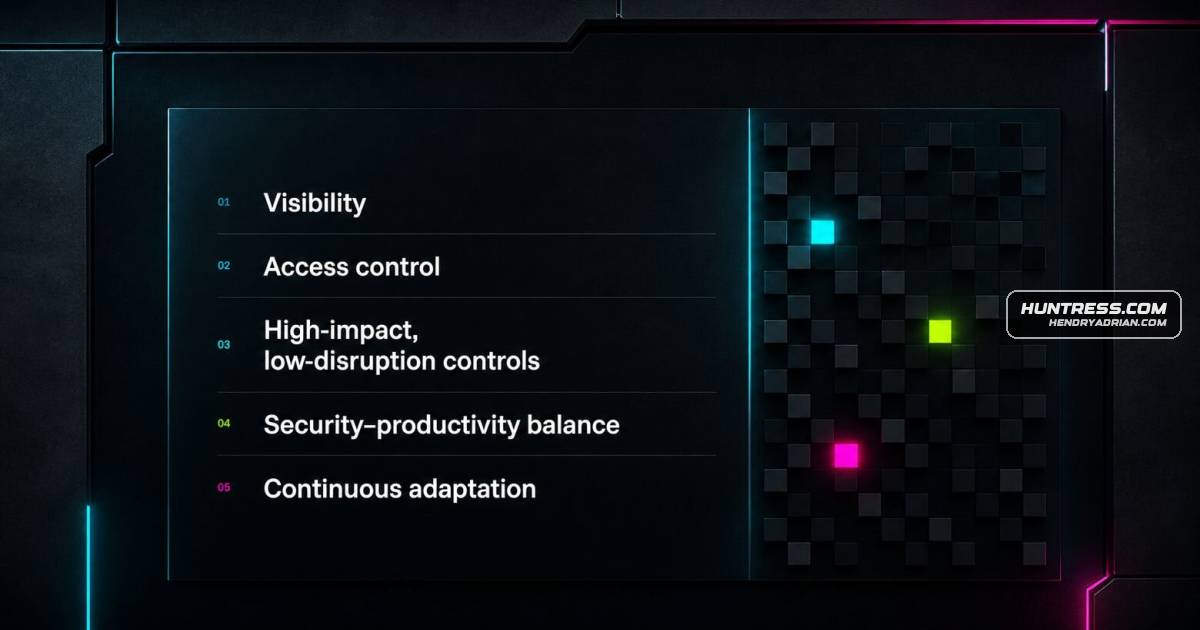
Endpoint Hardening Checklist Targets Common Paths to Business Compromise

Huntress outlines practical endpoint hardening steps for businesses, including limiting exposed remote access, reducing local admin rights, restricting abused tools, patching promptly, and continuously reviewing security posture.

Sep 10, 2026
Detection & Defense · cyber.gov.au

Advisory Explains How Crypter Services Evade Malware Detection

The advisory explains how crypter services obfuscate and encrypt malware to evade detection, including their builder/stub model and counter-antivirus checks, and recommends EDR/HIPS, application control, hardened antivirus settings, and runtime behavioral analysis.

Sep 8, 2026
Detection & Defense · thehackernews.com

Practical Advice for Reducing Identity Security Risks

The article warns that unmanaged privileged accounts and identity sprawl increase breach and lateral-movement risk, and recommends least privilege, continuous reviews, centralized visibility, and automated mitigation.

Sep 7, 2026
Detection & Defense · thehackernews.com

How AI-Native SIEM Could Help Security Teams Reduce Attacker Dwell Time

The article explains how security teams can use MTTD, MTTR, and investigation-workflow metrics to identify delays and assess whether AI-native SIEM helps reduce attacker dwell time and potential business impact.

Sep 7, 2026
Detection & Defense · cyberscoop.com

Human Judgment Remains Critical as AI Takes on More Security Operations

As AI speeds up security analysis, the article urges leaders to retain human context, grant autonomy based on reversibility and blast radius, measure how analysts handle recommendations, and scrutinize confident false negatives.

Sep 4, 2026
Detection & Defense · helpnetsecurity.com

Roy Katmor Outlines Five Checks for Securing AI Agent Credentials

Roy Katmor recommends tracking each AI agent’s owner, tools, credentials, authority, and behavior, then comparing intended with observed activity and applying scoped controls, including a targeted kill switch.

Sep 4, 2026
Detection & Defense · wazuh.com

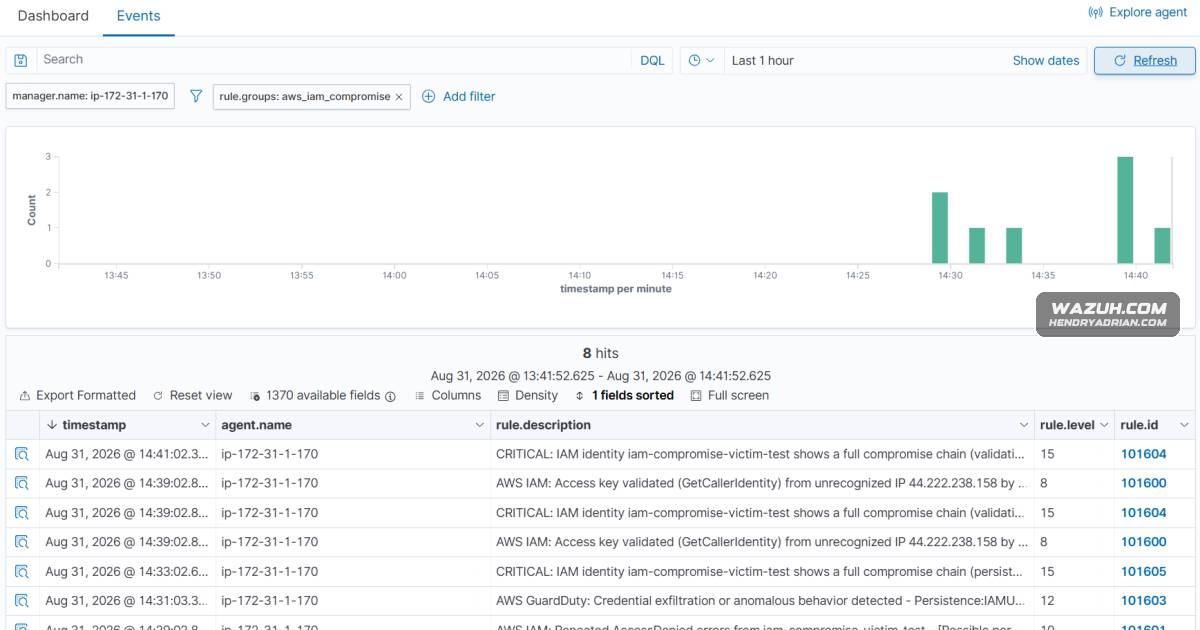
How to Detect AWS Access Key Compromise with Wazuh

A hands-on guide configures Wazuh to ingest AWS CloudTrail and GuardDuty logs, correlate suspicious access-key activity, and alert on validation, enumeration, persistence, and exfiltration signals.

Sep 3, 2026
Detection & Defense · helpnetsecurity.com

GitHub’s Dependabot Team Shares Five Lessons for Safely Ingesting Threat Intelligence

GitHub’s Dependabot team describes safeguards for ingesting malicious-package intelligence across eight ecosystems, including provenance tracking, deduplication, normalization, batch rollback, anomaly detection, and quarantining invalid records.

Sep 3, 2026
Detection & Defense · abstract.security

Detection Guidance for Reported CrowdStrike Falcon Local Privilege-Escalation PoC

A researcher claims FalconFlank can exploit CrowdStrike Falcon’s macro-remediation feature for local privilege escalation. The flaw is unverified; the article provides FDR and Sysmon detection ideas and defensive steps.

Sep 3, 2026
Detection & Defense · bleepingcomputer.com

Six Checks MSPs Should Require for Ransomware Readiness and Recovery

A sponsored MSP checklist covers exposure reduction, cross-environment detection, 24/7 response, protected recovery points, clean restores and multi-tenant operations, with drills to validate recovery objectives.

Sep 2, 2026
Detection & Defense · aikido.dev

Aikido Says Behavior-Based Detection Flagged Obfuscated Keyv Package

Aikido says its behavioral analysis flagged a newly published Keyv version on Aug. 4, 2026, after obfuscated install-time code downloaded Bun and staged another payload; the final payload and any data-theft objective remain unclear.

Sep 1, 2026
Detection & Defense · sysdig.com

Stateful Runtime Detections Aim to Keep Pace With AI-Assisted Cloud Attacks

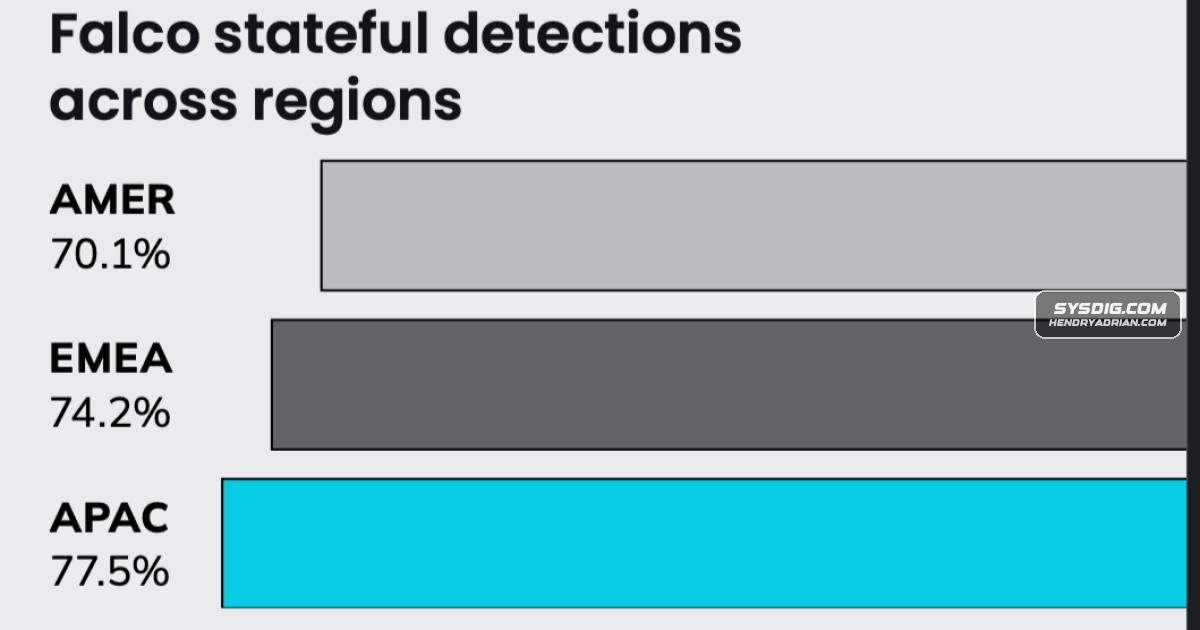
Sysdig argues stateful runtime detections can correlate container actions to reduce alert noise as cloud attacks accelerate, citing adoption and automation figures from its 2026 report and a Falco rule example.

Aug 31, 2026
Detection & Defense · censys.com

Investigating a CFO’s Compromised Phone: A Mobile DFIR Walkthrough

A mobile DFIR walkthrough uses fictional Android and iPhone incidents, informed by Censys ARC research, to show how responders can investigate malware, credential theft, and exploit infrastructure through endpoint, identity, and network telemetry.

Aug 31, 2026
Detection & Defense · helpnetsecurity.com

Joye Purser: Prioritize Exploited Vulnerabilities, Then Likelihood and Severity

Cohesity’s Joye Purser recommends prioritizing active exploitation, then exploit likelihood and severity, while accounting for exposure and business impact. She also outlines remediation targets and cost-conscious defensive controls.

Aug 31, 2026
Detection & Defense · bleepingcomputer.com

Five Practices for Securing File Server Access

Sponsored guidance recommends using dedicated and nested permission groups, relying on NTFS permissions for granular access control, preserving inheritance, and periodically reviewing privileges to secure file servers.

Aug 31, 2026
Detection & Defense · elastic.co

Elastic Says Added Context Raised Its SOC AI Triage Accuracy from 60% to 92%

Elastic says its SOC’s AI verdict correctness rose from 60% to 92% after alert triage was enriched with rule guides, Workday user data and 30 days of closed cases. The post details a three-agent workflow and analyst-feedback loop.

Aug 29, 2026
Detection & Defense · aikido.dev

How to Secure Docker Images with Hardening and Continuous Patching

The article gives practical Docker image-hardening guidance, including minimizing base images, removing unused packages, running as non-root, keeping secrets out of layers, signing images, generating SBOMs, and continuously patching. It also promotes Aikido’s image-patх

Aug 28, 2026
PreviousPage 11 of 26 Next
© 2026 cyber.hendryadrian.com