
Weaver E-cology RCE Flaw Exploited in Attacks Since Mid-March
Summary
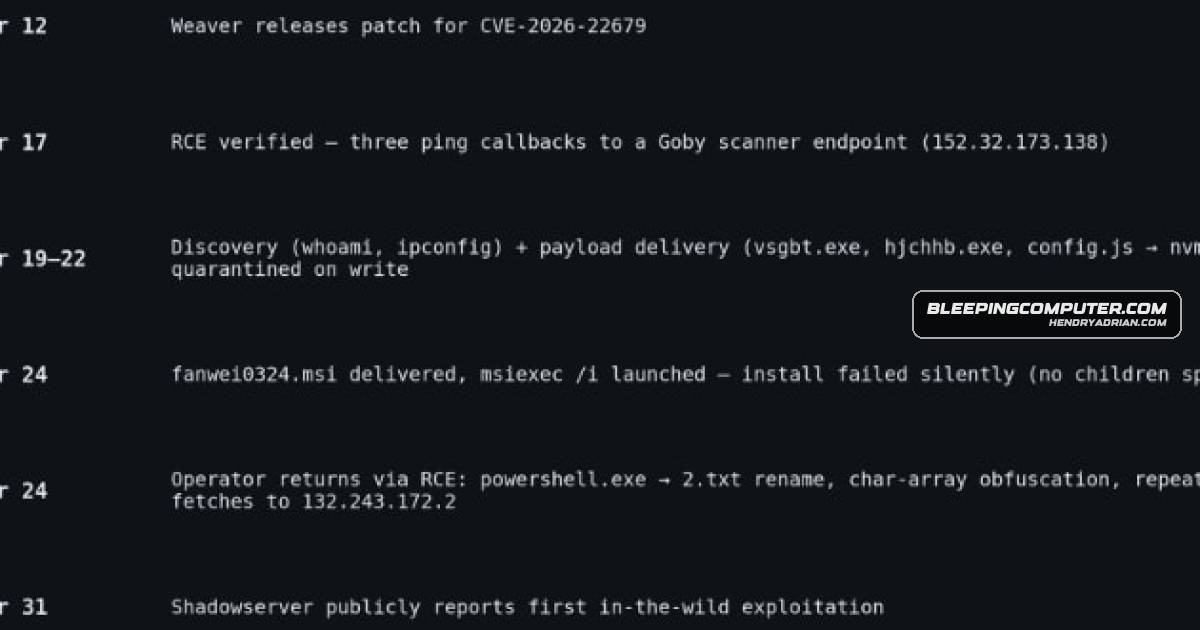
Vega reported attacks exploiting CVE-2026-22679, an unauthenticated RCE flaw in Weaver E-cology 10.0. Endpoint defenses blocked payloads, and researchers saw no persistent access. The vendor's build 20260312 removes the vulnerable debug endpoint.
Key points
- Vega documented attacks exploiting CVE-2026-22679 in Weaver E-cology 10.0, with activity beginning in mid-March.
- The flaw allowed unauthenticated command execution through an exposed debug API that passed user-supplied parameters to backend RPC functionality without validation.
- Attackers tested RCE with ping commands, ran reconnaissance commands, and attempted PowerShell payloads and a target-aware MSI; endpoint defenses blocked execution.
- Vega reported that attackers did not establish a persistent session on the targeted hosts.
- Vendor build 20260312 removes the vulnerable debug endpoint; upgrading is the only mitigation listed.
Article Details
- Vulnerability Types
- Unauthenticated remote code execution (RCE)
- Severity
- Critical
- Affected Versions
- Weaver E-cology 10.0 builds prior to March 12
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryAttackers ran ipconfig during reconnaissance.T1033 · System Owner/User DiscoveryAttackers ran whoami during reconnaissance.T1057 · Process DiscoveryAttackers ran tasklist during reconnaissance.T1059.001 · PowerShellAttackers used PowerShell-based payloads and repeatedly fetched remote scripts through obfuscated, fileless PowerShell.T1105 · Ingress Tool TransferAttackers attempted PowerShell payload downloads and repeatedly fetched remote scripts; endpoint defenses blocked the downloads.T1190 · Exploit Public-Facing ApplicationAttackers exploited the exposed, unauthenticated debug API in Weaver E-cology to obtain remote command execution.