
Progress Patches Critical MOVEit Automation Authentication Bypass
Summary
Progress patched CVE-2026-4670, a critical authentication bypass affecting earlier MOVEit Automation versions, and CVE-2026-5174, a high-severity privilege escalation flaw. It recommends upgrading with the full installer, which causes an outage.
Key points
- CVE-2026-4670 affects MOVEit Automation versions before 2025.1.5, 2025.0.9, and 2024.1.8.
- The authentication bypass can be exploited remotely without privileges in low-complexity attacks requiring no user interaction.
- Progress says upgrading to a patched release with the full installer is the only remediation and will cause a system outage.
- Progress also patched CVE-2026-5174, a high-severity privilege escalation flaw caused by improper input validation.
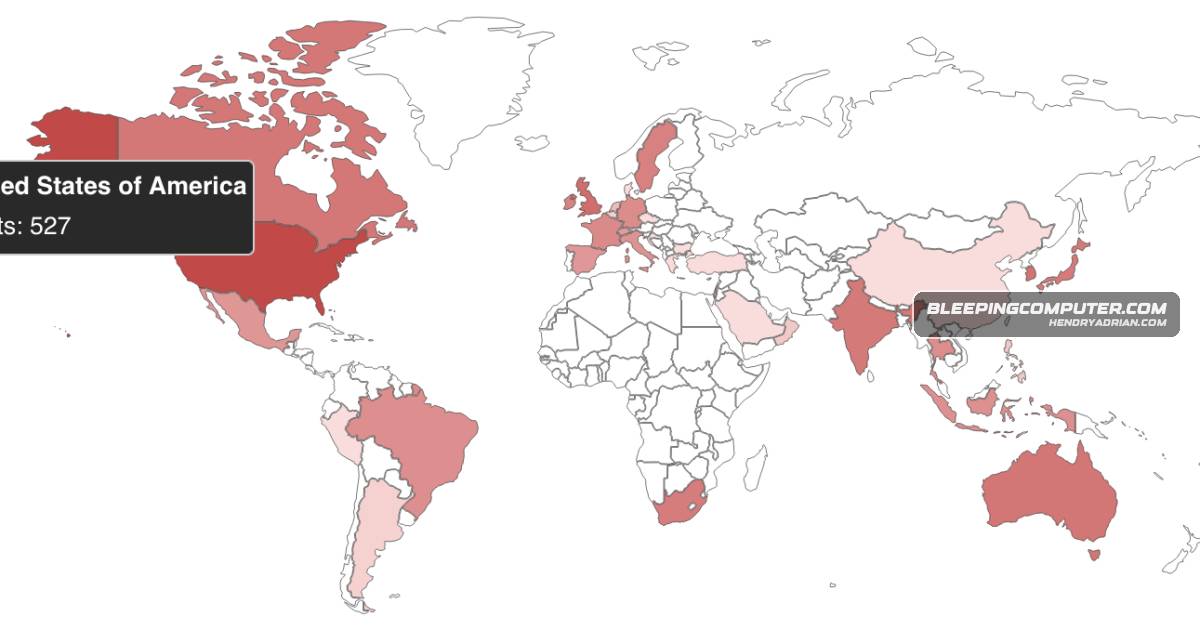
- A Shodan search cited in the article found more than 1,400 MOVEit Automation instances exposed online, including over a dozen linked to U.S. local and state governments.
- Progress had not flagged either flaw as exploited in the wild, and the article says it is unknown how many exposed systems have been secured.
Article Details
- Vulnerability Types
- Authentication bypass
- Improper input validation
- Privilege escalation
- Severity
- Critical for CVE-2026-4670; high for CVE-2026-5174
- Affected Versions
- MOVEit Automation versions before 2025.1.5
- MOVEit Automation versions before 2025.0.9
- MOVEit Automation versions before 2024.1.8
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
CVE
CVE-2026-4670Progress Software · MOVEit AutomationProgress Software warned customers to patch a critical authentication bypass vulnerability (CVE-2026-4670) in MOVEit Automation that allows remote, unauthenticated attackers to bypass authentication in low-complexity,CVE-2026-5174Progress Software · MOVEit AutomationThe company released patched updates (and a fix for a related privilege escalation CVE-2026-5174), recommends upgrading with the full installer despite an expected outage, and noted over 1,400 online instances with some
People
Threat Actors
Vendors
Products
MOVEit Automationwarned customers to patch a critical authentication bypass vulnerability (CVE-2026-4670) in MOVEit Automation that allows remote, unauthenticated attackers to bypass authentication in low-complexity,Progress MOVEit TransferFor instance, the Clop ransomware gang exploited a zero-day in the MOVEit Transfer secure file transfer platform in an extensive series of data theft attacks in 2023 that affected more than 2,100 organizations and over