
Ivanti Patches EPMM Zero-Day RCE Exploited in Limited Attacks
Summary
Ivanti says CVE-2026-6973, an admin-authenticated RCE affecting EPMM 12.8.0.0 and earlier, has seen very limited zero-day exploitation. Fixes are available; Ivanti also patched four other high-severity EPMM flaws.
Key points
- CVE-2026-6973 is an improper input validation flaw that can let remote attackers with administrator privileges execute arbitrary code.
- Ivanti reports very limited exploitation of CVE-2026-6973 but did not identify affected customers.
- Ivanti recommends upgrading to EPMM 12.6.1.1, 12.7.0.1, or 12.8.0.1 and reviewing administrator accounts and rotating credentials where needed.
- The vulnerabilities affect on-premises EPMM, not Ivanti Neurons for MDM, Ivanti EPM, Ivanti Sentry, or other Ivanti products.
- Ivanti also patched CVE-2026-5786, CVE-2026-5787, CVE-2026-5788, and CVE-2026-7821; it said it had no evidence those flaws were exploited in the wild.
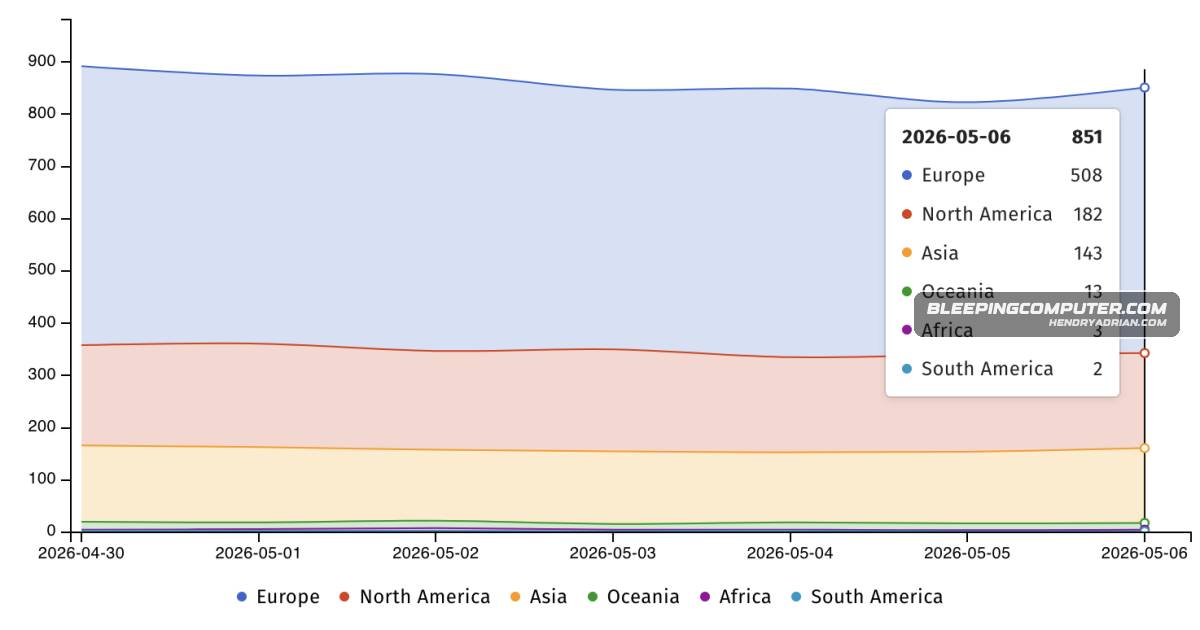
- Shadowserver tracks more than 850 IP addresses with exposed EPMM fingerprints; the article says it is unknown how many have been patched.
Article Details
- Vulnerability Types
- Improper input validation
- Severity
- High
- Affected Versions
- Ivanti EPMM 12.8.0.0 and earlier
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Review accounts with Admin rights and rotate those credentials where necessary.
CVE
CVE-2026-1281Ivanti · Endpoint manager mobileIn January, Ivanti disclosed two other critical EPMM code-injection vulnerabilities (CVE-2026-1281 and CVE-2026-1340) that were exploited in zero-day attacks affecting a “very limited number of customers.”CVE-2026-1340Ivanti · Endpoint manager mobileIn January, Ivanti disclosed two other critical EPMM code-injection vulnerabilities (CVE-2026-1281 and CVE-2026-1340) that were exploited in zero-day attacks affecting a “very limited number of customers.”CVE-2026-5786Ivanti · Endpoint Manager MobileâToday, Ivanti also patched four other high-severity EPMM vulnerabilities (CVE-2026-5786, CVE-2026-5787, CVE-2026-5788, and CVE-2026-7821) that can allow attackers to gain admin access, impersonate registered SentryCVE-2026-5787Ivanti · Endpoint Manager MobileâToday, Ivanti also patched four other high-severity EPMM vulnerabilities (CVE-2026-5786, CVE-2026-5787, CVE-2026-5788, and CVE-2026-7821) that can allow attackers to gain admin access, impersonate registered SentryCVE-2026-5788Ivanti · Endpoint Manager MobileIvanti also patched four other high-severity EPMM vulnerabilities (CVE-2026-5786, CVE-2026-5787, CVE-2026-5788, and CVE-2026-7821) that can allow attackers to gain admin access, impersonate registered Sentry hostsCVE-2026-6973Ivanti · Endpoint Manager MobileIvanti warned customers to patch CVE-2026-6973, a high-severity remote code execution flaw in Endpoint Manager Mobile (EPMM) that has been exploited in zero-day attacks and affects EPMM 12.8.0.0 and earlier.CVE-2026-7821Ivanti · Endpoint Manager Mobilefour other high-severity EPMM vulnerabilities (CVE-2026-5786, CVE-2026-5787, CVE-2026-5788, and CVE-2026-7821) that can allow attackers to gain admin access, impersonate registered Sentry hosts to obtain valid