
CVE-2026-41940 cPanel Flaw Exploited in Sorry Ransomware Attacks
Summary
A critical WHM and cPanel authentication bypass, CVE-2026-41940, is reportedly being exploited to deploy the Sorry Linux encryptor. Shadowserver reports at least 44,000 cPanel IP addresses compromised; an emergency update is available.
Key points
- CVE-2026-41940 is an authentication bypass in WHM and cPanel; an emergency security update has been released.
- The article reports exploitation attempts dating to late February and says attacks have used the flaw to breach servers.
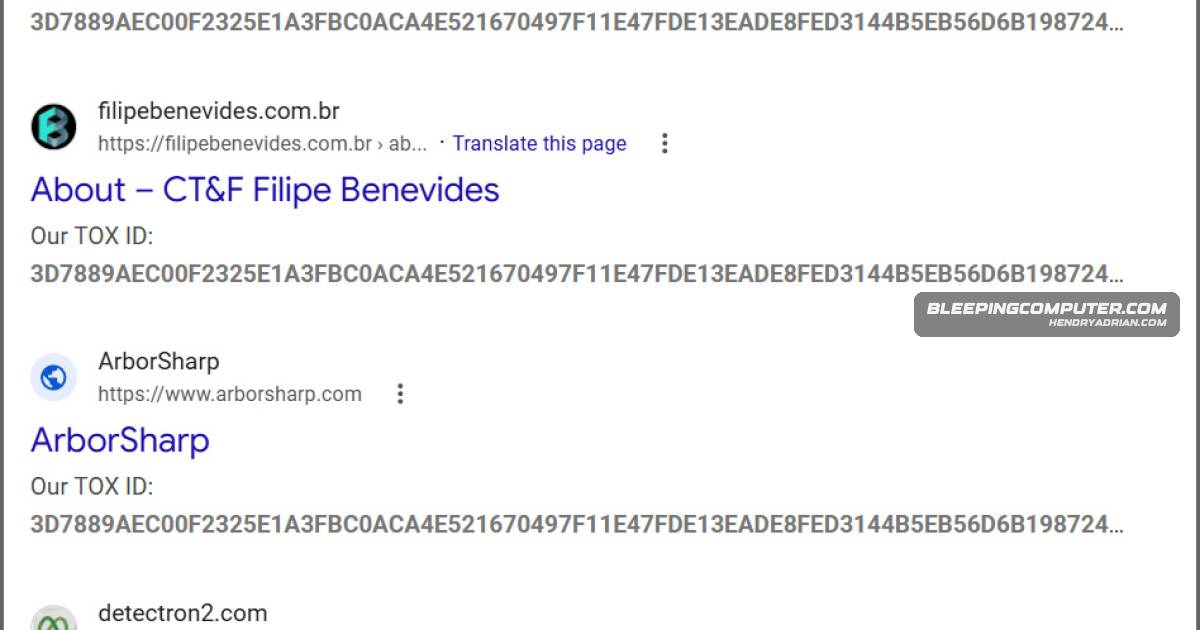
- Shadowserver reports at least 44,000 cPanel IP addresses compromised; hundreds of affected sites have reportedly appeared in Google search results.
- Attackers reportedly deploy a Go-based Linux encryptor called Sorry, which appends the .sorry extension to encrypted files.
- The encryptor reportedly uses ChaCha20, with its encryption key protected by an embedded RSA-2048 public key; an expert says decryption requires the corresponding private key.
- The ransom note, named README.md, directs victims to contact the threat actor through Tox to negotiate payment.
- The article urges WHM and cPanel users to install the available security updates.
Article Details
- Vulnerability Types
- Authentication bypass
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
People
Malware
Products
cPanelA critical authentication bypass in WHM and cPanel (CVE-2026-41940) is being mass-exploited to breach servers and deploy a Linux encryptor used in “Sorry” ransomware attacks.WHMA critical authentication bypass in WHM and cPanel (CVE-2026-41940) is being mass-exploited to breach servers and deploy a Linux encryptor used in “Sorry” ransomware attacks.