
CISA Adds Actively Exploited Linux Copy Fail Flaw to KEV
Summary
CISA added Linux kernel flaw CVE-2026-31431 (Copy Fail) to its KEV catalog, citing active exploitation. The local privilege-escalation flaw can grant root; fixes are available in kernel versions 6.18.22, 6.19.12, and 7.0.
Key points
- CISA added CVE-2026-31431, known as Copy Fail, to its KEV catalog after citing evidence of active exploitation; it did not provide exploitation details.
- The Linux kernel flaw lets an unprivileged local user potentially gain root by corrupting the in-memory page cache of a readable file.
- Fixes are available in Linux kernel versions 6.18.22, 6.19.12, and 7.0; FCEB agencies were advised to apply them by May 15, 2026.
- Researchers described a 732-byte Python proof of concept; Go and Rust versions were also reported in open-source repositories.
- Containerized environments may be at risk of isolation breaches and host-root access when the affected subsystem is accessible.
- If patching is not immediately possible, the article recommends disabling the affected feature, network isolation, and access controls.
Article Details
- Vulnerability Types
- Local privilege escalation
- Kernel page-cache corruption
- Severity
- High (CVSS 7.8)
- Exploitation Status
- active
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Disable the affected feature.
- Implement network isolation.
- Apply access controls.
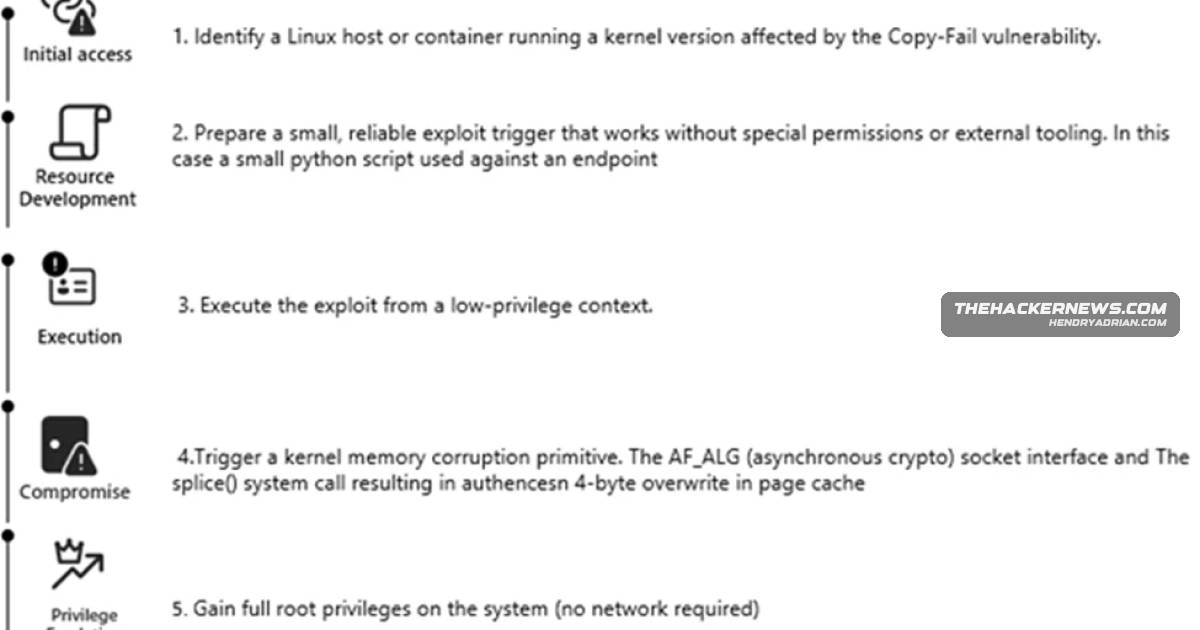
MITRE ATT&CK
CVE
Products
Dockerin its analysis of the flaw, said Copy Fail poses a serious risk to containerized environments, as Docker, LXC, and Kubernetes “grant processes inside a container access to the AF_ALG subsystem if the algif_aeadKubernetesof the flaw, said Copy Fail poses a serious risk to containerized environments, as Docker, LXC, and Kubernetes “grant processes inside a container access to the AF_ALG subsystem if the algif_aead module is loadedLinux kernelVulnerabilities catalog after observing active exploitation of a local privilege escalation bug in the Linux kernel that can allow an unprivileged user to obtain root; fixes are available in kernel versions 6.18.22,LXCin its analysis of the flaw, said Copy Fail poses a serious risk to containerized environments, as Docker, LXC, and Kubernetes “grant processes inside a container access to the AF_ALG subsystem if the algif_aead module