
ThreatBook and Imperva Report Fastjson CVE-2026-16723 Exploitation; No Fastjson 1.x Patch Available
Summary
ThreatBook and Imperva reported in-the-wild exploitation of CVE-2026-16723, affecting Fastjson 1.2.68–1.2.83 in certain Spring Boot fat-JAR applications. Alibaba has no fixed Fastjson 1.x release and recommends SafeMode or migration to Fastjson2.
Key points
- CVE-2026-16723 can enable unauthenticated code execution with Java process privileges in affected Spring Boot executable fat-JAR applications.
- The affected range is Fastjson 1.2.68 through 1.2.83; the described chain requires SafeMode to be disabled and does not require AutoType or a classpath gadget.
- ThreatBook and Imperva reported observing exploitation, but neither provided evidence of successful code execution or confirmed real-world compromises.
- Alibaba had not released a fixed Fastjson 1.x version as of July 25; it recommends enabling SafeMode or migrating to Fastjson2.
- The article describes an attacker-controlled @type value leading to class-resource lookup and, in compatible fat-JARs, loading attacker-controlled bytecode.
- Alibaba lists plain non-fat JARs, generic uber-JARs, and Tomcat or Jetty WAR deployments as unaffected.
Article Details
- Vulnerability Types
- Unauthenticated remote code execution
- Severity
- Critical (CVSS 9.0, assigned by Alibaba)
- Affected Versions
- Fastjson 1.2.68 through 1.2.83
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- unavailable
- Workarounds
- Enable SafeMode with -Dfastjson.parser.safeMode=true.
- Use com.alibaba:fastjson:1.2.83_noneautotype.
- Migrate to Fastjson2 as the long-term fix.
MITRE ATT&CK
T1105 · Ingress Tool TransferThe described newer-JDK exploit path downloads a remote JAR; the article also describes attacker-controlled bytecode fetched through a crafted nested JAR path.T1190 · Exploit Public-Facing ApplicationReported exploitation targets network-reachable Spring Boot applications that pass attacker-controlled JSON to an affected Fastjson parser.
CVE
People
Vendors
Products
FastJsonAttackers are exploiting CVE-2026-16723, a critical Fastjson flaw in Spring Boot fat-JAR applications that can lead to unauthenticated code execution with Java process privileges.fastjson2ThreatBook and Imperva reported in-the-wild activity, while Alibaba has not yet released a patched Fastjson 1.x version and recommends SafeMode or migration to Fastjson2.Spring BootAttackers are exploiting CVE-2026-16723, a critical Fastjson flaw in Spring Boot fat-JAR applications that can lead to unauthenticated code execution with Java process privileges.
Countries
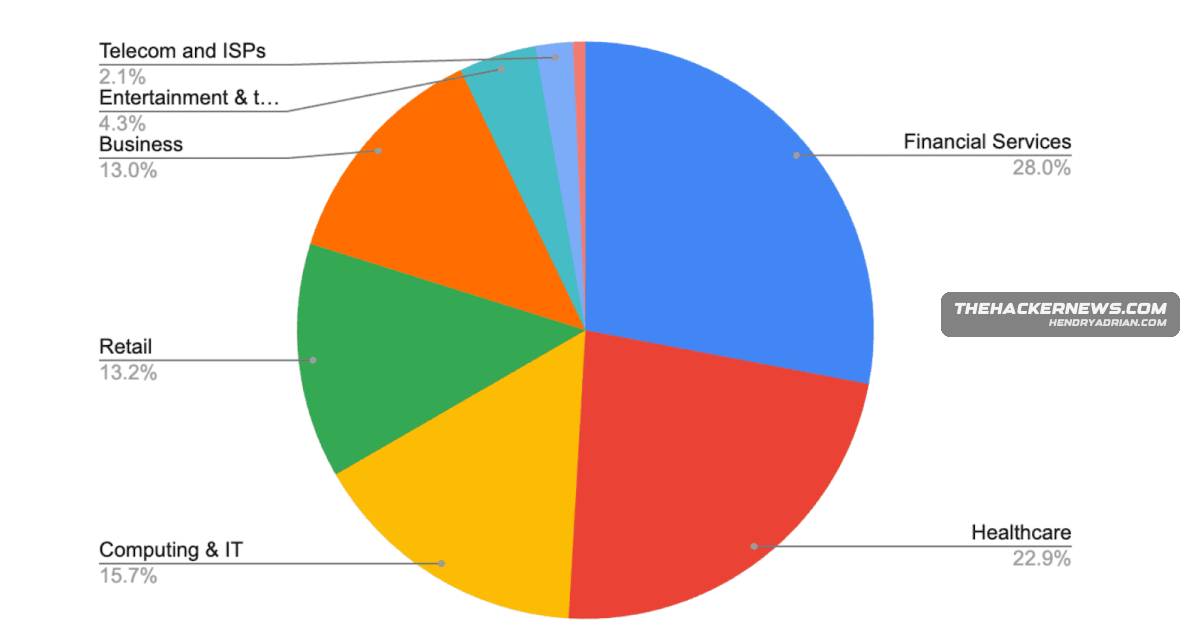
CanadaImperva reported activity against financial services, healthcare, computing, retail, and other organizations, primarily in the United States, with smaller volumes in Singapore and Canada.SingaporeImperva reported activity against financial services, healthcare, computing, retail, and other organizations, primarily in the United States, with smaller volumes in Singapore and Canada.United StatesImperva reported activity against financial services, healthcare, computing, retail, and other organizations, primarily in the United States, with smaller volumes in Singapore and Canada.
Industries
ComputingImperva reported activity against financial services, healthcare, computing, retail, and other organizations, primarily in the United States, with smaller volumes in Singapore and Canada.Financial ServicesImperva reported activity against financial services, healthcare, computing, retail, and other organizations, primarily in the United States, with smaller volumes in Singapore and Canada.HealthcareImperva reported activity against financial services, healthcare, computing, retail, and other organizations, primarily in the United States, with smaller volumes in Singapore and Canada.RetailImperva reported activity against financial services, healthcare, computing, retail, and other organizations, primarily in the United States, with smaller volumes in Singapore and Canada.