
AgentForger Flaw Could Let Phishing Links Deploy Rogue ChatGPT Agents
Summary
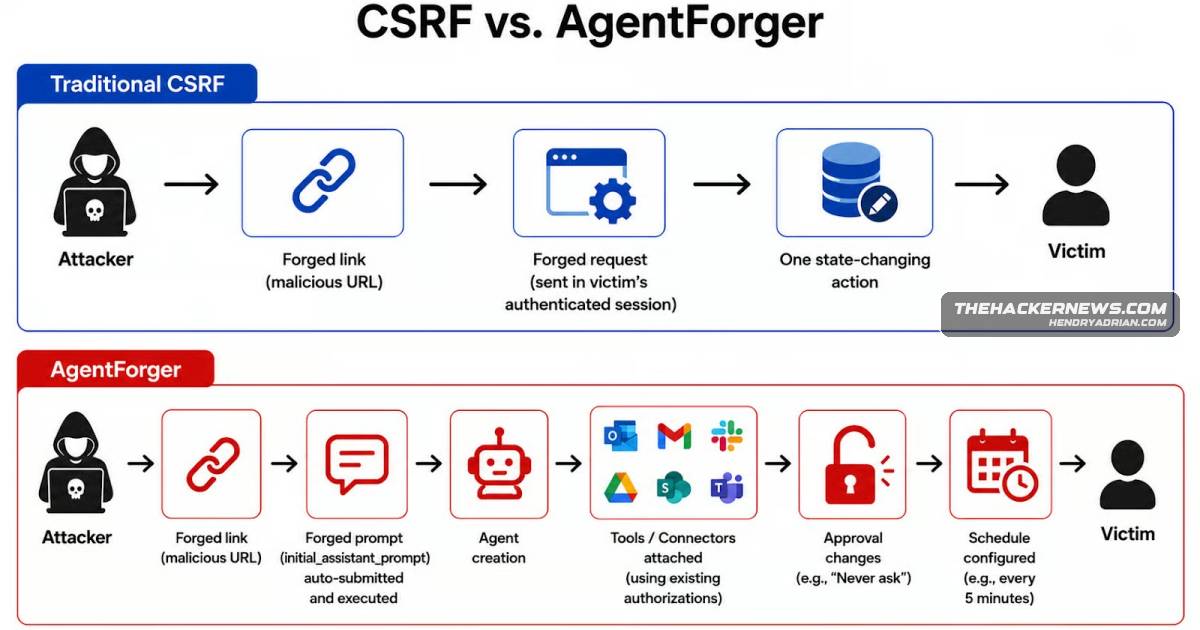
Zenity Labs reported that AgentForger could let a phishing link create and schedule a rogue ChatGPT Workspace Agent using a victim’s authorized connectors. OpenAI fixed the flaw on June 8, 2026.
Key points
- Zenity Labs described AgentForger as a cross-site request forgery flaw in ChatGPT Agent Builder.
- A logged-in user with Workspace Agents access and an authorized connector could trigger agent creation by opening a crafted link.
- The agent could attach available connectors, disable approval prompts, and run on an hourly schedule.
- Preview Mode could execute the agent against connected accounts, according to Zenity Labs.
- The described agent could process emailed tasks, access workspace data, and send results to an attacker.
- OpenAI fixed the flaw on June 8, 2026.
Article Details
- Vulnerability Types
- Cross-site request forgery (CSRF)
- Severity
- Critical
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1204.001 · Malicious LinkThe victim must click the phishing link while logged into ChatGPT for the forged agent creation flow to run.T1213 · Data from Information RepositoriesThe forged agent can retrieve sensitive documents from connected cloud storage and passwords mentioned in Slack messages.T1534 · Internal SpearphishingThe rogue agent can send phishing links to other people on Teams while operating through the victim's account.T1566.002 · Spearphishing LinkThe attack uses a phishing link containing URL parameters that trigger the vulnerable ChatGPT Agent Builder flow.T1656 · ImpersonationThe article says the rogue agent can impersonate the victim when sending phishing links on Teams.
People
Vendors
Products
Agent BuilderA phishing link could trigger a CSRF attack against ChatGPT Agent Builder.ChatGPTZenity Labs disclosed AgentForger, a critical flaw in OpenAI’s ChatGPT Workspace Agents that could let a single phishing link create and deploy an attacker-controlled autonomous agent inside a victim organization.ChatGPT Workspace AgentsZenity Labs disclosed AgentForger, a critical flaw in OpenAI’s ChatGPT Workspace Agents that could let a single phishing link create and deploy an attacker-controlled autonomous agent inside a victim organization.TeamsThe victim has at least one authorized connector (i.e., an already existing ChatGPT integration to an enterprise app like Outlook, Gmail, Google Calendar, Google Drive, Slack, or Teams)