
Adobe Acrobat Chrome Extension Flaw Could Expose WhatsApp Web Data
Summary
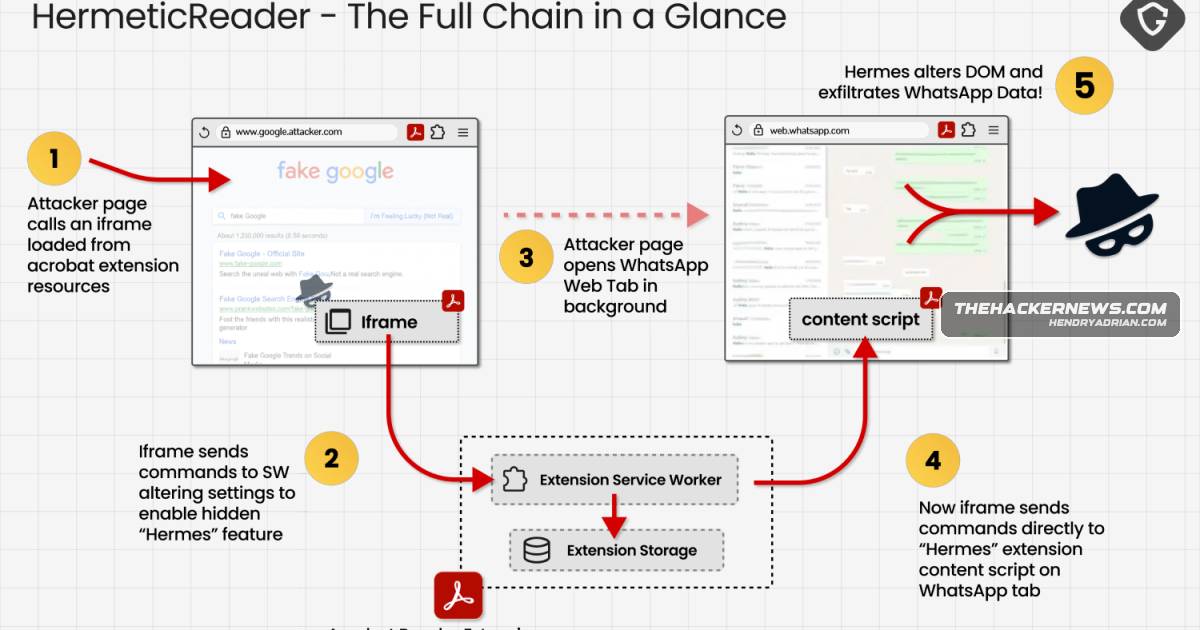
Guardio Labs describes HermeticReader (CVE-2026-48294), a patched Adobe Acrobat Chrome extension flaw affecting versions through 26.5.2.2 that could expose WhatsApp Web data when a user visits a crafted page.
Key points
- HermeticReader is a UXSS-class cross-origin data disclosure flaw tracked as CVE-2026-48294.
- The article says extension versions through 26.5.2.2 are affected and the flaw has been patched; it does not specify a fixed version.
- Exploitation requires user interaction: the victim must visit a crafted page or interact with a malicious URL.
- The described chain uses extension resources to activate its WhatsApp integration and interact with a WhatsApp Web tab.
- Guardio Labs says the technique could expose chat lists, contact names, message previews, profile names, and visible text from an open conversation.
Article Details
- Vulnerability Types
- Universal cross-site scripting (UXSS)
- Cross-origin data disclosure
- Severity
- CVSS 7.4
- Affected Versions
- Adobe Acrobat Chrome extension versions up to and including 26.5.2.2
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- available
CVE
People
Vendors
Products
Adobe Acrobat Chrome extensionGuardio Labs disclosed HermeticReader, a patched vulnerability chain in the Adobe Acrobat Chrome extension that could let an attacker silently read WhatsApp Web data from a victim’s session.WhatsApp WebGuardio Labs disclosed HermeticReader, a patched vulnerability chain in the Adobe Acrobat Chrome extension that could let an attacker silently read WhatsApp Web data from a victim’s session.