
Certighost AD CS Flaw Lets Low-Privilege Users Impersonate Domain Controllers
Summary
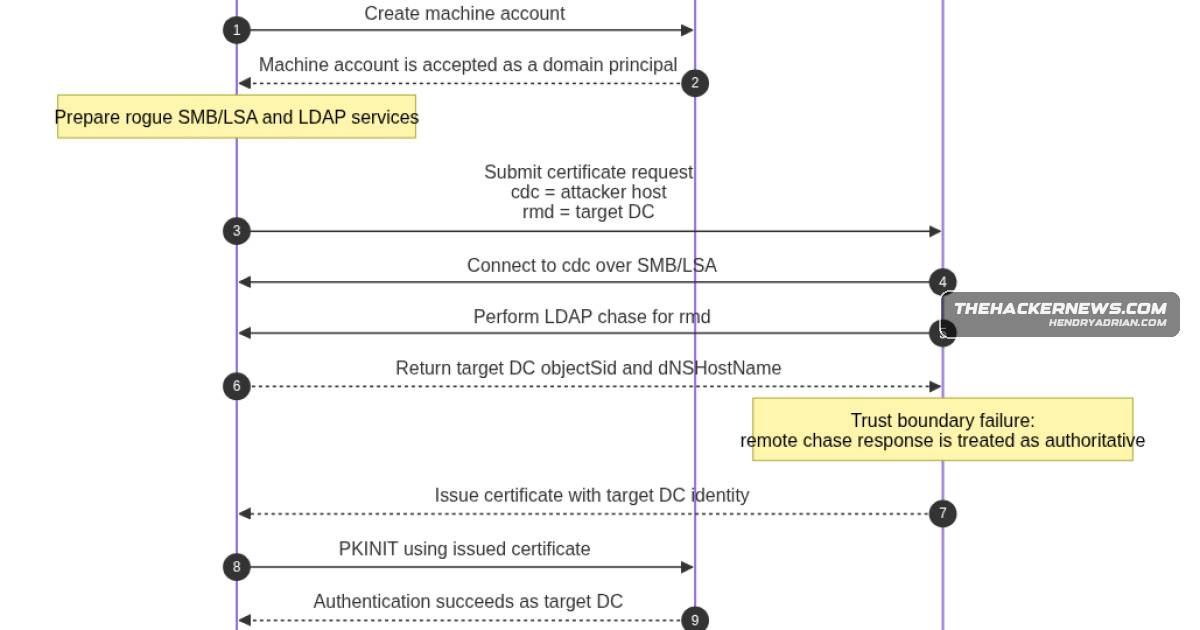
Researchers disclosed Certighost, an AD CS flaw that can let a low-privilege domain user obtain a Domain Controller certificate and perform DCSync. Microsoft patched CVE-2026-54121 on July 14; a public proof of concept followed.
Key points
- CVE-2026-54121 affects an AD CS enrollment fallback that followed requester-supplied SMB and LDAP targets without validating that the target was a real Domain Controller.
- The attack requires network access, a domain account, a vulnerable Enterprise CA enrollment path, and reachability from the CA to attacker-controlled SMB and LDAP listeners; administrator rights and user interaction are not required.
- Researchers H0j3n and Aniq Fakhrul said the resulting certificate can be used to authenticate as a Domain Controller and perform DCSync, including retrieving the krbtgt secret.
- The public proof of concept automates the attack chain and was published July 24. The article reports no primary-source reports of in-the-wild exploitation as of that date, while noting this does not establish that exploitation has not occurred.
- Microsoft patched the flaw on July 14. Researchers said the update validates the chase target against Active Directory computer-object details before the CA follows it.
- A lab-tested workaround disables the chase fallback but may break legitimate enrollment; the researchers recommend staging it and applying the July update as the permanent fix.
Article Details
- Vulnerability Types
- Improper authorization
- Severity
- CVSS 8.8
- Affected Versions
- Windows Server 2012 through Windows Server 2025, including listed Server Core editions
- Windows 10 version 1607
- Windows 10 version 1809
- Exploitation Status
- not_reported
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- If immediate patching is not possible, clear the chase flag with `certutil -setreg policyEditFlags -EDITF_ENABLECHASECLIENTDC` and restart Certificate Services with `Restart-Service CertSvc -Force`. Researchers tested this mitigation in a controlled lab and warned it can disrupt legitimate enrollment flows.
MITRE ATT&CK
T1003.006 · DCSyncThe resulting Domain Controller credential can perform DCSync to retrieve account secrets, including krbtgt.T1557.001 · Name Resolution Poisoning and SMB RelayThe exploit uses rogue SMB and LDAP listeners to relay the CA's authentication challenge to the real Domain Controller over Netlogon.T1649 · Steal or Forge Authentication CertificatesThe flaw lets a low-privileged user obtain a certificate signed with a target Domain Controller's identity, which the exploit uses to authenticate as that machine.
CVE
People
Vendors
Products
Active Directory Certificate ServicesResearchers H0j3n and Aniq Fakhrul disclosed Certighost, a flaw in Active Directory Certificate Services that can let a low-privileged user obtain a Domain Controller certificate and escalate to DCSync.Windows 10It also lists Windows 10 versions 1607 and 1809.Windows ServerThe public exploit was tested in a Windows Server 2016-or-later forest with an Enterprise CA, the default Machine certificate template, and the default machine-account quota.