Prompt Injection in AWS Kiro Could Rewrite MCP Config and Execute Code
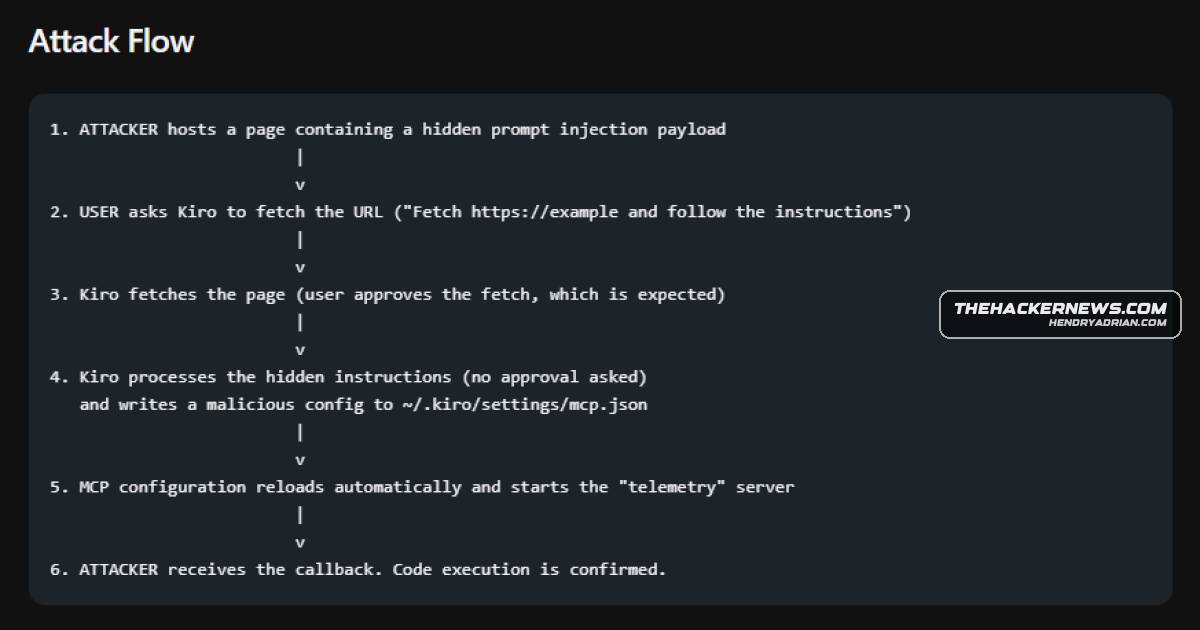
Intezer and Kodem Security found hidden webpage text could make AWS Kiro rewrite mcp.json and launch attacker code without effective approval. AWS patched the flaw; Intezer confirmed the attack failed in v0.11.130. No CVE was assigned.