
Attackers Exploit Sangoma Switchvox SQL Injection Flaw for Remote Code Execution
Summary
Horizon3 reported active exploitation of unauthenticated SQL injection flaw CVE-2026-9586 in Sangoma Switchvox. The vendor fixed it in version 8.4.0.2; administrators are advised to upgrade and check logs for signs of targeting.
Key points
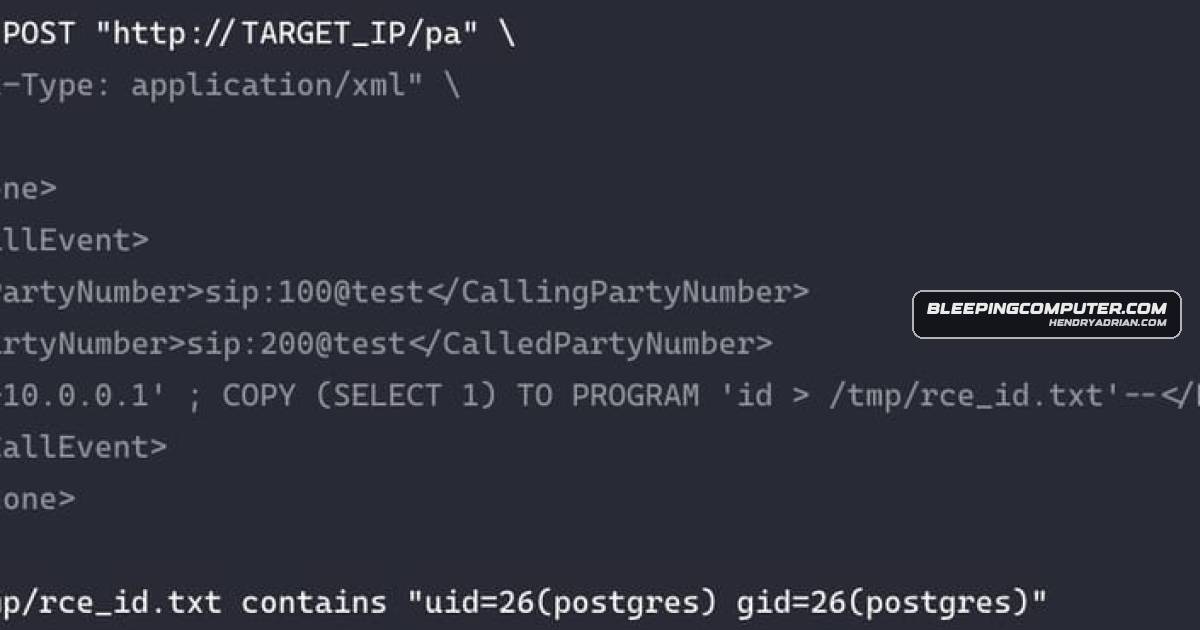
- CVE-2026-9586 is an unauthenticated SQL injection in Switchvox’s /pa HTTP endpoint that can enable remote code execution.
- Horizon3 observed rapid exploitation attempts across multiple honeypots from 176.65.148.184.
- The observed attempts tried to establish a reverse shell, collect process information, and send it to a remote server in base64-encoded form.
- Horizon3 warned that most internet-exposed Switchvox systems may have been or soon be targeted; it cited approximately 4,000 internet-exposed devices.
- Sangoma fixed the flaw in Switchvox 8.4.0.2, released July 14; administrators are advised to upgrade to that version or later.
- Horizon3 recommended checking /var/log/switchvox/db-quirks.log for suspicious statements and reviewing connections to the observed IP, particularly on port 39323.
Article Details
- Vulnerability Types
- Unauthenticated SQL injection
- Remote code execution
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 176[.]65[.]148[.]184 | Source IP observed by Horizon3 honeypots during active exploitation attempts; also listed as an address administrators should check for suspicious network connections. |
MITRE ATT&CK
T1057 · Process DiscoveryAfter the initial payload, the attacker collected information about the top processes running on the Switchvox system.T1059.004 · Unix ShellA crafted XML request was used to execute operating-system commands, and the attacker attempted to establish a reverse shell.T1132.001 · Standard EncodingThe collected process information was transmitted to a remote server in base64-encoded form.T1190 · Exploit Public-Facing ApplicationAttackers exploited the unauthenticated SQL injection in Switchvox’s exposed /pa endpoint.