
Attackers Target Citrix NetScaler Authentication Bypass Flaw CVE-2026-19490
Summary
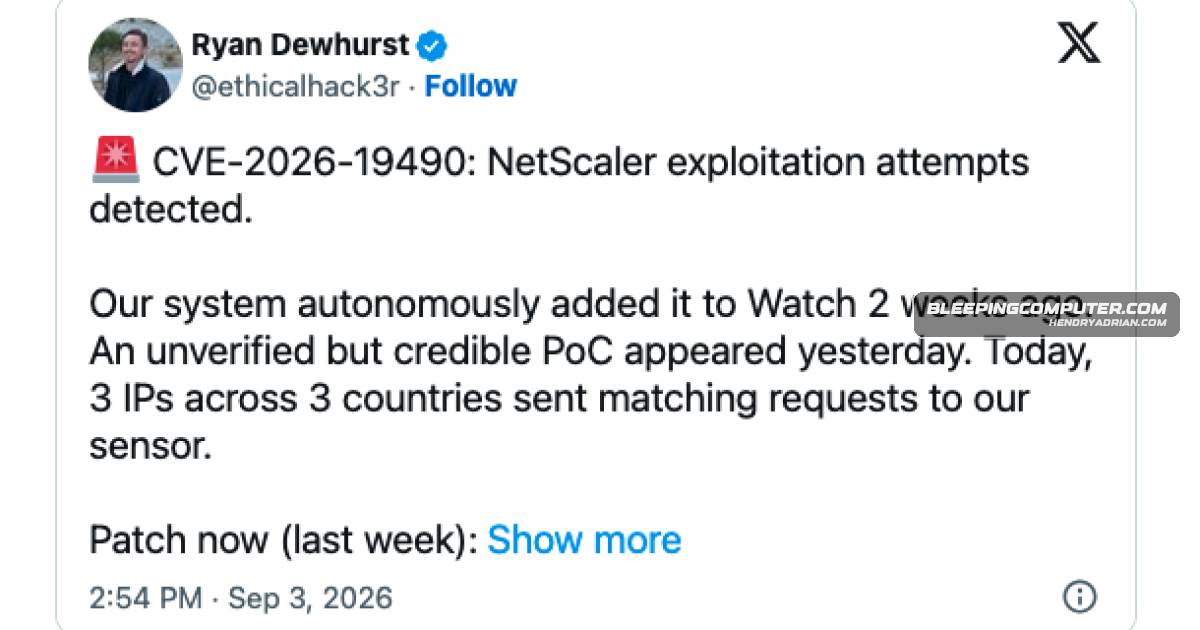
Previdian and Belgium’s NCC-BE report attempts to exploit CVE-2026-19490, a Citrix NetScaler authentication bypass. Successful compromise is unconfirmed; Citrix urges administrators to patch affected appliances.
Key points
- CVE-2026-19490 can enable remote authentication bypass on certain NetScaler ADC and Gateway configurations.
- Previdian observed requests matching a public proof of concept from three source IPs on September 3; the researcher said this indicates attempts, not confirmed compromise.
- Belgium’s NCC-BE warned of exploitation attempts and urged administrators to prioritize patching.
- Citrix had addressed the flaw and recommended upgrading affected appliances to the specified builds.
- Shadowserver tracks more than 22,000 exposed NetScaler ADC appliances and nearly 1,700 Gateway instances; the article says it is unknown how many are vulnerable or patched.
Article Details
- Vulnerability Types
- Remote authentication bypass
- Severity
- Critical
- Exploitation Status
- reported
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Upgrade impacted appliances to the recommended builds.
CVE
CVE-2026-19490Attackers are actively targeting CVE-2026-19490, a critical Citrix NetScaler authentication bypass flaw, after a credible proof-of-concept exploit was published online.CVE-2026-3055Citrix urged admins to patch two other NetScaler flaws (CVE-2026-3055 and CVE-2026-4368) in March, just days before threat actors began exploiting them in attacks.CVE-2026-4368Citrix urged admins to patch two other NetScaler flaws (CVE-2026-3055 and CVE-2026-4368) in March, just days before threat actors began exploiting them in attacks.
People
Vendors
Products
NetScaler ADCCitrix and Belgium’s NCC-BE have urged administrators to patch vulnerable NetScaler ADC and NetScaler Gateway appliances immediately, as evidence points to exploitation attempts but not yet confirmed compromise.NetScaler GatewayCitrix and Belgium’s NCC-BE have urged administrators to patch vulnerable NetScaler ADC and NetScaler Gateway appliances immediately, as evidence points to exploitation attempts but not yet confirmed compromise.
Countries
Australia“On 3 September, one of our NetScaler sensors received requests matching the PoC from three distinct source IPs, geolocated to Australia, the United States and Germany,” Dewhurst told BleepingComputer.Germany“On 3 September, one of our NetScaler sensors received requests matching the PoC from three distinct source IPs, geolocated to Australia, the United States and Germany,” Dewhurst told BleepingComputer.United States“On 3 September, one of our NetScaler sensors received requests matching the PoC from three distinct source IPs, geolocated to Australia, the United States and Germany,” Dewhurst told BleepingComputer.