
Unpatched StyleSmuggler Flaw Exploited to Install Backdoors on Magento Stores
Summary
Attackers are exploiting the unauthenticated StyleSmuggler flaw in Magento Open Source and Adobe Commerce to execute code and install persistent backdoors. Two stores were confirmed compromised; Adobe had not released a fix as of September 6.
Key points
- Sansec said exploitation began September 4; Disrex independently reported two Magento Open Source stores compromised and a third attacked but not breached.
- Sansec said versions 2.4.6-p15 through 2.4.9 are affected; Adobe had not published an advisory, CVE, patch, or workaround as of September 6.
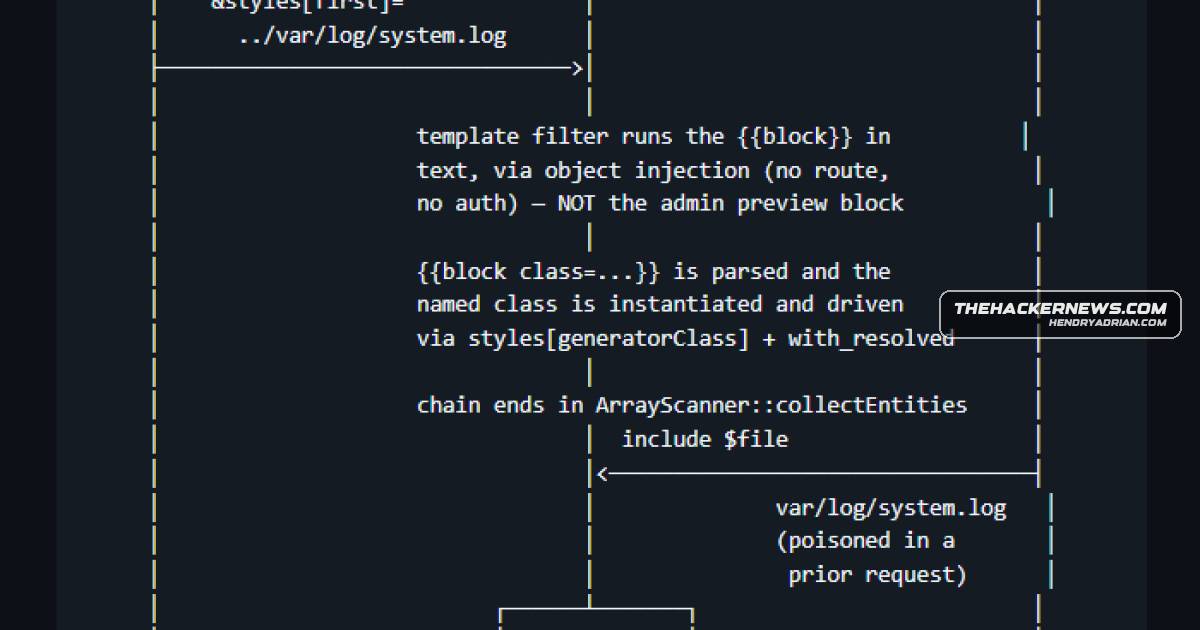
- The reported attack plants PHP code in a Magento-written file and triggers its execution through the Payment Transaction Failed Reminder email process.
- The implant runs as the site user, disguises itself as a kernel thread, and uses a cron entry to restart every five minutes.
- Disrex said it found no evidence of data exfiltration or other listed follow-on activity on the two stores; both were contained, and credential rotation was underway.
- Sansec advised temporarily disabling GraphQL until a fix is available. Disrex also published unofficial mitigations, while warning that some rules block the campaign as observed rather than fixing the flaw.
- Disrex said a scanner reported one infected store clean because its scan was limited to the document root, while the implant was installed in the account's home directory.
Article Details
- Vulnerability Types
- Unauthenticated remote code execution
- Affected Versions
- Magento Open Source 2.4.6-p15 through 2.4.9
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- unavailable
- Workarounds
- Temporarily disable GraphQL until Adobe releases a fix.
- Add proc_open to PHP's disable_functions.
- Mount /tmp, /var/tmp, and /dev/shm with noexec.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 247[.]cdnflare[.]xyz | Malware download host listed by Sansec. |
| IPV4 | 5[.]181[.]86[.]133 | Attacker source address sending requests in bulk, according to Disrex. |
| IPV4 | 88[.]216[.]72[.]181 | Attacker source address listed by Sansec. |
| IPV4 | 99[.]84[.]67[.]186 | Command-and-control address listed by Sansec for WebSocket over TLS. |
| SHA256 | 251fabd50d7b18a8b5e1b3ef5d64e7198c17244778f6461fb1ab07f6169bf220 | SHA-256 of the implant running in memory on one Disrex store. |
| SHA256 | 8334b434fa3fe9f59cebe9609b11e0b1fd19d10212c45c705adec1902a1d06ef | SHA-256 of the implant file found on disk at both Disrex stores. |
| SHA256 | e315687a1dfe61ef4a5a5642214db6d3b2b05d81391285eebc2af664641a26a7 | SHA-256 of Sansec's sample of the implant. |
MITRE ATT&CK
T1053.003 · CronA cron entry restarted the implant every five minutes, providing persistence.T1059 · Command and Scripting InterpreterThe exploit caused Magento to execute injected PHP code, which attempted PHP functions to start a process.T1071.001 · Web ProtocolsSansec identified the implant's command-and-control traffic as using WebSocket over TLS.T1105 · Ingress Tool TransferThe PHP dropper downloaded and launched the implant.T1190 · Exploit Public-Facing ApplicationAttackers exploited the unauthenticated StyleSmuggler flaw in Magento storefronts to execute code on store servers.
Vendors
AdobeAttackers are exploiting the unpatched StyleSmuggler flaw in Magento Open Source and Adobe Commerce to execute code on store servers and plant persistent backdoors without authentication.DisrexSansec and Disrex confirmed active compromises affecting Magento Open Source versions 2.4.6-p15 through 2.4.9, and advised merchants to disable GraphQL temporarily while waiting for Adobe’s fix.SansecSansec and Disrex confirmed active compromises affecting Magento Open Source versions 2.4.6-p15 through 2.4.9, and advised merchants to disable GraphQL temporarily while waiting for Adobe’s fix.
Products
Adobe CommerceAttackers are exploiting the unpatched StyleSmuggler flaw in Magento Open Source and Adobe Commerce to execute code on store servers and plant persistent backdoors without authentication.MagentoAttackers are exploiting the unpatched StyleSmuggler flaw in Magento Open Source and Adobe Commerce to execute code on store servers and plant persistent backdoors without authentication.Sansec ShieldThe store Disrex labels Store A ran Magento Open Source 2.4.8 and was a Sansec Shield customer, with the module installed, enabled, and licensed.