cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · bleepingcomputer.com

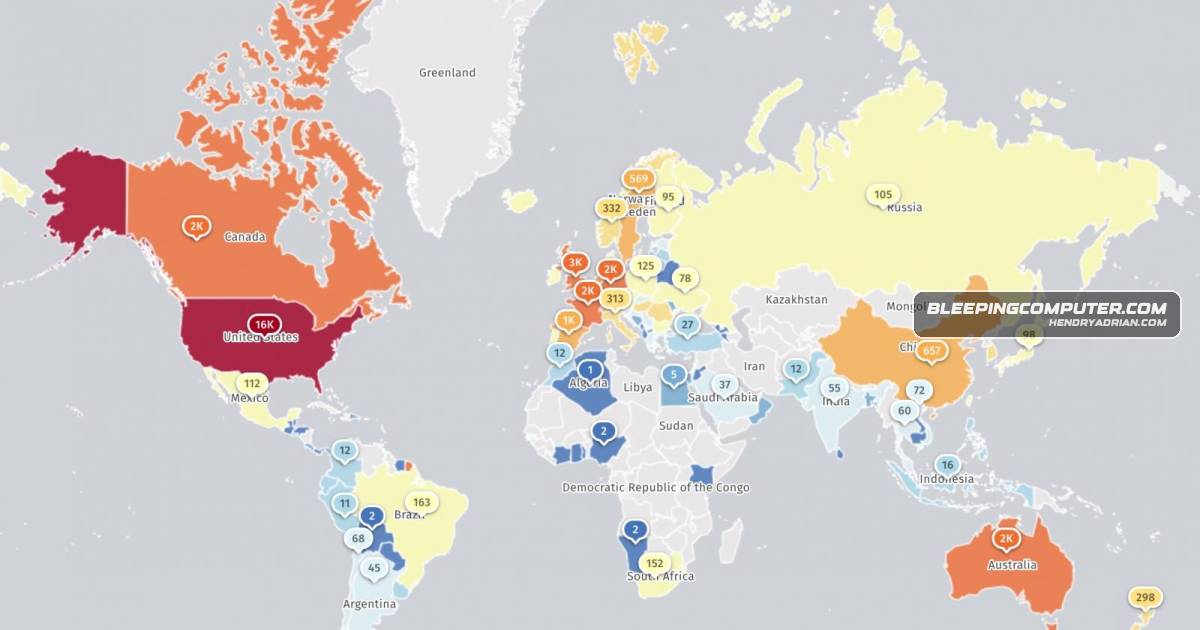
Over 36,000 Internet-Exposed Plex Servers Remain Unpatched Against Security Flaws

Plex says multiple flaws affect Media Server v1.43.2 and earlier and urges users to upgrade. Shadowserver reports more than 36,000 exposed instances remain unpatched; the flaws have no CVE IDs yet.

Sep 9, 2026
Vulnerability & Exploit · thehackernews.com

cPanel Patches EmailTrack Flaw That Could Let Hosting Accounts Gain Root Access

CVE-2026-67401 affects supported cPanel and WHM versions. An authenticated account with mail-related privileges could use EmailTrack to create files and potentially run code as root. Fixed builds are available; no public exploit or exploitation report was found.

Sep 9, 2026
Vulnerability & Exploit · thehackernews.com

Google Patches Actively Exploited Chrome V8 Zero-Day Among 230 Vulnerabilities

Google patched 230 Chrome vulnerabilities, including actively exploited V8 flaw CVE-2026-87491. Updated versions are available for Windows, macOS, and Linux; users of Chromium-based browsers should apply fixes when available.

Sep 9, 2026
Vulnerability & Exploit · thehackernews.com

CISA Flags Actively Exploited N-able N-central RCE Flaw

CISA added CVE-2026-86218, a critical pre-authentication RCE flaw in N-able N-central, to its KEV catalog. N-able reports in-the-wild exploitation and released a hotfix; Huntress cannot confirm which flaw was used in a customer compromise.

Sep 9, 2026
Vulnerability & Exploit · helpnetsecurity.com

WeChat VoIP Flaw Enabled Zero-Click WeWorm Account Hijacking

Calif researchers say a WeChat VoIP memory-corruption flaw enabled WeWorm to hijack accounts and spread through calls without user interaction. Tencent issued app updates and server-side mitigations; technical details remain undisclosed.

Sep 9, 2026
Vulnerability & Exploit · fieldeffect.com

ConnectWise Patches Critical ScreenConnect File-Transfer Vulnerability After Worm-Like Campaign

ConnectWise patched ScreenConnect CVE-2026-84869 in version 26.6.5. Researchers described malware spreading through rogue clients, but ConnectWise has not linked the campaign to the vulnerability.

Sep 9, 2026
Vulnerability & Exploit · arcticwolf.com

N-able N-central CVE-2026-86218 Enables Pre-Auth RCE; Patch Available

Arctic Wolf reports that CVE-2026-86218 enables unauthenticated remote code execution on N-able N-central systems before build 2026.3.1.14. Exploitation was observed before disclosure; N-able released a hotfix.

Sep 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

SAP Patches Critical OVERPASS Kernel Flaw and S4GET NetWeaver Vulnerability

SAP’s September 2026 updates fix 20 flaws, including OVERPASS, a SAP Kernel buffer overflow that can enable administrative command execution, and S4GET, a NetWeaver Message Server authentication flaw that can expose clusters to remote code execution.

Sep 8, 2026
Vulnerability & Exploit · rapid7.com

Two N-able N-central Flaws Allow Unauthenticated Attackers to Create Administrator Accounts

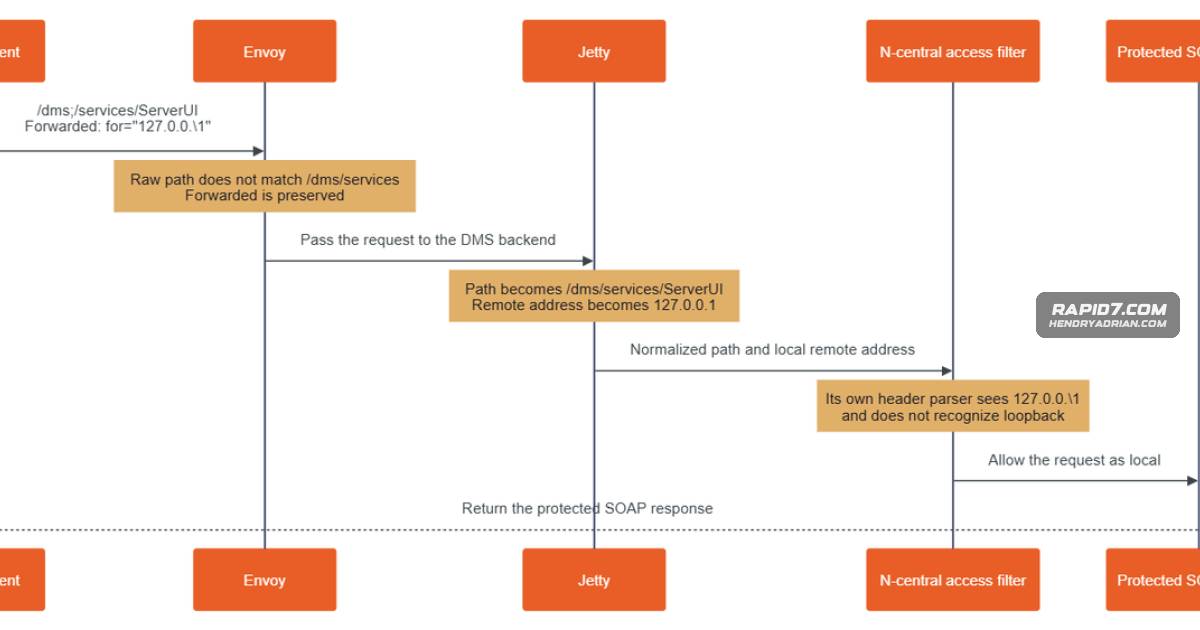
Rapid7 disclosed two N-central vulnerabilities that can be chained to bypass authentication and create a privileged account. All versions before 2026.3.1.13 are affected; hosted customers have already been updated.

Sep 8, 2026
Vulnerability & Exploit · securityweek.com

MikroTik Patches RouterOS Flaws Reportedly Chained to Take Over Routers

CERT Poland says attackers are chaining two MikroTrick flaws to take control of MikroTik routers with publicly accessible SSH. MikroTik has released patches and urges users to update.

Sep 8, 2026
Vulnerability & Exploit · helpnetsecurity.com

MikroTik RouterOS Flaws Exploited to Hijack Internet-Exposed Devices

CERT Polska says attackers are exploiting the MikroTrick chain to take over internet-exposed MikroTik devices via SSH. MikroTik released patched RouterOS versions; administrators should update and check for signs of compromise.

Sep 7, 2026
Vulnerability & Exploit · bleepingcomputer.com

Magento StyleSmuggler Zero-Day Exploited to Install Linux Backdoor

Sansec reports active exploitation of the StyleSmuggler zero-day in all Magento and Adobe Commerce versions, deploying a Linux backdoor. Adobe was preparing a fix; Sansec advised disabling GraphQL until one is available.

Sep 7, 2026
Vulnerability & Exploit · helpnetsecurity.com

N-able Patches Critical N-central RCE; Customer Notice Says It Was Exploited

N-able released Hotfix 4 for critical pre-authenticated RCE CVE-2026-86218 in N-central. A private notice said it was exploited in the wild, while the public advisory reported no confirmed production exploitation.

Sep 7, 2026
Vulnerability & Exploit · securityweek.com

Researcher Releases Three Zero-Day Exploits Targeting Avast, CrowdStrike and Nvidia

Nightmare Eclipse released three proof-of-concept exploits targeting Avast, CrowdStrike and Nvidia products. GenDigital says it fixed the Avast issue; CrowdStrike and Nvidia say they are investigating, with CrowdStrike advising a policy change.

Sep 7, 2026
Vulnerability & Exploit · bleepingcomputer.com

ConnectWise Issues Temporary Mitigation for Unpatched ScreenConnect Flaw

A newly discovered ScreenConnect file-transfer flaw affects cloud and on-premises deployments. ConnectWise advises disabling TransferFiles permissions while it prepares a patch; the flaw has no CVE ID yet.

Sep 7, 2026
Vulnerability & Exploit · bleepingcomputer.com

MikroTik RouterOS Flaws Chained to Hijack Internet-Exposed Routers

Poland’s CERT says the MikroTrick chain exploits two RouterOS flaws to take over routers with exposed SSH. MikroTik released fixes and startup compromise detection; CERT advises updates and securing exposed services.

Sep 7, 2026
Vulnerability & Exploit · thehackernews.com

N-able Releases Fourth N-central Hotfix for Critical Pre-Auth RCE Flaw

N-able’s Hotfix 4 fixes CVE-2026-86218 in on-premises N-central builds before 2026.3.1.14. The company’s notices conflict on in-the-wild exploitation; hosted instances are patched, and on-premises users are urged to update.

Sep 7, 2026
Vulnerability & Exploit · securityweek.com

Adobe Commerce and Magento Zero-Day Used to Backdoor Online Stores

Sansec reports active exploitation of the StyleSmuggler zero-day in Adobe Commerce and Magento, enabling PHP injection and deployment of a Rust backdoor. Adobe fixes were expected September 8, but it was unclear when the flaw would be addressed.

Sep 7, 2026
Vulnerability & Exploit · helpnetsecurity.com

ConnectWise Confirms ScreenConnect File-Transfer Flaw and Recommends Disabling Transfers

ConnectWise confirmed a ScreenConnect file-transfer flaw affecting Cloud and On-Premise deployments and advised disabling transfers pending a fix. Separately, Huntress reported rogue clients spreading VBScript payloads and persisting on systems.

Sep 7, 2026
Vulnerability & Exploit · bleepingcomputer.com

N-able patches critical N-central RCE; exploitation remains unconfirmed

N-able released N-central 2026.3 HF4 for unauthenticated RCE CVE-2026-86218. The company says exploitation is unconfirmed; Huntress flagged possible zero-day activity, and Shadowserver tracks nearly 1,500 exposed servers.

Sep 7, 2026
Vulnerability & Exploit · aikido.dev

StyleSmuggler Zero-Day Reportedly Enables Unauthenticated RCE on Magento and Adobe Commerce

Aikido reports an unauthenticated GraphQL-to-template RCE affecting current Magento Open Source and Adobe Commerce, with exploitation reported since September 4. The post conflicts on whether Adobe has issued hotfixes.

Sep 7, 2026
Vulnerability & Exploit · thehackernews.com

Attackers Exploit Internet-Exposed MikroTik RouterOS SSH to Gain Admin Access

CERT Polska reports attacks since at least September 2 exploiting exposed MikroTik RouterOS SSH for unauthenticated admin access. Updates are available; the reported MikroTrick flaw chain and zero-day status remain under investigation.

Sep 6, 2026
Vulnerability & Exploit · huntress.com

N-able Issues N-central Hotfix 4 for Actively Exploited Pre-Auth RCE

N-able released Hotfix 4 for an actively exploited, critical pre-auth RCE in on-prem N-central. Huntress also reports separate authentication-bypass flaws and urges patching, restricted access, and checks for suspicious accounts and activity.

Sep 6, 2026
Vulnerability & Exploit · thehackernews.com

Broadcom Patches Critical VMware Workstation and Fusion Flaws Enabling Host Code Execution

Broadcom patched two VMware Workstation and Fusion flaws, including a critical integer overflow that could enable host code execution by a local VM administrator. A separate HGFS flaw was also fixed; no in-the-wild exploitation was reported.

Sep 5, 2026
PreviousPage 32 of 65 Next
© 2026 cyber.hendryadrian.com