
Over 440,000 Exploit Attempts Target WordPress Super Forms and Elementor Pro Flaws
Summary
Wordfence reports over 440,000 blocked exploit attempts against unauthenticated file-upload RCE flaws in Super Forms and Elementor Pro. Site owners should patch and check for malicious PHP files.
Key points
- CVE-2026-14894 affects Super Forms and allows unauthenticated arbitrary file uploads, including PHP; it is fixed in version 6.3.314.
- CVE-2026-32475 affects Elementor Pro and allows unauthenticated PHP uploads through forms with a File Upload field; it is fixed in version 4.2.2.
- Wordfence reported blocking more than 250,000 attempts against CVE-2026-14894 and more than 190,000 against CVE-2026-32475.
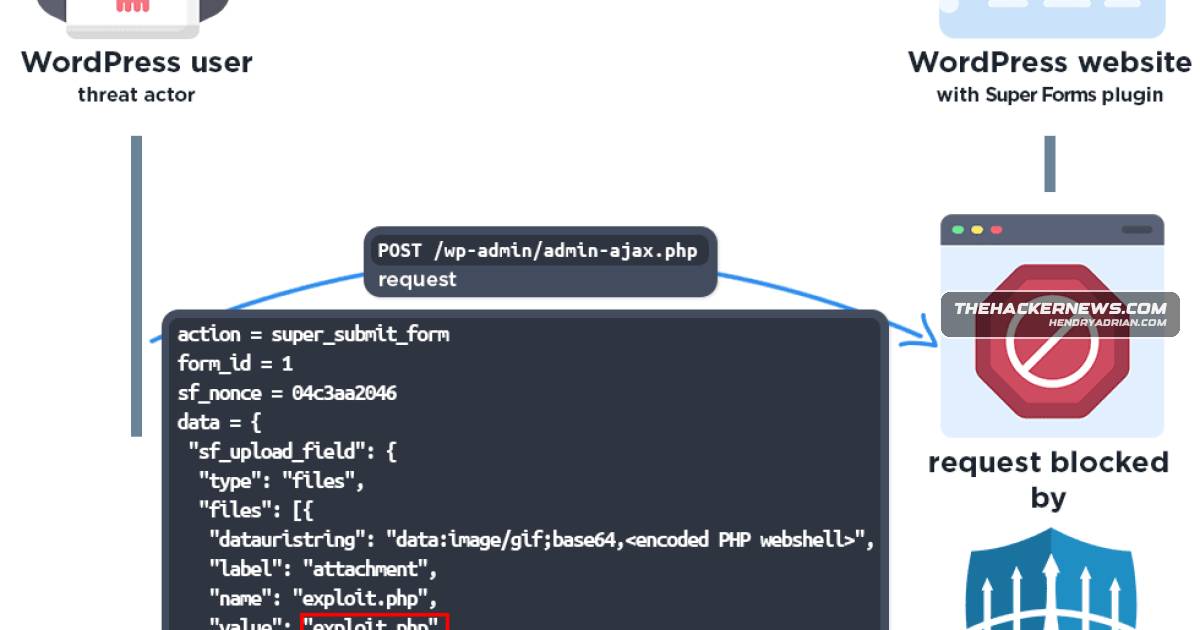
- Super Forms attacks used a POST request to the admin AJAX endpoint and uploaded a PHP web shell named Mushr00w_upl.php.
- Elementor Pro attacks exploited a validation bypass in the form upload field; uploaded PHP files were placed in the Elementor forms uploads directory and could be requested to execute commands.
- Wordfence said Super Forms exploitation began July 14, 2026, and peaked above 40,000 requests on August 18; Elementor Pro exploitation began August 19, 2026.
- Site owners are advised to apply the fixes, scan for indicators of compromise, and check for unexpected or recently modified PHP files.
Article Details
- Vulnerability Types
- Missing file type validation enabling arbitrary file upload and unauthenticated remote code execution
- File upload validation bypass enabling arbitrary PHP file upload and unauthenticated remote code execution
- Severity
- Critical; CVE-2026-14894 has a CVSS score of 9.8, and CVE-2026-32475 has a reported CVSS score of 9.0/9.8.
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 103[.]154[.]152[.]178 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 103[.]164[.]182[.]122 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 103[.]168[.]146[.]131 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 103[.]168[.]147[.]235 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 103[.]170[.]97[.]7 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 103[.]84[.]230[.]85 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV4 | 103[.]90[.]148[.]202 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV4 | 114[.]10[.]17[.]253 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV4 | 114[.]10[.]45[.]151 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV4 | 129[.]227[.]46[.]143 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 167[.]254[.]240[.]75 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV4 | 167[.]254[.]241[.]119 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV4 | 182[.]10[.]130[.]51 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 185[.]196[.]220[.]85 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV4 | 189[.]4[.]122[.]140 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 216[.]126[.]225[.]208 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV4 | 37[.]9[.]33[.]62 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV4 | 64[.]176[.]209[.]104 | Source-reported origin IP for attacks exploiting CVE-2026-14894. |
| IPV6 | 2406:ef80:2:7d19::1 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
| IPV6 | 2602:fa59:10:7a1::1 | Source-reported origin IP for attacks exploiting CVE-2026-32475. |
MITRE ATT&CK
CVE
Products
Elementor Pro for WordPressWordfence says threat actors are exploiting critical file upload flaws in the Super Forms and Elementor Pro WordPress plugins, with both issues enabling unauthenticated remote code execution.Super Forms for WordPressWordfence says threat actors are exploiting critical file upload flaws in the Super Forms and Elementor Pro WordPress plugins, with both issues enabling unauthenticated remote code execution.WordPressWordfence says threat actors are exploiting critical file upload flaws in the Super Forms and Elementor Pro WordPress plugins, with both issues enabling unauthenticated remote code execution.