cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited WSO2 and Adobe Commerce Flaws to KEV Catalog

CISA added two WSO2 and Adobe Commerce/Magento vulnerabilities to its KEV catalog based on exploitation evidence. The flaws may enable remote code execution or access to customer data; FCEB agencies must patch by September 27, 2026.
Sep 25, 2026
Vulnerability & Exploit · thehackernews.com

Cloudflare Fixes Container Disk Flaw That Exposed Leftover Customer Data

A flaw in Cloudflare Containers let a customer read leftover data from other customers’ deleted containers on shared servers. Cloudflare fixed Containers and Sandboxes, cleared affected disks and caches, and found no evidence of other use.

Sep 25, 2026
Vulnerability & Exploit · securityweek.com

Attackers Exploit Unauthenticated SQL Injection in Roundcube Webmail

Canada’s Cyber Centre warns that attackers are exploiting CVE-2026-48842, an unauthenticated SQL injection in Roundcube’s virtuser_query plugin. Fixed versions are 1.6.16 and 1.7.1; the number of vulnerable servers is unknown.

Sep 25, 2026
Vulnerability & Exploit · fieldeffect.com

Roundcube SQL Injection Vulnerability Reportedly Exploited in the Wild

Canada’s cybersecurity centre reported active exploitation of CVE-2026-48842, a pre-authentication SQL injection flaw in Roundcube’s optional virtuser_query plugin. Versions before 1.6.16 or 1.7.1 are affected; updating or disabling the plugin mitigates exposure.

Sep 25, 2026
Vulnerability & Exploit · thehackernews.com

Unpatched OnePlus flaws let installed apps gain root access

A researcher chained two OnePlus software flaws to let an installed, no-permission app gain root on affected phones. OnePlus had released no fix by disclosure; there was no evidence of real-world exploitation.

Sep 24, 2026
Vulnerability & Exploit · bleepingcomputer.com

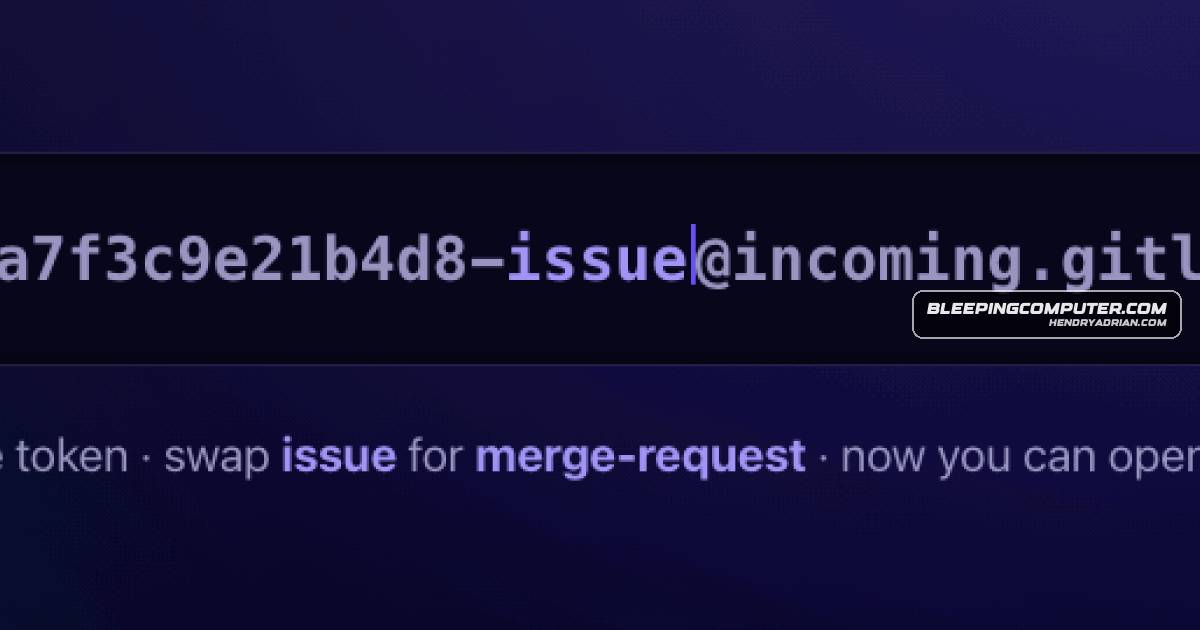
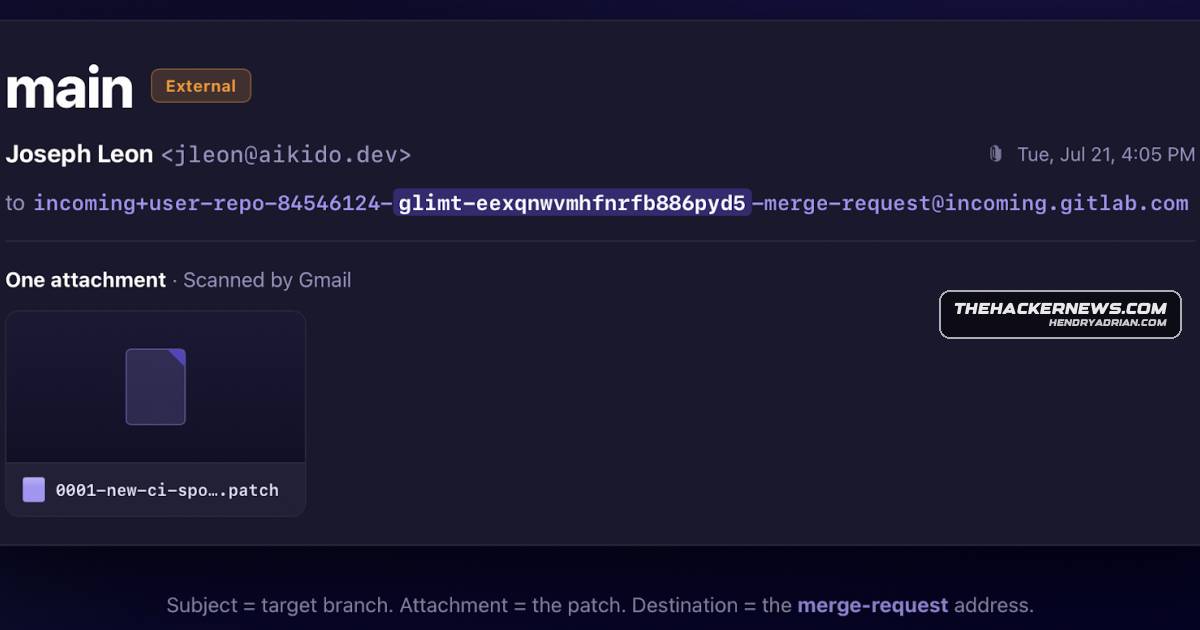
Exposed GitLab Email Addresses Could Let Attackers Create Merge Requests

Aikido researchers found private GitLab project email addresses exposed in public documentation. Anyone with an address could change its suffix to create merge requests, potentially bypassing IP restrictions; GitLab advises resetting leaked tokens.

Sep 24, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Actively Exploit Critical Roundcube SQL Injection Flaw

Canada’s Cyber Centre says attackers are exploiting CVE-2026-48842, a pre-authentication SQL injection flaw in Roundcube’s virtuser_query plugin. Admins should upgrade to patched versions or disable the plugin.

Sep 24, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Says Ransomware Gangs Are Exploiting Critical TeamCity Flaw

CISA says ransomware gangs are exploiting CVE-2026-63077, an unauthenticated command-execution flaw in TeamCity. JetBrains patched it in versions 2025.11.7 and 2026.1.3; administrators are urged to patch or restrict access.

Sep 24, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Two Actively Exploited WSO2 and Adobe Commerce Vulnerabilities to KEV Catalog

CISA added two actively exploited vulnerabilities—affecting WSO2 products and Adobe Commerce/Magento—to its KEV Catalog and urges organizations to prioritize risk-based remediation.

Sep 24, 2026
Vulnerability & Exploit · securityweek.com

SolarWinds Patches Unauthenticated RCE Flaws in Observability Self-Hosted

SolarWinds patched two unauthenticated RCE vulnerabilities in Observability Self-Hosted, affecting versions through 2026.2.2, and a separate hardcoded-key RCE flaw in Access Rights Manager. The company reported no known exploitation in the wild.

Sep 24, 2026
Vulnerability & Exploit · fieldeffect.com

WordPress 7.1.1 Fixes Click2Shell and Comment2Shell Code-Execution Paths

WordPress 7.1.1 fixes 11 vulnerabilities, including two attack paths that can lead to PHP code execution by abusing an administrator’s existing session. Upgrade to 7.1.1 or later and review administrative workflows.

Sep 24, 2026
Vulnerability & Exploit · fieldeffect.com

WordPress CVE-2026-87902 Exploitation Attempts Begin Within Hours of Patch

Researchers observed reconnaissance and exploitation attempts targeting unauthenticated WordPress path traversal CVE-2026-87902 shortly after the September 22, 2026, release of version 7.1.2. Affected deployments should be updated and investigated.

Sep 24, 2026
Vulnerability & Exploit · darkreading.com

Salesforce Agentforce Flaws Could Expose Data and Enable Phishing in Slack

Researchers found Agentforce flaws that could let attackers inject prompts through Web-to-lead forms, expose customer data, and send convincing phishing messages in Slack. Salesforce updated URL inspection and made some Slack actions require confirmation.

Sep 24, 2026
Vulnerability & Exploit · bleepingcomputer.com

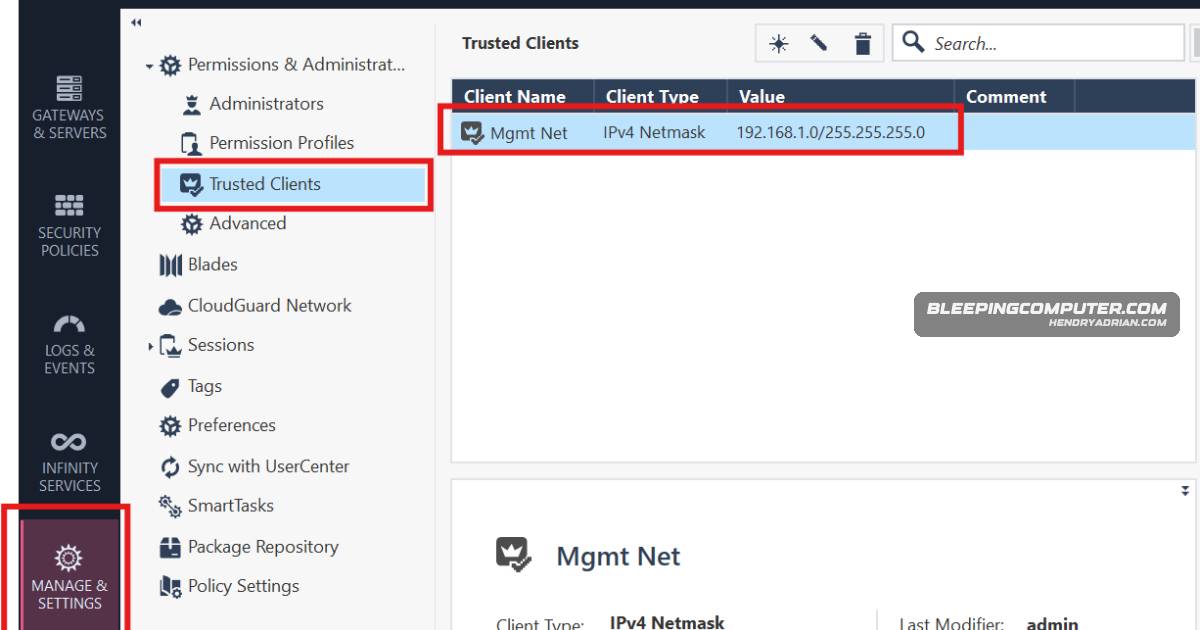
Check Point Confirms Active Exploitation of Two Security Gateway Flaws

Check Point confirmed active exploitation of two pre-authentication flaws affecting Security Gateway and Management web services. CISA added both to its KEV catalog; Check Point recommends updates or mitigations.

Sep 23, 2026
Vulnerability & Exploit · thehackernews.com

GitLab Incoming Email Token Can Let Attackers Commit Code and Run CI Jobs as Account Holders

Aikido Security found that GitLab’s non-expiring incoming-email token can let anyone who obtains it create commits and trigger CI jobs with the account holder’s permissions, bypassing IP restrictions and 2FA. Users can reset the token.

Sep 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Exploit Critical WordPress Flaw to Write Files That Can Execute Shell Commands

Attackers have moved from probing CVE-2026-87902 to writing PHP files that can execute shell commands when accessed. WordPress 7.1.2 fixes the flaw; administrators are urged to update and check logs.

Sep 23, 2026
Vulnerability & Exploit · securityweek.com

Adobe Patches Critical Connect and AEM Forms Flaws Among 36 Vulnerabilities

Adobe patched 36 vulnerabilities across its products, including critical flaws in Connect and AEM Forms that could enable code execution or privilege escalation. Adobe says it is unaware of exploitation in the wild.

Sep 23, 2026
Vulnerability & Exploit · helpnetsecurity.com

WordPress 7.1.2 Patches Critical Unauthenticated Path Traversal Flaw

WordPress 7.1.2 fixes CVE-2026-87902, a critical path traversal flaw affecting versions 4.7.0–7.1.1 that could enable unauthenticated attackers to run code under certain server and theme conditions.

Sep 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

F5 Patches Actively Exploited BIG-IP APM Zero-Day Enabling Remote Code Execution

F5 patched actively exploited CVE-2026-94127, a BIG-IP APM flaw that can enable remote code execution when specific OAuth authorization server settings are configured. CISA added it to its KEV Catalog and set a federal patch deadline.

Sep 23, 2026
Vulnerability & Exploit · rapid7.com

Critical F5 BIG-IP APM Flaw Enables Unauthenticated Remote Code Execution

CVE-2026-94127 is a critical heap-based buffer overflow in F5 BIG-IP APM that may allow unauthenticated RCE when an APM access policy and OAuth profile are configured together. F5 released hotfixes, and the flaw is listed in CISA KEV.

Sep 23, 2026
Vulnerability & Exploit · securityweek.com

Arista Patches Actively Exploited Critical VCO Zero-Day

Arista says CVE-2026-93952, a critical VCO input-validation flaw exploited as a zero-day, affects on-premises deployments. Fixed versions are available; administrators should patch and review logs for suspicious activity.

Sep 23, 2026
Vulnerability & Exploit · securityweek.com

Critical F5 BIG-IP APM Vulnerability Exploited as a Zero-Day

F5 says attackers are exploiting CVE-2026-94127, an unauthenticated RCE flaw in certain BIG-IP APM OAuth configurations. F5 released hotfixes, and CISA added the vulnerability to its KEV list.

Sep 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

Check Point Patches Actively Exploited Management Server Zero-Day

Check Point says attackers are exploiting CVE-2026-93616, a path traversal flaw allowing unauthenticated script execution on several Management Server products. It released a hotfix and recommends temporary mitigations for customers unable to patch.

Sep 22, 2026
Vulnerability & Exploit · thehackernews.com

WordPress Patches Critical Flaw That Could Enable Code Execution on Some Servers

WordPress fixed critical CVE-2026-87902, affecting versions 4.7.0–7.1.1. The unauthenticated flaw can load PHP files outside a theme folder and may enable code execution on some servers. No attacks were reported as of September 22.

Sep 22, 2026
PreviousPage 28 of 65 Next
© 2026 cyber.hendryadrian.com